

awesome-lists
 mthcht/awesome-lists
Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
curated-resourcesdigital-forensicseducation+4
1.9k
mthcht/awesome-listsCurated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
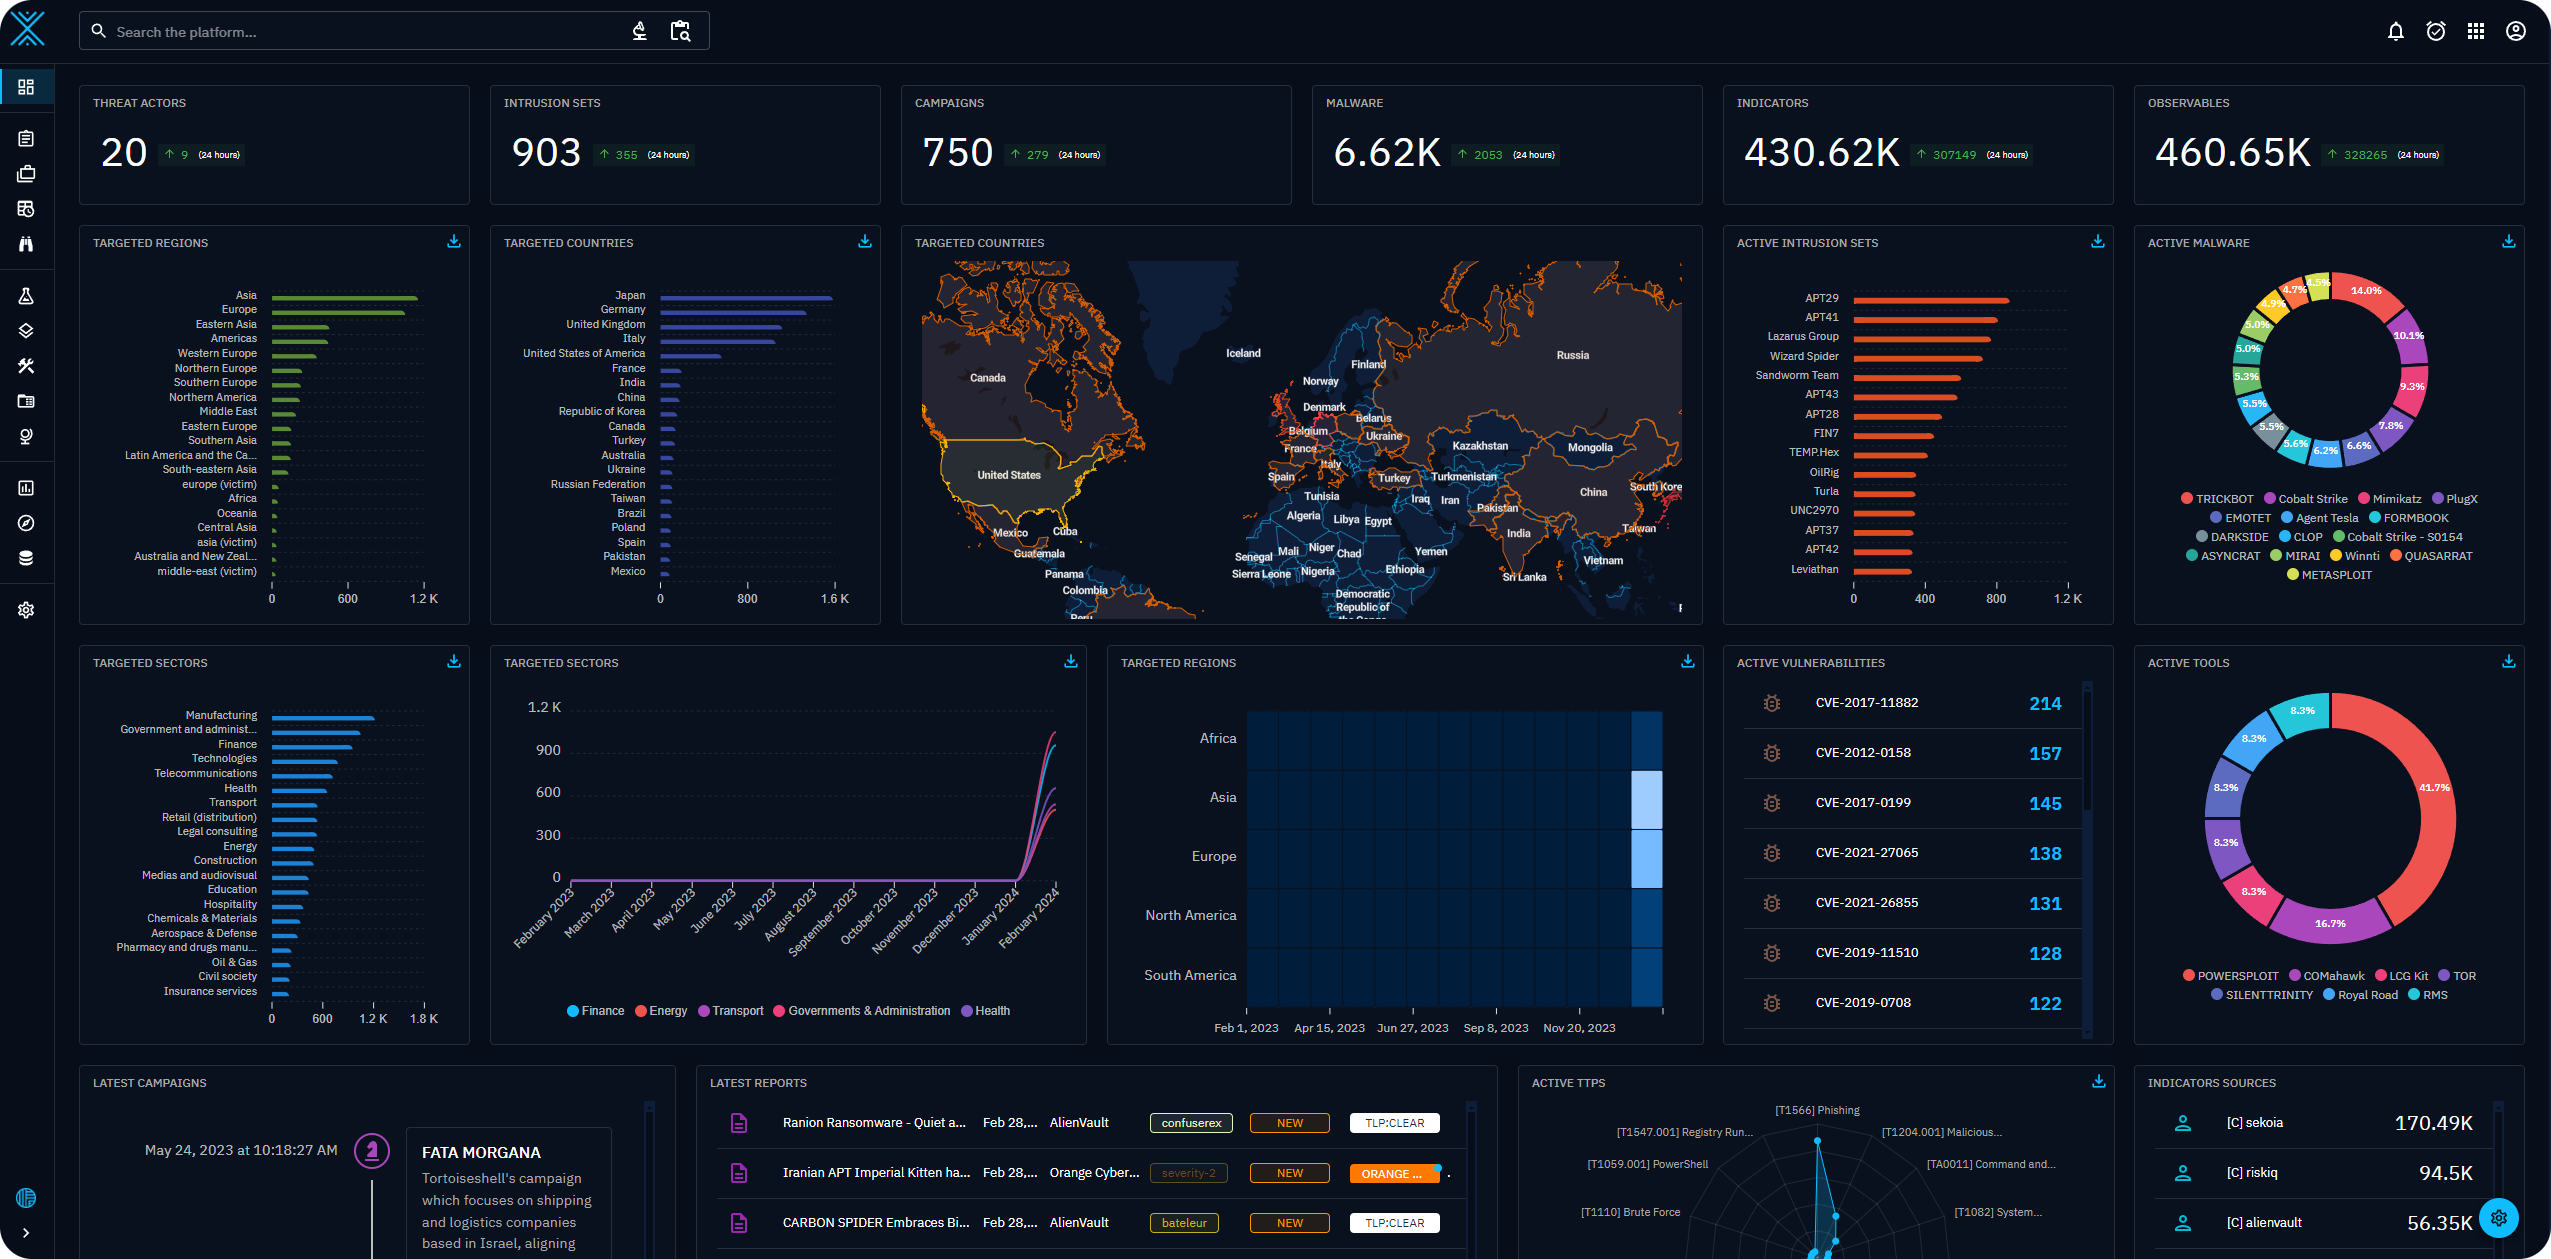 opencti-platform/opencti
Open Cyber Threat Intelligence Platform
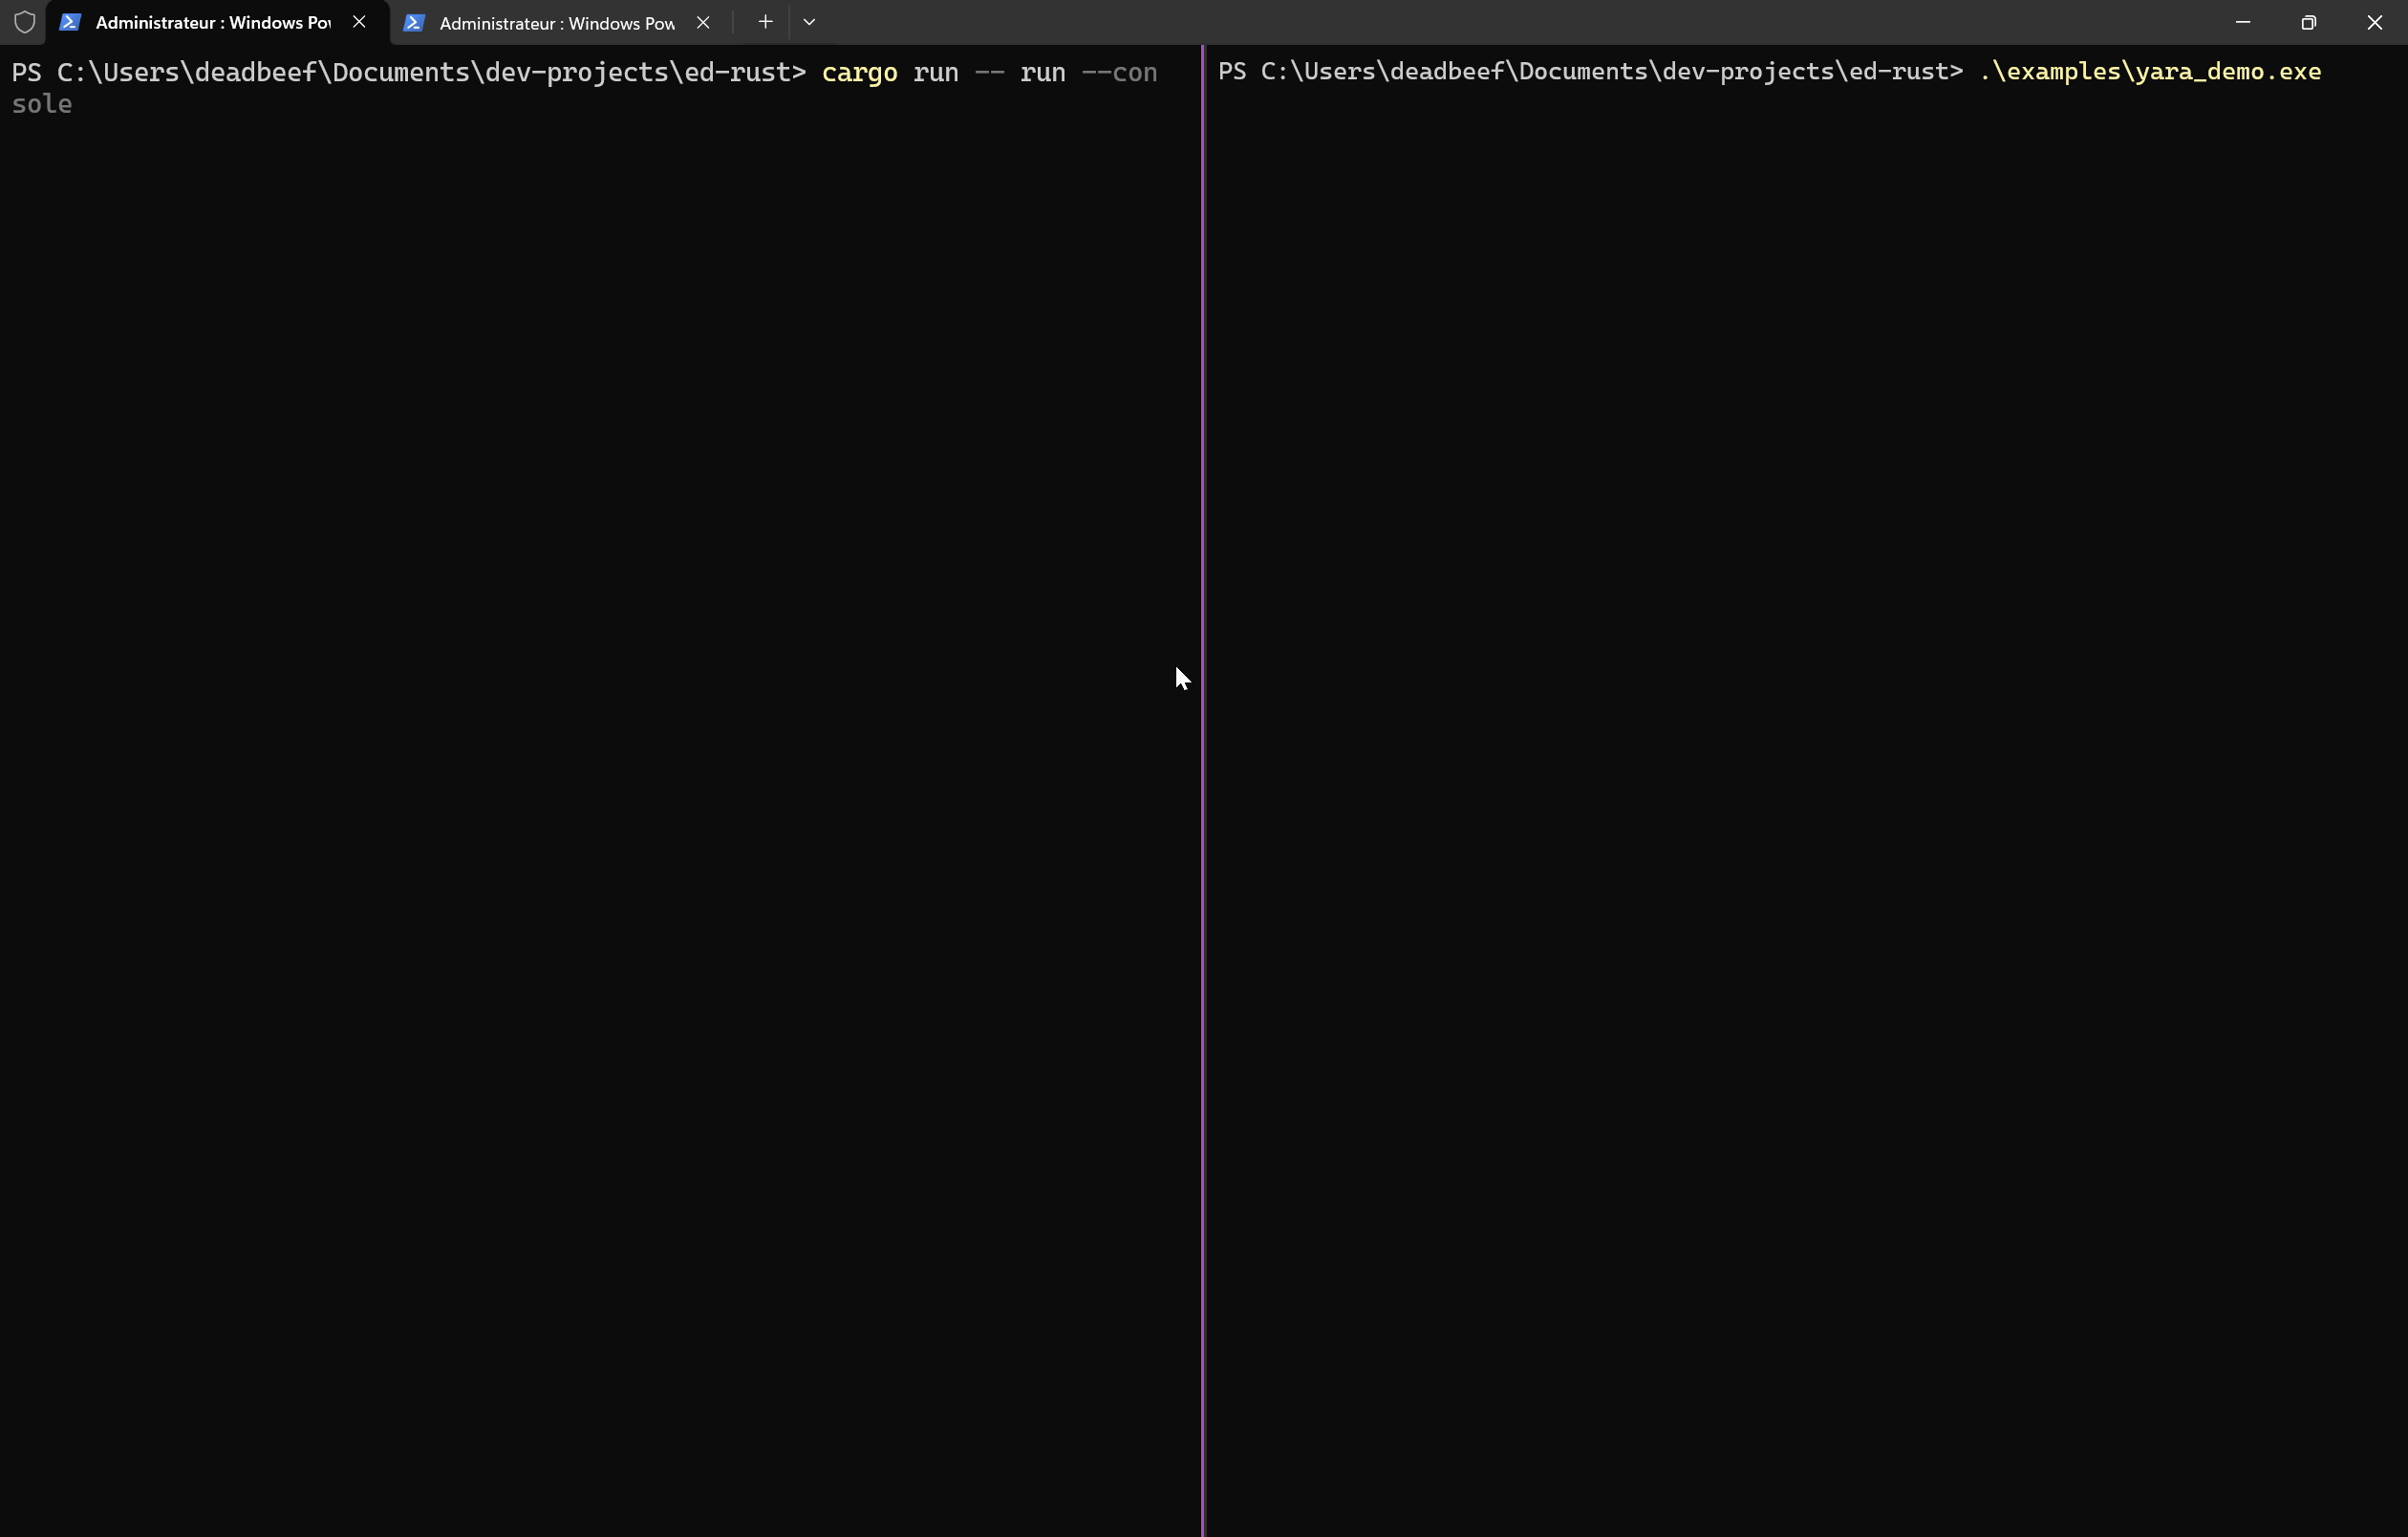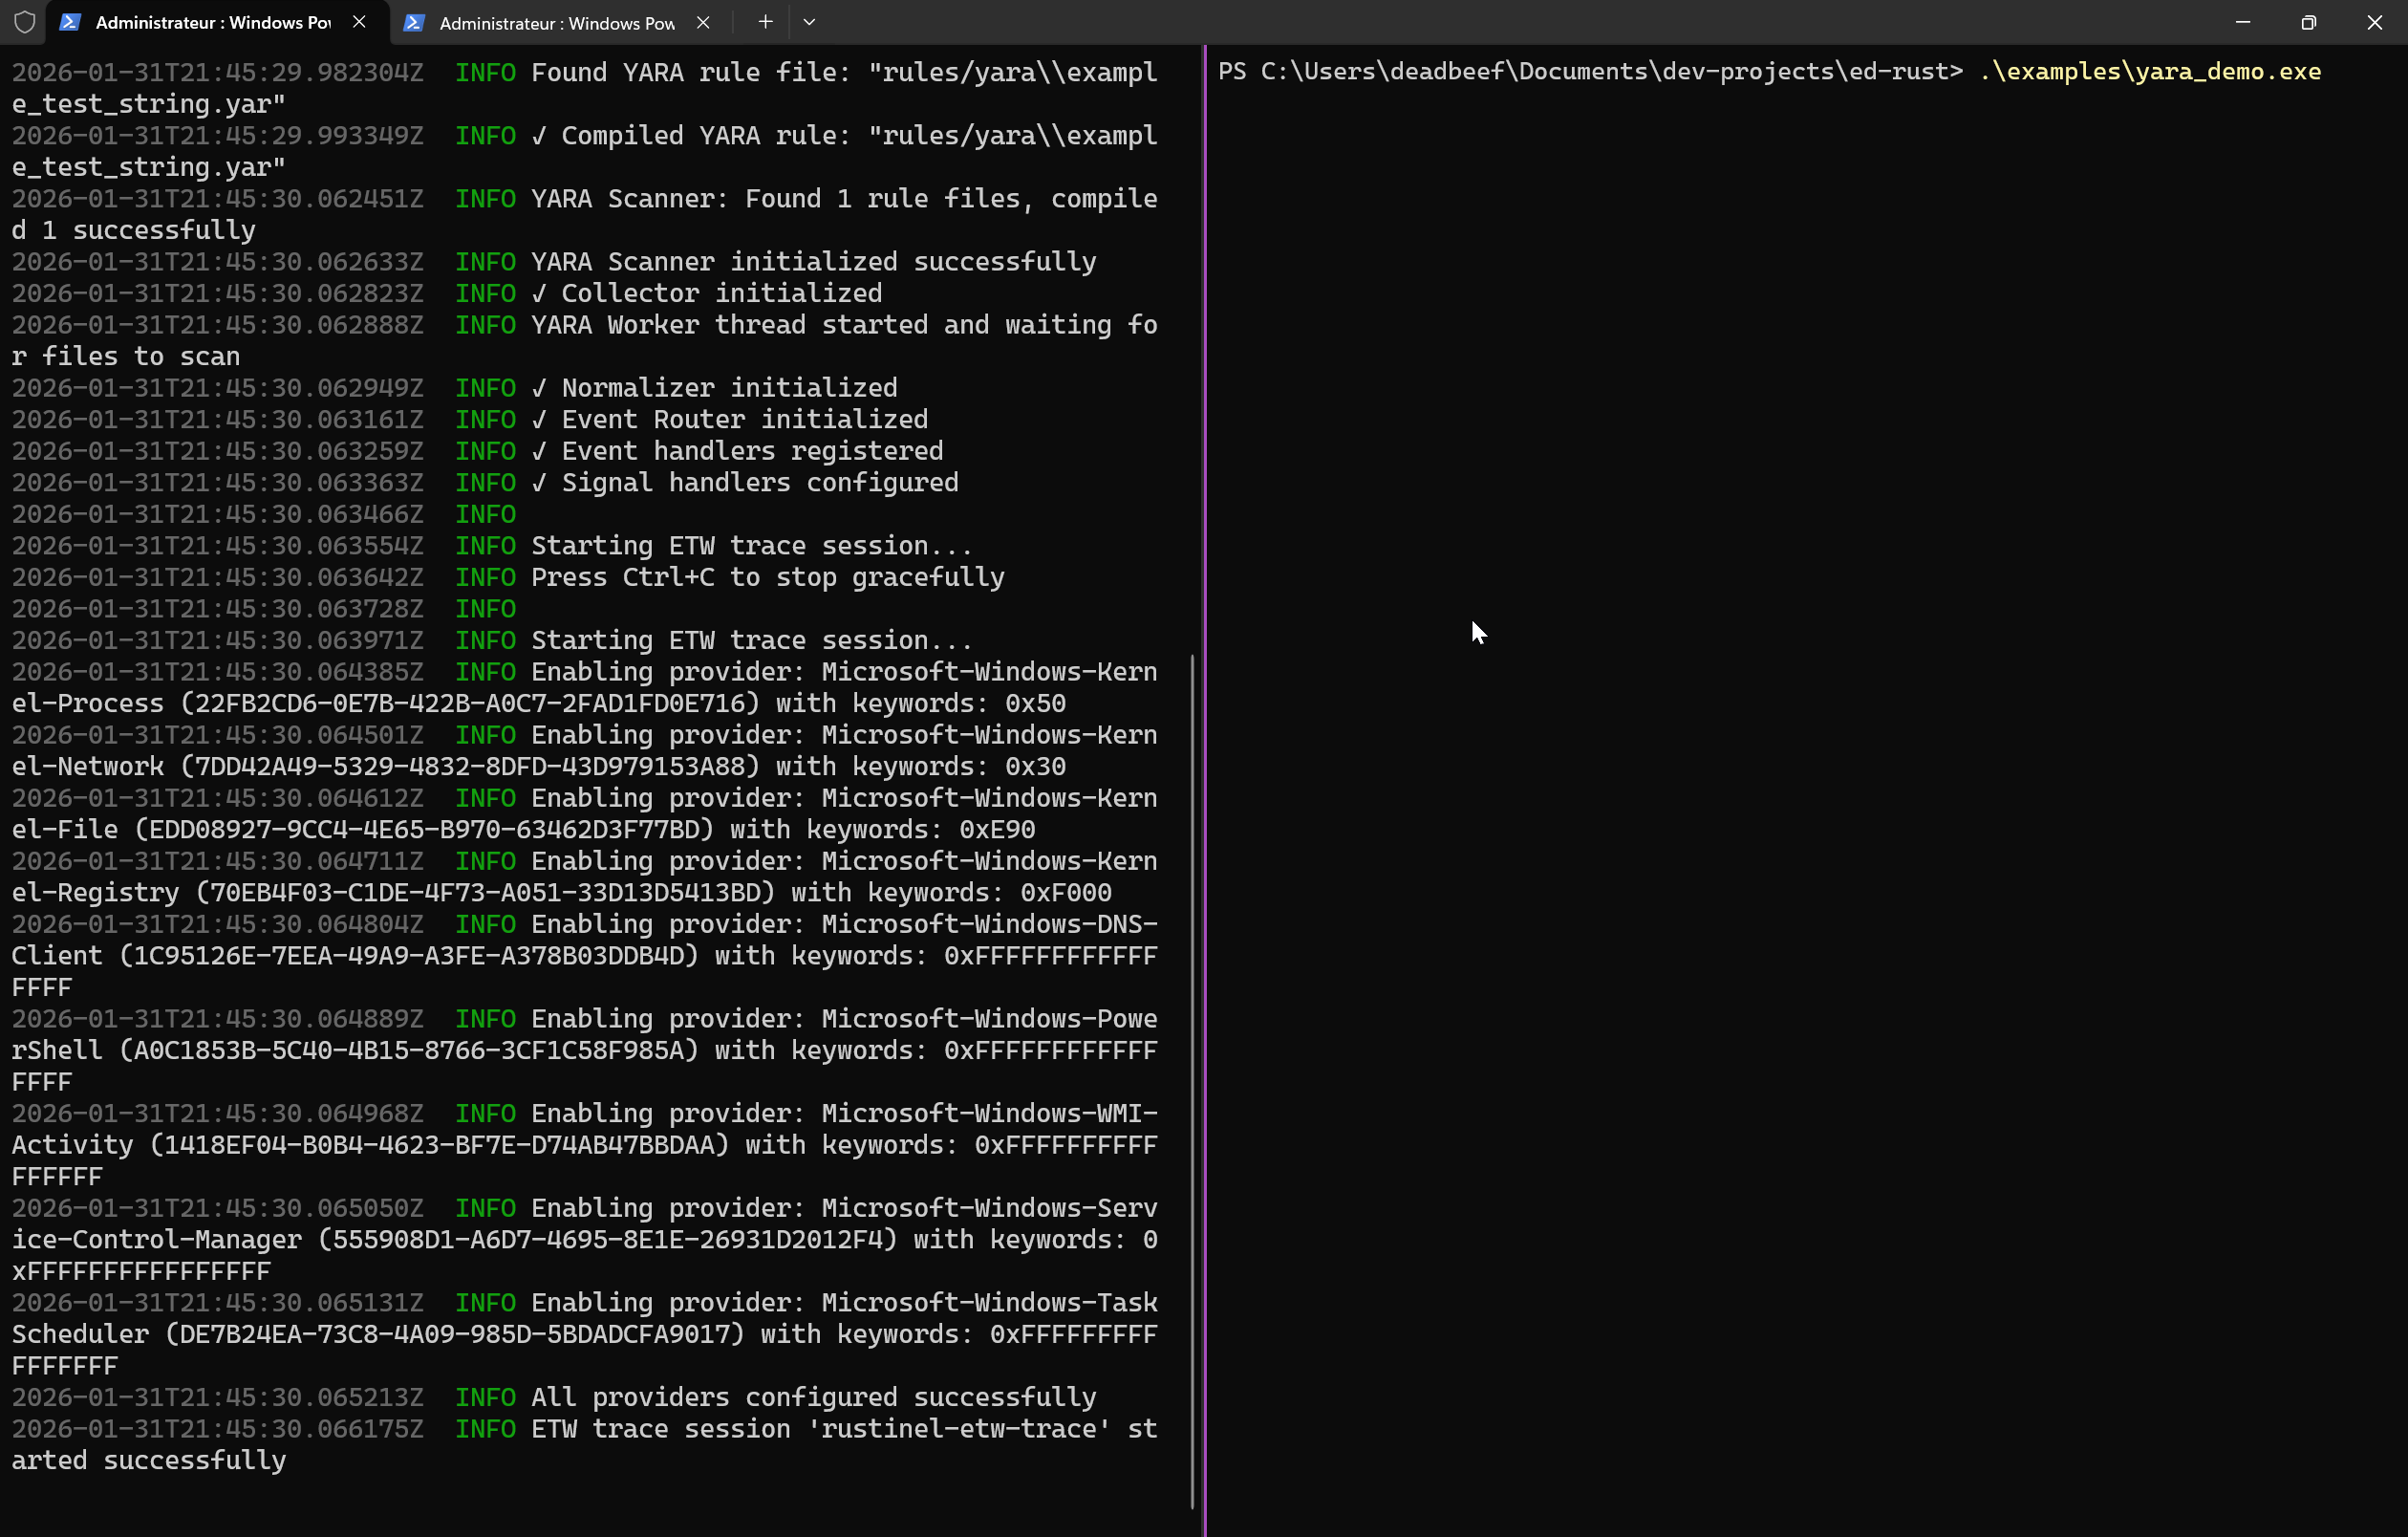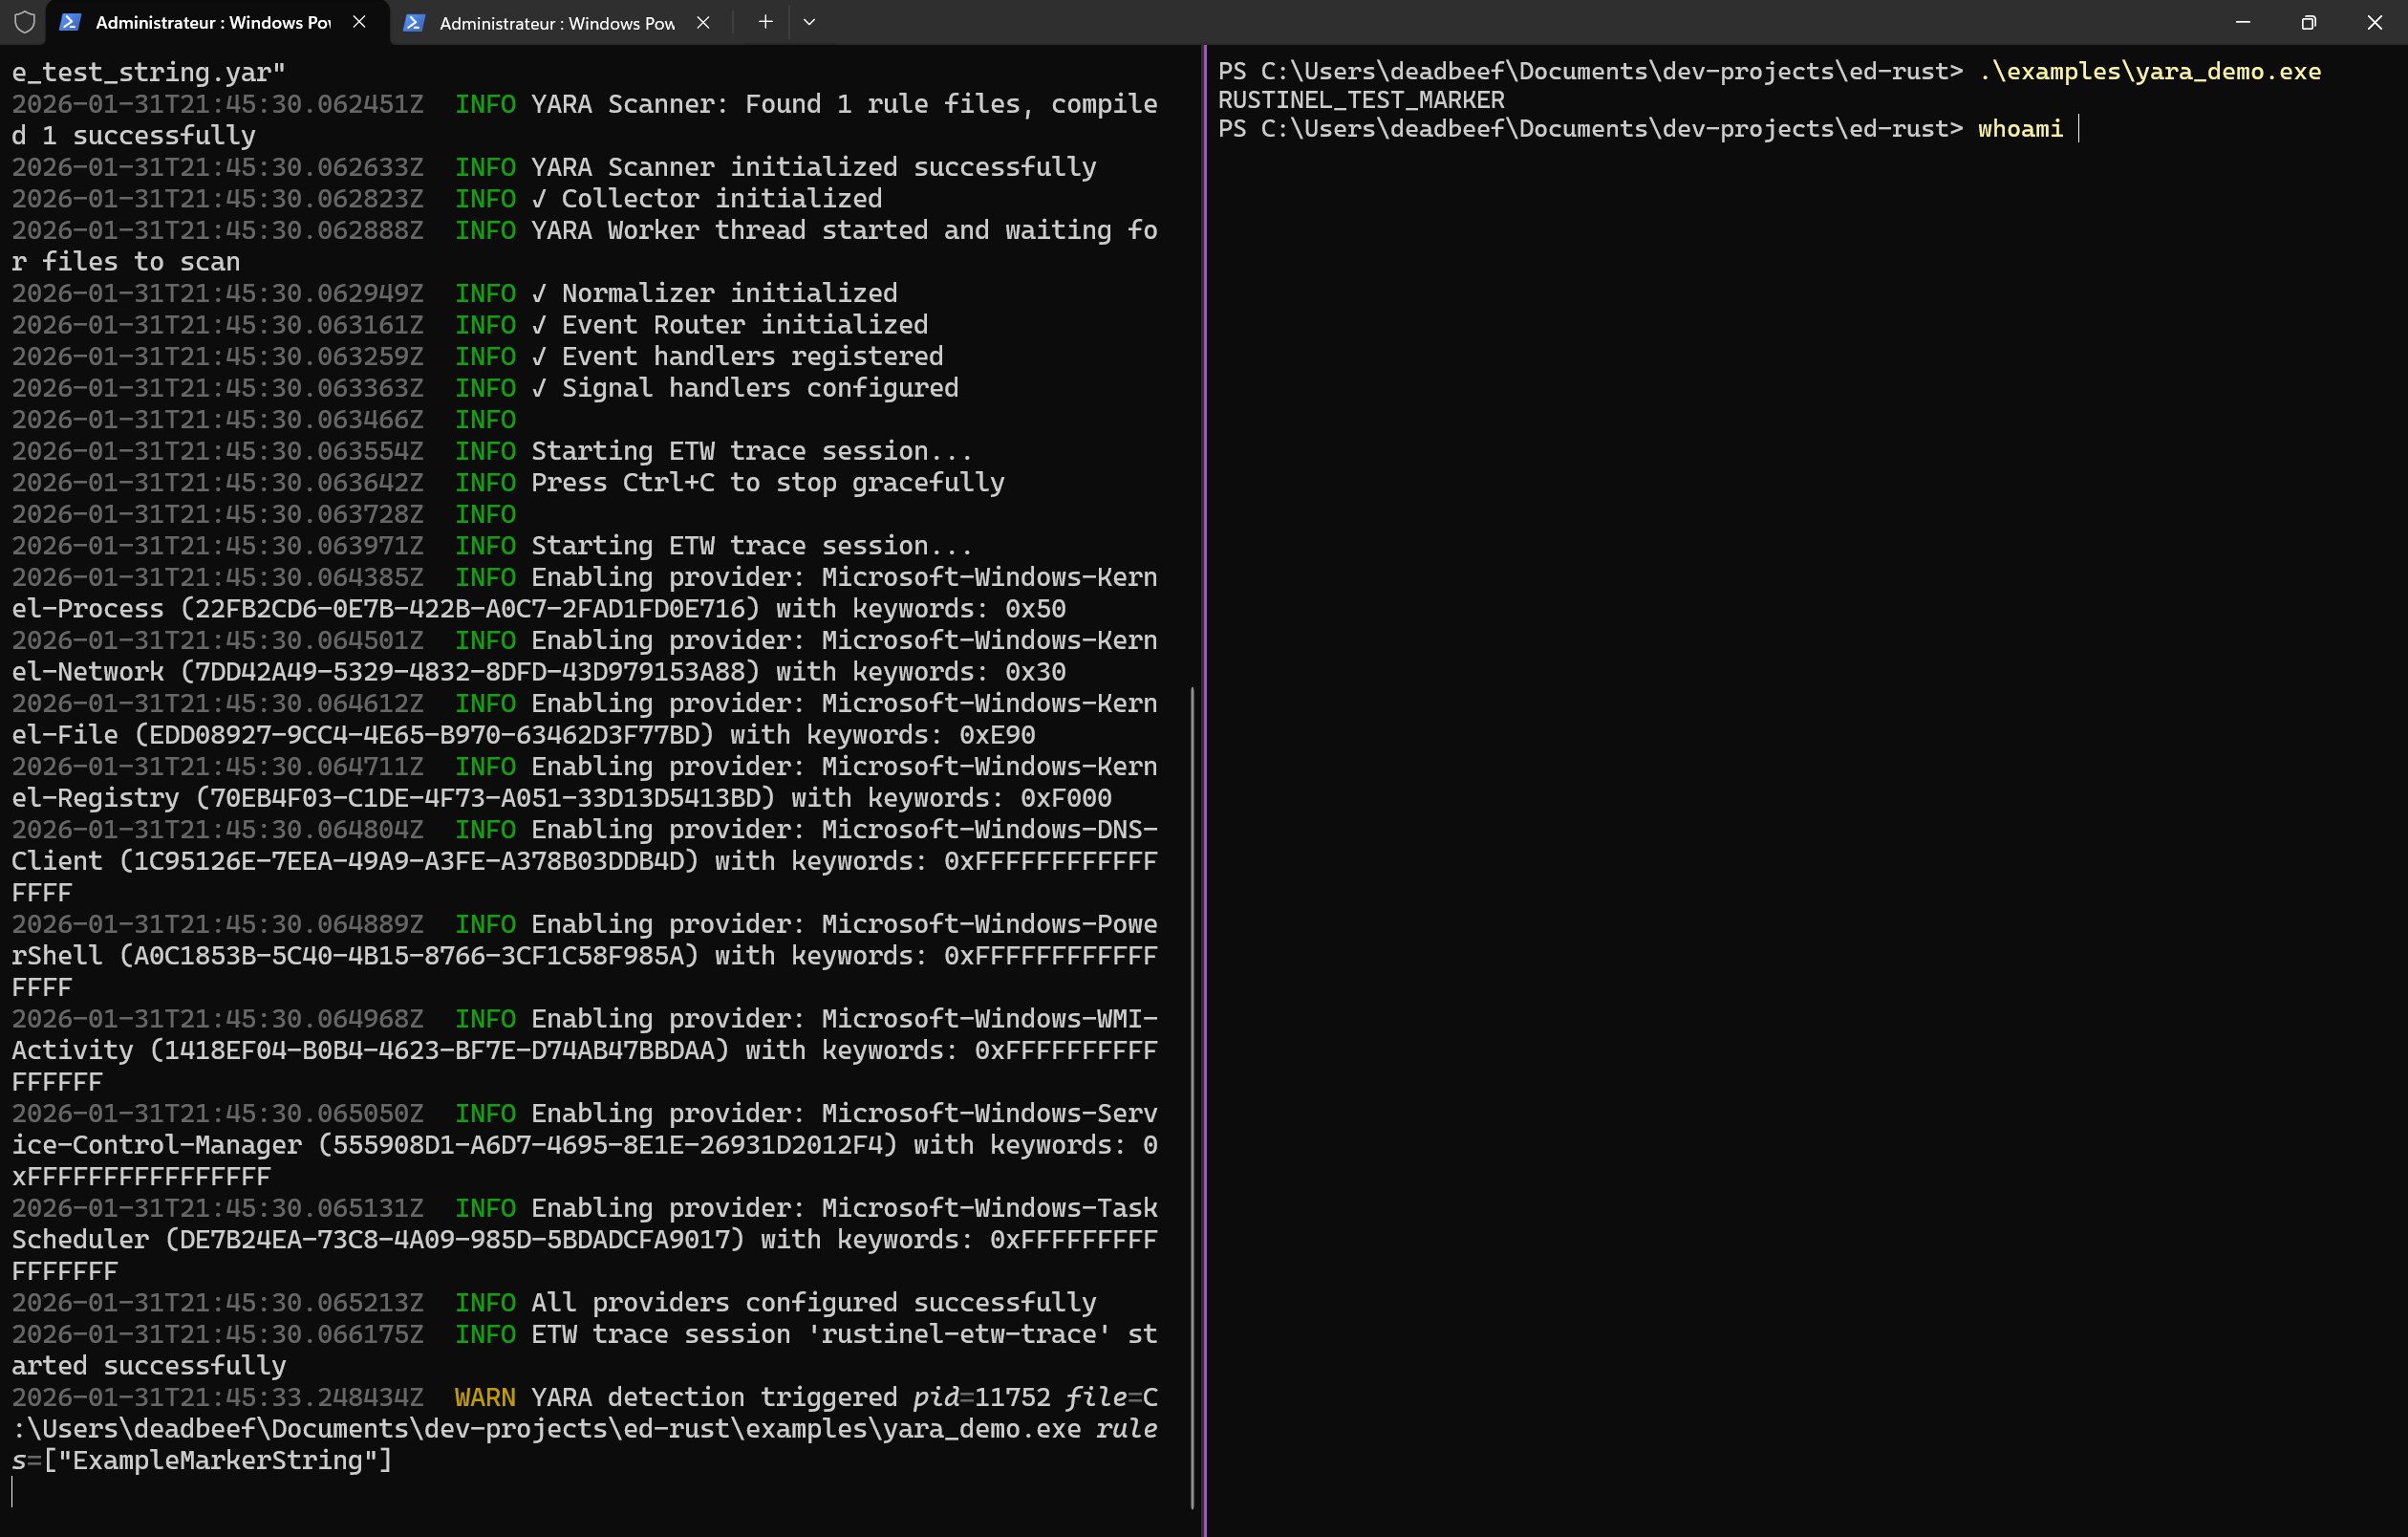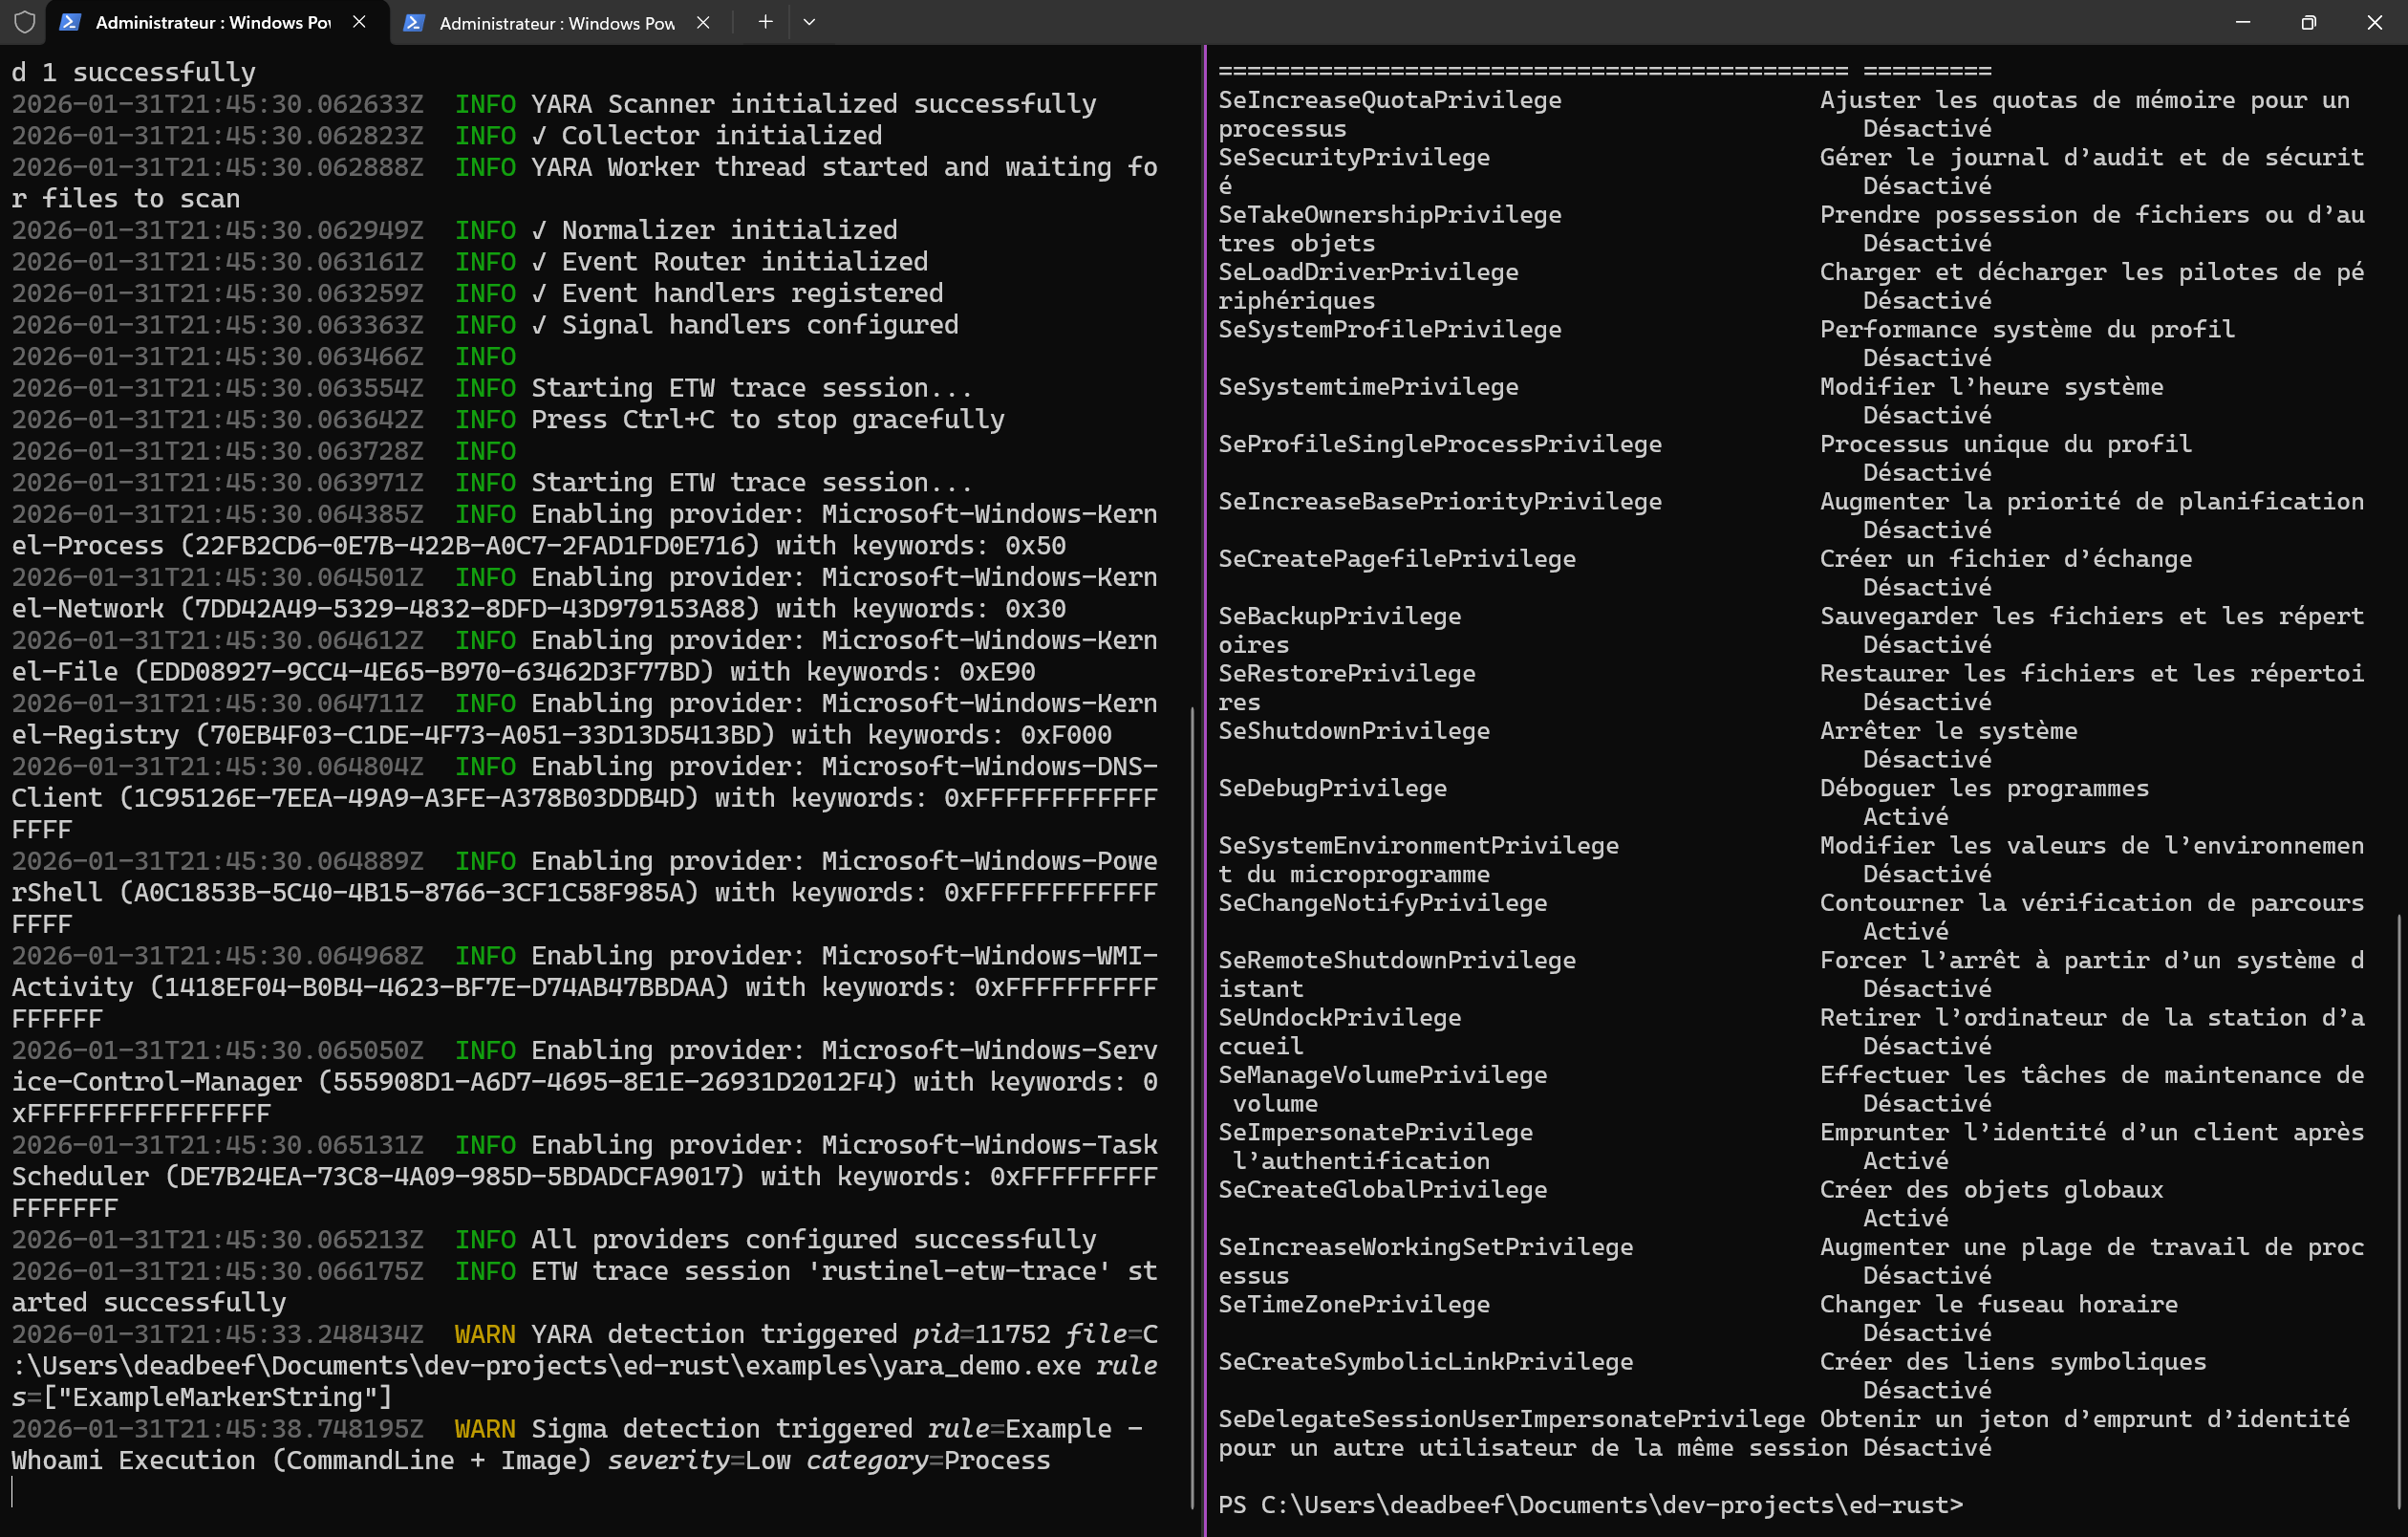 karib0u/rustinel
Endpoint detection for Windows, Linux, and macOS. Sigma, YARA, and IOC rules on native telemetry. Written in Rust. No cloud account required.

 julioliraup/antiphishing
Advanced Phishing Protection: Suricata rulesets open and free
 toborrm9/malicious_extension_sentry
Malicious Extension Database
 essexrich/threatactors-ttps
Repository created to share information about tactics, techniques and procedures used by threat actors. Initially with ransomware groups and evolving…
 misp/misp-objects
Curated JSON object templates that define MISP attributes and relationship types for structured threat intelligence sharing and interoperable IOC…
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 infostealers-stats/data-breach
A continuously updated resource that catalogs confirmed data breaches from across the globe. Each entry includes the breach name, usually aligned…
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
 magicsword-io/loldrivers
Curated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 threatray/threat-research
IoCs and YARA rules from Threatray's Threat Research