Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
177 results
malicious_extension_sentry preview

malicious_extension_sentry

GitHubtoborrm9/malicious_extension_sentry

Malicious Extension Database

curated-resourcesdefensive-toolseducation+6
206
2h 42m ago
awesome-lists preview

awesome-lists

GitHubmthcht/awesome-lists

Curated repository of threat intelligence feeds, IoC lists, YARA rules, and DFIR tool references for SOC/CERT/CTI detection and incident response.
curated-resourcesdigital-forensicseducation+4
1.9k5 hours ago
destroylist preview

destroylist

GitHubphishdestroy/destroylist

Real-time phishing & scam domain blocklist - 205k+ curated threats, 1M+ community, free API, multiple formats

curated-resourcesdefensive-toolsdns-analysis+8
1.9k9h 38m ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

data-recoverydigital-forensicsdisk-forensics+9
3.0k14h 8m ago
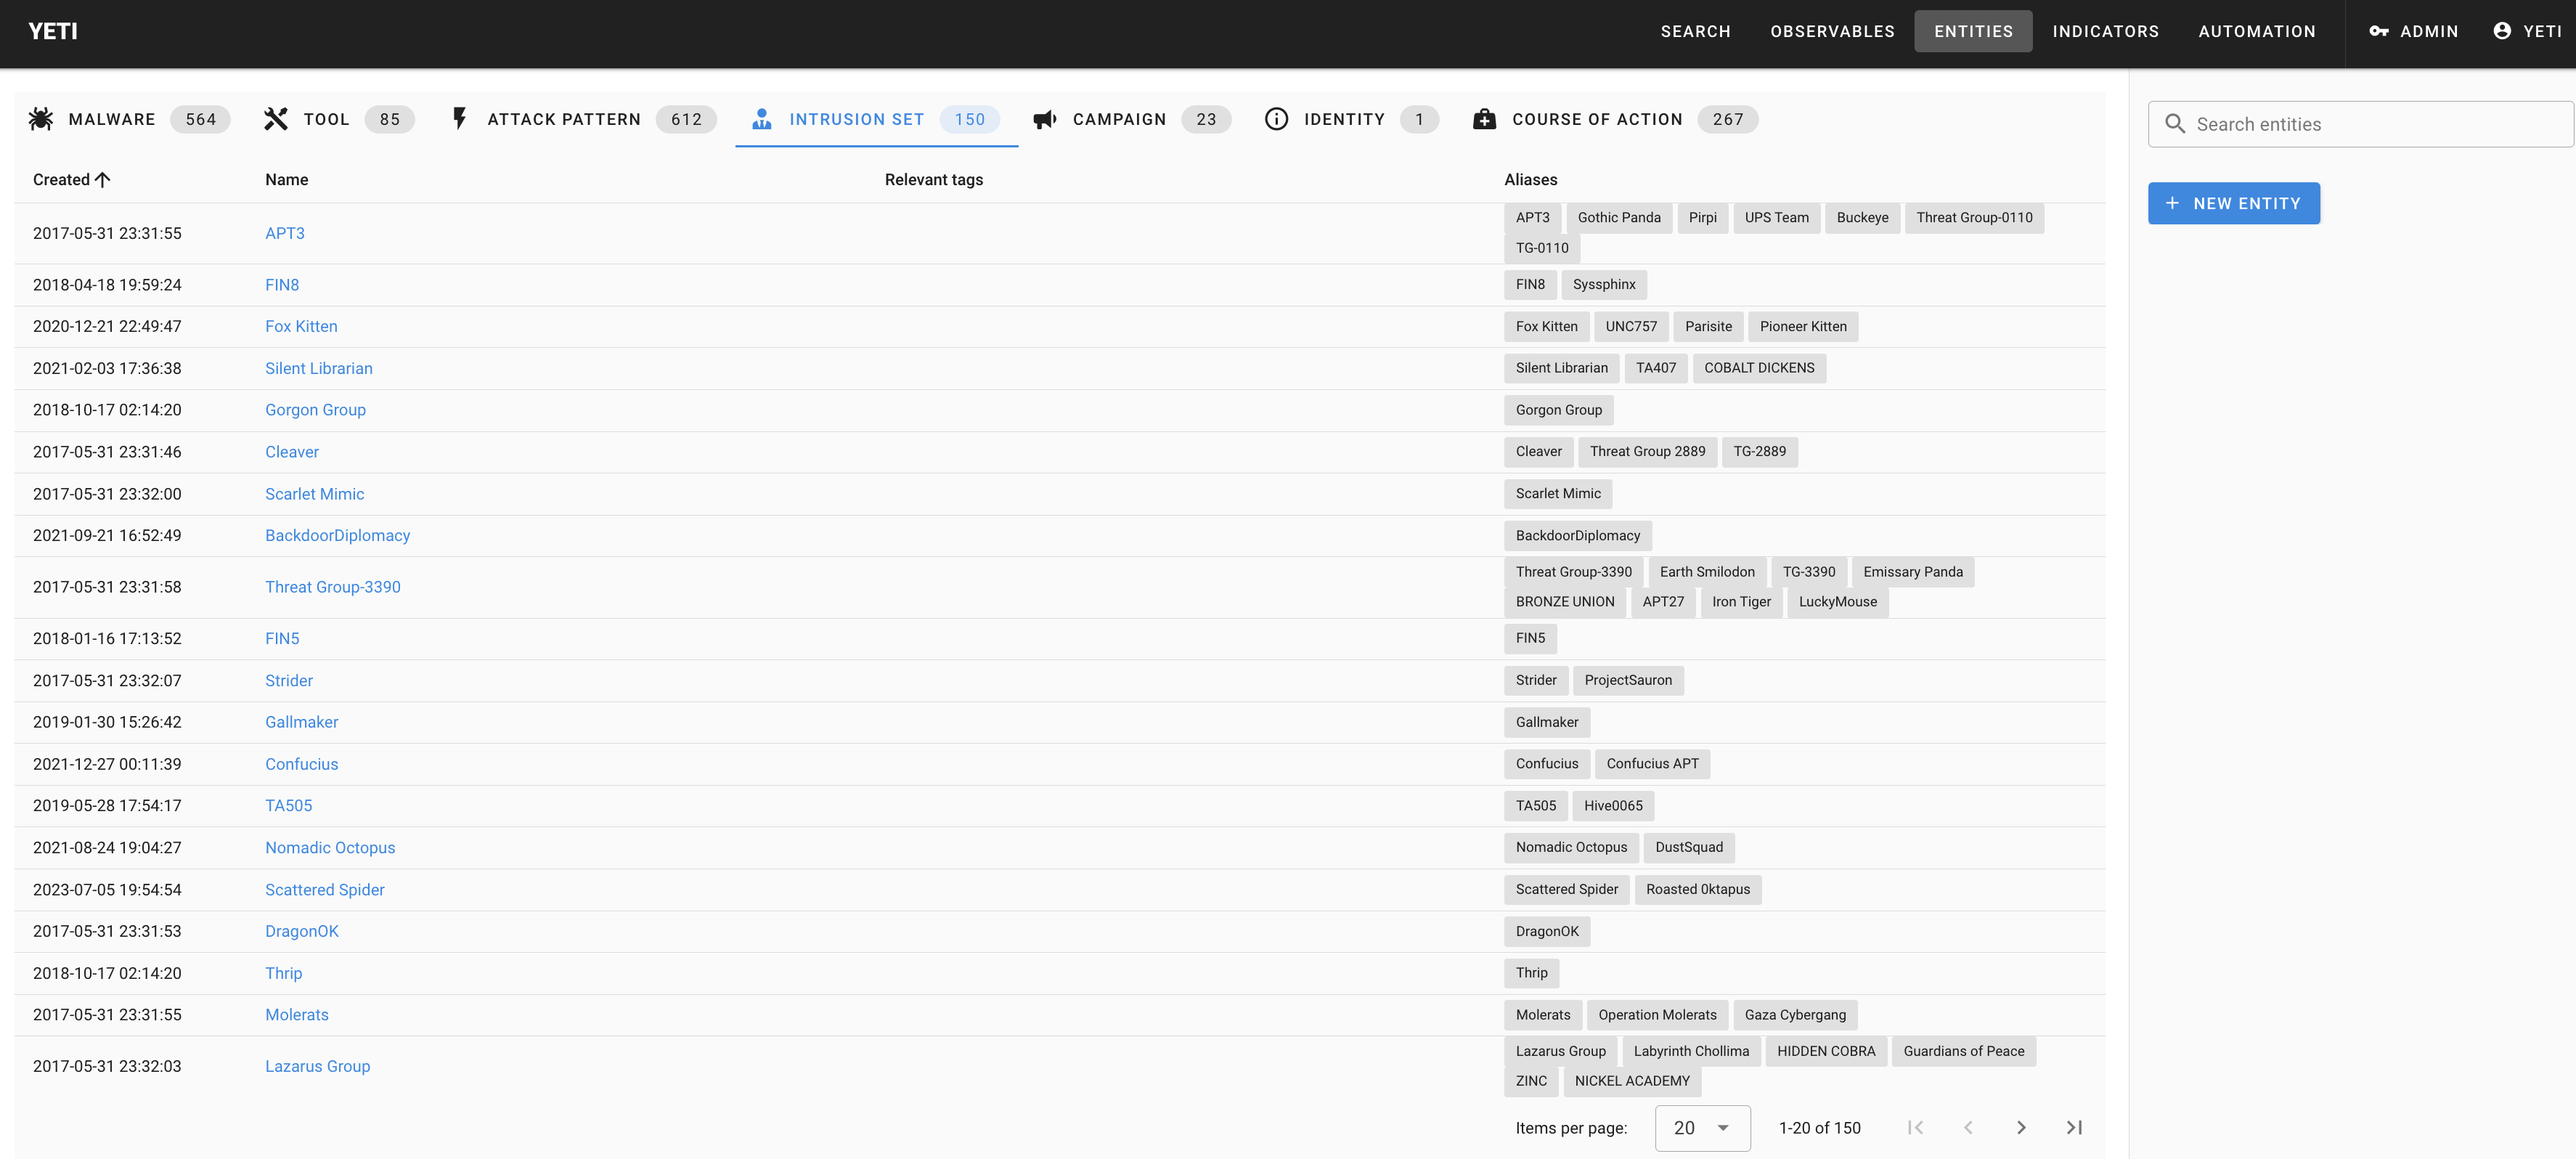
yeti preview

yeti

GitHubyeti-platform/yeti

Your Everyday Threat Intelligence

digital-forensicseducationforensics+8
2.0k18h 13m ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.3k18h 47m ago
Antiphishing preview

Antiphishing

GitHubjulioliraup/antiphishing

Advanced Phishing Protection: Suricata rulesets open and free
defensive-toolsdns-analysisids-ips-evasion+6
3822h 58m ago
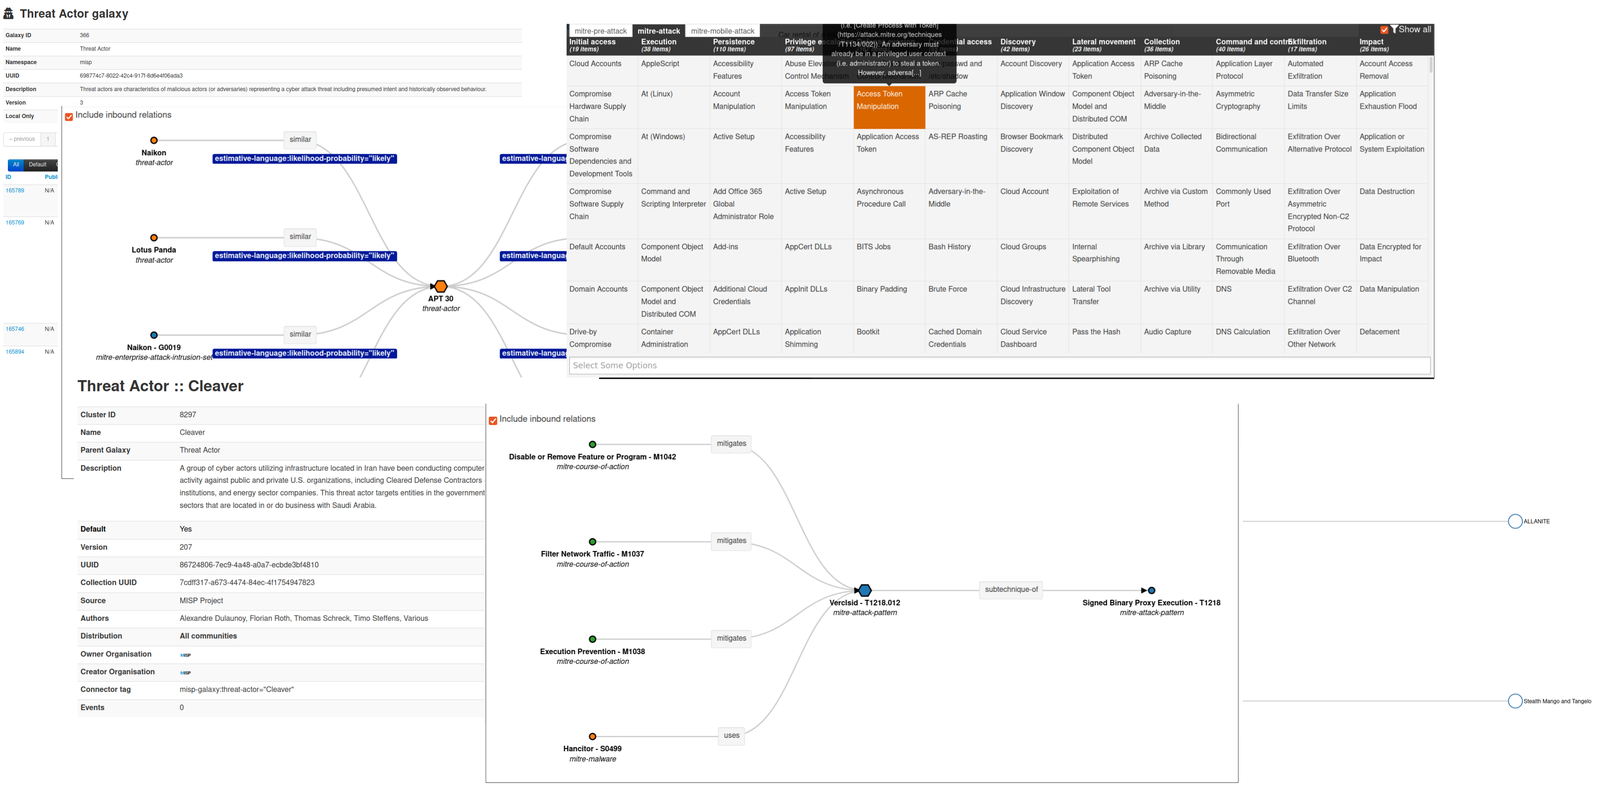
misp-galaxy preview

misp-galaxy

GitHubmisp/misp-galaxy

Clusters and elements to attach to MISP events or attributes (like threat actors)
adversarial-attackcurated-resourcesioc-management+5
6411 day ago
ThreatActors-TTPs preview

ThreatActors-TTPs

GitHubessexrich/threatactors-ttps

Repository created to share information about tactics, techniques and procedures used by threat actors. Initially with ransomware groups and evolving…

curated-resourcesdigital-forensicseducation+6
491 day ago
maltrail preview

maltrail

GitHubstamparm/maltrail

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
anomaly-detectionanti-botdefensive-tools+11
8.6k1 day ago
rustinel preview

rustinel

GitHubkarib0u/rustinel

Endpoint detection for Windows, Linux, and macOS. Sigma, YARA, and IOC rules on native telemetry. Written in Rust. No cloud account required.

incident-responseioc-management
4931 day ago
timesketch preview

timesketch

GitHubgoogle/timesketch

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
data-recoverydigital-forensicsdisk-forensics+7
3.4k1 day ago
Veto preview

Veto

GitHubprofessorquantumuniverse/veto

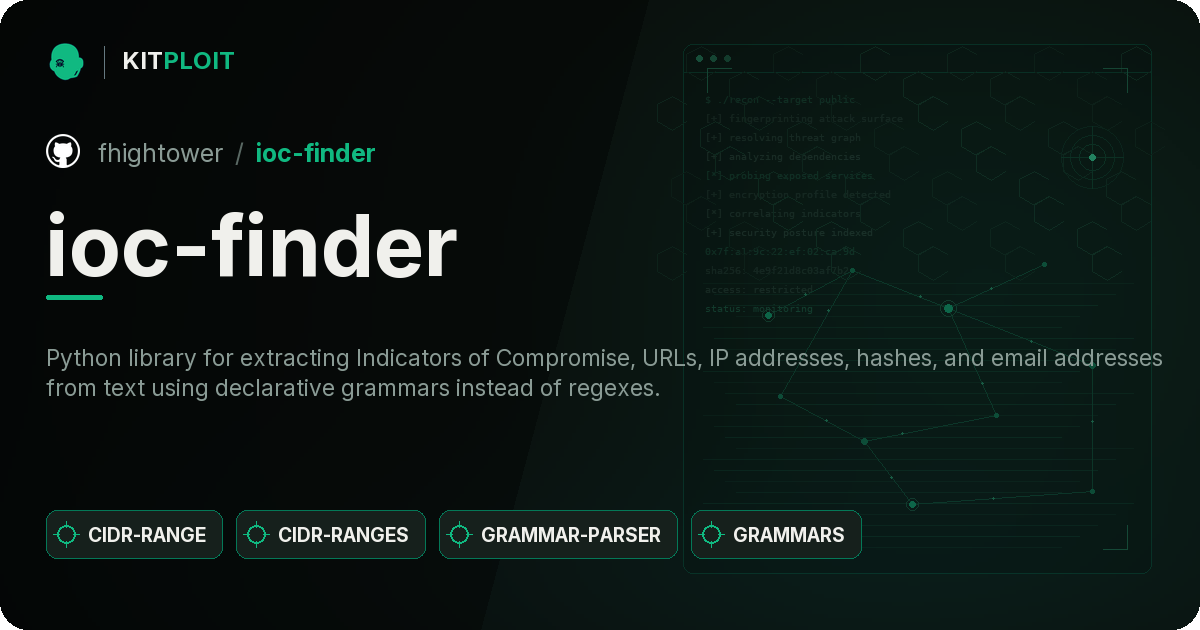
Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…
android-securitydynamic-analysis-sandboxingforensics+8
192 days ago
ioc-finder preview

ioc-finder

GitHubfhightower/ioc-finder

Simple, effective, and modular package for parsing observables (indicators of compromise (IOCs), network data, and other, security related…
ioc-managementmalware-analysisthreat-intelligence+1
1842 days ago
LOLDrivers preview

LOLDrivers

GitHubmagicsword-io/loldrivers

Curated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…

curated-resourceseducationforensics+5
1.8k2 days ago
SOC335-CVE-2024-49138-Exploitation-Detected preview

SOC335-CVE-2024-49138-Exploitation-Detected

GitHubmohamedbrek/soc335-cve-2024-49138-exploitation-detected

LetsDefend SOC lab investigating CVE-2024-49138 and related malicious activity.
digital-forensicseducationincident-response+6
3 days ago
misp-objects preview

misp-objects

GitHubmisp/misp-objects

Curated JSON object templates that define MISP attributes and relationship types for structured threat intelligence sharing and interoperable IOC…
curated-resourcesincident-responseioc-management+3
1113 days ago
Data-Shield_IPv4_Blocklist preview

Data-Shield_IPv4_Blocklist

GitHubduggytuxy/data-shield_ipv4_blocklist

Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…

defensive-toolsincident-responseinformation-gathering+5
6073 days ago
Previous12…10Next