

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
122 results
SigLens preview

SigLens

GitHubst0rn/siglens

Windows artifact analysis toolkit that maps AV detections to PE offsets, sections, RVA/VA and strings, with YARA, AMSI, capa and multi-engine…
binary-analysisdefensive-toolsdigital-forensics+7
3
9 days ago
Exploit-Index preview

Exploit-Index

GitHubsecurewithumer/exploit-index

The Ultimate CVE Proof of Concept (PoC) & Exploit Database. A zero-API, high-performance aggregator for 0days, vulnerabilities, and Threat…
curated-resourcesexploitationinformation-gathering+8
646 days ago
fortimail-zero-day-cve-2026-104286 preview

fortimail-zero-day-cve-2026-104286

GitHubtechupdate24/fortimail-zero-day-cve-2026-104286

A complete guide and workflow for integrating Agile sprints with DevOps CI/CD pipelines.
email-securityexploitationincident-response+3
8 days ago
SOC335---CVE-2024-49138-Exploitation-Detected preview

SOC335---CVE-2024-49138-Exploitation-Detected

GitHubfabianch20/soc335---cve-2024-49138-exploitation-detected

SOC335 incident response walkthrough for CVE-2024-49138 CLFS privilege escalation, covering alert triage, threat intel enrichment, process tree…

digital-forensicseducationincident-response+7
25 days ago
DFIR-Companion preview

DFIR-Companion

GitHubhasamba/dfir-companion

DFIR forensics companion server + capture extension
ai-securitydefensive-toolsdigital-forensics+9
278 days ago
wordpress-upgrade-check preview

wordpress-upgrade-check

GitHubitskill-jp/wordpress-upgrade-check

Read-only check of every WordPress core version on a server. Flags CVE-2026-87902 (fixed in 7.1.2 and backports), auto-updates turned off, and…
configuration-auditingdefensive-toolsincident-response+6
14 days ago
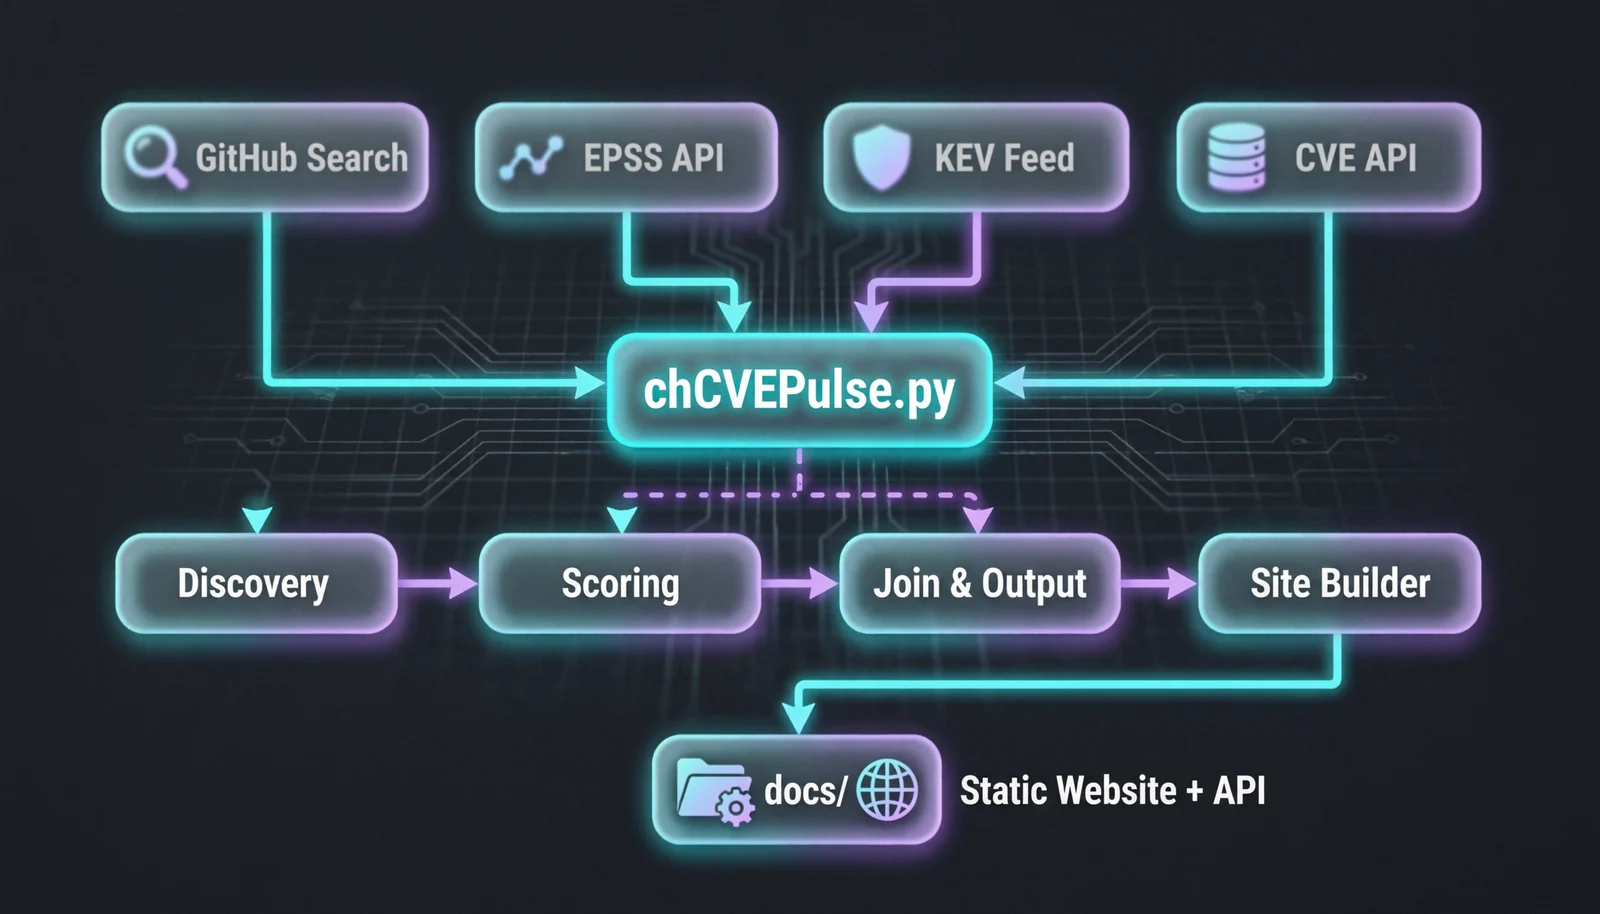
Ch4120N-CVE-Pulse preview

Ch4120N-CVE-Pulse

GitHubch4120n/ch4120n-cve-pulse

Live CVE PoC (Proof-of-Concepts) Aggregator with Smart Search & Threat Intelligence
curated-resourcesexploitationinformation-gathering+8
31 day ago
malware-analysis-fake-hwmonitor preview

malware-analysis-fake-hwmonitor

GitHubdmitry-matvienko/malware-analysis-fake-hwmonitor

Technical analysis, writeup, and YARA rules for a DLL Sideloading campaign disguised as HWMonitor
defensive-toolsdigital-forensicseducation+6
18 days ago
SOC335-CVE-2024-49138-Exploitation-Detected preview

SOC335-CVE-2024-49138-Exploitation-Detected

GitHubmohamedbrek/soc335-cve-2024-49138-exploitation-detected

LetsDefend SOC lab investigating CVE-2024-49138 exploitation and related malicious activity.
digital-forensicseducationincident-response+6
14 days ago
irdoc-app preview

irdoc-app

GitHubsoc-irdoc/irdoc-app

Incident Response Documentation Platform
defensive-toolsdigital-forensicseducation+5
47h 5m ago
SOC-Investigation-CVE-2024-49138 preview

SOC-Investigation-CVE-2024-49138

GitHubbasitsajidsoc/soc-investigation-cve-2024-49138

Investigation and Incident Response report for LetsDefend Alert SOC335 (CVE-2024-49138 Exploitation)

defensive-toolsdigital-forensicseducation+5
1 month ago
ThreatIntel-Aggregator preview

ThreatIntel-Aggregator

GitHubethan-andrews/threatintel-aggregator

Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…

ai-securitydefensive-toolsincident-response+7
5925 days ago
Kage-DFIR-toolkit preview

Kage-DFIR-toolkit

GitHubkarim852/kage-dfir-toolkit

Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
defensive-toolsdigital-forensicsforensics+8
2622 days ago
Tourmaline preview

Tourmaline

GitHubv-pun215/tourmaline

Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…

command-and-controlcryptographydigital-forensics+7
1029 days ago
BlueBox preview

BlueBox

GitHubsvdwi/bluebox

Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
ioc-managementmachine-learningmalware-analysis+4
504 years ago
citrix-netscaler-triage preview

citrix-netscaler-triage

GitHubfox-it/citrix-netscaler-triage

Forensic triage toolkit for Citrix NetScaler devices, featuring a Dissect-based IOC scanner for webshells, timestomping, and suspicious binaries,…
digital-forensicsincident-responseioc-management+3
748 days ago
zimbra-cve-2026-73570-ir preview

zimbra-cve-2026-73570-ir

GitHubdahnutz/zimbra-cve-2026-73570-ir

Detection-first incident-response toolkit for Zimbra administrators investigating CVE-2026-73570. Searches logs for exploit indicators, examines…
defensive-toolsdigital-forensicsincident-response+4
25 days ago
sorry-ransomware-analysis preview

sorry-ransomware-analysis

GitHubhabibkaratas/sorry-ransomware-analysis

Sorry ransomware (.sorry) IOCs, YARA rules and forensic analysis - CVE-2026-41940 cPanel campaign

cryptographydigital-forensicsforensics+4
65 months ago
Previous1234567Next