
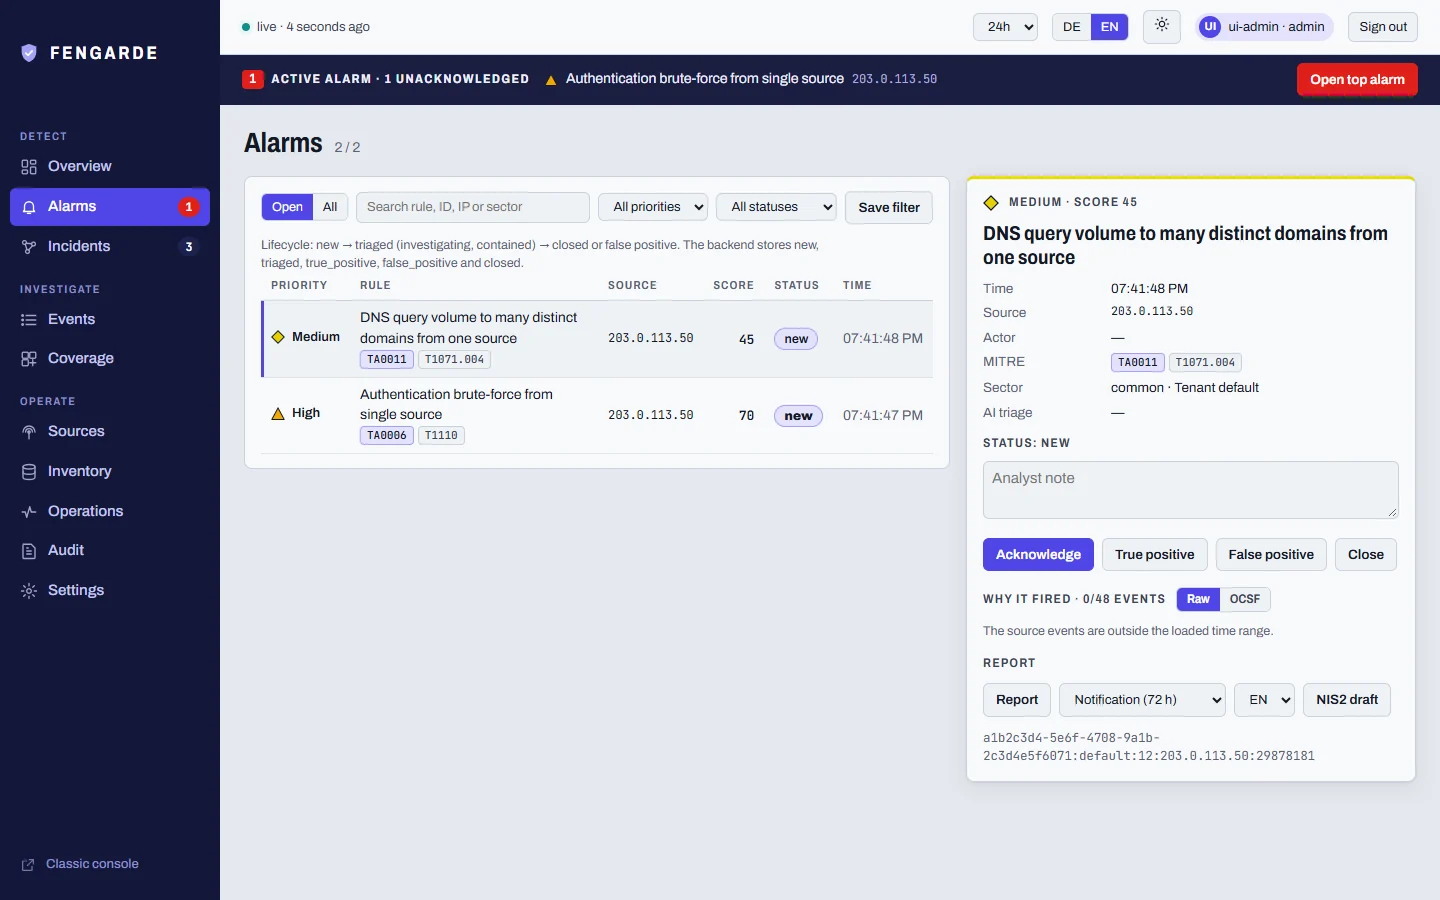
fengarde
 supermhel/fengarde
Open-source, self-hosted security pipeline for IT, AI and OT. Logs in. Evidence out.: OCSF normalization, 46 detection rules…
ai-securitydefensive-toolsincident-response+4
15
supermhel/fengardeOpen-source, self-hosted security pipeline for IT, AI and OT. Logs in. Evidence out.: OCSF normalization, 46 detection rules…
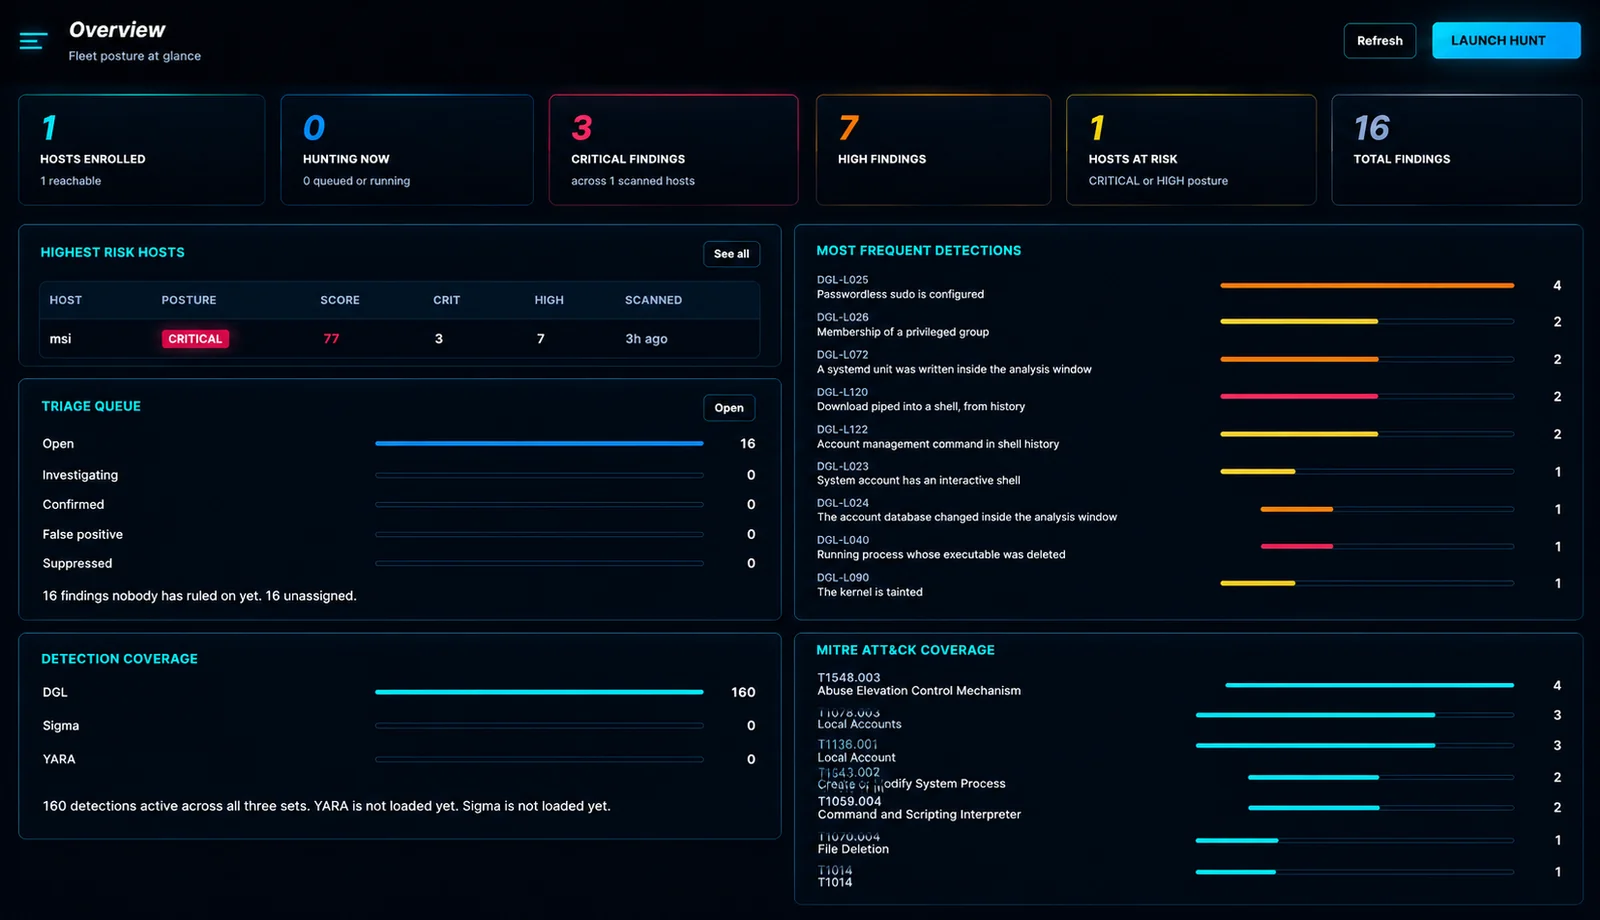 douglas-042/douglas-042-hq
Central console for Douglas-042 HEADQUARTERS collectors. Sweeps a fleet, correlates results across hosts, and manages IOC feeds and SIEM delivery…
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 kadir/copy-fail-cve-2026-31431-ioc
Detection, mitigation, and IOC toolkit for Copy Fail CVE-2026-31431 Linux kernel page-cache privilege escalation
 spectralzero/netscope
Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
 volexity/threat-intel
Signatures and IoCs from public Volexity blog posts.
 gendigitalinc/ioc
Threat Intel IoCs + bits and pieces of dark matter. Published by Gen Threat Labs.
 sifalcon/detection
Curated collection of detection rules and IOCs extracted from DFIR engagements and malware analyses to support threat hunting, incident response, and…
 huntresslabs/threat-intel
This repository contains supplemental items including IOCs, and signatures discussed in Huntress blogposts, and other media.
 michael-kanda/wp2shell-ioc-scanner
Detects shadow-administrator accounts in WordPress via configurable indicators and heuristics, then removes selected accounts through guarded, logged…
 nccgroup/mimikatz-detector-busylight
USB HID driver emulation with PID/VID (0x3bca/0x27bb) of Plenom A/S Busylight Alpha, that is supported by Mimikatz. When mimikatz is executed, a…
 synacktiv/synacktiv-rules
Public repository of Sigma and YARA rules created by Synacktiv
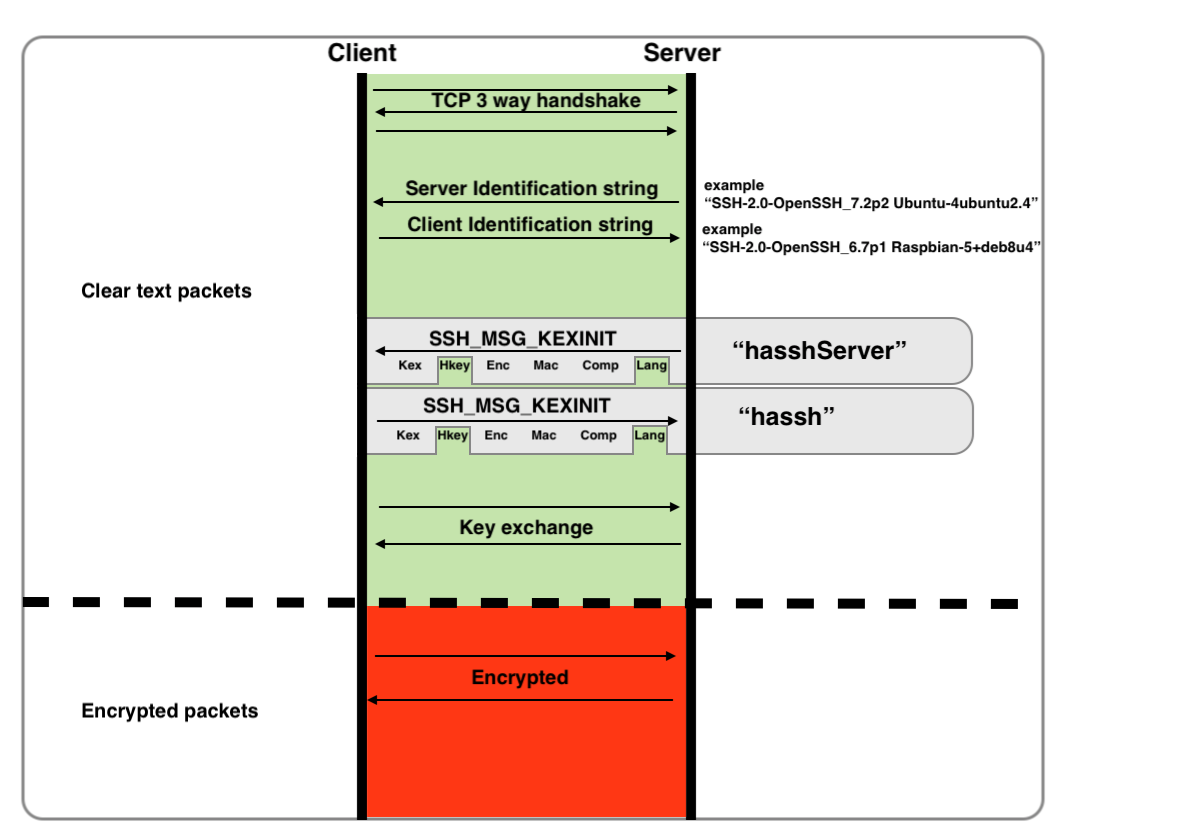 corelight/hassh
Fingerprint SSH clients and servers.
 travisbgreen/cve-2025-8088
cve-2025-8088_detection
 murrayr0123/cve-2024-3400-compromise-checker
A simple bash script to check for evidence of compromise related to CVE-2024-3400
 limo57640-crypto/cpanel-cve-41940-detector
Read-only cPanel CVE-2026-41940 IOC detector for .sorry ransomware, Mr_Rot13 Filemanager backdoors, C2 callbacks, cron, SSH, and logs.
 pisut4152/sigma-rule-for-cve-2021-40438-exploitation-attempt
Sigma-Rule-for-CVE-2021-40438-Attack-Attemp