

yara-rules
 inquest/yara-rules
Collection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
curated-resourcesdefensive-toolsincident-response+5
389
inquest/yara-rulesCollection of YARA rules for hunting malware, malicious Office documents, and exploit artifacts, with references to samples and research write-ups.
 ahmed-tarek22752/security-vulnerability-in-microsoft-office.
Blue-team analysis of a malicious DOCX exploiting CVE-2017-0199, covering sandbox detonation, network forensics, IOC extraction, MITRE ATT&CK…
 basitsajidsoc/soc-investigation-cve-2024-49138
Investigation and Incident Response report for LetsDefend Alert SOC335 (CVE-2024-49138 Exploitation)
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
 nkopylov/tanscript-exploit-check
IOC checker for the TanStack/Mini Shai-Hulud npm supply chain attack (CVE-2026-45321)
 jonathanstross/cve-2025-31324
A Python-based security scanner for identifying the CVE-2025-31324 vulnerability in SAP Visual Composer systems, and detecting known Indicators of…
 respondiq/jsp-webshell-scanner
🔍 A simple Bash script to detect malicious JSP webshells, including those used in exploits of SAP NetWeaver CVE-2025-31324.
 hackinghippo/log4shell_ioc_ips
log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)
 ernestak/sigma-rule-for-cve-2022-30190
Sigma rule for detecting exploitation of CVE-2022-30190 (Follina) via Windows process creation events, enabling SOC teams to identify malicious…
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
 toborrm9/malicious_extension_sentry
Malicious Extension Database
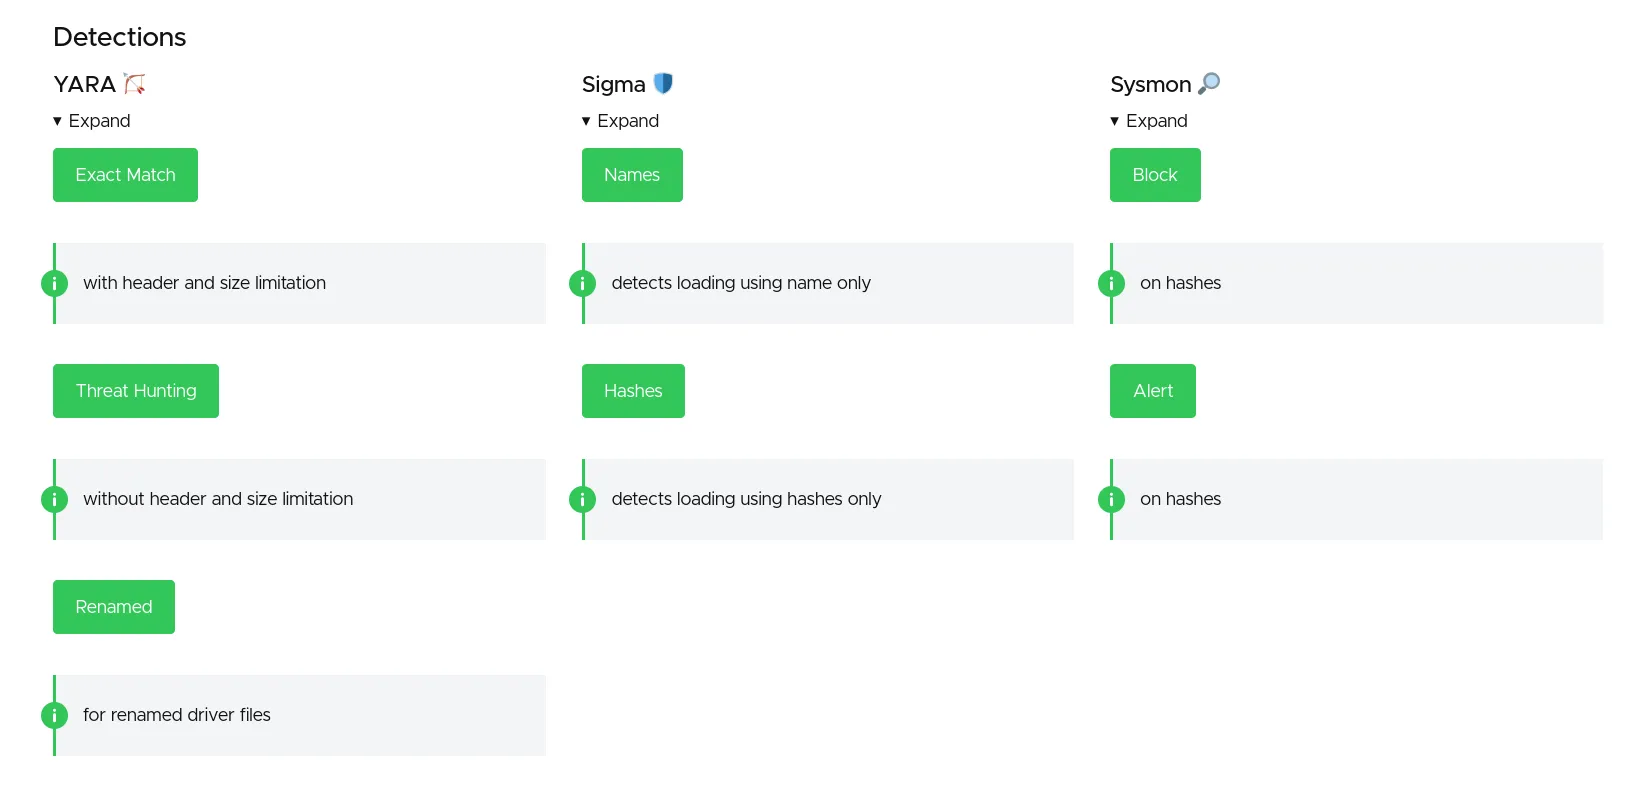 magicsword-io/loldrivers
Curated database of vulnerable and malicious Windows drivers with YARA, Sigma, ClamAV, and Sysmon detection rules for proactive threat hunting and…
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
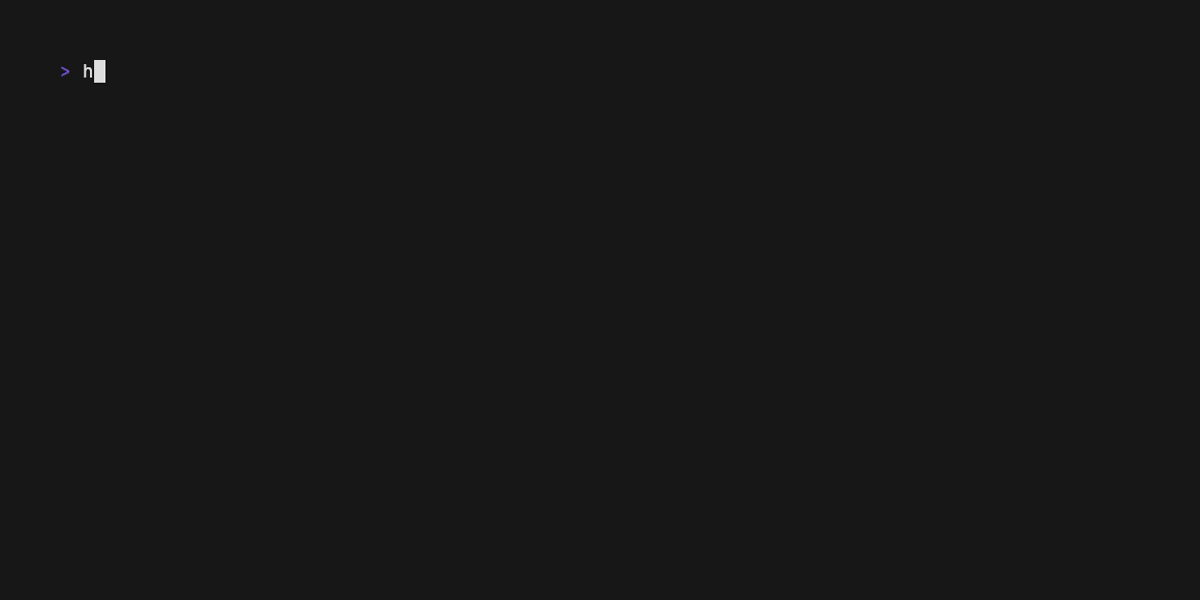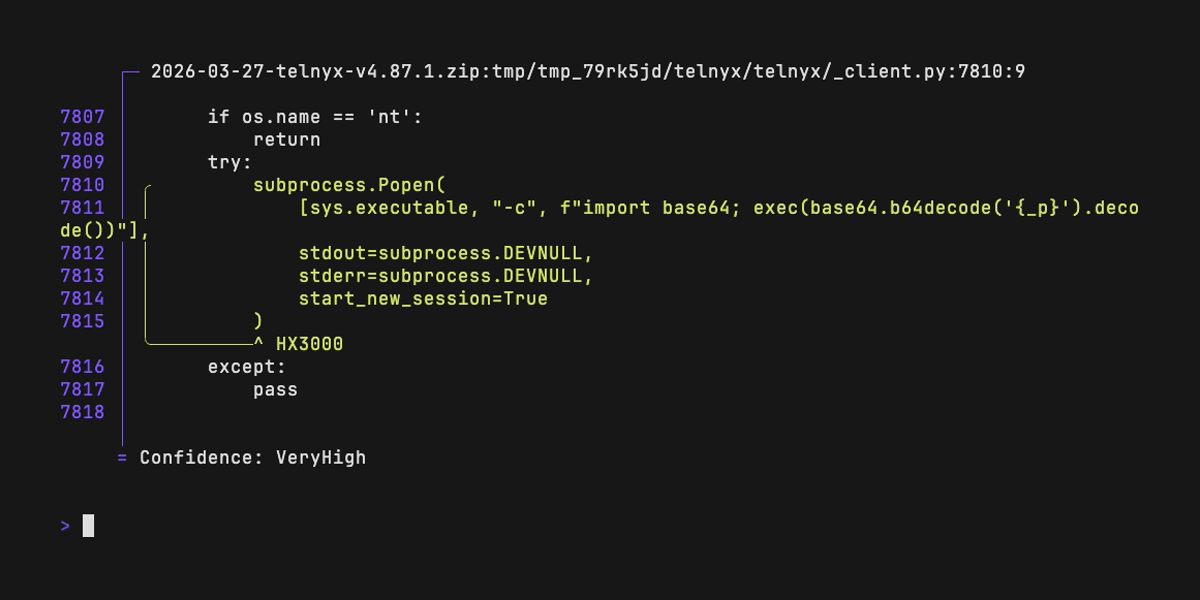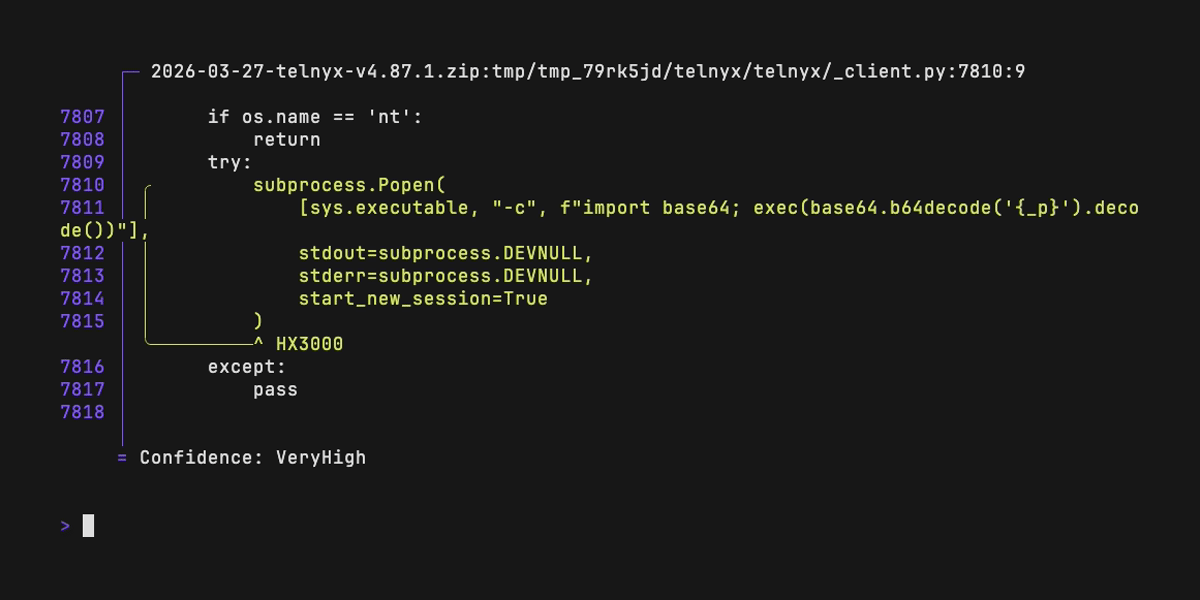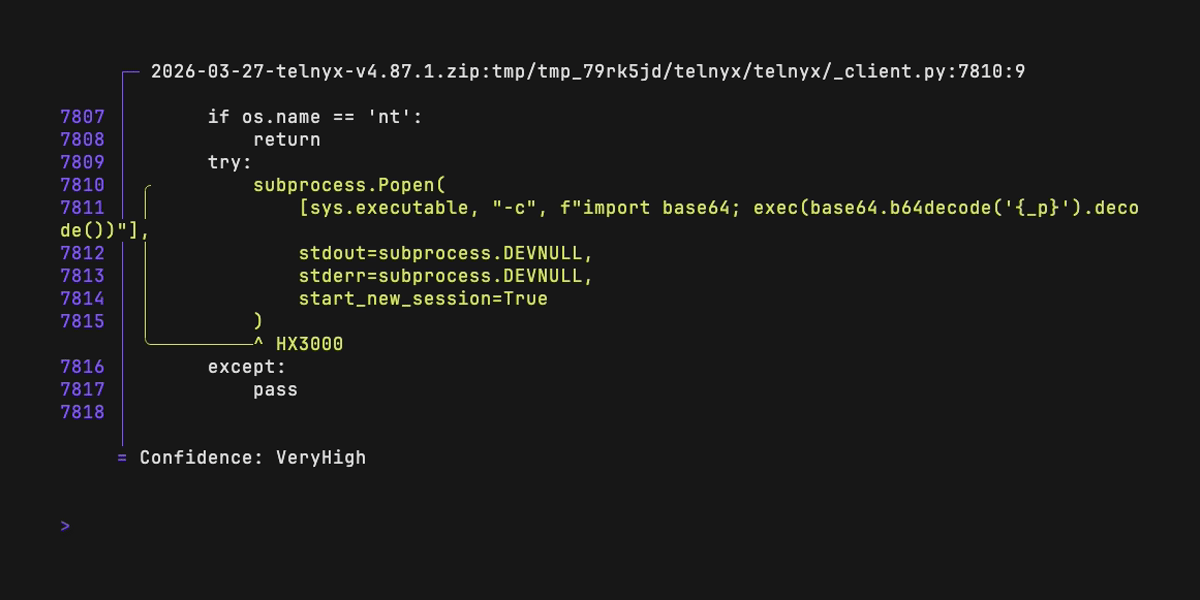 rushter/hexora
Static analysis of malicious Python code
 assafmo/xioc
Extract indicators of compromise from text, including "escaped" ones.
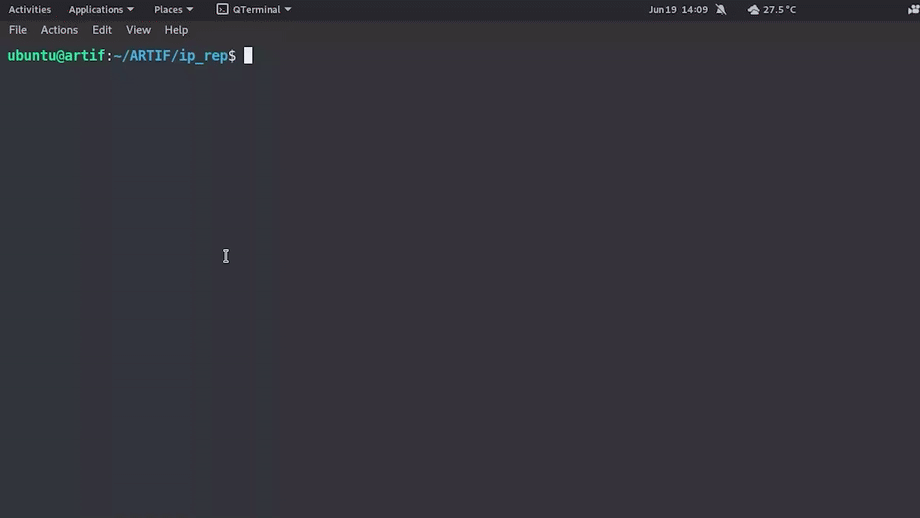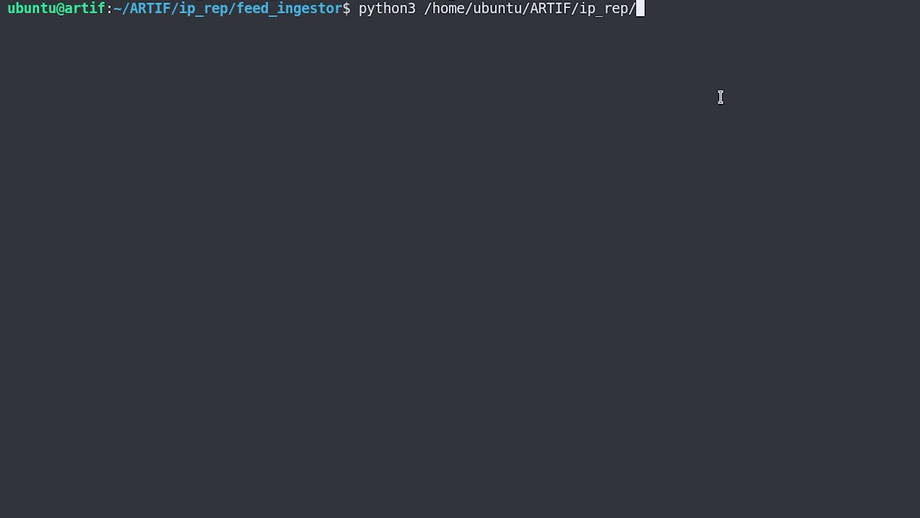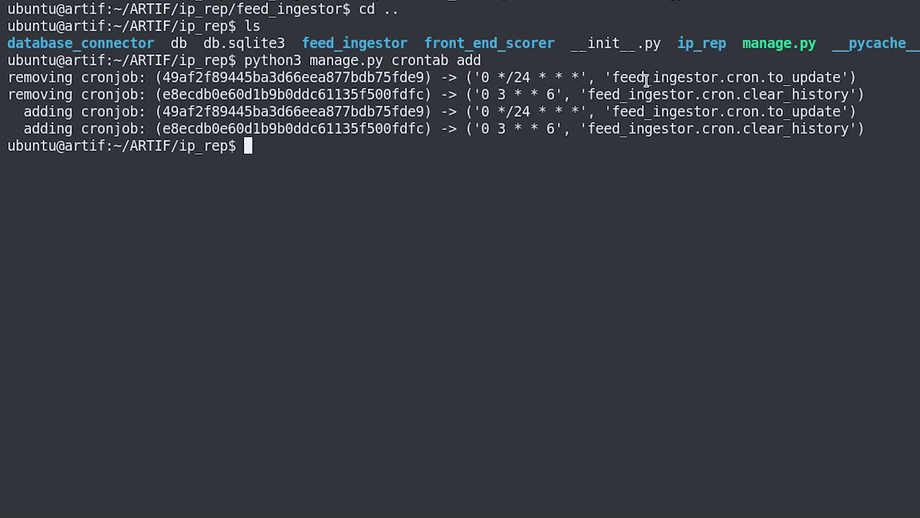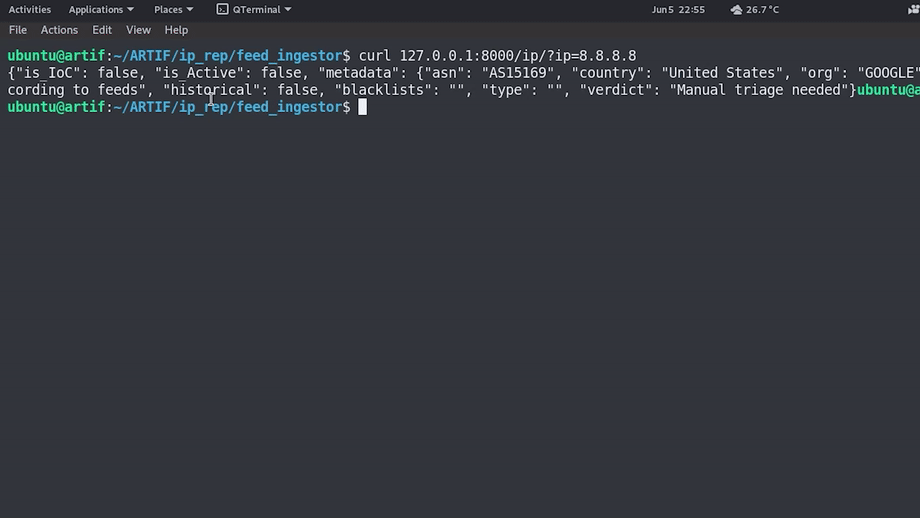 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
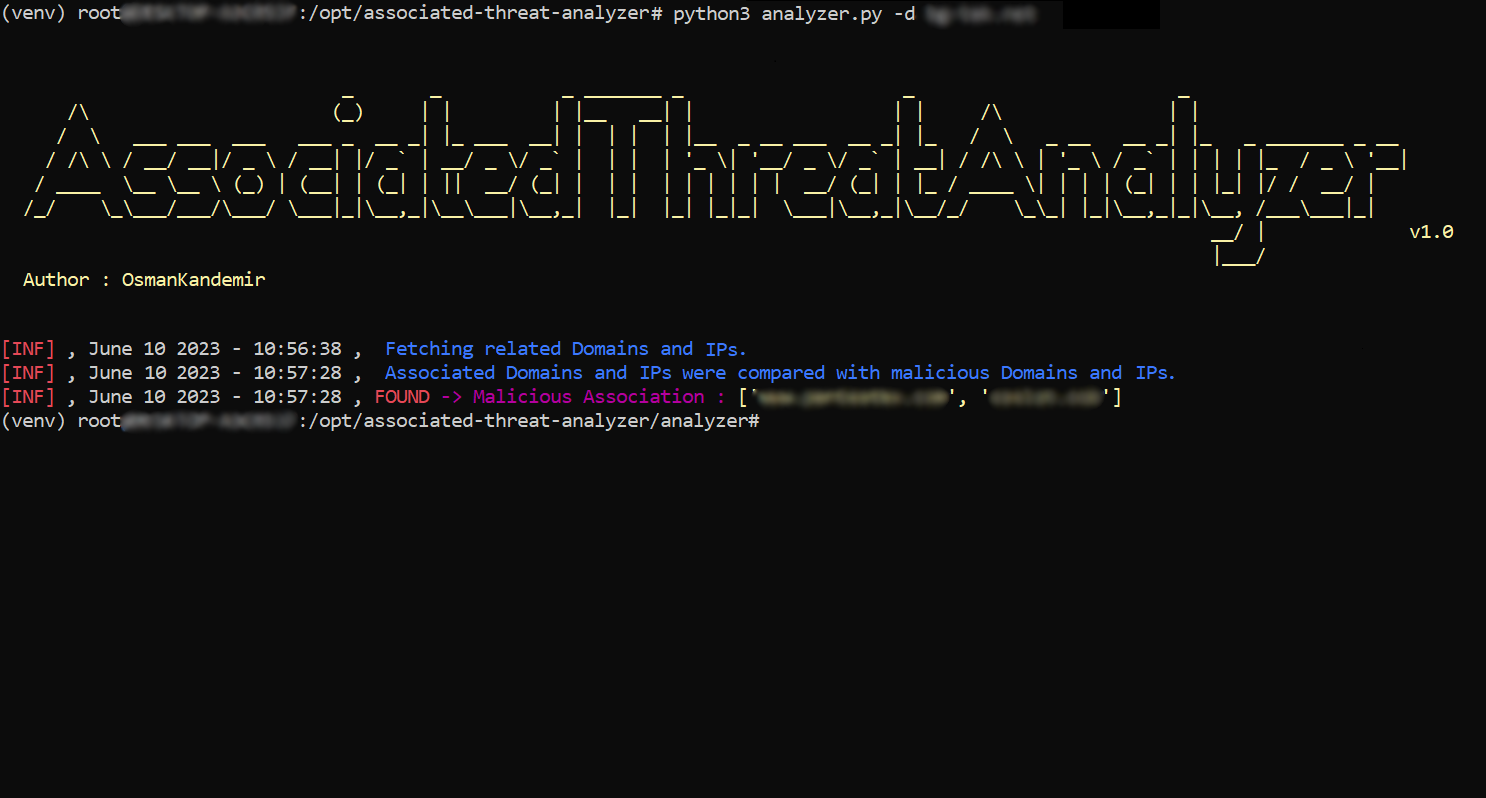 osmankandemir/associated-threat-analyzer
Detects malicious IPv4 addresses and domain names associated with a web application by comparing against local threat intelligence lists of known…