

Kage-DFIR-toolkit
 karim852/kage-dfir-toolkit
Windows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
defensive-toolsdigital-forensicsforensics+8
39
karim852/kage-dfir-toolkitWindows host DFIR triage console that chains artefact collection, Sigma-correlated timelines, YARA scans, socket and account inspection, indicator…
 aquasecurity/vuln-list-update
Automated vulnerability data aggregator that collects advisories from NVD, OSV, Alpine, Red Hat, and 20+ other sources into a unified parsable format…
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
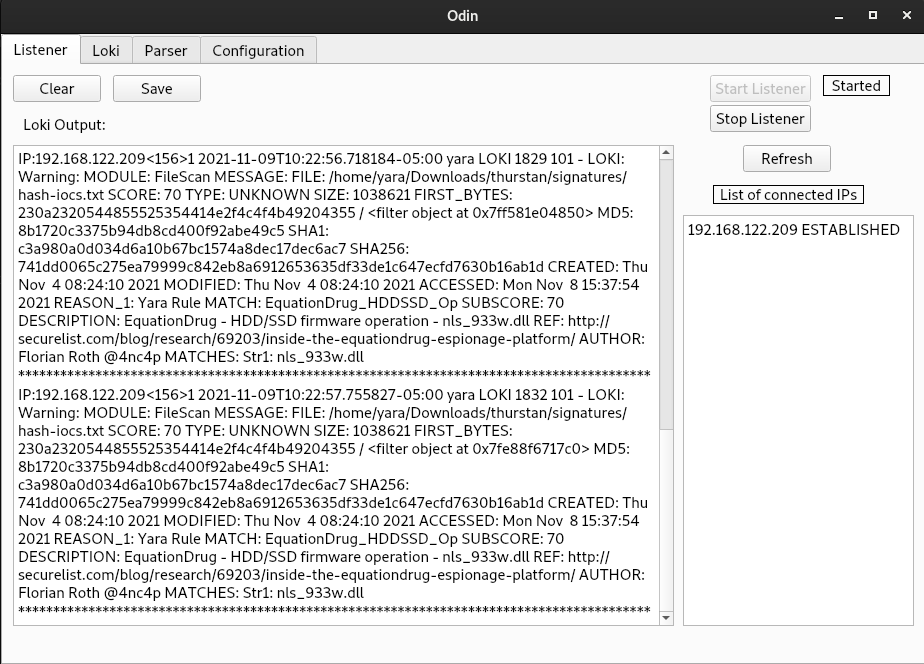 hamza-megahed/odin
Centralized IoC scanner that deploys Loki across endpoints, collects detection results, and parses logs into CSV for incident response and forensic…