
OsintCase
 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
curated-resourcesdata-recoverydigital-forensics+6
emrekybs/osintcaseAn OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
 svdwi/bluebox
Open-source threat intelligence platform for malware and observable analysis. Enriches IPs, domains, URLs, and hashes with external sources, performs…
 kadir/copy-fail-cve-2026-31431-ioc
Detection, mitigation, and IOC toolkit for Copy Fail CVE-2026-31431 Linux kernel page-cache privilege escalation
 log2timeline/plaso
Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 corelight/extendintel
This package extends the Intel package to log more fields

 hackinglz/panrapidcheck
Extract useful information from PANOS support file for CVE-2024-3400
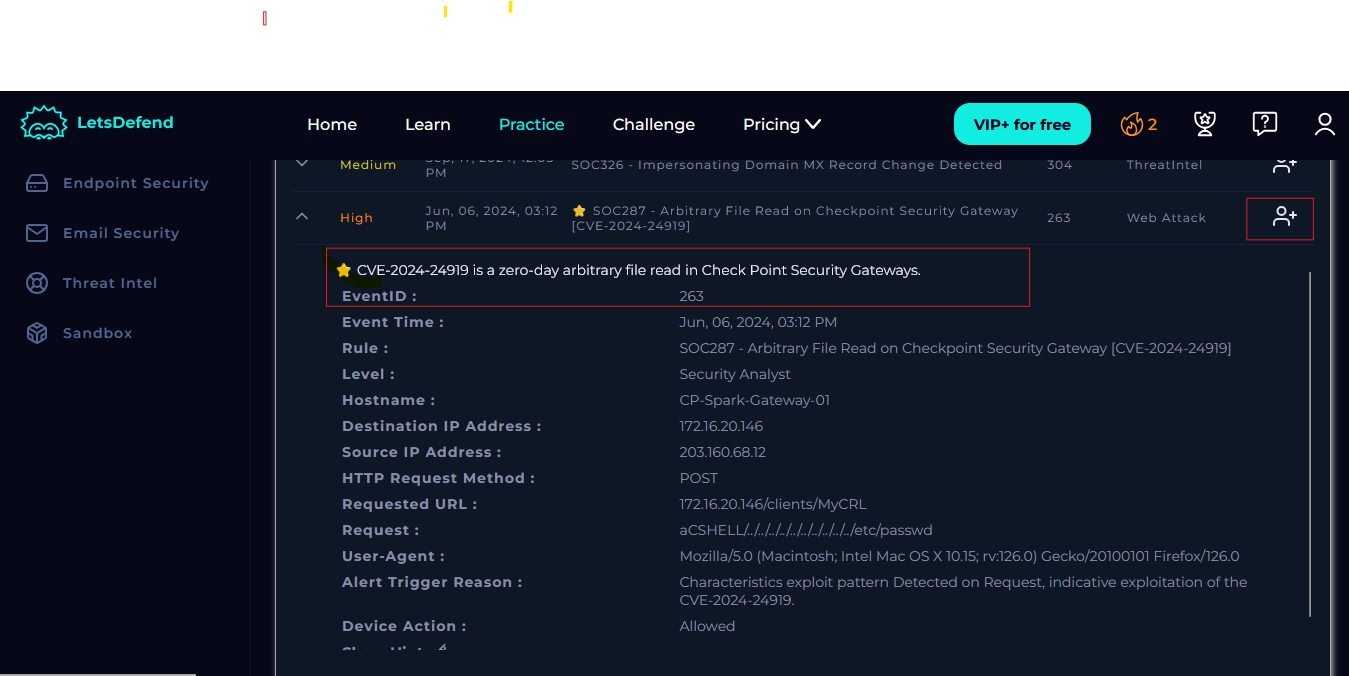 cyberbibs/event-id-263-arbitrary-file-read-on-checkpoint-security-gateway-cve-2024-24919-
Step-by-step SOC incident response walkthrough for CVE-2024-24919 arbitrary file read on Check Point gateways, covering detection, analysis,…
 vishvacyber/detection-tool-kit-for-cve-2026-31431
Layered detection toolkit for CVE-2026-31431 (Copy Fail) Linux kernel LPE. Provides eBPF, auditd, Sigma rules, page-cache diff, and IOC guides for…
 pascalasch/cve-2023-38831-kql
KQL Hunting for WinRAR CVE-2023-38831
 mrezqi/cve-2021-1675_carbonblack_huntingquery
CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.
 garethmsheldon/cve-2025-60787-detection-motioneye-rce-via-config-injection
Detection rules and YARA/KQL signatures for CVE-2025-60787, an unauthenticated RCE in motionEye via config injection, with process execution and file…
 hackinghippo/log4shell_ioc_ips
log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)
 bakedmuffinman/blacklotusdetection
Created to help detect IOCs for CVE-2022-21894: The BlackLotus campaign
 faysalferdous/cve-2025-68645-exploiting-zimbra-webmail-lfi-vulnerability
Defender-focused reference pack for CVE-2025-68645 Zimbra LFI, including Sigma/Splunk detection rules, WAF mitigation snippets, IOC patterns, and…
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…