

mvt
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
android-securitydigital-forensicsdisk-forensics+7
15.7k
mvt-project/mvtForensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 kavan00/android-projector-c2-malware
Breakdown of a c2-network of chinese beamers - SilentSDK-Analysis
 professorquantumuniverse/veto
Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…
 interplains/zero-breach-toolkit
Free, open-source, offline checks for traces of known mercenary spyware. Works on Windows, macOS and Linux, Android phones and iPhone backups.
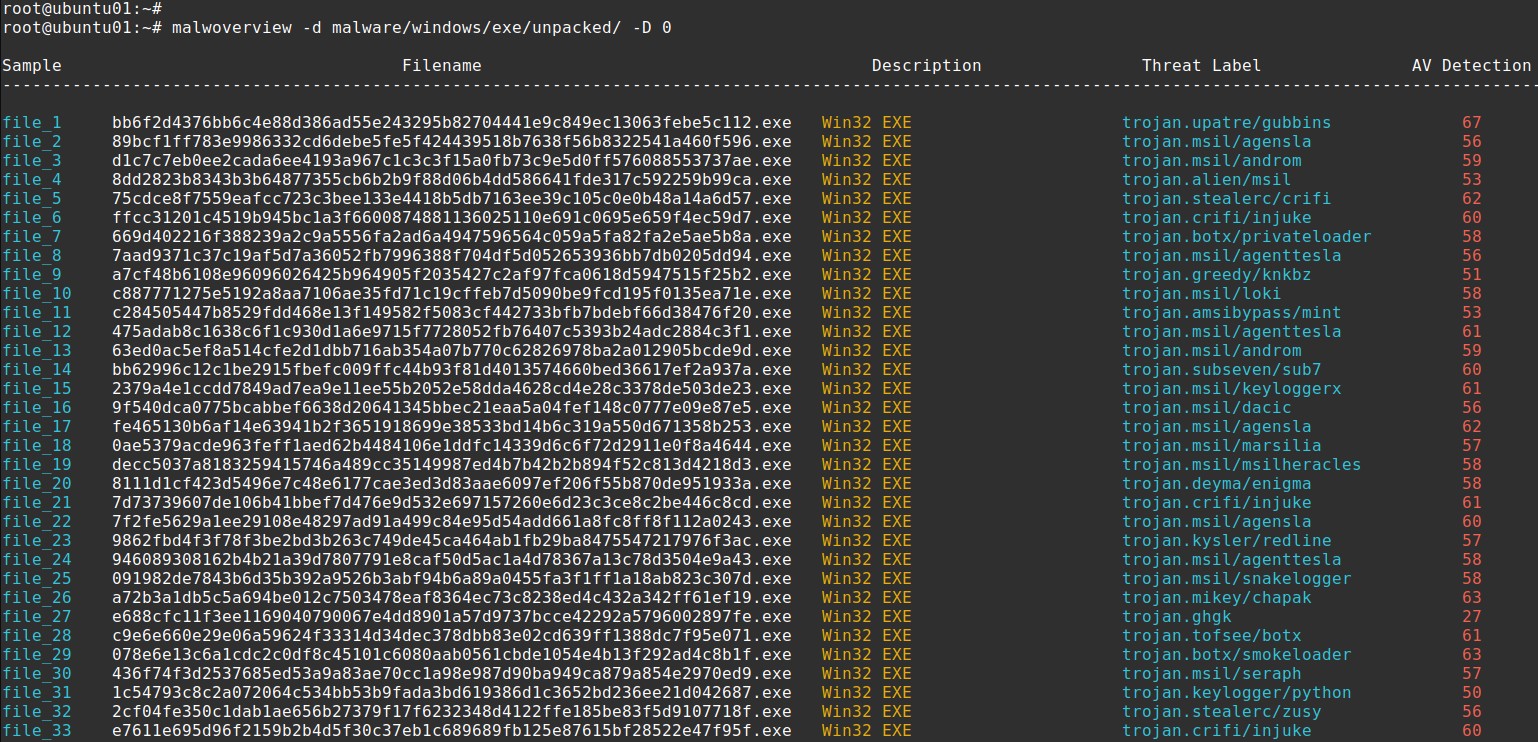 alexandreborges/malwoverview
Malwoverview is a first response tool for threat hunting across VirusTotal, Hybrid Analysis, URLHaus, Polyswarm, Malshare, Alien Vault, Malpedia,…
 0xajstrike/emsign-trust-scan
Offline scanner for the October 2026 eMudhra/emSign CA key compromise, finds affected certificates across OS trust stores, CA bundles, Java cacerts,…
 0xblackash/cve-2026-73570
Advisory and detection guidance for CVE-2026-73570, an unauthenticated OS command injection in Zimbra SNMP notification processing leading to remote…
 swaybs/cve-2024-3400
Python script to check Palo Alto firewalls for CVE-2024-3400 exploit attempts
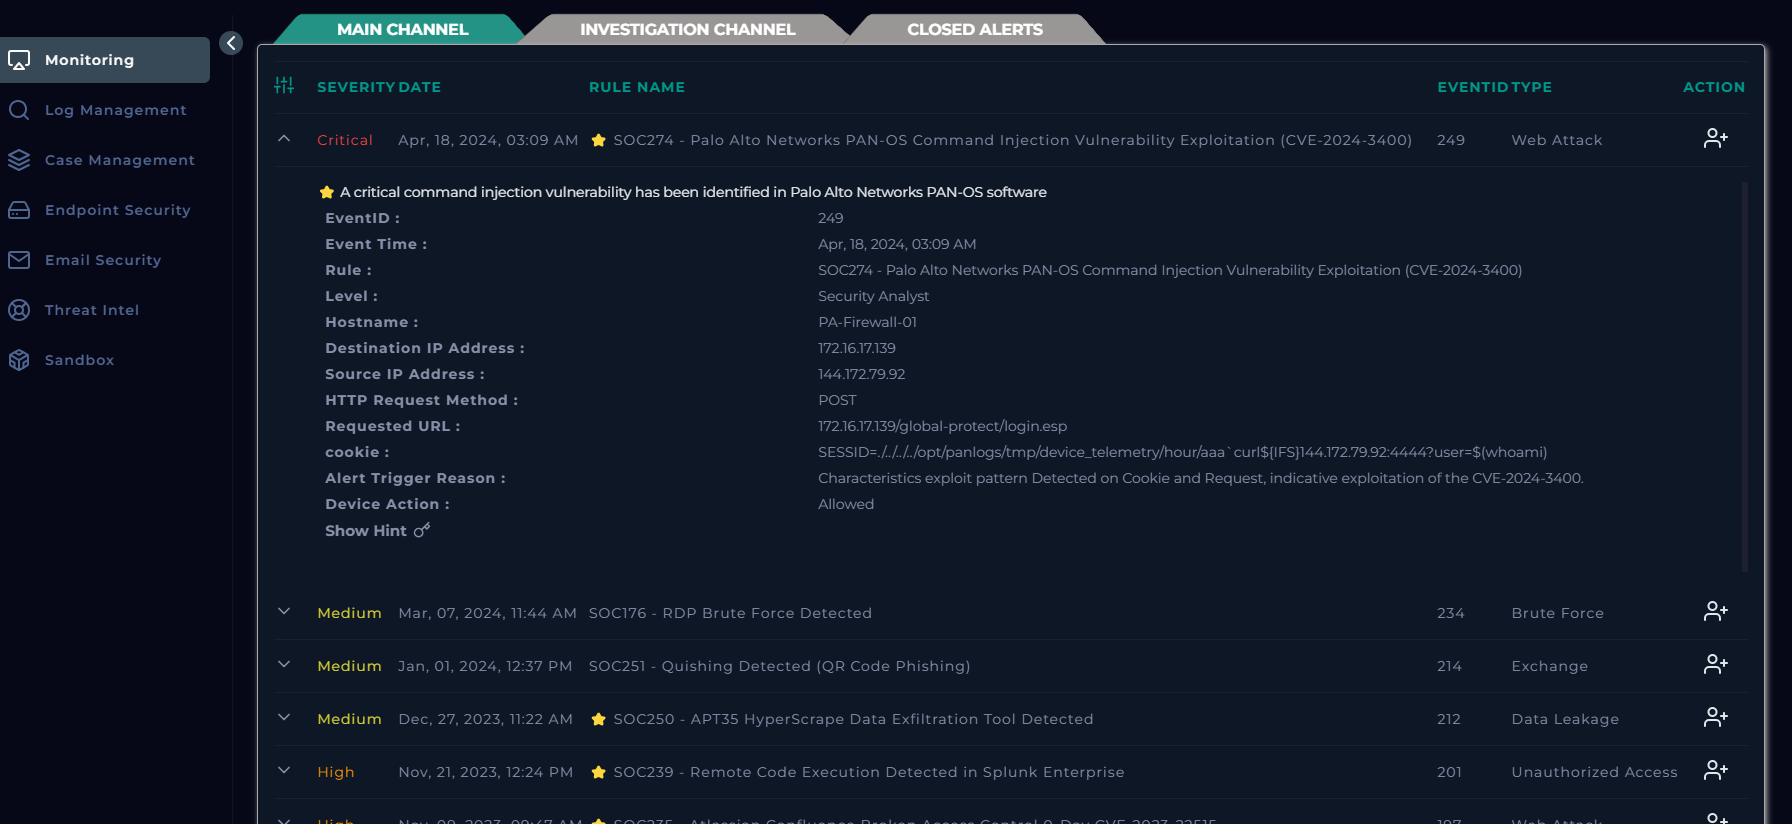 cyprianatsyor/letsdefend-cve2024-3400-case-study
Detection, analysis, and response strategies for CVE-2024-3400 exploitation attempts targeting Palo Alto PAN-OS GlobalProtect portals. Includes IOCs,…