
thrunt-god
 backbay-labs/thrunt-god
Threat hunting command system for agentic IDEs
incident-responseinformation-gatheringintrusion-detection+5
backbay-labs/thrunt-godThreat hunting command system for agentic IDEs
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 nomi-sec/nvd-database
📕NVD Database
 chaitanyakrishna/iocscraper
IOCPARSER.COM is a Fast and Reliable service that enables you to extract IOCs and intelligence from different data sources.
 cloudflare/exim-cve-2019-10149-data
Curated dataset of IPs, ASNs, and SMTP banners for Exim CVE-2019-10149, with linked advisories and threat actor intelligence for vulnerability…
 abhinavbom/threat-intelligence-hunter
TIH is an intelligence tool that helps you in searching for IOCs across multiple openly available security feeds and some well known APIs. The idea…
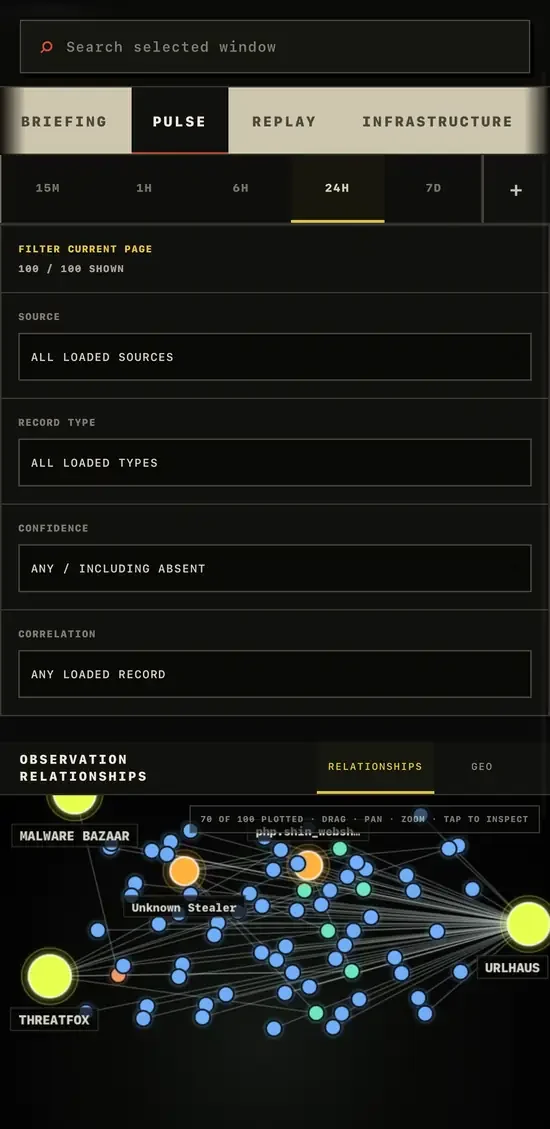
 gnomeman/badbanana-threat-observatory
Threat intel observatory aggregating CISA KEV, ThreatFox, URLhaus, and MalwareBazaar feeds with search, change tracking, and STIX/CSV/JSONL export.
 expel-io/expel-intel
This is the home of the Expel Intel Team. Here, we will share IOCs and other information that is either not suitable for fitting into other mediums…
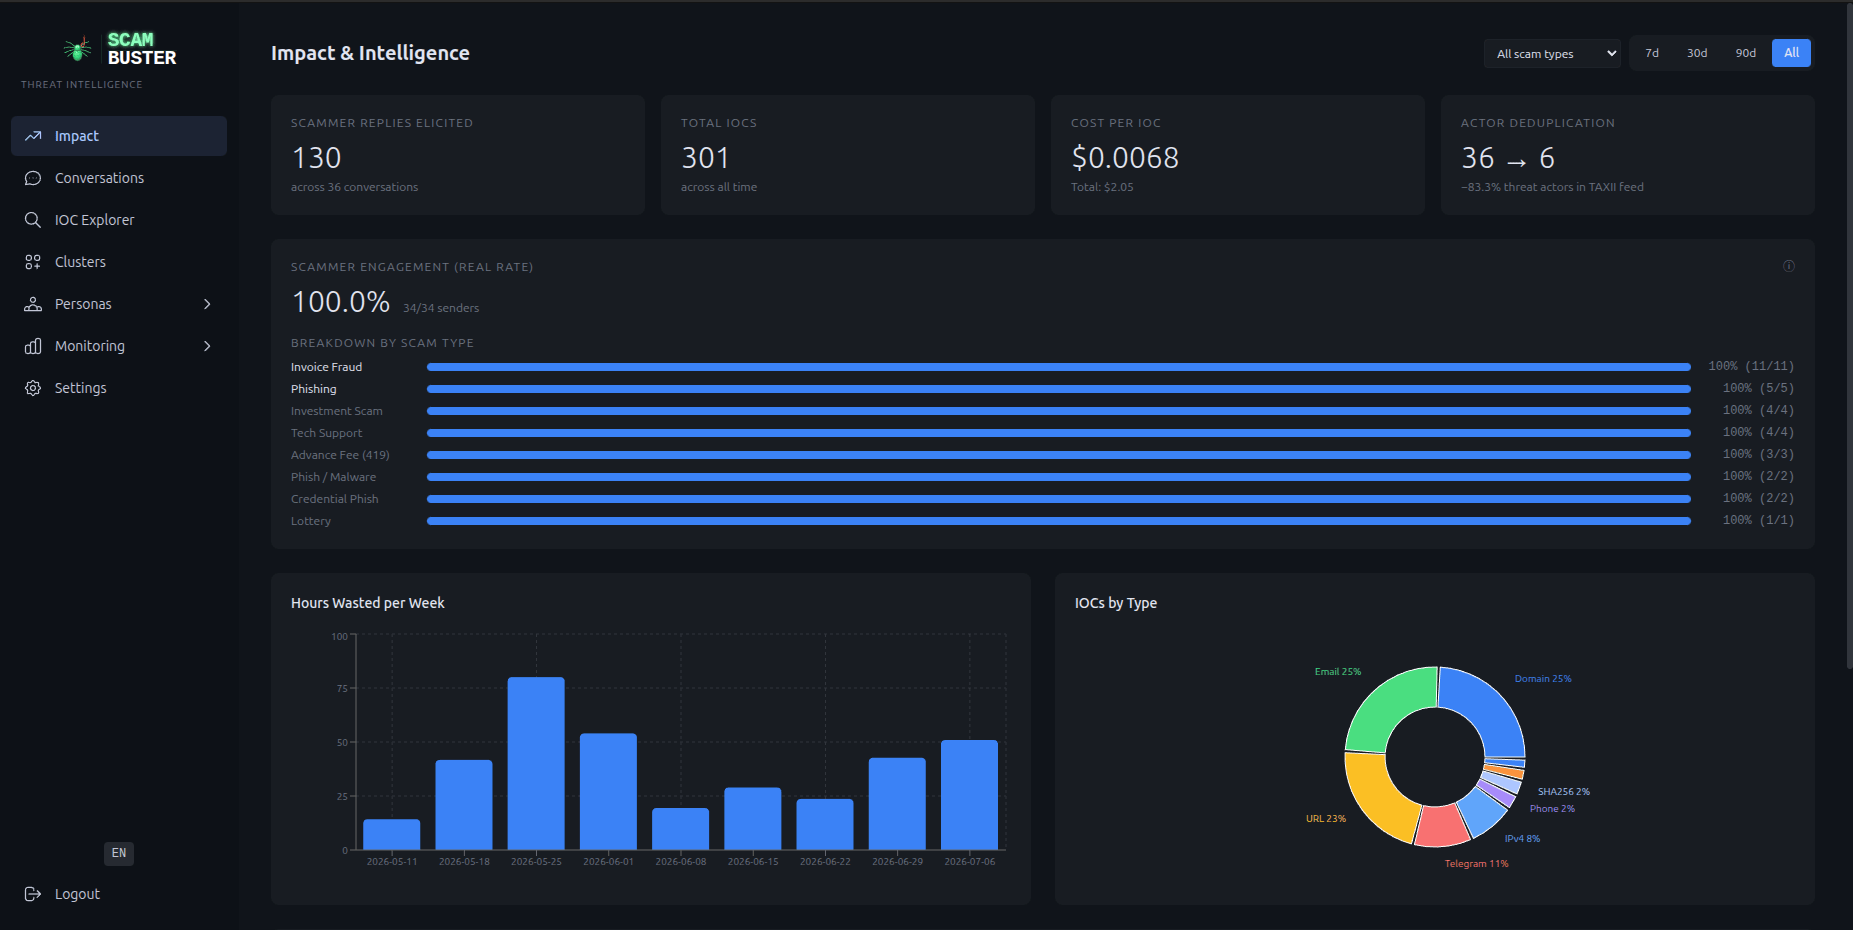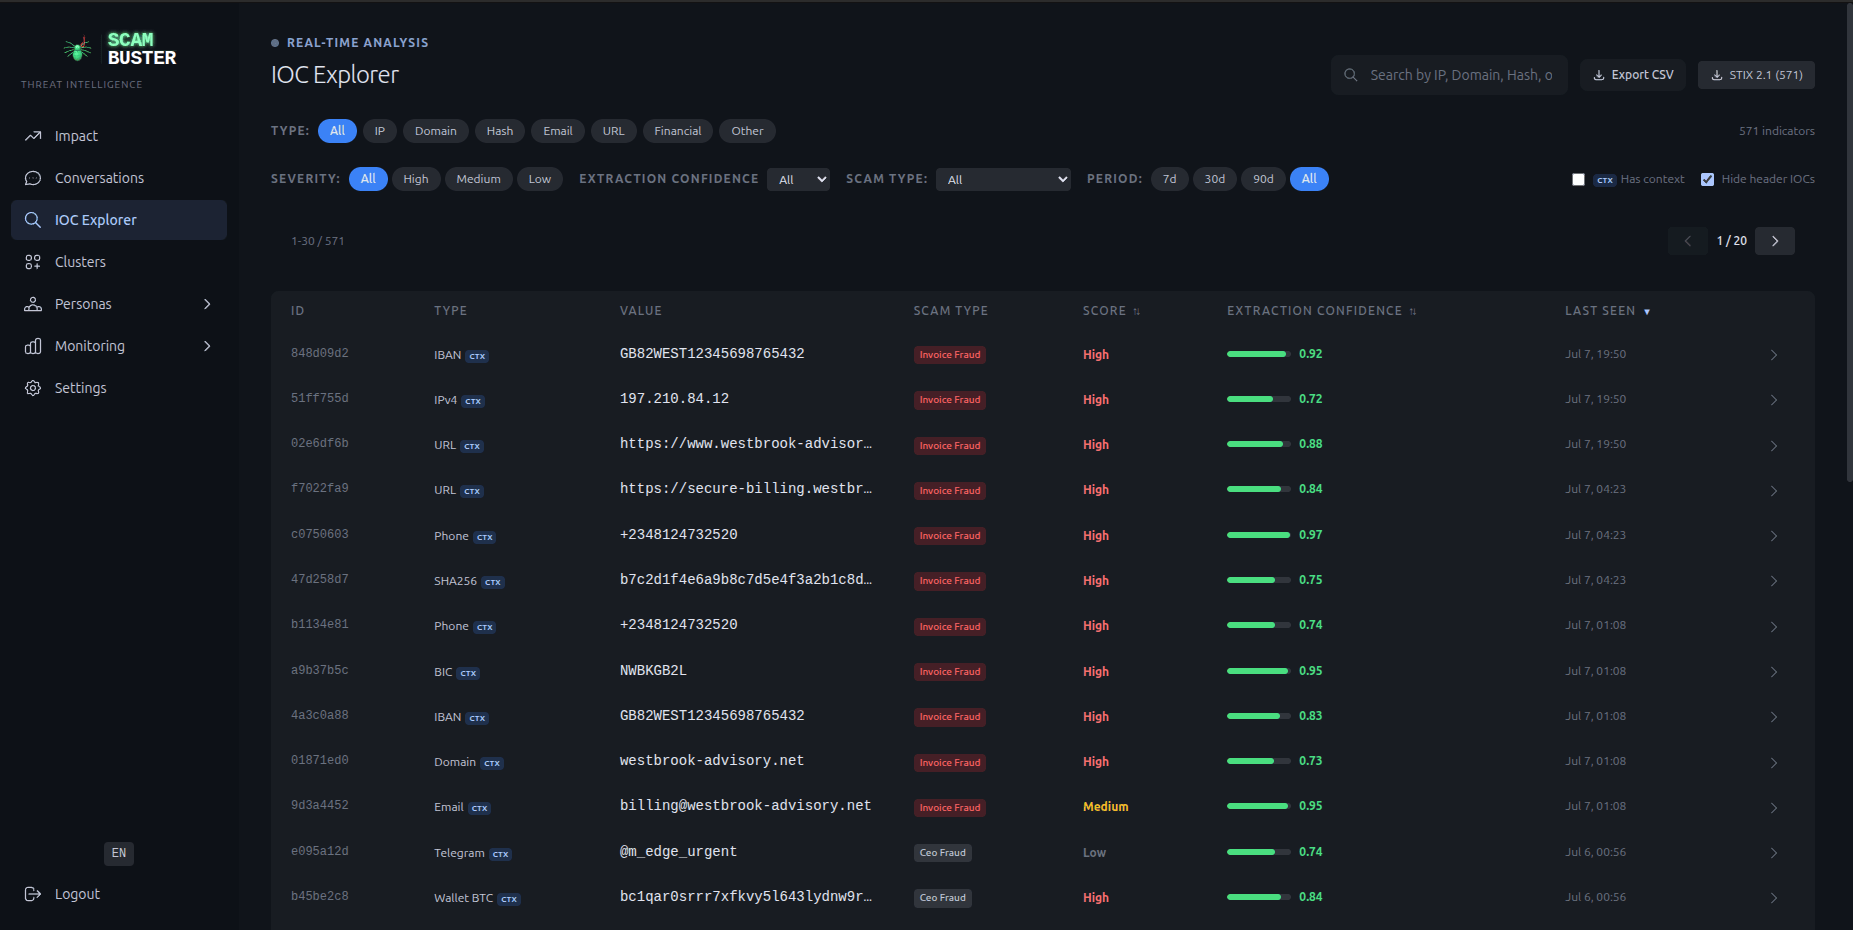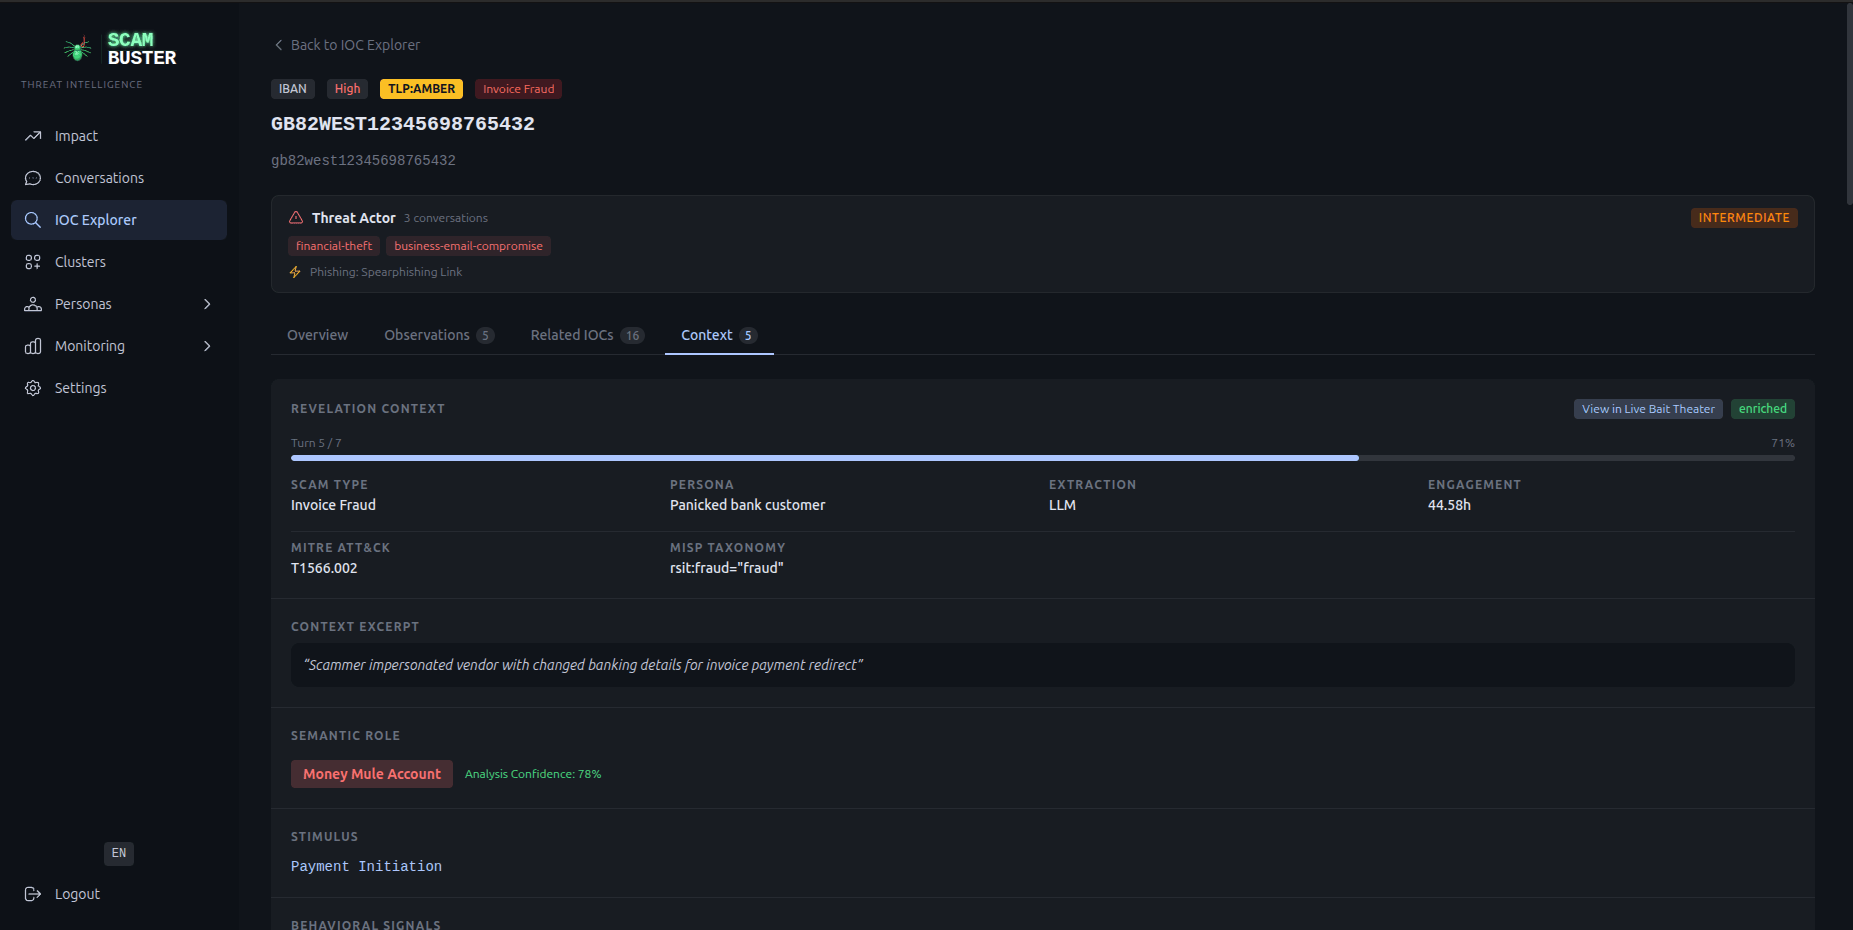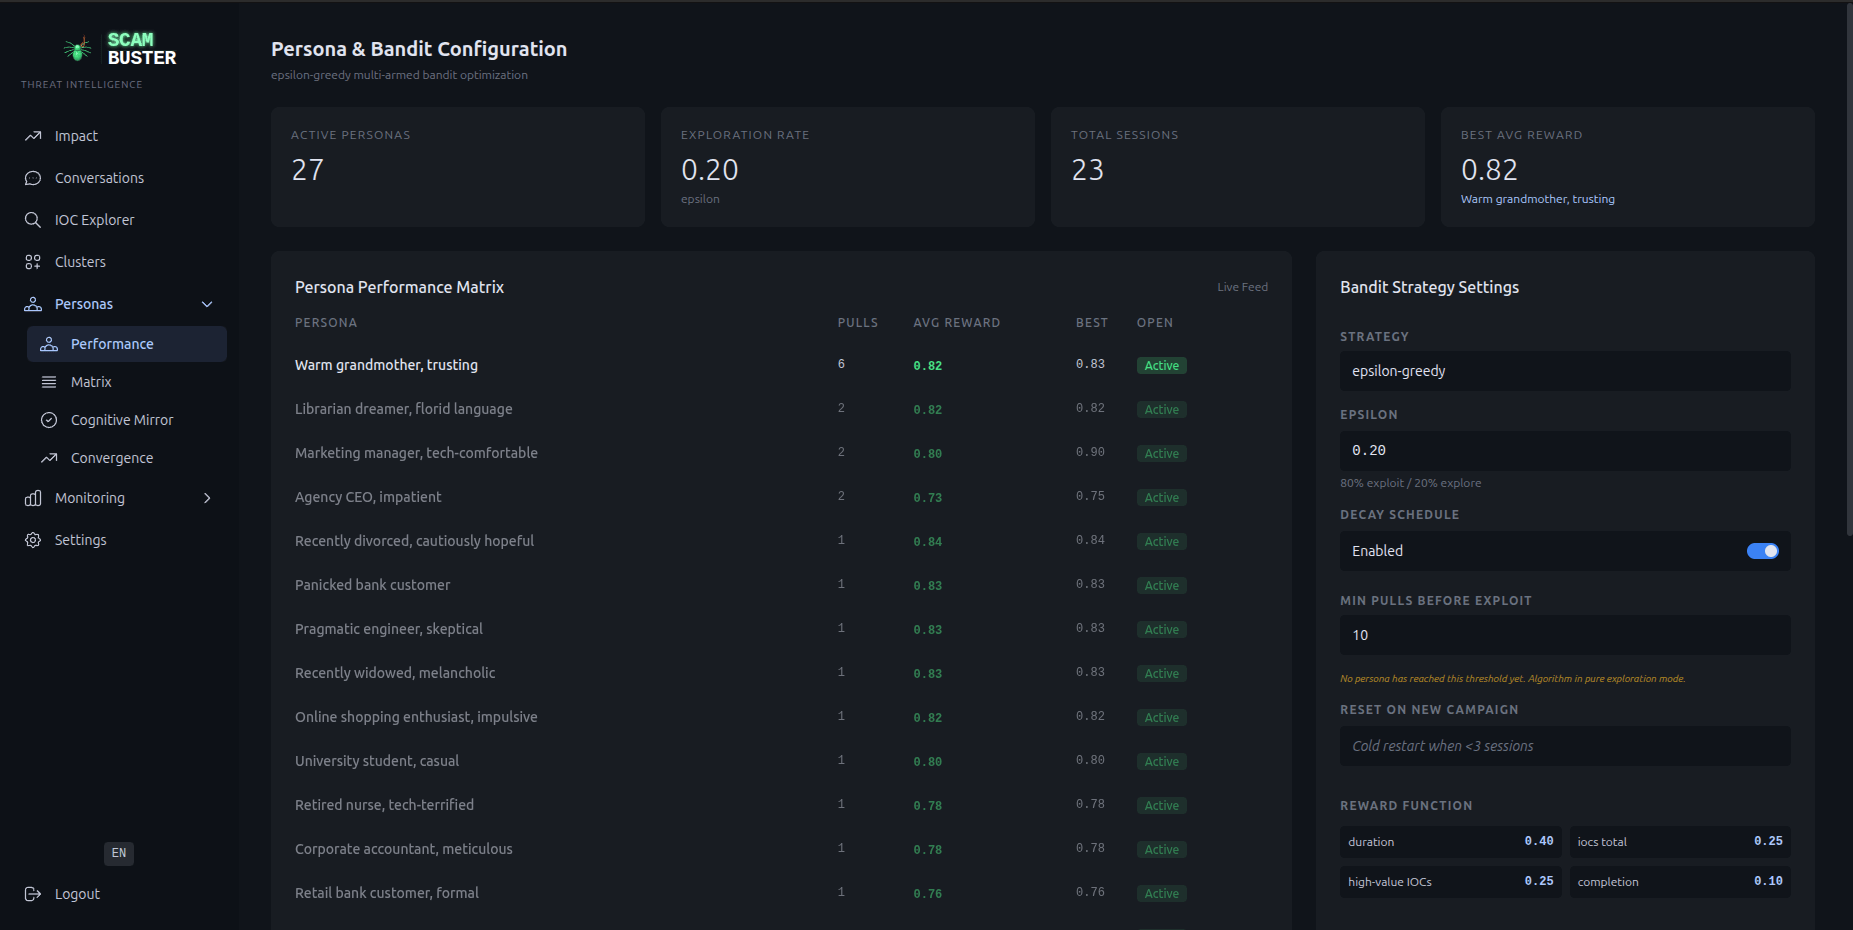 laugiov/scambuster
Defensive engagement & threat intelligence research laboratory. Converts inbound scam emails into actionable IOCs through controlled, policy-driven…
 cve-search/cve-search
Local CVE/CPE vulnerability database with search, ranking, web interface, and API for offline vulnerability analysis and management.
 pedramamini/threatingestor
Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
 hackinghippo/log4shell_ioc_ips
log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)
 guardicode/cve-2021-44228_iocs
Curated collection of public Indicators of Compromise (IoCs) for the Log4j vulnerability (CVE-2021-44228), aggregated from multiple sources for…
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 rastrea2r/rastrea2r
Collecting & Hunting for IOCs with gusto and style
 360netlab/dga
Suspicious DGA from PDNS and Sandbox.
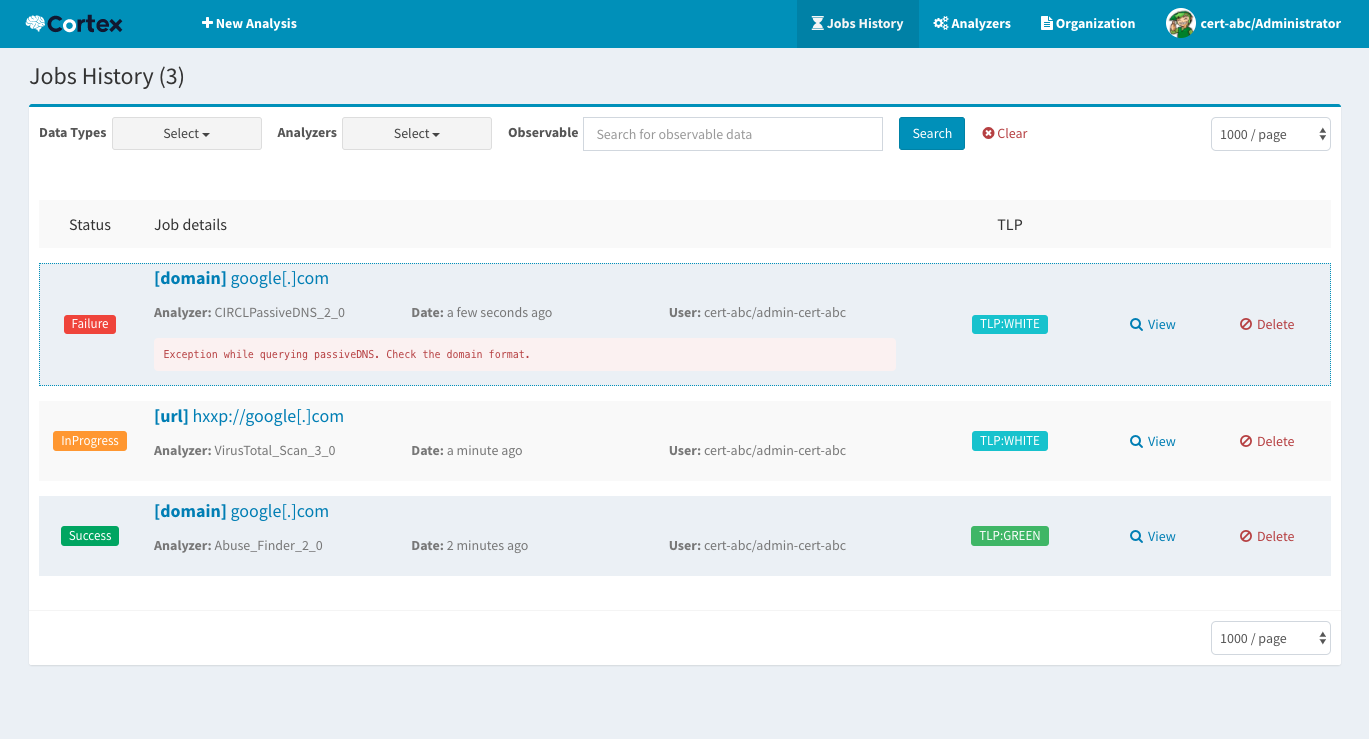 thehive-project/cortex
Cortex: a Powerful Observable Analysis and Active Response Engine
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.