

misp-galaxy
 misp/misp-galaxy
Clusters and elements to attach to MISP events or attributes (like threat actors)
adversarial-attackcurated-resourcesioc-management+5
6501 day ago
misp/misp-galaxyClusters and elements to attach to MISP events or attributes (like threat actors)
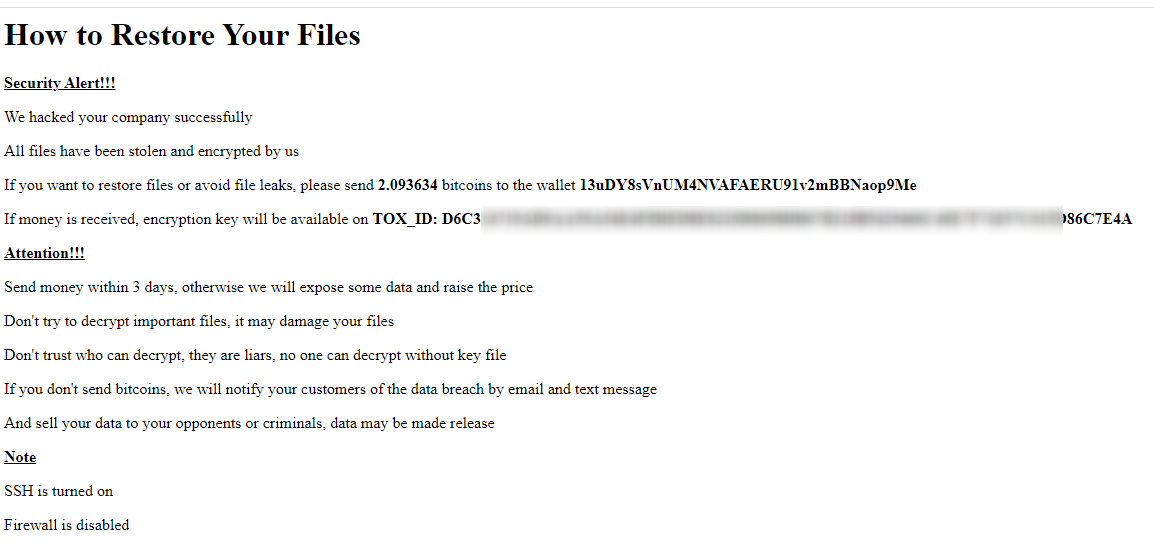 soufianetahiri/esxi_ransomware_bitcoinwallets
ESXi semi-automated ransomware attacks bitcoin wallets
 misp/misp-taxonomies
Taxonomies used in MISP taxonomy system and can be used by other information sharing tool.
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 eris-ths/supply-chain-guard
Detect, assess, and respond to supply chain attacks across npm/yarn and Python (pip/poetry/uv). Claude Code skill + standalone scripts. Built during…
 rapticore/orenpmguard
Defense Against the Shai-Hulud Supply Chain Attack
 hahasagined/cve-2024-3400
External Dynamic List (EDL) of IP addresses actively exploiting CVE-2024-3400, for use in firewall and SIEM blocklists to defend against ongoing…
 binarly-io/supplychainattacks
Curated repository of documented firmware supply chain attacks, featuring IoCs, detection tools, and references to help defenders understand and…
 fastfire/ioc_attack_esxi_feb_2023
Collection of IoCs available and related to attacks on ESXi infrastructures that occurred as of Friday February 3, 2023.
 digi4care/shai-scan
Zero-dependency CLI scanner for npm/PyPI supply chain compromises. Detects compromised packages in lockfiles and system-level IOCs from attacks like…
 respondiq/jsp-webshell-scanner
🔍 A simple Bash script to detect malicious JSP webshells, including those used in exploits of SAP NetWeaver CVE-2025-31324.
 bakedmuffinman/blacklotusdetection
Created to help detect IOCs for CVE-2022-21894: The BlackLotus campaign
 zephrfish/cve-2025-53770-scanner
ToolShell scanner - CVE-2025-53770 and detection information
 reddrip7/log4shell_cve-2021-44228_related_attacks_iocs
Curated repository of Indicators of Compromise (IOCs), attack source IPs, and Snort/Suricata detection rules for Log4Shell (CVE-2021-44228) attacks.
 b401/clickstudio-compromised-certificate
Repository containing the compromised certificate seen in recent CVE-2022-30190 (Follina) attacks.