

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
30 results
c2detect preview

c2detect

GitHubcognis-digital/c2detect

C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel

command-and-controldefensive-toolsfingerprint-spoofing+8
43
1 month ago
Open-Source-Threat-Intel-Feeds preview

Open-Source-Threat-Intel-Feeds

GitHubbert-janp/open-source-threat-intel-feeds

This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…

intrusion-detectionioc-managementnetwork-security+3
96819h 32m ago
Loki preview

Loki

GitHubneo23x0/loki

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
anomaly-detectiondigital-forensicsdisk-forensics+11
3.8k9 months ago
Tourmaline preview

Tourmaline

GitHubv-pun215/tourmaline

Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…

command-and-controlcryptographydigital-forensics+7
111 month ago
C2IntelFeeds preview

C2IntelFeeds

GitHubdrb-ra/c2intelfeeds

Automatically generated C2 threat intelligence feeds of IPs, domains, URL paths, and implant configuration metadata, derived from internet scanning…

command-and-controldefensive-toolsincident-response+6
7463 days ago
rust-deobf preview

rust-deobf

GitHubvahpem/rust-deobf

Recover what obfuscation hides in Rust binaries (strings, crates, library functions, flattened control flow) via static analysis + Unicorn emulation,…

ai-assisted-reversingbinary-analysisdynamic-analysis-sandboxing+6
44 days ago
PolinRider preview

PolinRider

GitHubopensourcemalware/polinrider

Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…

code-analysiscurated-resourceseducation+8
1033 months ago
Overlord-RAT-Reverse-Engineering-a-Go-Based-RAT-Injection-Keylogging-C2-Exfiltration-Analysis preview

Overlord-RAT-Reverse-Engineering-a-Go-Based-RAT-Injection-Keylogging-C2-Exfiltration-Analysis

GitHubkaandemir993/overlord-rat-reverse-engineering-a-go-based-rat-injection-keylogging-c2-exfiltration-analysis

Full static & memory analysis of Overlord RAT: Go agent architecture, HTTP/2 + WebSocket C2, reflective DLL injection, browser keylogging, and IOCs.…
command-and-controldata-exfiltrationdigital-forensics+6
920 days ago
C2-Tracker preview
Archived

C2-Tracker

GitHubmontysecurity/c2-tracker

Live Feed of C2 servers, tools, and botnets
command-and-controlinformation-gatheringioc-management+5
7846 months ago
PayloadAutomation preview

PayloadAutomation

GitHubemcghee/payloadautomation

Automates Cobalt Strike payload development, testing, and deployment via a Python-to-Sleep bridge; includes artifact inspection, IoC tracking, and…
command-and-controlioc-managementpayload-development+3
1184 years ago
livewire-honeypot preview

livewire-honeypot

GitHubhelgesverre/livewire-honeypot

High-interaction honeypot mimicking a vulnerable Laravel/Livewire app. Captures RCE exploits and webshells targeting CVE-2024-47823, CVE-2025-54068,…
command-and-controldynamic-analysis-sandboxingexploitation+6
75 months ago
sleep_python_bridge preview

sleep_python_bridge

GitHubcobalt-strike/sleep_python_bridge

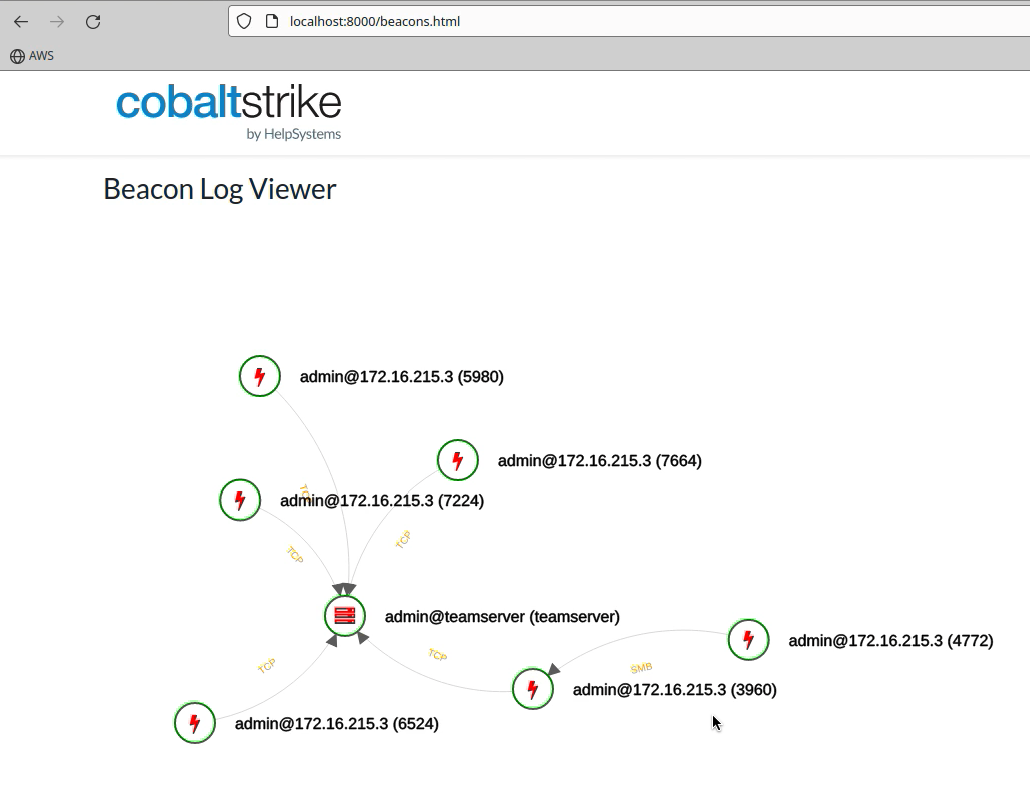
This project is 'bridge' between the sleep and python language. It allows the control of a Cobalt Strike teamserver through python without the need…
command-and-controlioc-managementlog-analysis+3
1881 year ago
hyperhives-macos-infostealer-analysis preview

hyperhives-macos-infostealer-analysis

GitHubdarksp33d/hyperhives-macos-infostealer-analysis

Full static analysis of HyperHives macOS Rust infostealer — 571 decrypted config values, C2 infrastructure, DPRK/Contagious Interview attribution,…
curated-resourceseducationforensics+6
336 months ago
DesckVB-RAT preview

DesckVB-RAT

GitHubshadowopcode/desckvb-rat

Full analysis of a never documented before Remote Access Trojan linked to Pjoao1578 toolchain

command-and-controldigital-forensicseducation+8
108 months ago
tanstack-compromise-checker preview

tanstack-compromise-checker

GitHubry-allan/tanstack-compromise-checker

Detects CVE-2026-45321 (TanStack supply chain compromise) and Mini Shai-Hulud worm artifacts. Scans node_modules, lockfiles, persistence hooks…

command-and-controlforensicsincident-response+6
5 months ago
Qakbot preview

Qakbot

GitHubpr0xylife/qakbot
command-and-controlioc-managementmalware-analysis+3
1912 years ago
OpenWire-CVE-2023-46604-Investigation preview

OpenWire-CVE-2023-46604-Investigation

GitHubaelshimony-cloud/openwire-cve-2023-46604-investigation

Incident response walkthrough analyzing CVE-2023-46604 exploitation of Apache ActiveMQ via OpenWire, including PCAP analysis, IOC identification, and…
command-and-controldigital-forensicsexploitation+7
4 months ago
ThreatKB preview

ThreatKB

GitHubinquest/threatkb

Knowledge base workflow management for YARA rules and C2 artifacts (IP, DNS, SSL) (ALPHA STATE AT THE MOMENT)

information-gatheringioc-managementmalware-analysis+2
1047 months ago
Previous12Next