
ToolShell-Honeypot
 bitsalv/toolshell-honeypot
Honeypot for CVE-2025-53770 aka ToolShell
incident-responseintrusion-detectionioc-management+5
bitsalv/toolshell-honeypotHoneypot for CVE-2025-53770 aka ToolShell
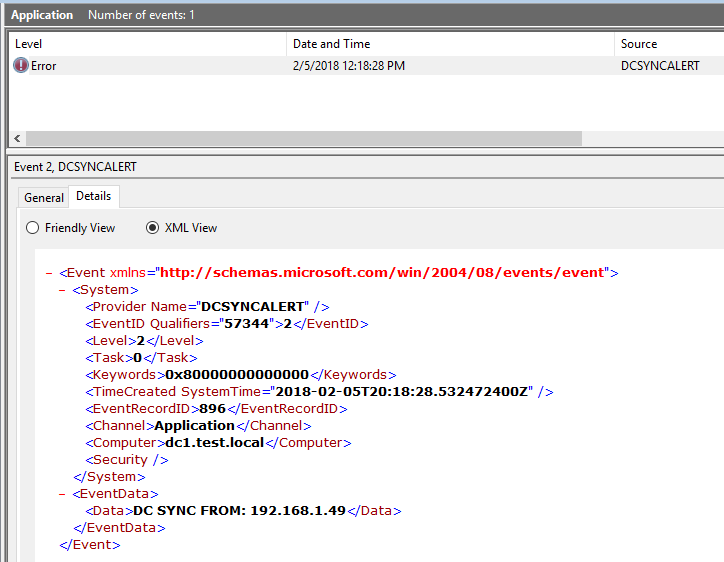 shellster/dcsyncmonitor
Monitors for DCSYNC and DCSHADOW attacks and create custom Windows Events for these events.
 cybereason-public/owlsm
Sigma Rules Engine inside the Linux Kernel using eBPF. Focusing on prevention capabilities
 andreicscs/honeywire
Open-source deception platform that turns any Linux machine into a high-signal canary. Deploy tripwire sensors on files, ports, and network services…
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
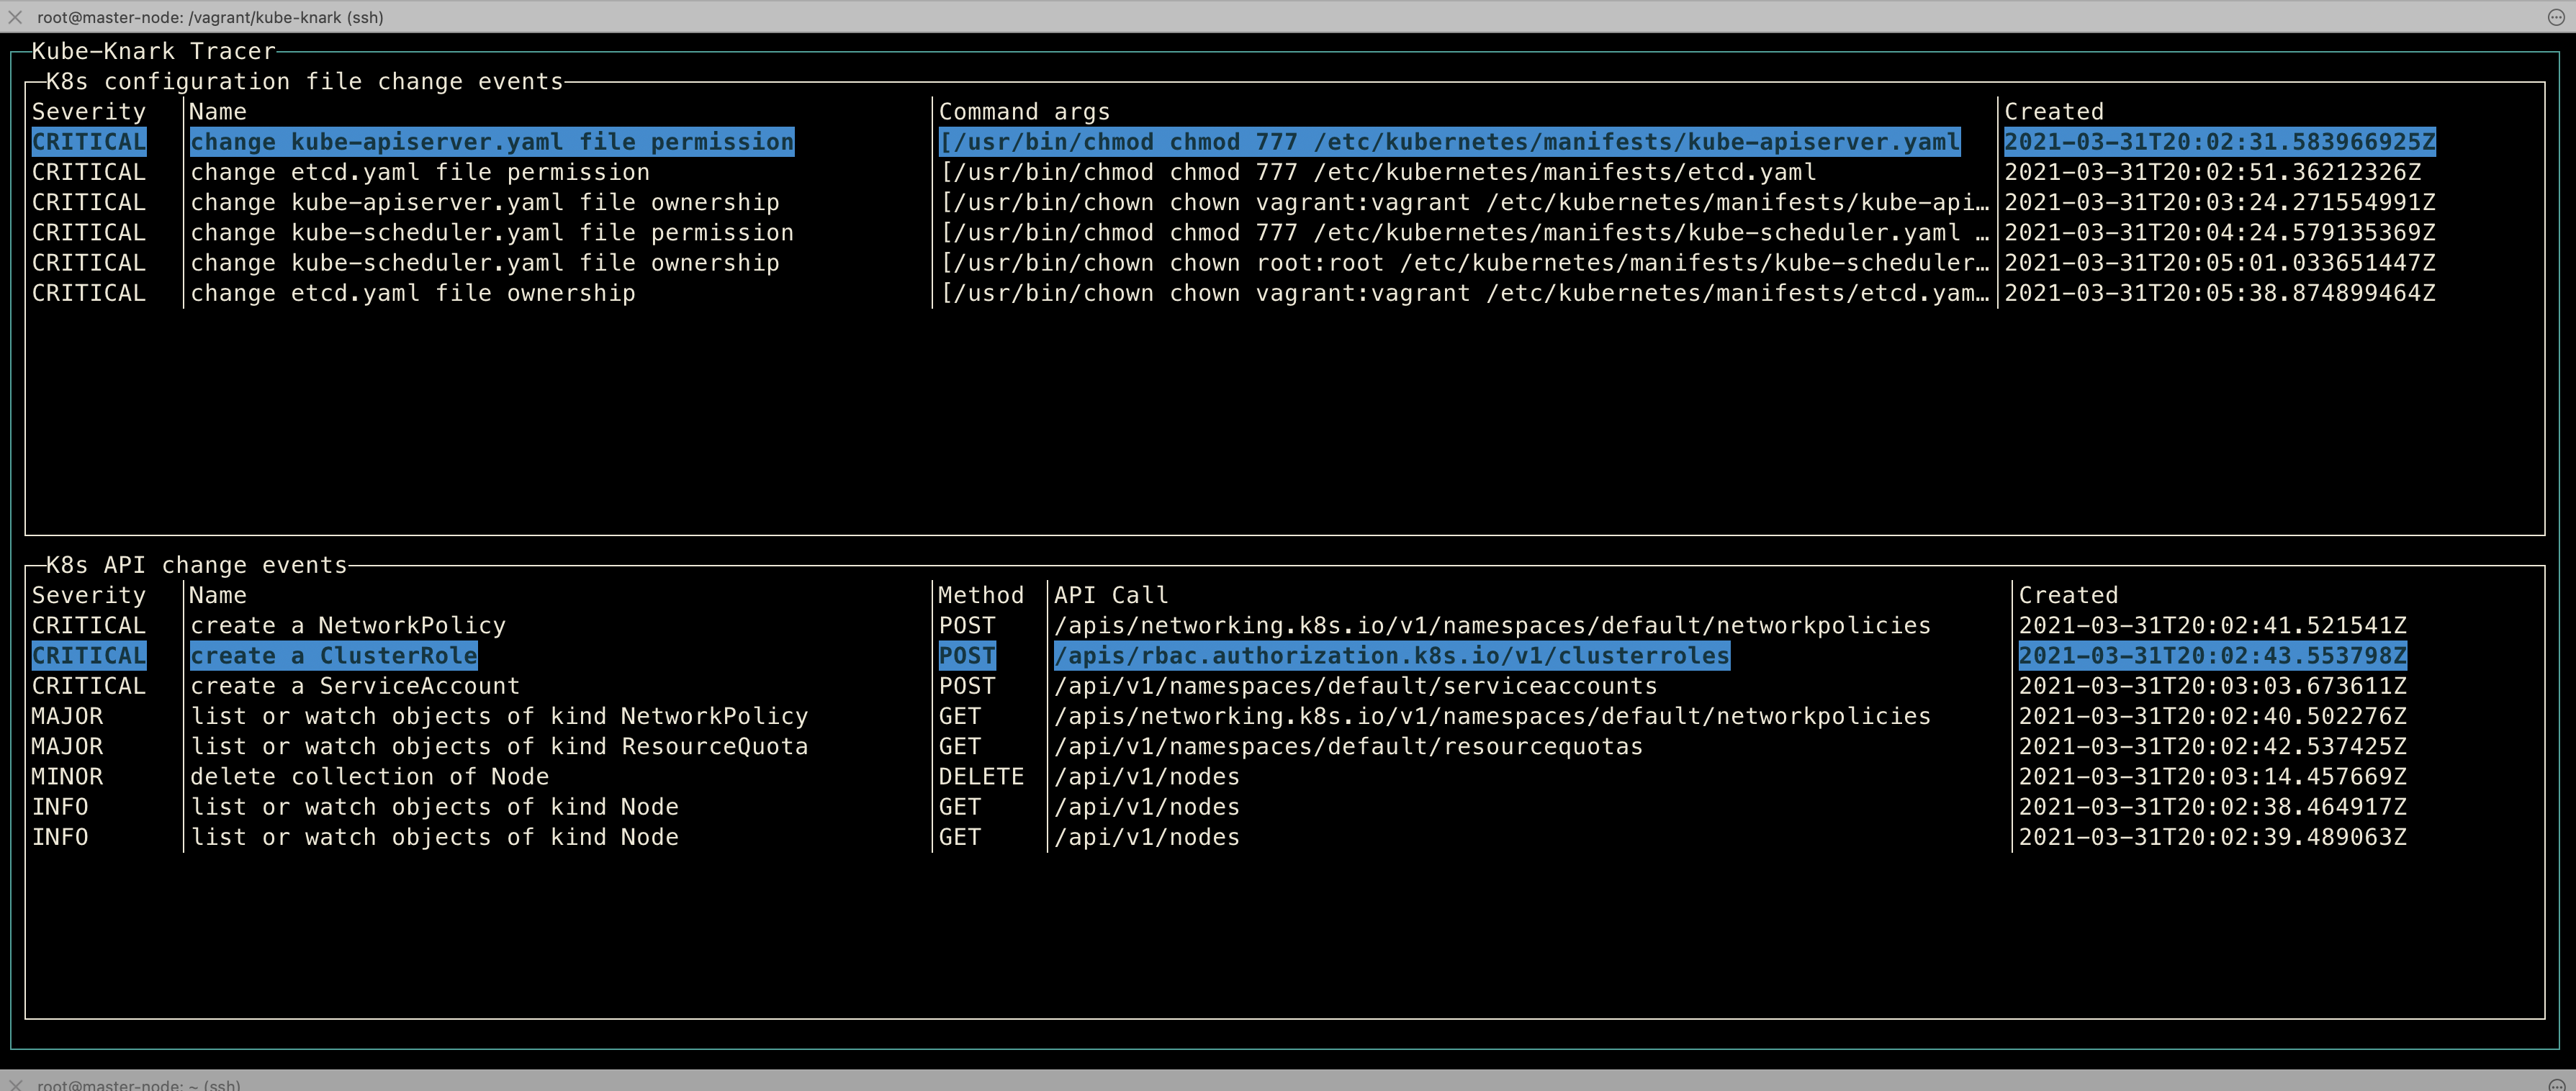 chen-keinan/kube-knark
Open Source runtime tool which help to detect malware code execution and run time mis-configuration change on a kubernetes cluster
 nabhan-mohy/dirty-frag-research-cve-2026-43284-
Comprehensive technical research on CVE-2026-43284 (Dirty Frag), including Linux kernel internals, root cause analysis, patch analysis, detection…
 devopstoday11/tarian
Anti-Virus for K8s. Protect your Applications running on Kubernetes from malicious attacks with pre-registered source code, runtime processes…
 cr0nx/awesome-linux-attack-forensics-purplelabs
This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.
 binarydefense/log4j-honeypot-flask
Internal network honeypot for detecting if an attacker or insider threat scans your network for log4j CVE-2021-44228
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
 thinkst/canarytokens-docker
Docker configuration to quickly setup your own Canarytokens.
 gojue/ehids-agent
A Linux Host-based Intrusion Detection System based on eBPF.
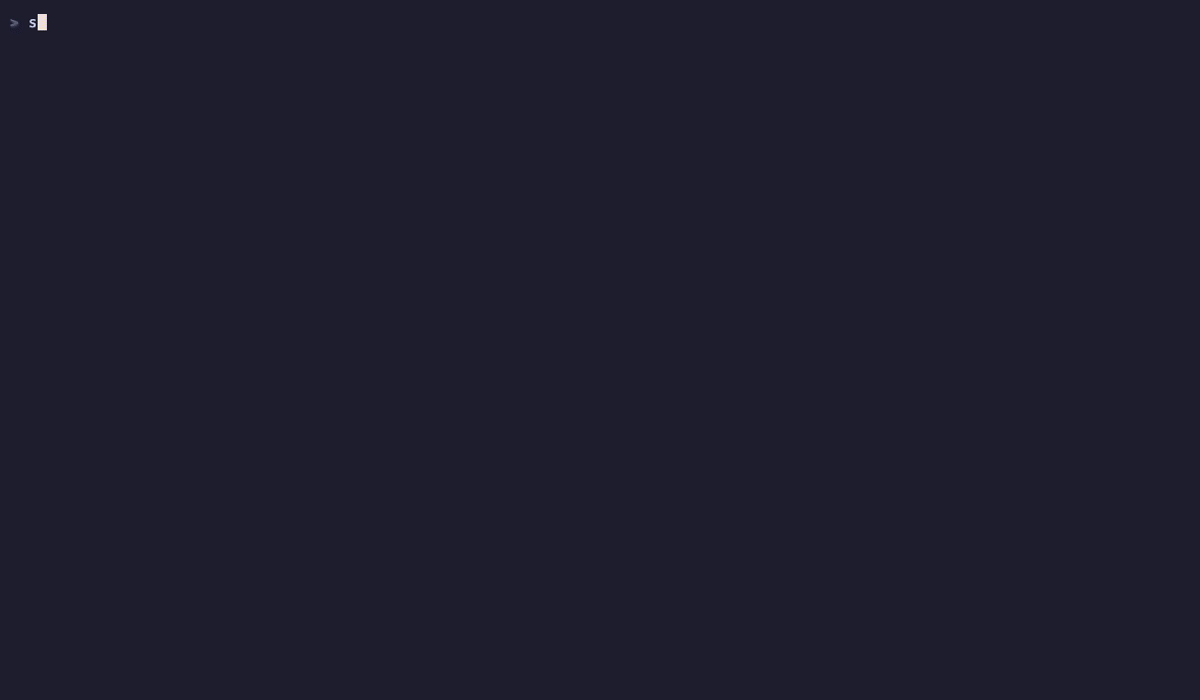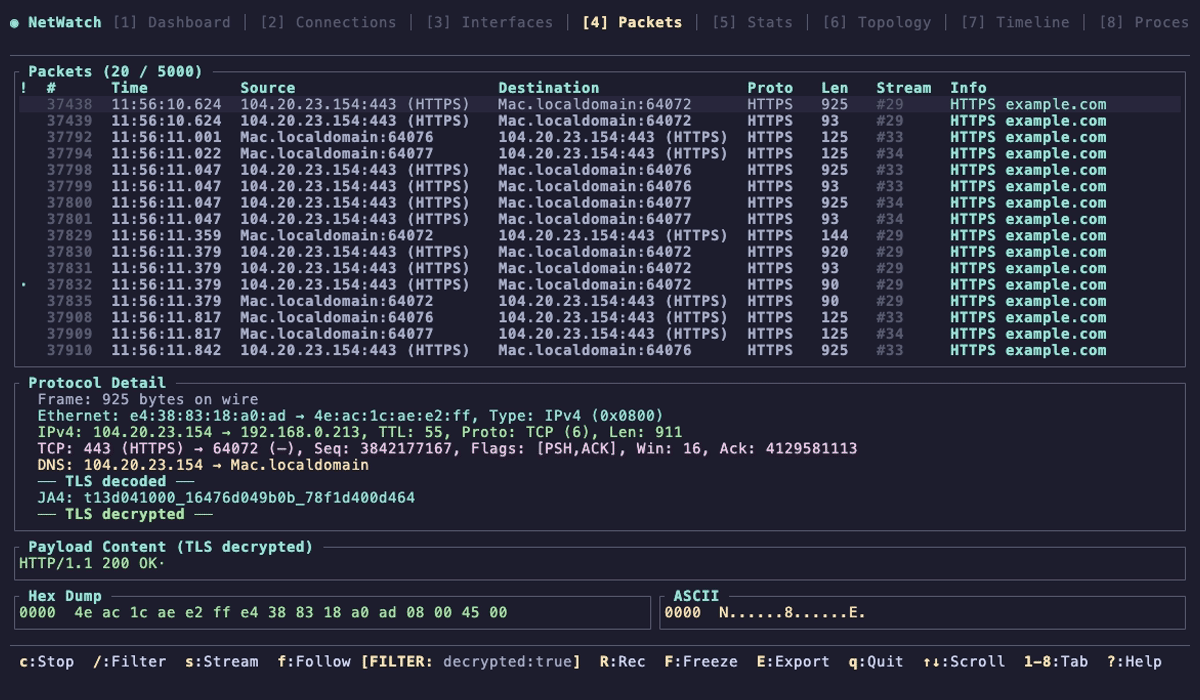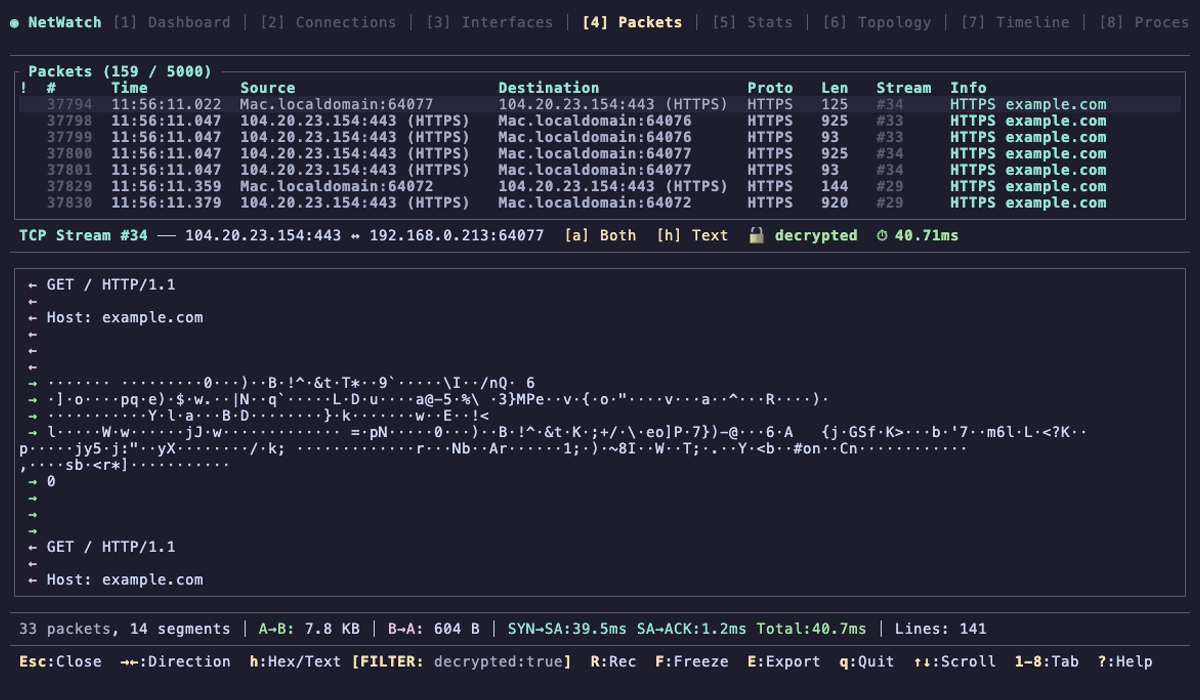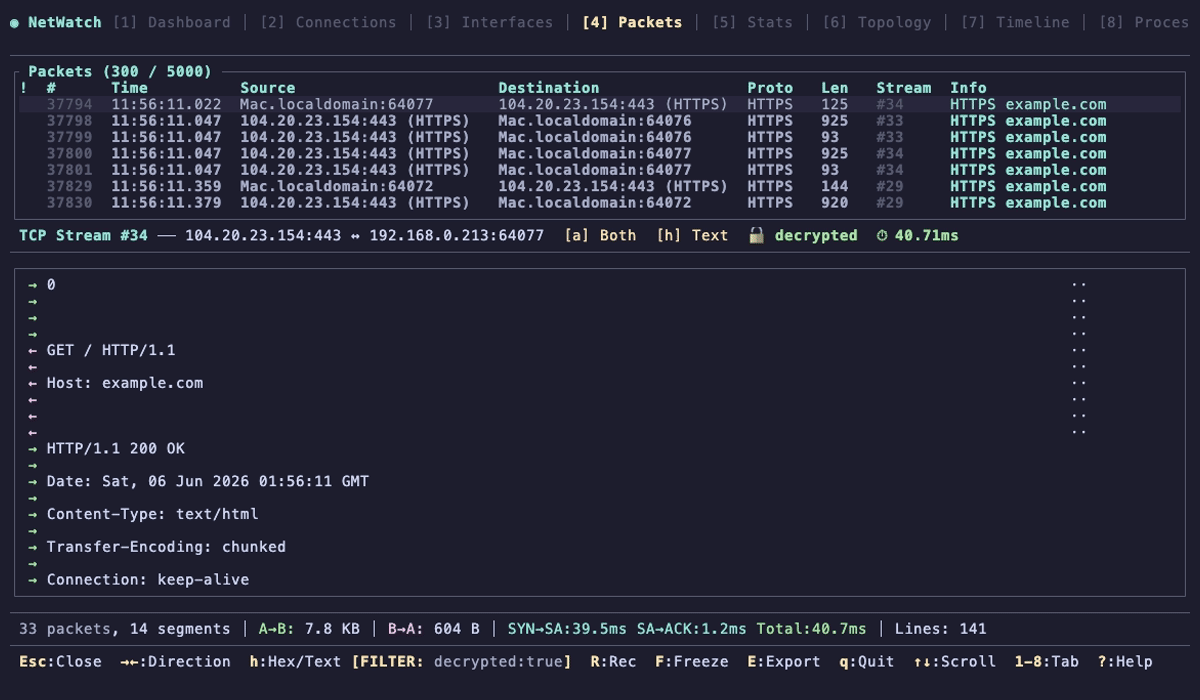 matthart1983/netwatch
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
 neo23x0/auditd
Best Practice Auditd Configuration
 wortell/cve-2020-0618
CVE-2020-0618 Honeypot
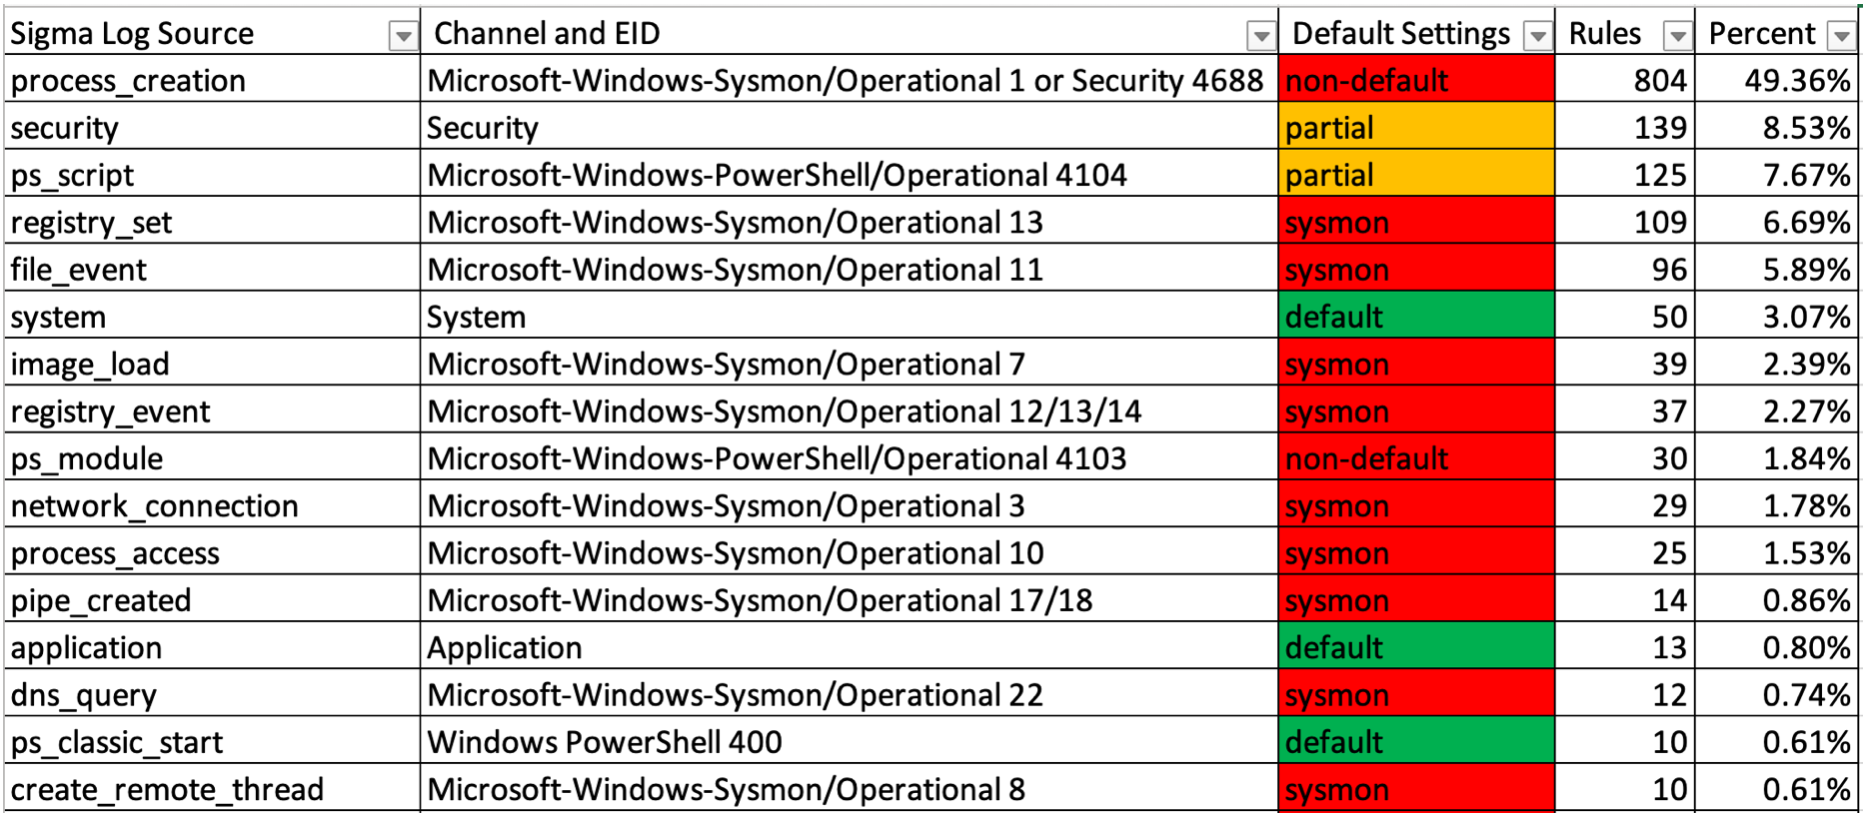 yamato-security/enablewindowslogsettings
Documentation and scripts to properly enable Windows event logs.
 snorby/snorby
Ruby On Rails Application For Network Security Monitoring