

threat-intel
 volexity/threat-intel
Signatures and IoCs from public Volexity blog posts.
defensive-toolsintrusion-detectionioc-management+4
3734 days ago
volexity/threat-intelSignatures and IoCs from public Volexity blog posts.
 sifalcon/detection
Curated collection of detection rules and IOCs extracted from DFIR engagements and malware analyses to support threat hunting, incident response, and…
 mellow-hype/c2finder
Look for un-sinkholed C&C IPs in your Bro logs (from Bambanek Consulting C&C master list)
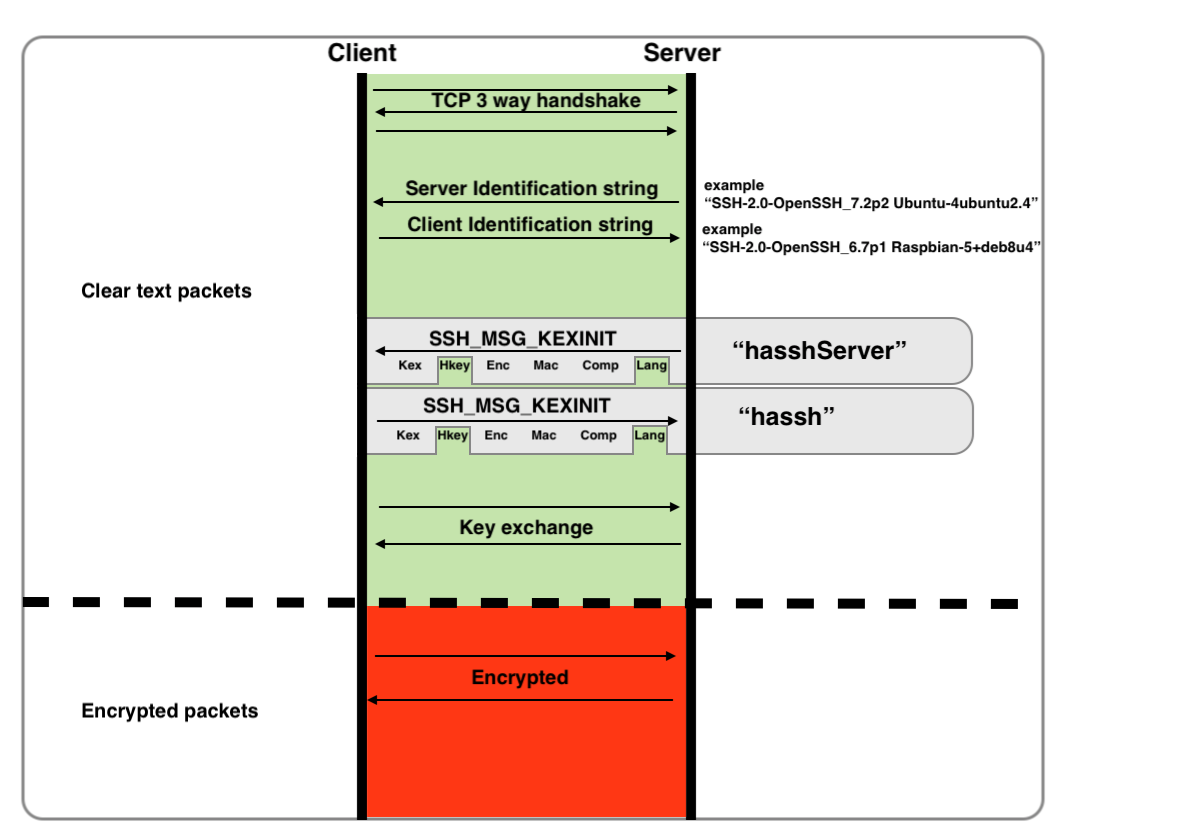 corelight/hassh
Fingerprint SSH clients and servers.