
KQL-threat-hunting-queries
 cyb3rmik3/kql-threat-hunting-queries
A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).
ctfcurated-resourceseducation+4
798
cyb3rmik3/kql-threat-hunting-queriesA repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).
 initconf/cve-2017-5638_struts
Bro/Zeek script for detecting Apache Struts CVE-2017-5638 reconnaissance, compromise, and malware download tracking with automated IP extraction.
 ohmyadd/wetland
A high interaction SSH honeypot
 corelight/zeek-openvpn
A Zeek OpenVPN protocol analyzer plugin.
 jconeby/elastic-peak-dashboards
PEAK Baseline Threat Hunt dashboards for Security Onion 3.0 — covering DNS, HTTP, TLS, SMB, Kerberos, SSH, RDP, DCE/RPC, LDAP, Modbus, DNP3,…
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 v1d1an/s1em
This project is a SIEM with SIRP and Threat Intel, all in one.
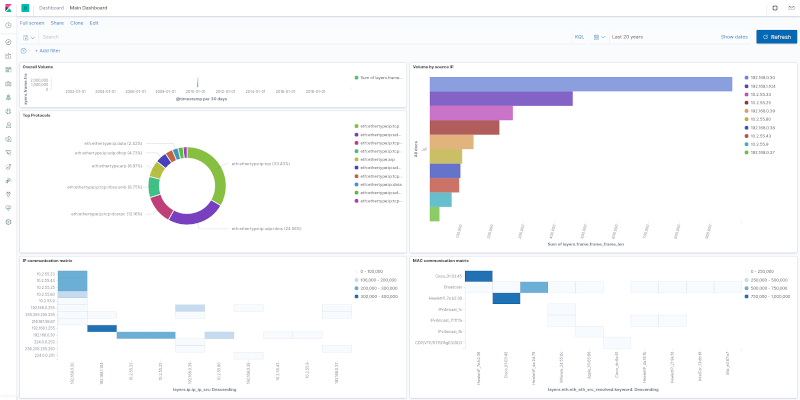 h21lab/tsharkvm
tshark + ELK analytics virtual machine