dsiem
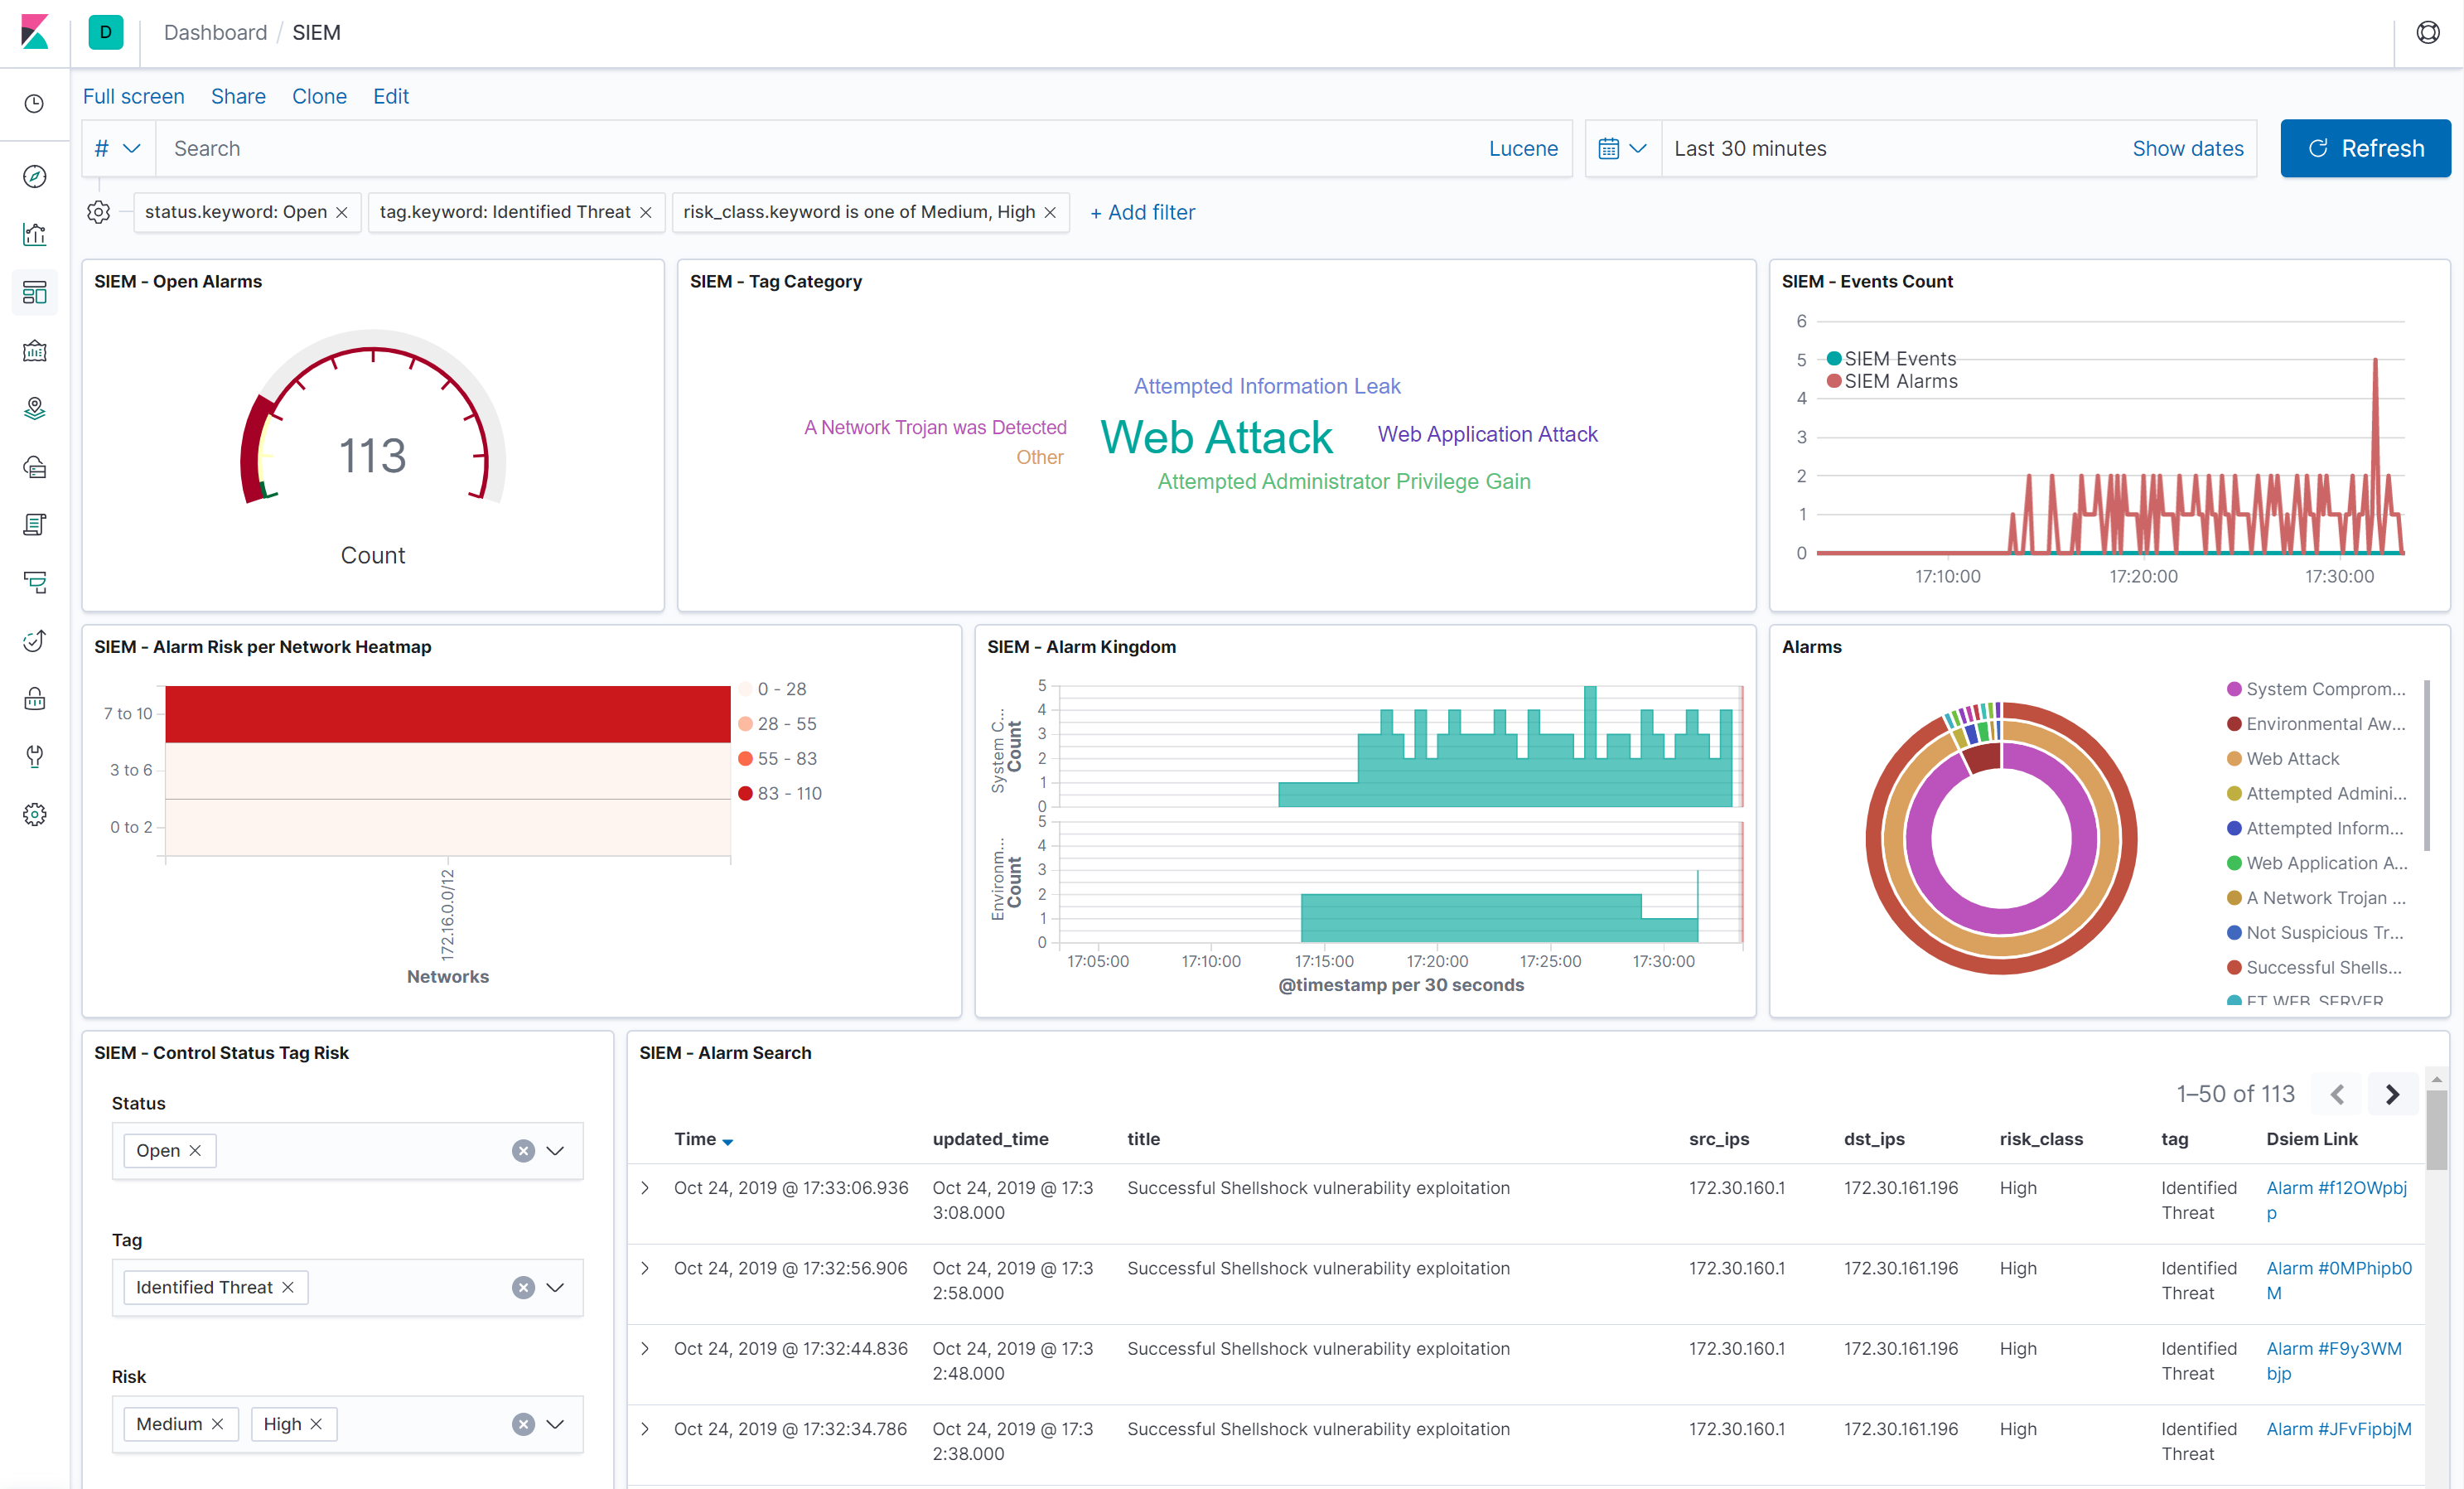
 defenxor/dsiem
Security event correlation engine for ELK stack
cloud-securityincident-responseintrusion-detection+3
defenxor/dsiemSecurity event correlation engine for ELK stack
 damnkrishna/cve-2025-32433-lab
A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 cybereason-public/owlsm
Sigma Rules Engine inside the Linux Kernel using eBPF. Focusing on prevention capabilities
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 cr0nx/awesome-linux-attack-forensics-purplelabs
This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.
 devopstoday11/tarian
Anti-Virus for K8s. Protect your Applications running on Kubernetes from malicious attacks with pre-registered source code, runtime processes…
 ashok523/cve-2026-31431
Defensive IR playbook and detection package for CVE-2026-31431 (Copy Fail) Linux kernel LPE, including Sigma, auditd, Falco, Wazuh, YARA, eBPF, and…
 azdevops143/fragnesia-charan-cve-2026-46300
Hardened container staging framework with seccomp syscall whitelisting and eBPF telemetry to detect and block container escape and kernel ULP…
 bytedance/elkeid
Elkeid is an open source solution that can meet the security requirements of various workloads such as hosts, containers and K8s, and serverless. It…
 thomaspatzke/log4pot
A honeypot for the Log4Shell vulnerability (CVE-2021-44228).
 cmpnn-romain/cve-2024-27198_lab
Lab for the CVE-2024-27198
 clong/detectionlab
Automate the creation of a lab environment complete with security tooling and logging best practices
 deckhouse/d8-copy-fail-mitigation
Kubernetes-native CVE-2026-31431 mitigation with automated kernel module blocking, runtime Falco detection rules, and bashible-based node…
 neo23x0/auditd
Best Practice Auditd Configuration
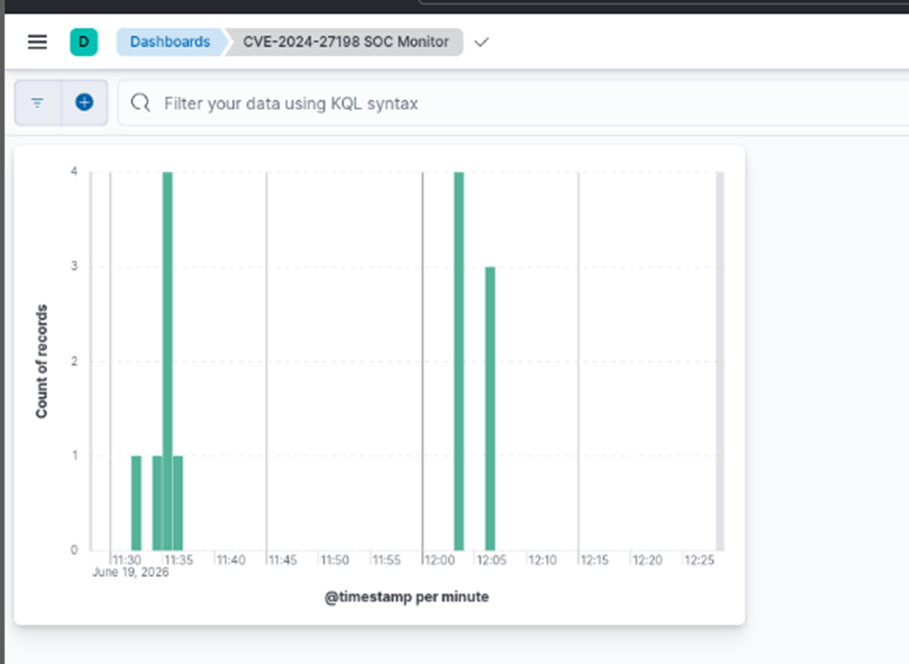 ptd200110/cve-2024-27198-soc-lab
SOC detection and incident response lab simulating CVE-2024-27198 authentication bypass in JetBrains TeamCity. Includes ELK SIEM, Suricata IDS, Sigma…
 fankh/vulnerability-poc
CVE proof-of-concept labs, exploit scripts, and detection/prevention rules (Nginx, Apache, Snort, YARA) for high-severity CVEs. Authorized security…