

zerologon
 corelight/zerologon
Zeek package to detect Zerologon
defensive-toolsintrusion-detectionnetwork-security+2
corelight/zerologonZeek package to detect Zerologon
 millikanjohnl-blip/dirtyfrag-detection-rules
Detection rules and analysis for Dirty Frag (CVE-2026-43284/CVE-2026-43500) Linux kernel LPE vulnerability. Based on community research and health…
 hardenedvault/ved-ebpf
eBPF-based runtime kernel security monitor detecting exploits and rootkits via control flow integrity (wCFI) and privilege escalation detection (PSD)…
 kadir/copy-fail-cve-2026-31431-ioc
Detection, mitigation, and IOC toolkit for Copy Fail CVE-2026-31431 Linux kernel page-cache privilege escalation
 corelight/cve-2021-42292
Zeek package detecting CVE-2021-42292 Microsoft Excel local privilege escalation exploit via network traffic analysis of spreadsheet downloads.
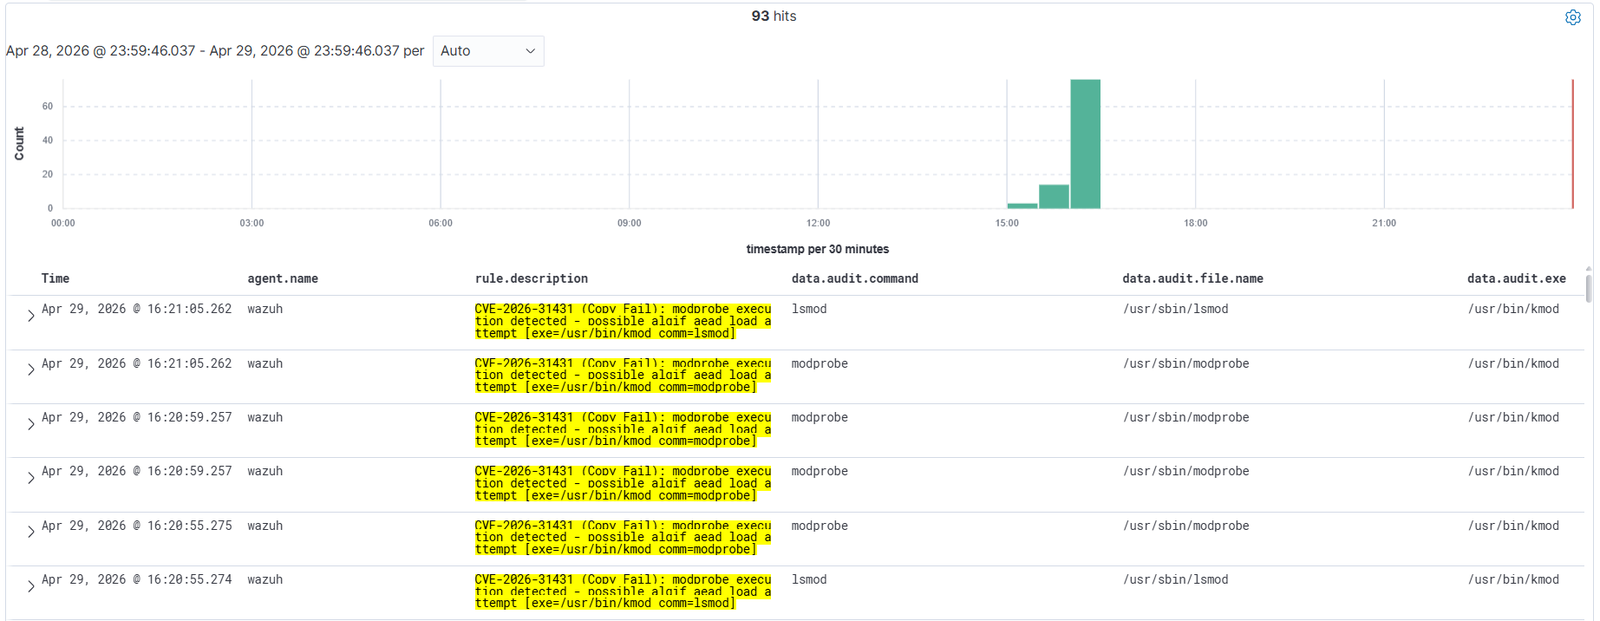 mym0us3r/copy-fail-detection-with-wazuh-4.14.4
Wazuh 4.14.4 detection rules for CVE-2026-31431 (Copy Fail) - Linux Local Privilege Escalation via authencesn page cache write
 kuniyal08/dirty-frag-cve-2026-43284
A report on Dirty Frag, which is a Linux Local Privilege Escalation (LPE) vulnerability chain that allows an unprivileged user to gain root access
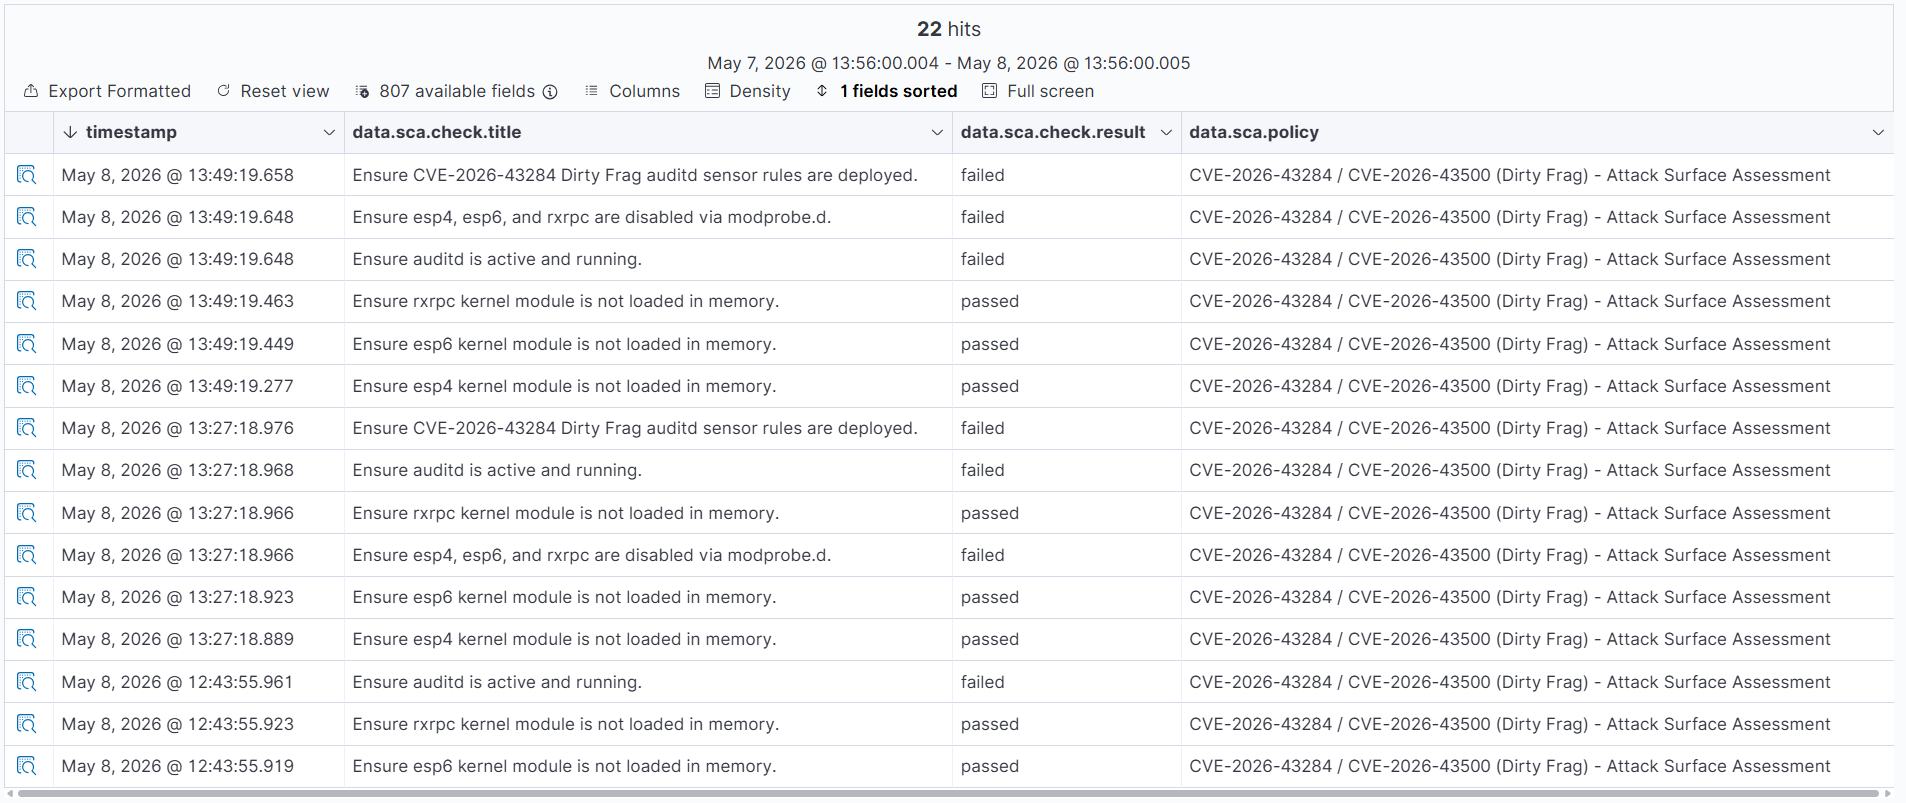 mym0us3r/dirty-frag-detection-with-wazuh-4.14.4
Wazuh 4.14.4 detection rules for CVE-2026-43284 / CVE-2026-43500 (Dirty Frag) - Linux Local Privilege Escalation via page cache write
 daryllundy/cve-2025-32463
Detection framework for CVE-2025-32463 sudo privilege escalation vulnerability. Provides real-time monitoring, forensic analysis, and SIEM…
 insomnisec/detections-cve-2026-31431
Detection rules, YARA signatures, auditd/Wazuh rules, and MISP event templates for CVE-2026-31431 Linux kernel LPE vulnerability (Copy Fail).…
 g0thamrabb1t/cve-2026-46331-pedit-cow-detection
Defensive validation of CVE-2026-46331 / pedit COW with auditd, AppArmor, mitigation comparison and detection logic.
 ashok523/cve-2026-31431
Defensive IR playbook and detection package for CVE-2026-31431 (Copy Fail) Linux kernel LPE, including Sigma, auditd, Falco, Wazuh, YARA, eBPF, and…
 vishvacyber/detection-tool-kit-for-cve-2026-31431
Layered detection toolkit for CVE-2026-31431 (Copy Fail) Linux kernel LPE. Provides eBPF, auditd, Sigma rules, page-cache diff, and IOC guides for…
 g0thamrabb1t/cve-2026-43284-dirtyfrag-detection
Lab validation report and detection artifacts for CVE-2026-43284 (DirtyFrag) Linux LPE. Provides auditd telemetry, event correlation rules, and…
 gojue/ehids-agent
A Linux Host-based Intrusion Detection System based on eBPF.
 nitrocao/cve-2024-21626
PoC and Detection for CVE-2024-21626