

snort3
 snort3/snort3
Multi-threaded network intrusion detection and prevention system with rule-based detection, protocol-aware inspection, and pcap analysis for…
anti-botdefensive-toolsfuzzing+3
3.5k3 months ago
snort3/snort3Multi-threaded network intrusion detection and prevention system with rule-based detection, protocol-aware inspection, and pcap analysis for…
 c2dc/anomaly-flow
Framework for implementing Network Intrusion Detection Systems (NIDS) aimed at identifying anomalies in network flows using Federated Learning models.
 siddharth2440/network-detection-engine
Lightweight network intrusion detection engine capturing live traffic with libpcap. Detects SYN/ICMP floods, port scans, and signature-based web…
 camp0/aiengine
AIEngine is a next generation interactive/programmable Python/Ruby/Java/Lua and Go NIDS (Network intrusion detection system).
 barghest-ngo/mesh
Encrypted peer-to-peer mesh VPN for remote mobile forensics, enabling wireless ADB and libimobiledevice acquisition, network monitoring, and…
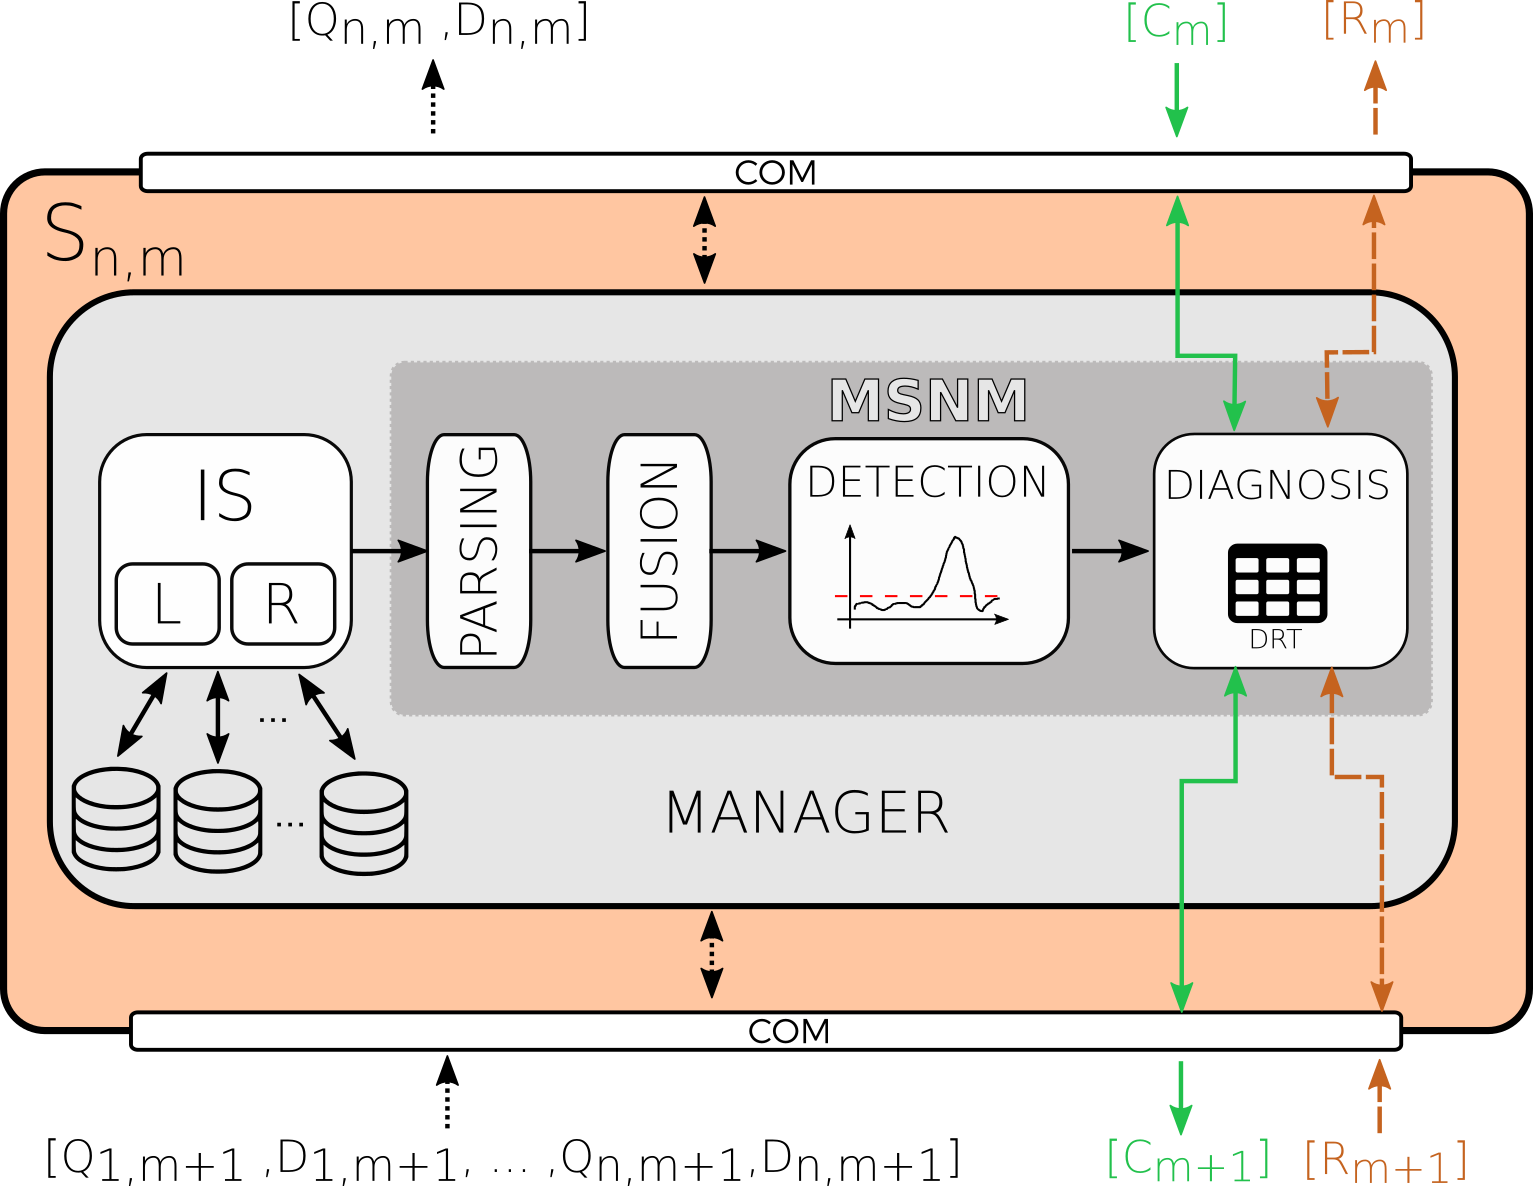 nesg-ugr/msnm-sensor
Multivariate statistical network monitoring sensor that detects anomalies using PCA-based techniques, aggregating lightweight statistics from…
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
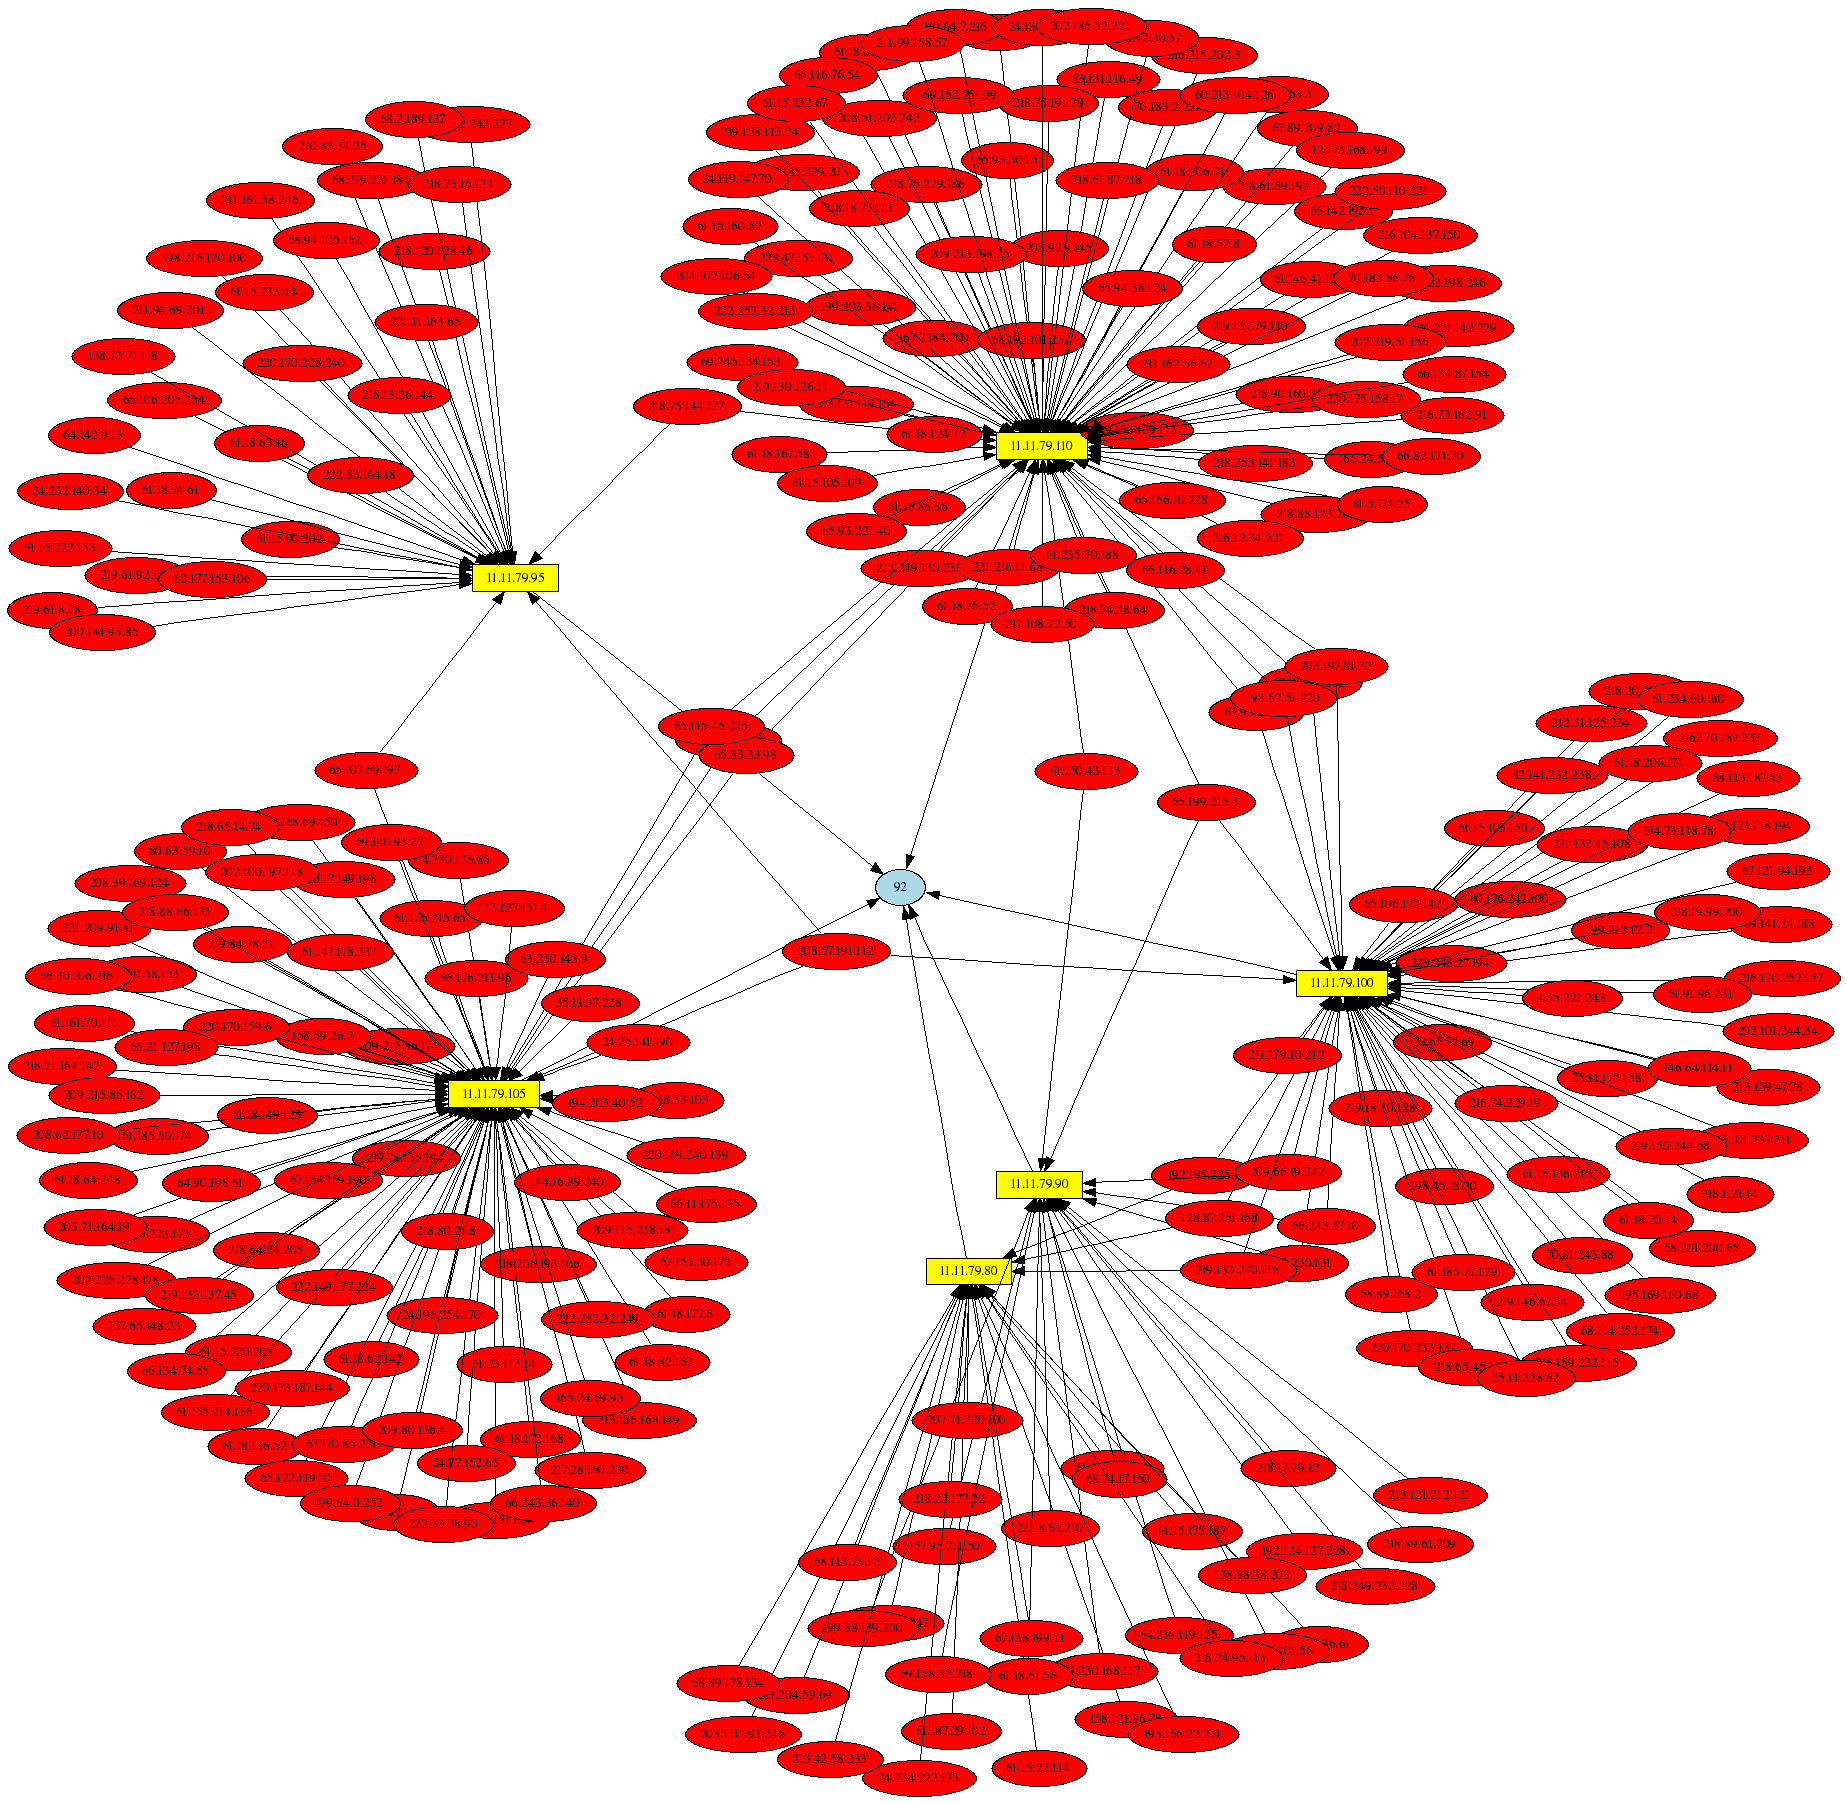 mrash/psad
psad: Intrusion Detection and Log Analysis with iptables
 yojiwatanabe/networkalarm
A tool to monitor local network traffic for possible security vulnerabilities. Warns user against possible nmap scans, Nikto scans, credentials sent…
 advanced-threat-research/cve-2020-16899
CVE-2020-16899 - Microsoft Windows TCP/IP Vulnerability Detection Logic and Rule
 corelight/cve-2022-26937
Zeek package detecting CVE-2022-26937 exploitation attempts against Windows NFS servers via Network Lock Manager protocol analysis.
 solidevil14/suricata-rule-for-detecting-cve-2025-55182
CVE‑2025‑55182 Detection
 lp008/cve-2020-13942
Exploit for Apache Unomi pre-auth RCE (CVE-2020-13942) with a Suricata detection rule for identifying exploitation attempts.
 corelight/cve-2022-24497
Zeek-based network detector for CVE-2022-24497, identifying RPC portmap exploit attempts via real-time traffic analysis and alerting.
 corelight/cve-2022-24491
Zeek-based network detector for CVE-2022-24491, monitoring RPC portmap set and dump actions to identify exploit attempts in real-time traffic.
 h7hac9/cve-2020-1938
Suricata and Bro detection rules for CVE-2020-1938 (Ghostcat) Tomcat AJP file read vulnerability, enabling network-level monitoring and alerting.
 aricooper/suricata-script
CVE-2020-16898 — “Bad Neighbor” (ICMPv6 RDNSS length parsing) — Suricata Lua Detection
 streghstreek/cve-2020-1938
Detection rules for CVE-2020-1938 (Ghostcat) vulnerability in Apache Tomcat AJP connector, with Suricata and Bro signatures for network-based…