
Detection
 sifalcon/detection
Curated collection of detection rules and IOCs extracted from DFIR engagements and malware analyses to support threat hunting, incident response, and…
curated-resourcesdigital-forensicsincident-response+4
24
sifalcon/detectionCurated collection of detection rules and IOCs extracted from DFIR engagements and malware analyses to support threat hunting, incident response, and…
 pbssubhash/h0neytr4p
Easy to configure Honeypot for Blue Team
 cyberdefenders/detectionlabelk
DetectionLabELK is a fork from DetectionLab with ELK stack instead of Splunk.
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 0warn/defender
This is a bash script focus on hardening linux. This is a custom think of windows defender but unlike of their privacy issue. User can feel freedom…
 jaksi/sshesame
An easy to set up and use SSH honeypot, a fake SSH server that lets anyone in and logs their activity
 nccgroup/uninstalledappcanary
A Canary which fires when uninstalled
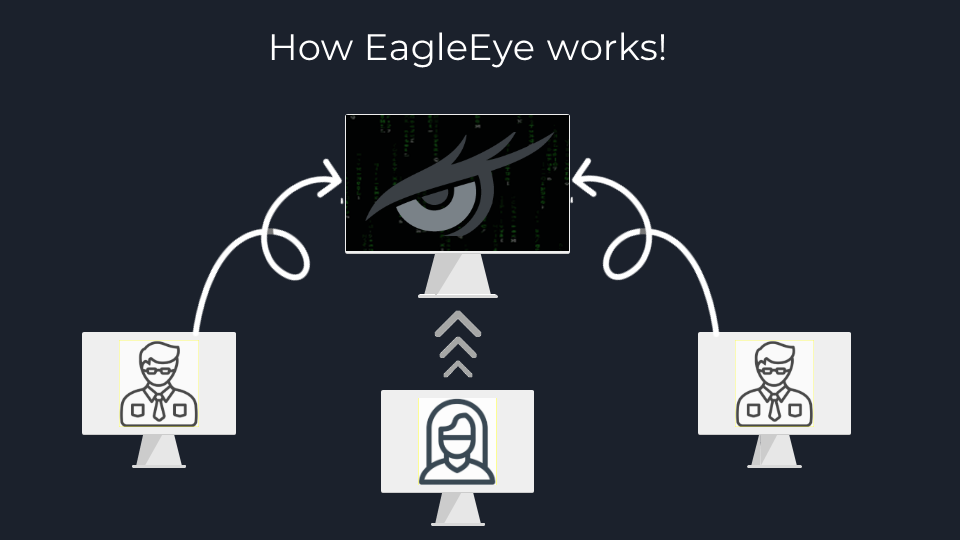 d4vinci/eagleeye
A host-based IDS and network monitoring system (My graduation project)
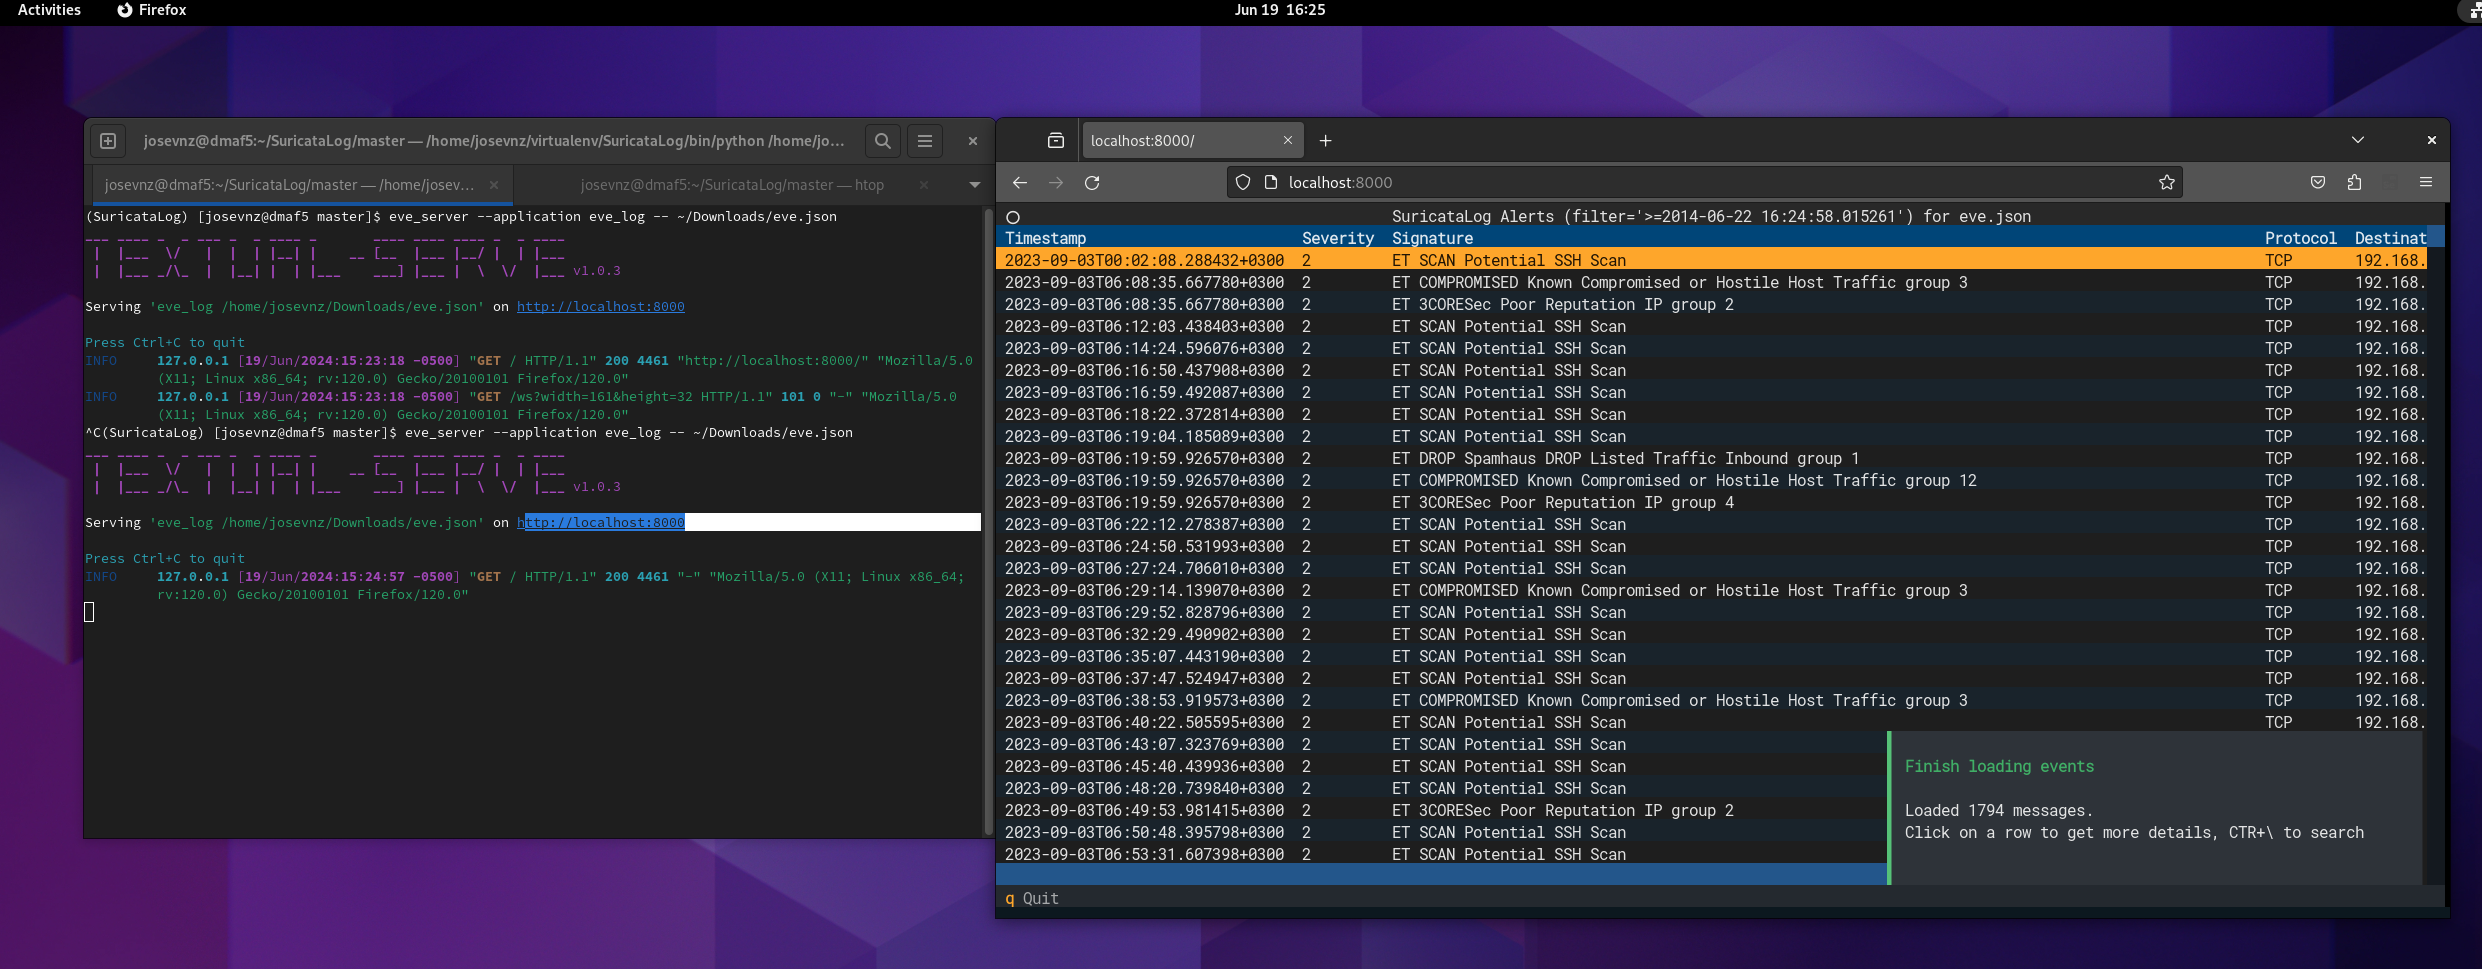 josevnz/suricatalog
Parse, filter, and visualize Suricata eve.json logs with CLI tools for alerts, flows, DNS, and payloads. Includes a tutorial for learning Suricata…