

ARTIF
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
information-gatheringintrusion-detectionioc-management+5
cred-club/artifAn advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 the-tcpdump-group/libpcap
System-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…
 corelight/icanntld
Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 ma111e/melody
Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
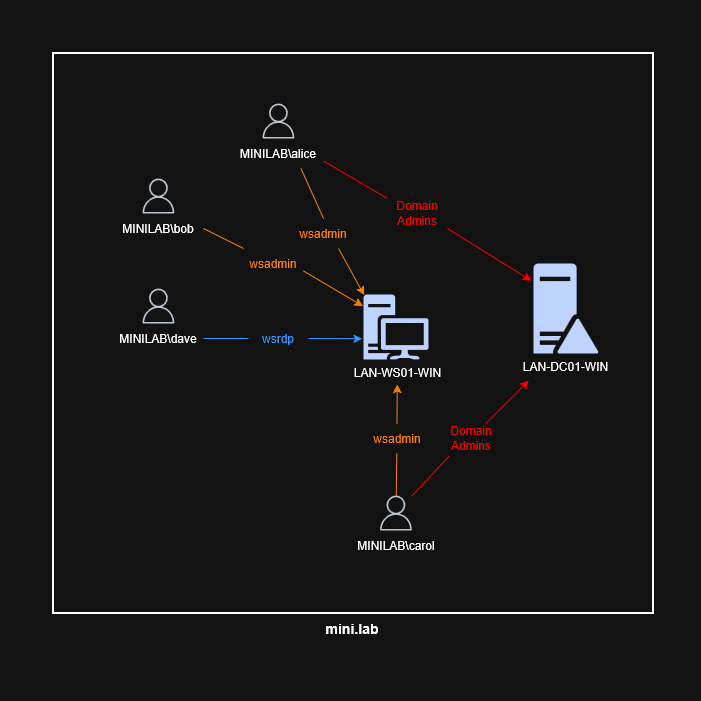 0xmr007/lab4purplesec
Lab4PurpleSec is a modular Purple Team homelab combining a vulnerable Active Directory environment (GOAD), a Docker-based web DMZ, pfSense +…
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
 taisa456/network-security-snort
Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…
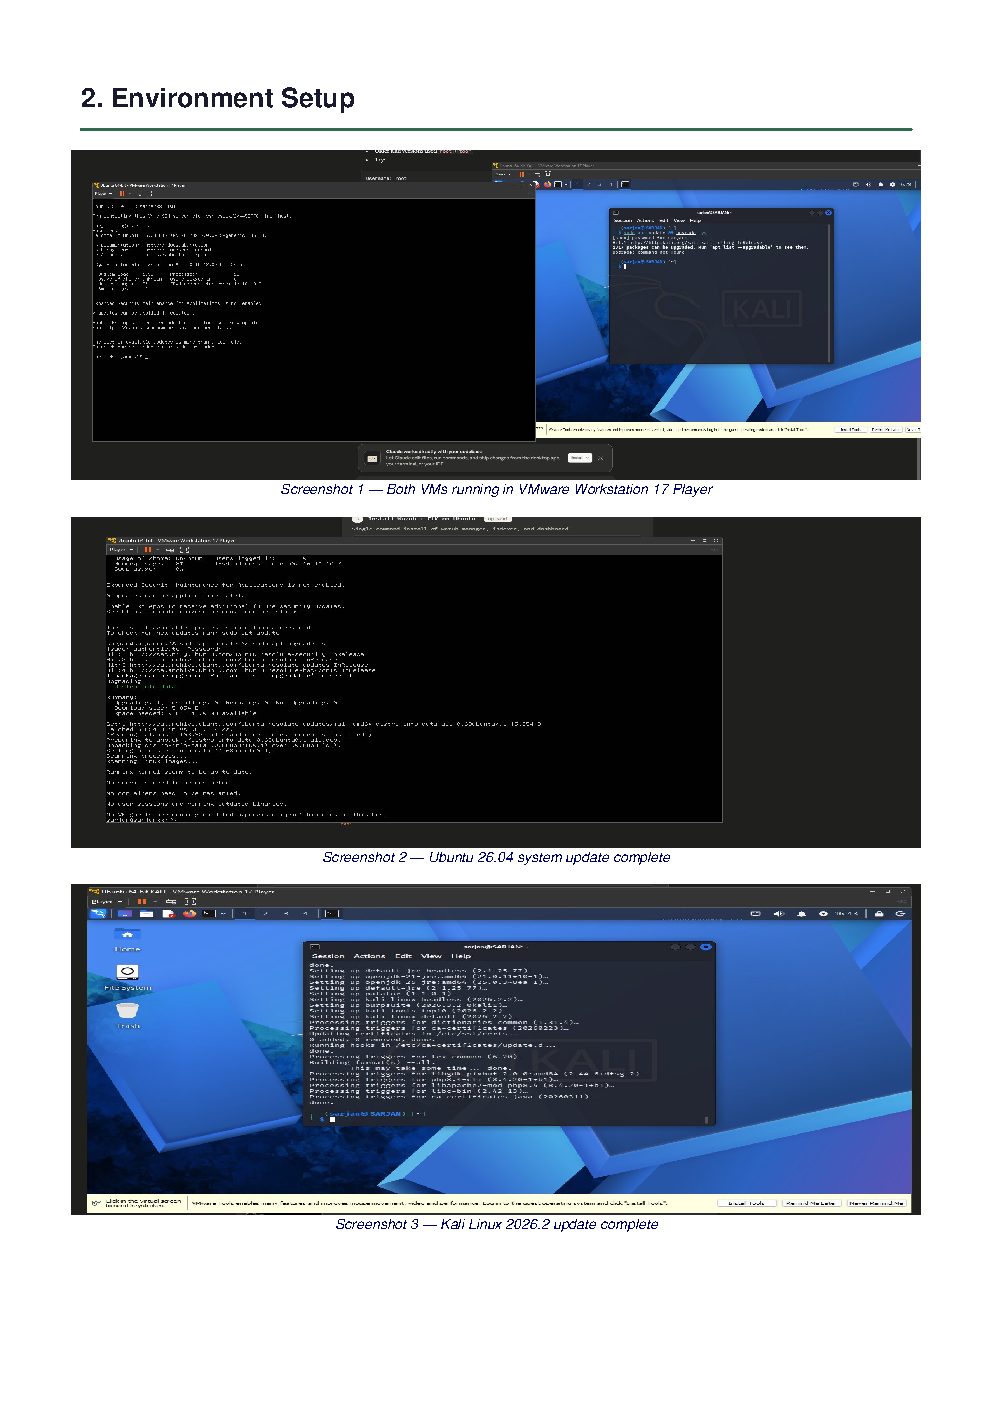 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
 mcastens/alycon-threat-landscape
Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 jay123anta/laravel-threat-detection
Passive Laravel middleware that detects and logs SQL injection, XSS, RCE, bot scanners, and 175+ attack patterns. Features a built-in dashboard,…
 initconf/cve-2017-5638_struts
Bro/Zeek script for detecting Apache Struts CVE-2017-5638 reconnaissance, compromise, and malware download tracking with automated IP extraction.
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 oisf/suricata
Open-source network IDS/IPS/NSM engine for real-time traffic inspection, intrusion detection and prevention, protocol analysis, and rule-based threat…