
cve-2022-26809
 corelight/cve-2022-26809
Zeek package detecting CVE-2022-26809 remote code execution attempts and successful exploitation over DCE/RPC, generating actionable exploit attempt…
exploitationincident-responseintrusion-detection+3
32
corelight/cve-2022-26809Zeek package detecting CVE-2022-26809 remote code execution attempts and successful exploitation over DCE/RPC, generating actionable exploit attempt…
 corelight/cve-2022-26937
Zeek package detecting CVE-2022-26937 exploitation attempts against Windows NFS servers via Network Lock Manager protocol analysis.
 corelight/cve-2021-1675
Zeek script and Suricata rules to detect PrintNightmare (CVE-2021-1675) exploitation via RpcAddPrinterDriver DCE RPC events, with PCAP-based testing.
 corelight/cve-2022-3602
Zeek package detecting CVE-2022-3602 exploitation attempts and vulnerable OpenSSL servers via HTTP Server header and TLS punycode anomalies,…
 lp008/cve-2020-13942
Exploit for Apache Unomi pre-auth RCE (CVE-2020-13942) with a Suricata detection rule for identifying exploitation attempts.
 corelight/cve-2022-30216
Zeek package detecting CVE-2022-30216 NTLM relay attacks against Windows Server. Raises notices for exploit attempts and successful exploitation via…
 streghstreek/cve-2020-1938
Detection rules for CVE-2020-1938 (Ghostcat) vulnerability in Apache Tomcat AJP connector, with Suricata and Bro signatures for network-based…
 initconf/cve-2021-1675-printnightmare
Zeek package to detect CVE-2021-1675 (PrintNightmare) by monitoring named pipes and RPC operations for spoolss exploitation attempts.
 dopheide-esnet/zeek-jetdirect
Zeek package to detect exploitation attempts of CVE-2017-2741 targeting HP JetDirect printers via network traffic analysis.
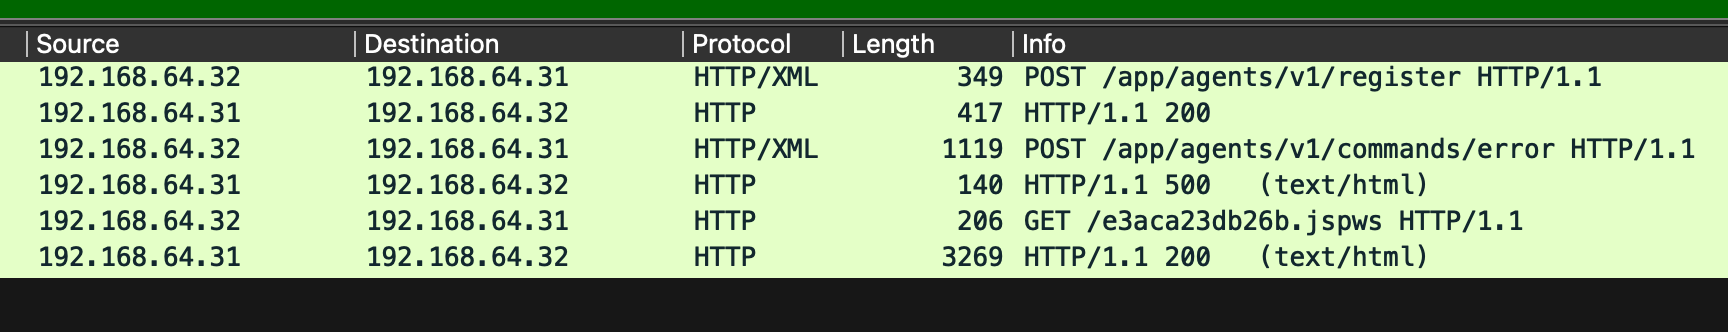 boredhackerblog/teamcity-cve-2026-63077-pcap
teamcity teamcity-CVE-2026-63077 exploitation pcap
 fox-it/cisco-ios-xe-implant-detection
Cisco IOS XE implant scanning & detection (CVE-2023-20198, CVE-2023-20273)
 yardenshafir/conference_talks
Slides from various conference talks
 solidevil14/suricata-rule-for-detecting-cve-2025-55182
CVE‑2025‑55182 Detection
 hslatman/awesome-industrial-control-system-security
A curated list of resources related to Industrial Control System (ICS) security.
 advanced-threat-research/cve-2020-16898
CVE-2020-16898 (Bad Neighbor) Microsoft Windows TCP/IP Vulnerability Detection Logic and Rule
 nicholasadamou/minipwner
A script to configure a TP-Link MR3040 running OpenWRT into a simple, yet powerful penetration-testing "dropbox".
 malwaretech/log4jtools
Tools for investigating Log4j CVE-2021-44228
 reddrip7/log4shell_cve-2021-44228_related_attacks_iocs
Curated repository of Indicators of Compromise (IOCs), attack source IPs, and Snort/Suricata detection rules for Log4Shell (CVE-2021-44228) attacks.