
 petabi/sniffles
Sniffles: Packet Capture Generator for IDS and Regular Expression Evaluation
 0xxon/cve-2020-0601-plugin
Zeek package that uses OpenSSL to detect CVE-2020-0601 exploit attempts
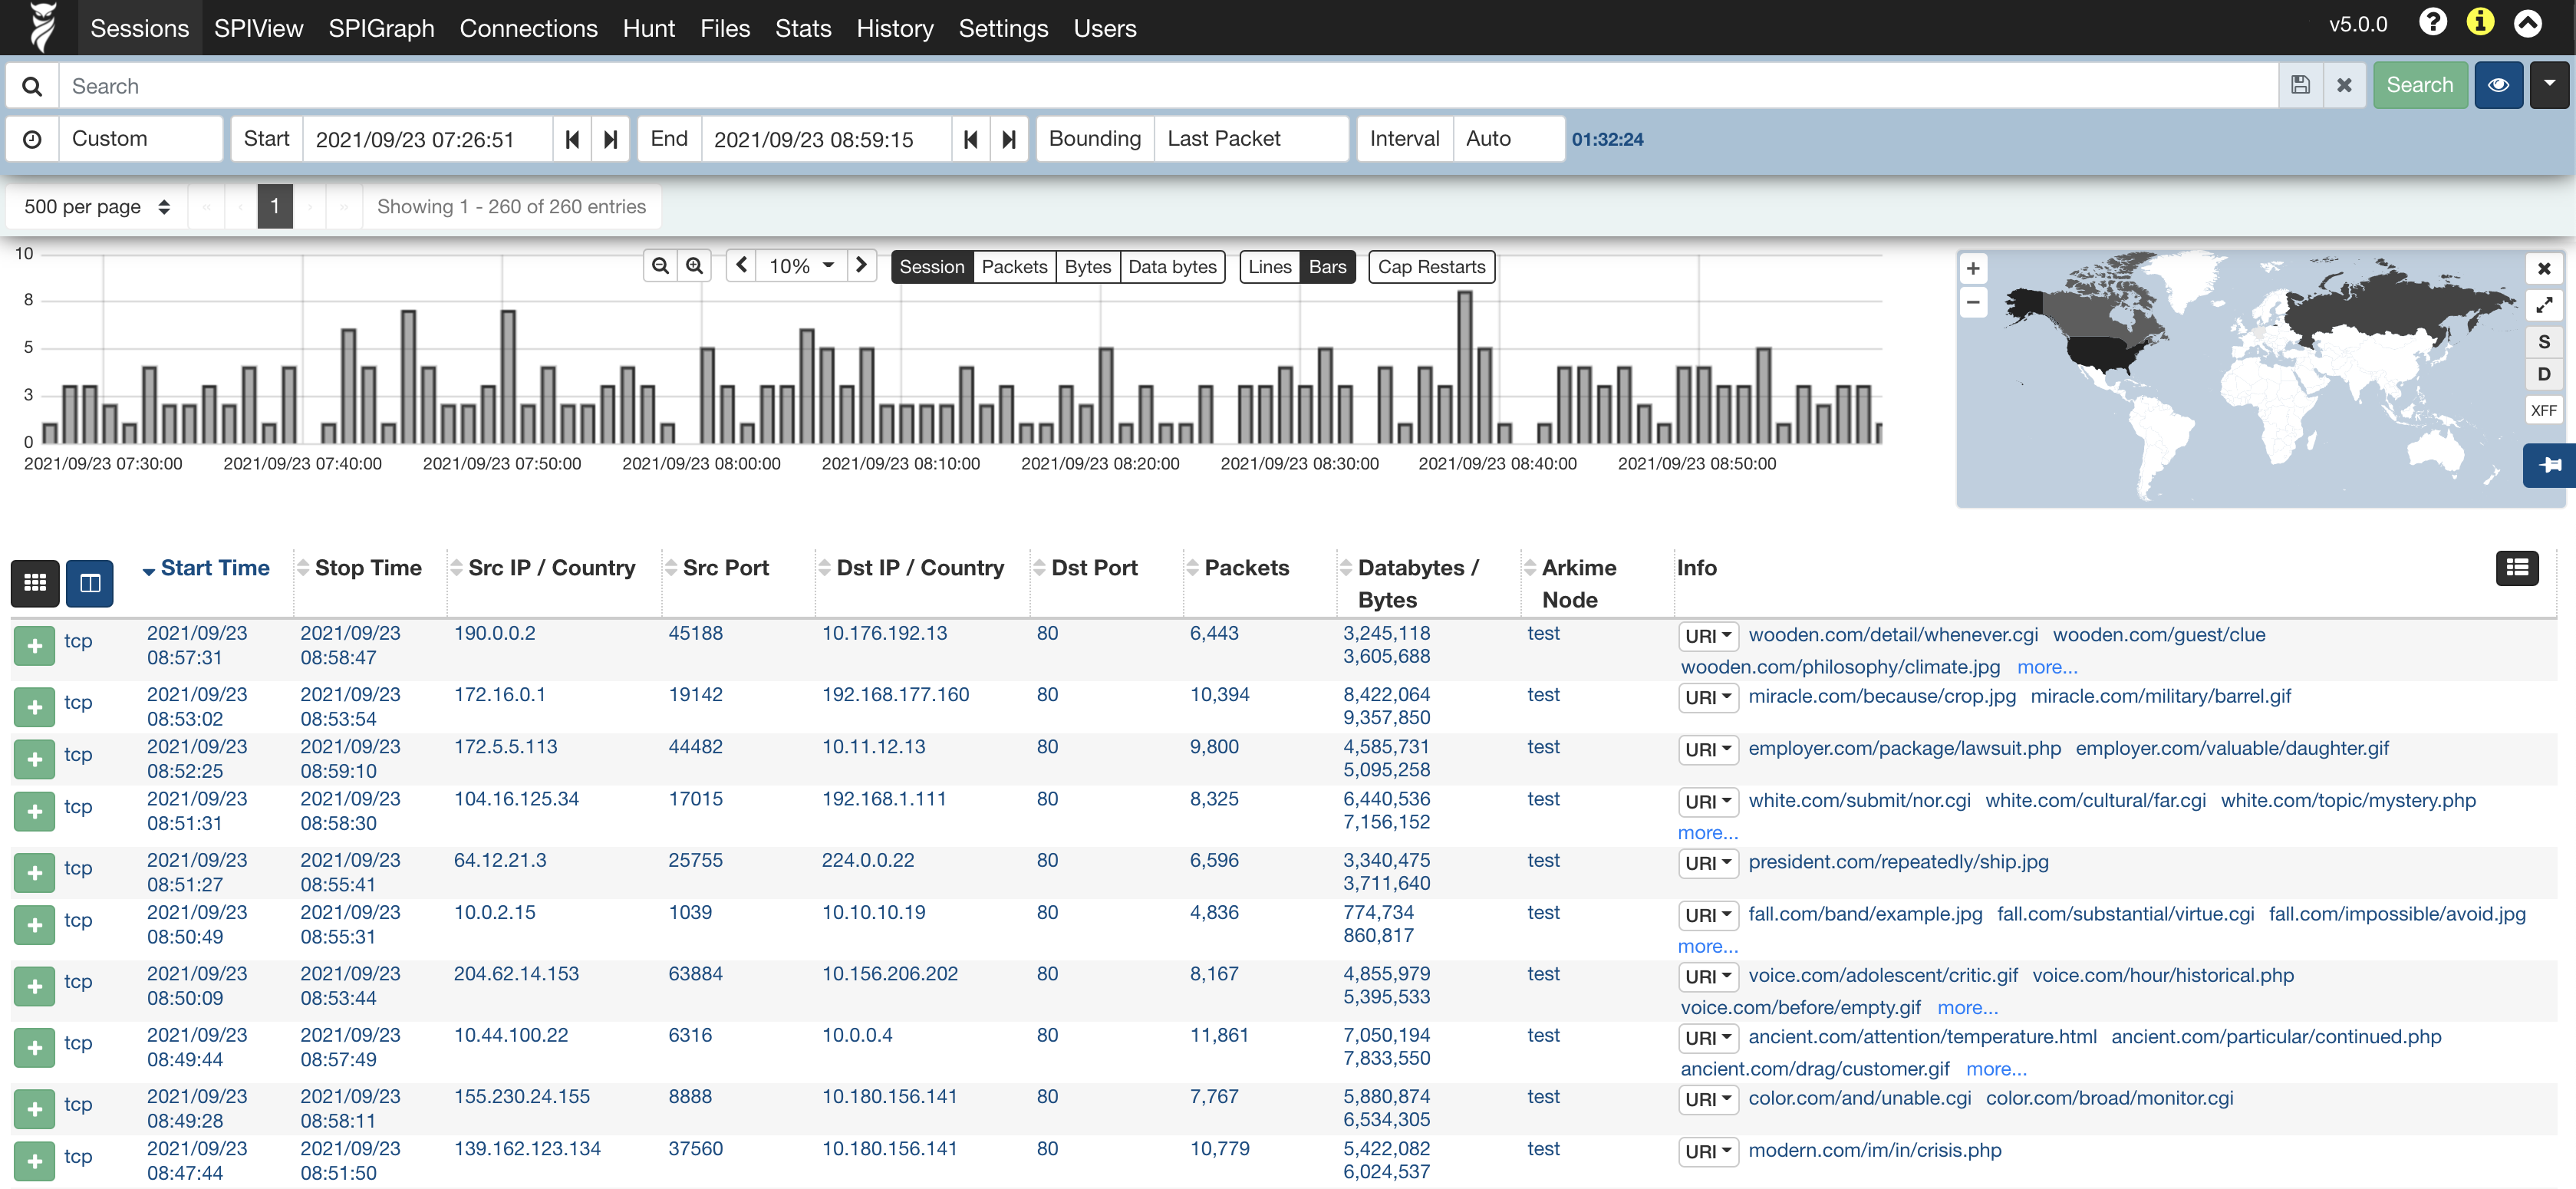 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 the-tcpdump-group/libpcap
System-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…
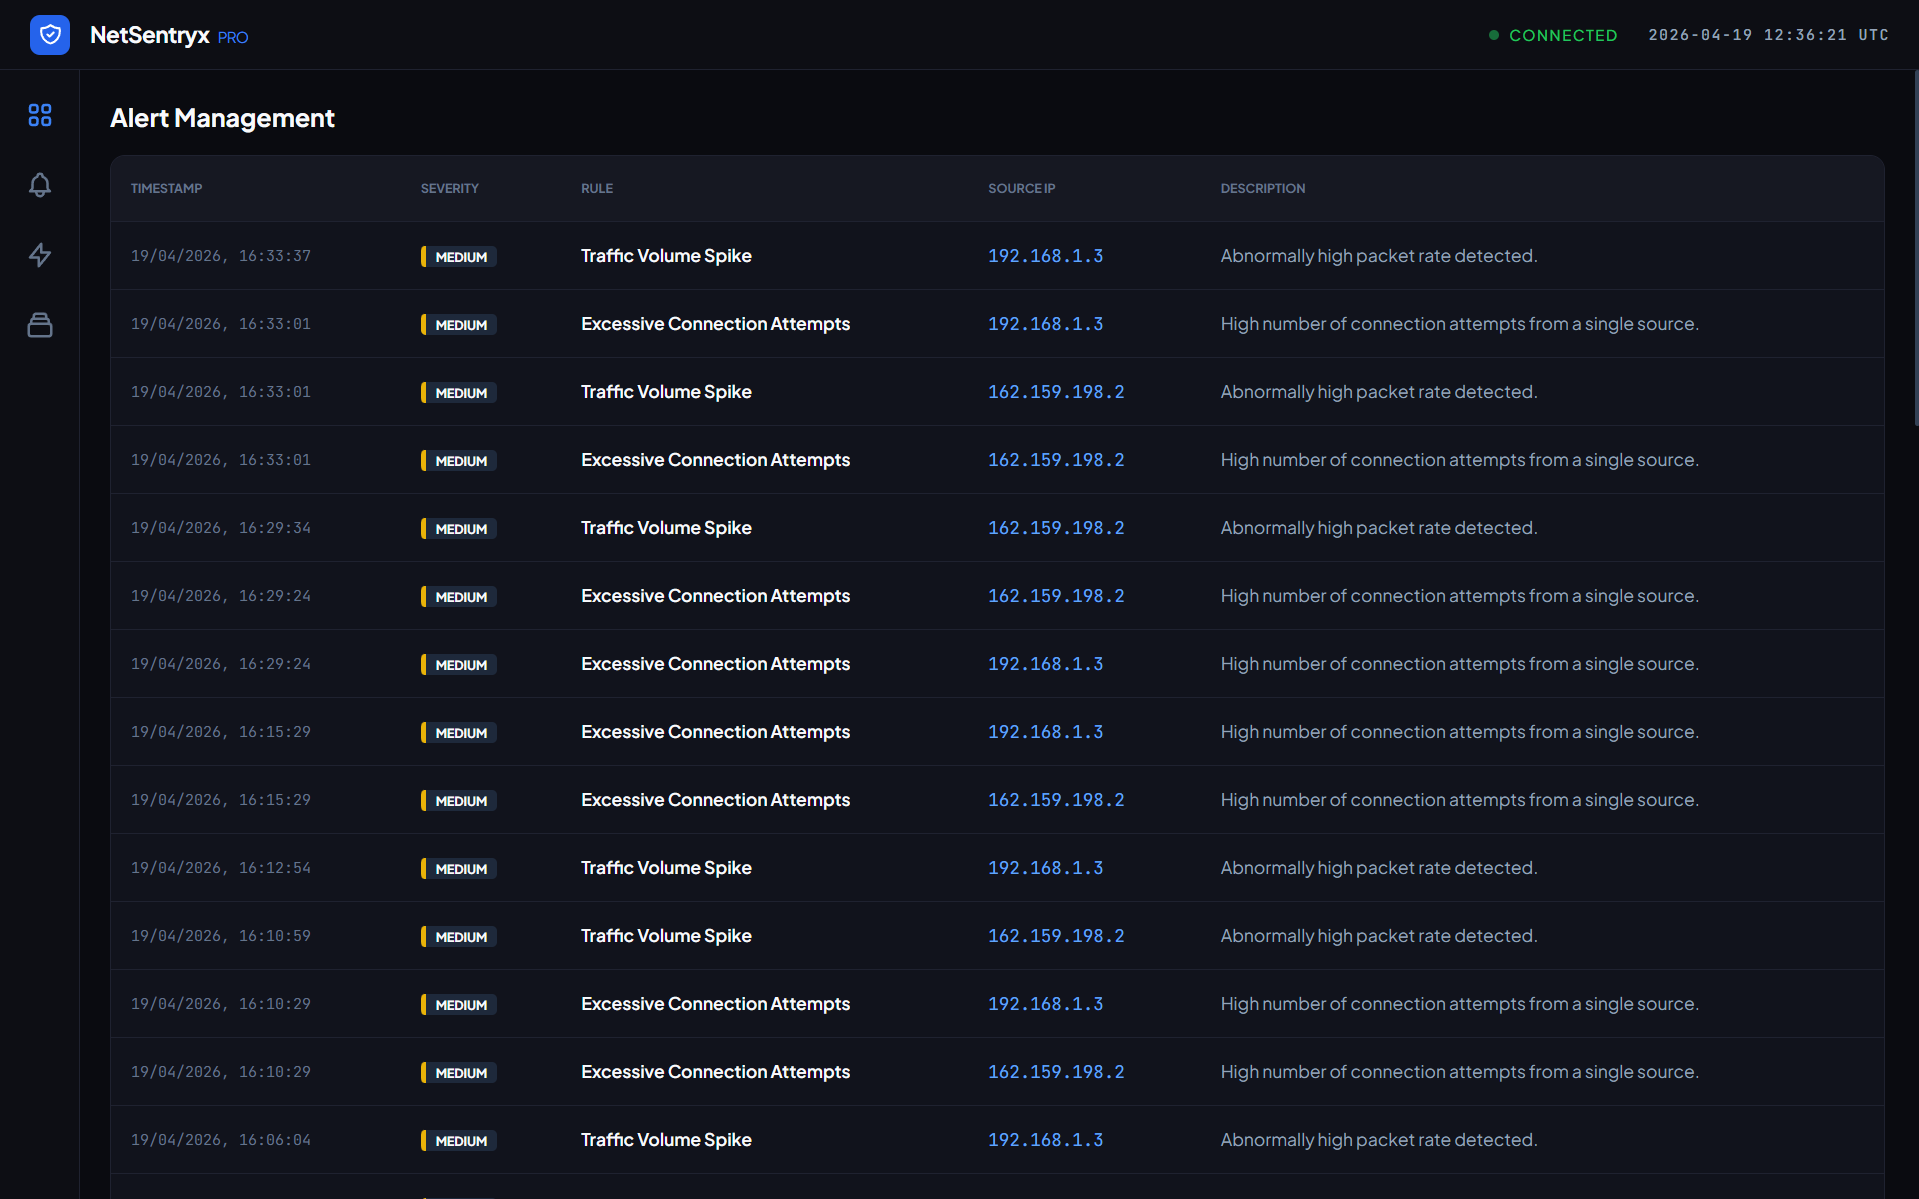 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
 idaholab/malcolm
Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…
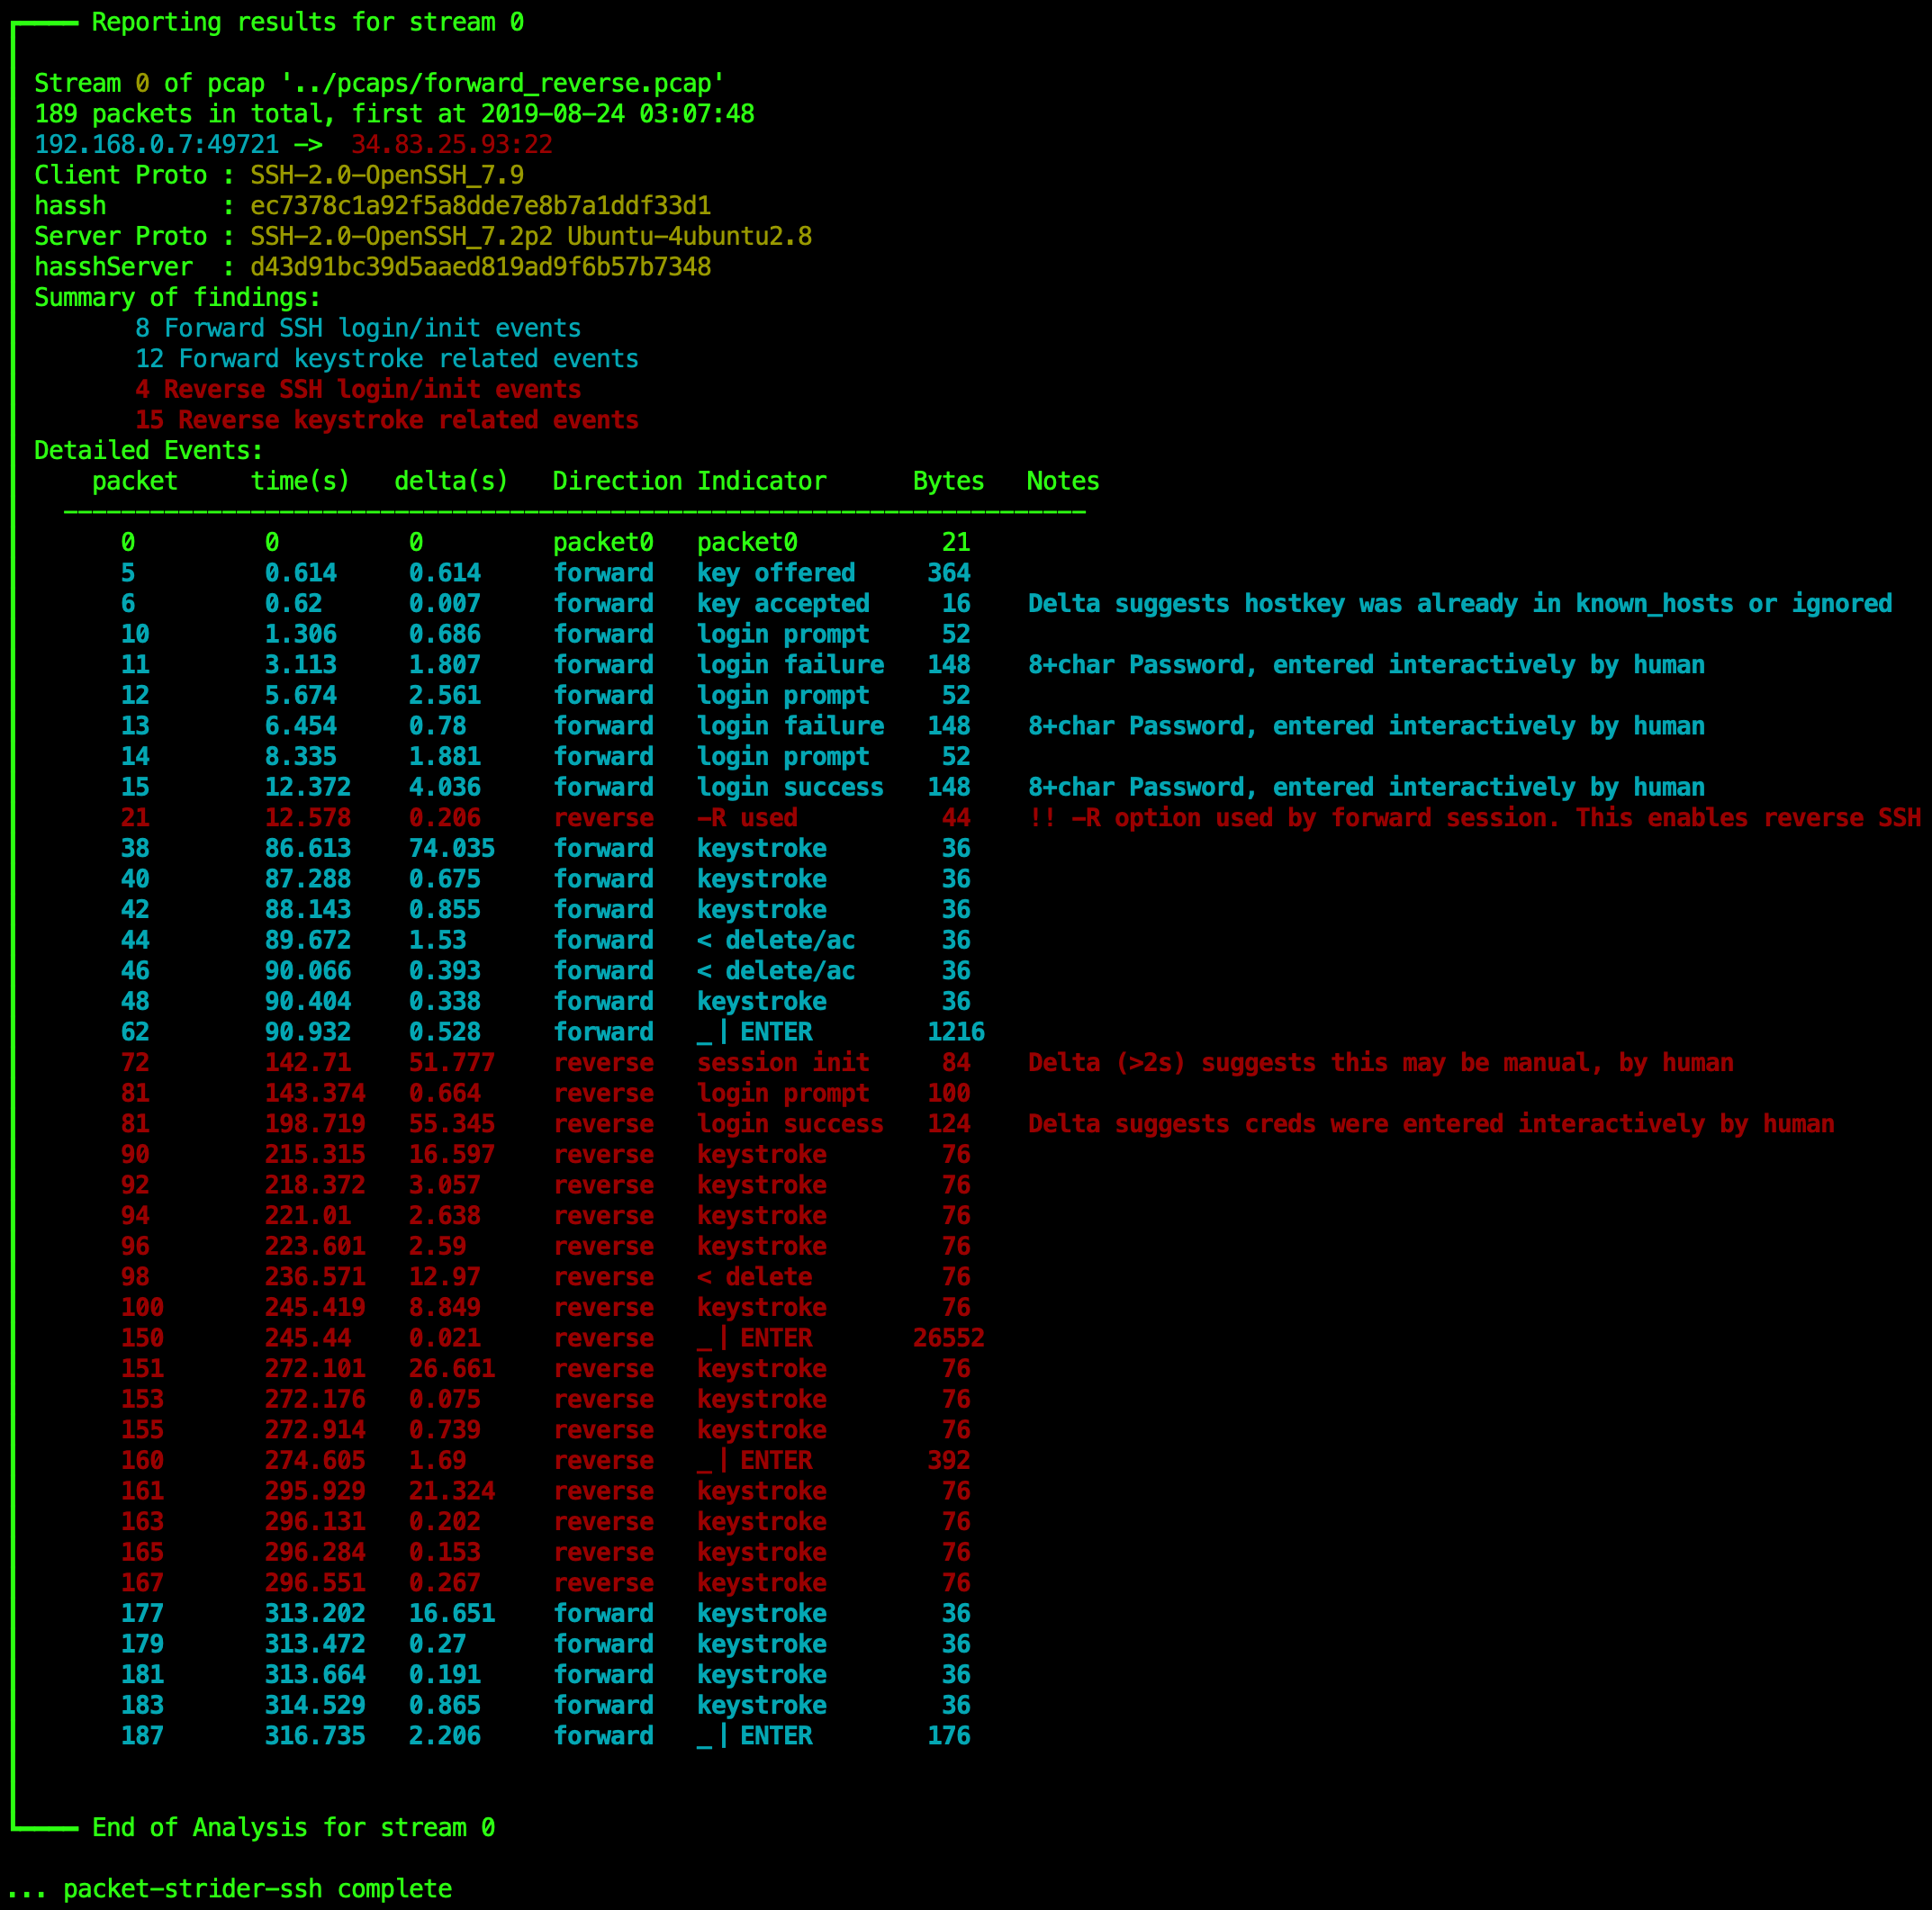 benjeems/packetstrider
A network packet forensics tool for SSH
 dowrighttv/dnxfirewall
DNXFIREWALL® and DAD'S NEXT-GEN FIREWALL™, a C/CPython hybrid next generation firewall built on top of Linux and bound to kernel/ netfilter hooks for…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 halildeniz/networkassessment
NetworkAssessment: Network Compromise Assessment Tool
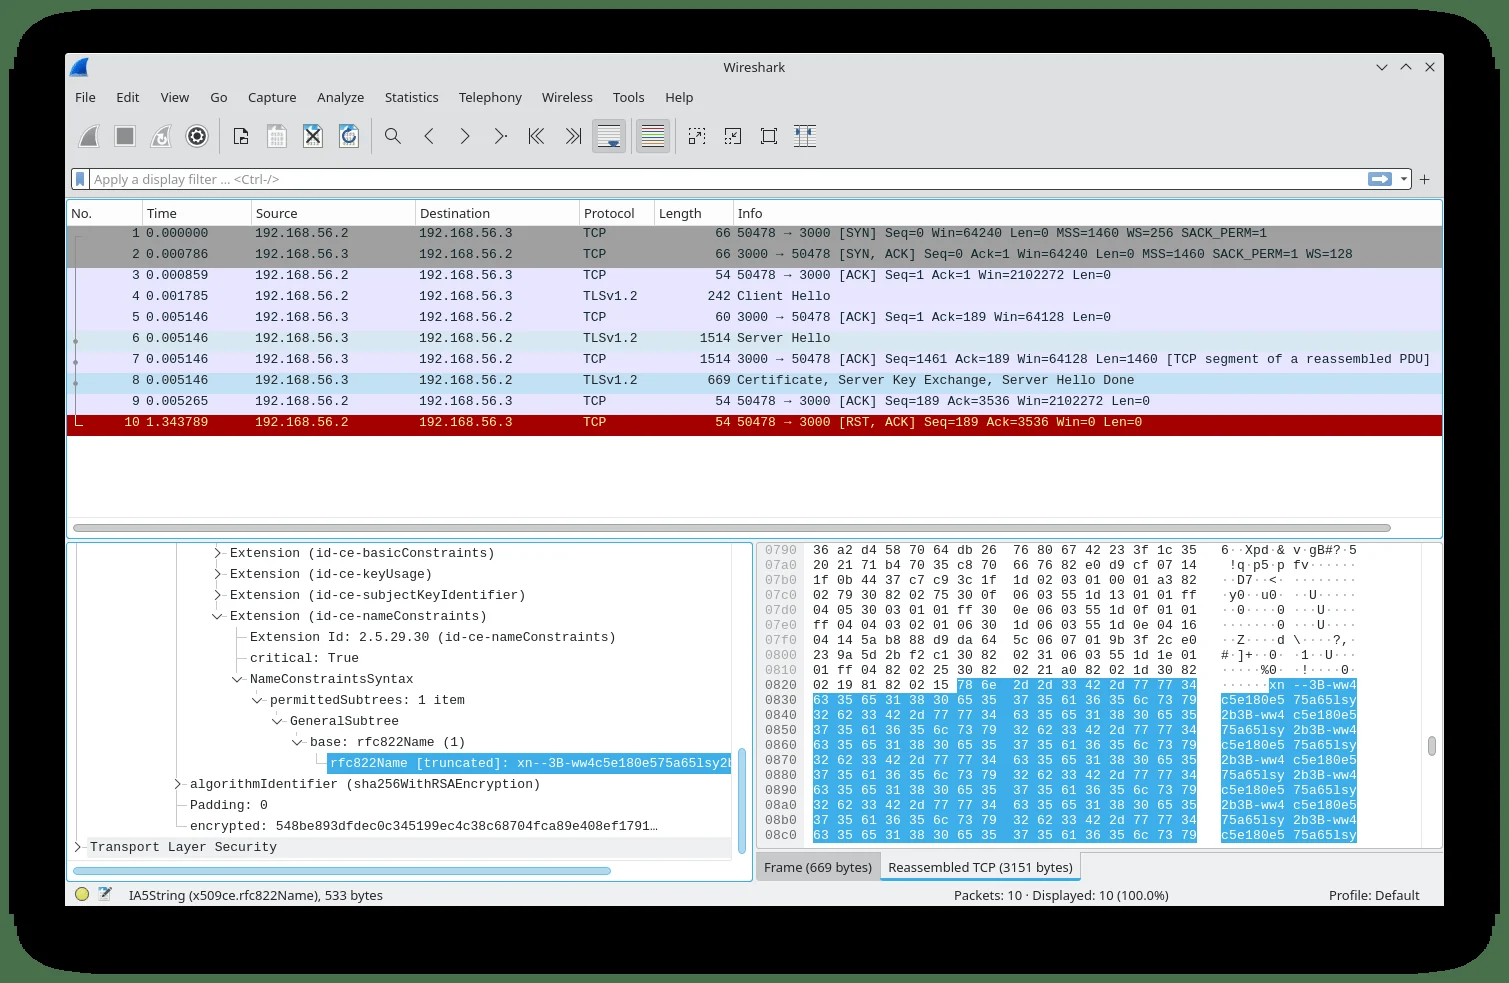 fox-it/spookyssl-pcaps
PCAPs and Suricata signatures for detecting OpenSSL CVE-2022-3602 exploitation attempts, including malicious client/server traffic and legitimate…
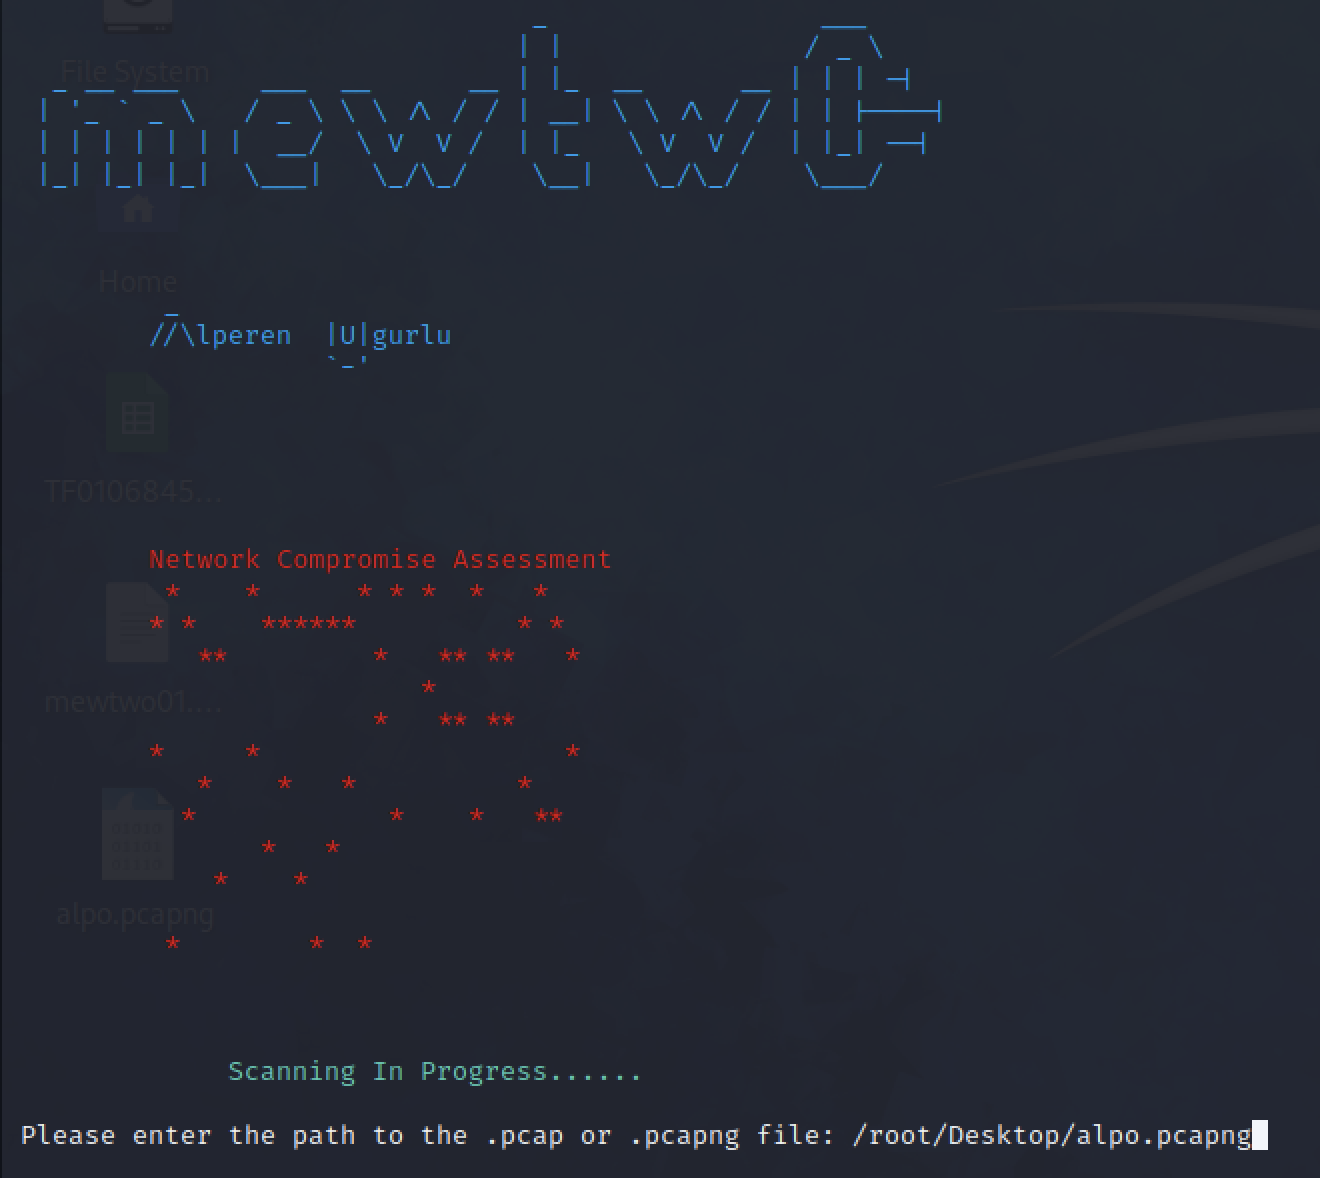 alperenugurlu/network_assessment
With Wireshark or TCPdump, you can determine whether there is harmful activity on your network traffic that you have recorded on the network you…
 rnehra01/arp-validator
Security Tool to detect arp poisoning attacks
 corelight/cve-2020-16898
A network detection package for CVE-2020-16898 (Windows TCP/IP Remote Code Execution Vulnerability)
 corelight/cve-2022-21907
Zeek package to detect CVE-2022-21907 HTTP exploit attempts by analyzing packet captures for malformed requests and triggering alerts.
 siddharth2440/network-detection-engine
Lightweight network intrusion detection engine capturing live traffic with libpcap. Detects SYN/ICMP floods, port scans, and signature-based web…
 dlee35/curveball_lua
Repo containing lua scripts and PCAP to find CVE-2020-0601 exploit attempts via network traffic