
packetfence
PacketFence is a fully supported, trusted, Free and Open Source network access control (NAC) solution. Boasting an impressive feature set including a…

PacketFence is a fully supported, trusted, Free and Open Source network access control (NAC) solution. Boasting an impressive feature set including a…

VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 15k CVEs

VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 15k CVEs

An open standard for hashing network flows into identifiers, a.k.a "Community IDs".

Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…

Arkime is an open source, large scale, full packet capturing, indexing, and database system.

Runs custom filters on Elasticsearch and alerts on matches

Elkeid is an open source solution that can meet the security requirements of various workloads such as hosts, containers and K8s, and serverless. It…

🛡️Awesome lists about all kinds of interesting topics of Wazuh XDR/SIEM

ModSecurity is an open source, cross platform web application firewall (WAF) engine for Apache, IIS and Nginx. It has a robust event-based…

StyleSmuggler (CVE-2026-75650) IOC toolkit for Magento Open Source and Adobe Commerce. Detect compromised stores, Rust implants, PHP web shells,…

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.

By Kprobe technology Open Source Host-based Intrusion Detection System(HIDS), from E_Bwill.

This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…

Detection signature repository providing YARA rules and threat-hunting content for identifying malware and malicious activity across enterprise…

JA4+ is a suite of network fingerprinting standards

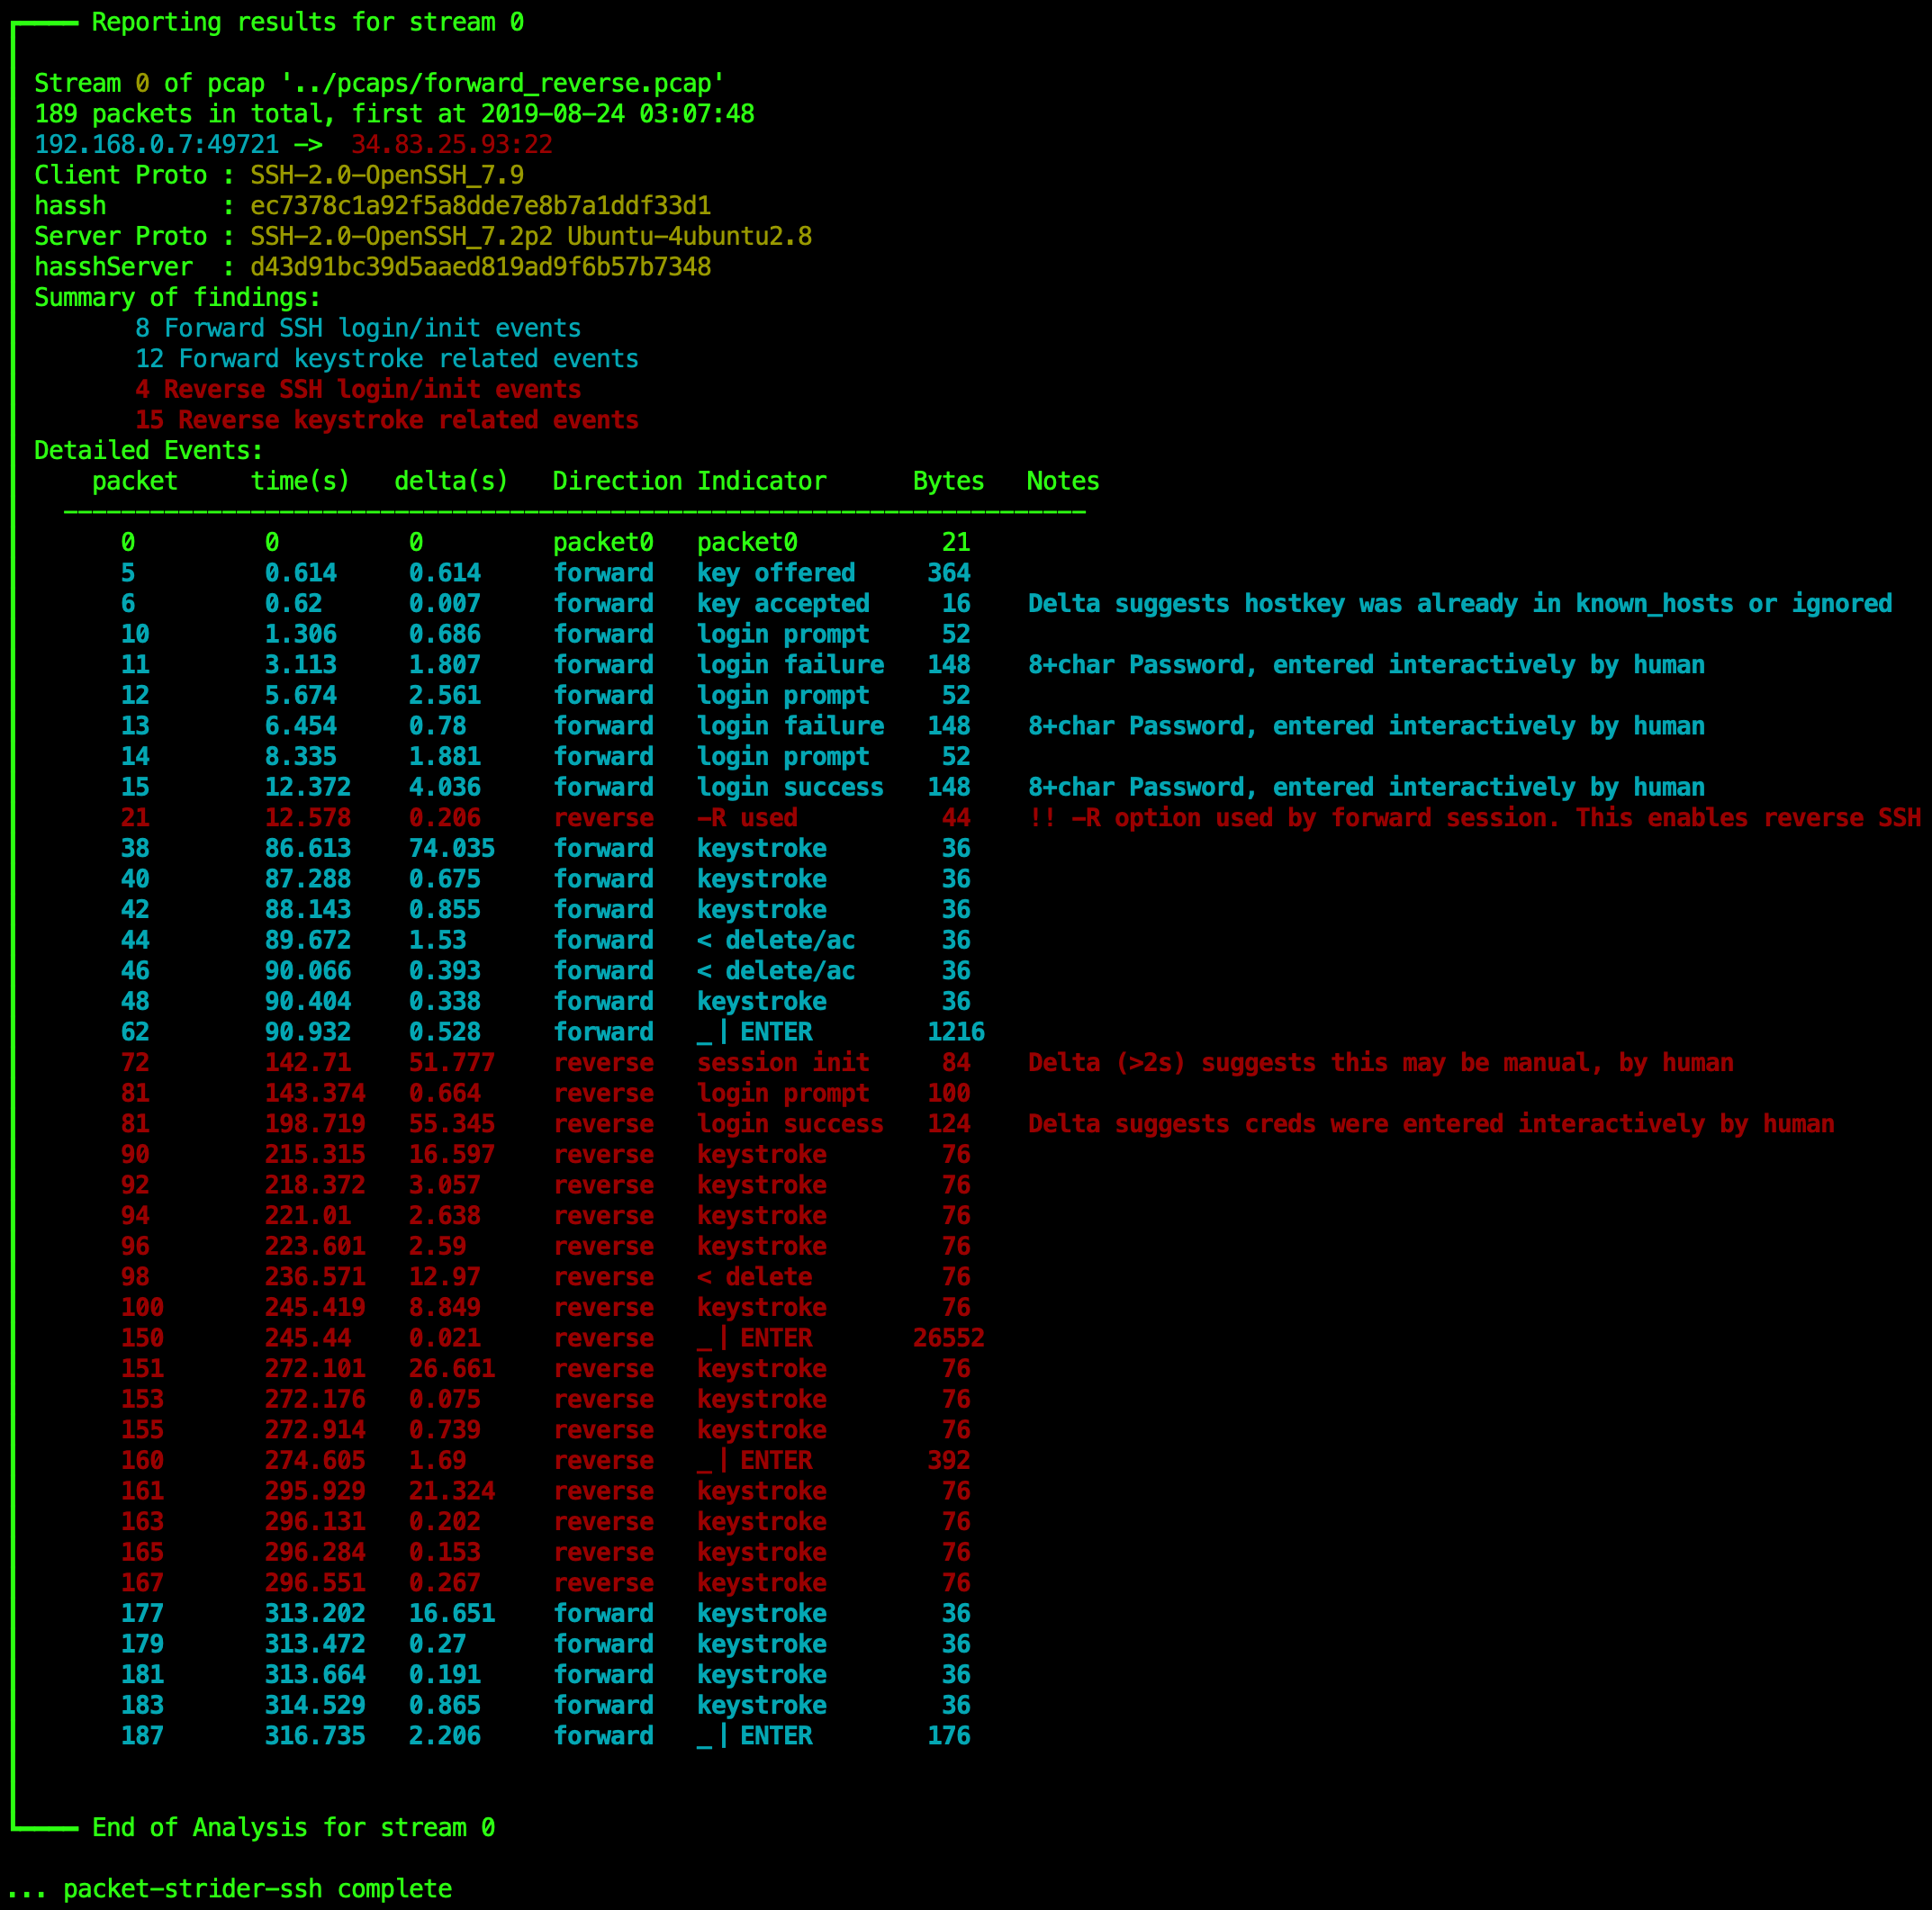
A network packet forensics tool for SSH