
Archived
GCTI
 chronicle/gcti
Detection signature repository providing YARA rules and threat-hunting content for identifying malware and malicious activity across enterprise…
defensive-toolsintrusion-detectionmalware-analysis+1
 sifalcon/detection
Curated collection of detection rules and IOCs extracted from DFIR engagements and malware analyses to support threat hunting, incident response, and…
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
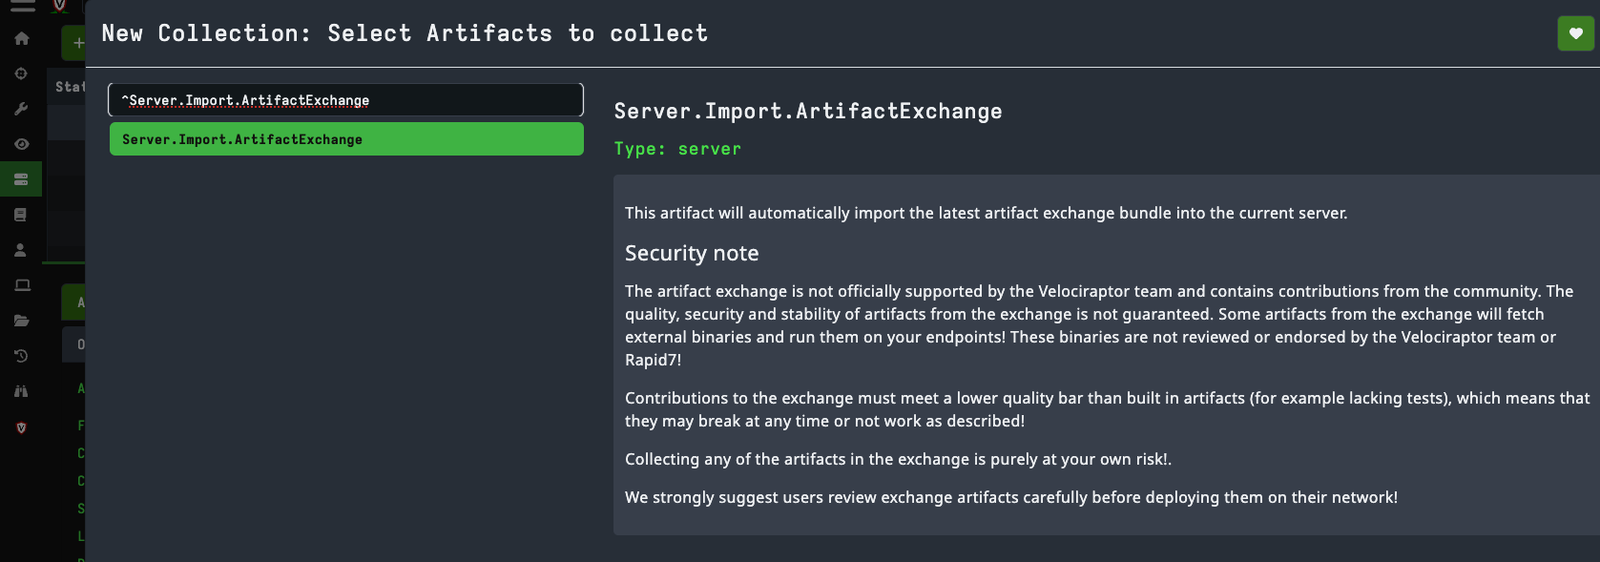 mgreen27/detectraptor
A repository to share publicly available Velociraptor detection content
 synacktiv/synacktiv-rules
Public repository of Sigma and YARA rules created by Synacktiv
 garethmsheldon/fortinet-fortiweb-fabric-connector-cve-2025-25257-detection
This repository provides production-ready detection engineering content for **CVE-2025-25257**, a pre-authentication SQL Injection vulnerability in…
 volexity/threat-intel
Signatures and IoCs from public Volexity blog posts.
 c3rb3ru5d3d53c/signatures
Community Detection Signature Build and Distribution Pipeline for YARA, Suricata, Snort and Sigma
 snyk/leaky-vessels-dynamic-detector
eBPF-based runtime detector for container breakout vulnerabilities in runc and Docker, monitoring syscalls and Docker daemon calls to detect…