Zeek-Intelligence-Feeds

Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…

Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…

A utility to safely generate malicious network traffic patterns and evaluate controls.

Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.

A collection of Tools and Rules for decoding Brute Ratel C4 badgers

A Zeek package to detect the Pingback malware ICMP tunnel command and control (C2) network traffic.

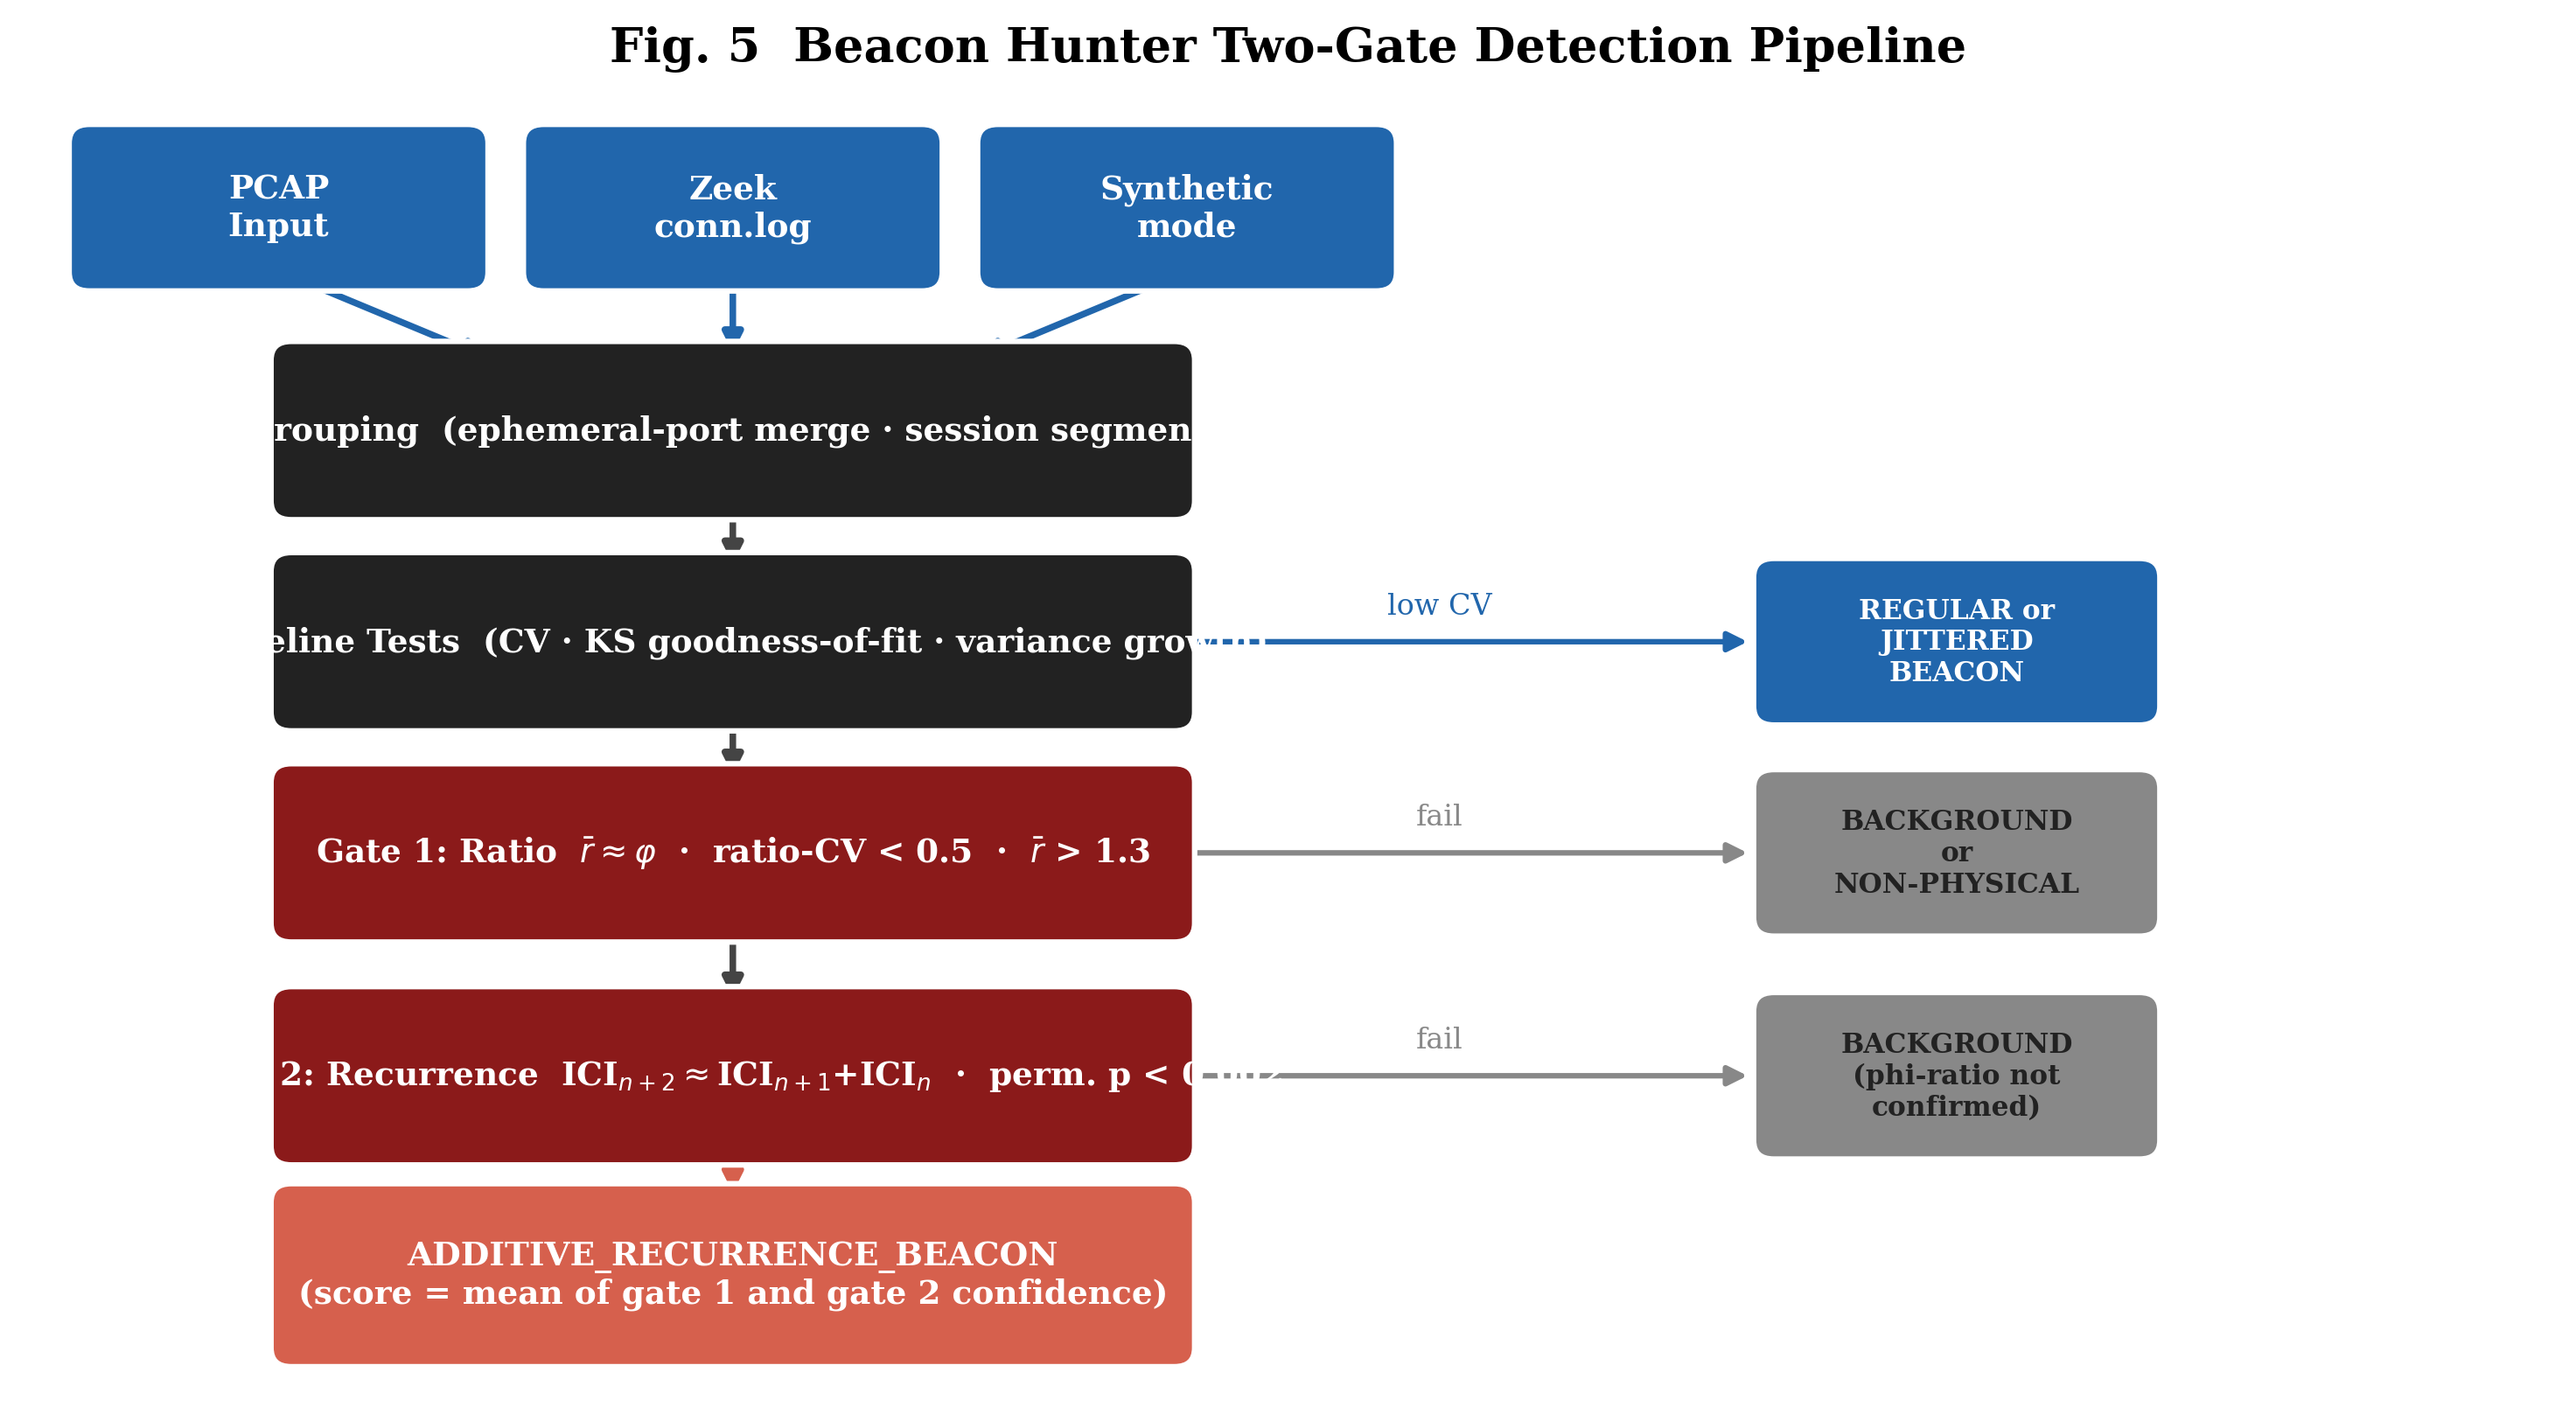
Detects phi-structured C2 beacons that evade RITA and standard regularity-based detectors

Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…

CVE-2026-24207 — NVIDIA Triton SageMaker auth bypass to unauth RCE. Detection script, bypass demo, RCE-chain PoC, and IDS rules.

Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE

Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…

C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel

Detection of Manjusaka C2 framework

A Zeek based AsyncRAT malware detector.

A Zeek based Mitre Caldera detector.

A Zeek protocol analyzer for the Facefish rootkit, based on Spicy.

Royal APT - APT15 - Related Information from NCC Group Cyber Defense Operations Research

A Zeek based NetSupport detector. NetSupport is often abused by attackers in malware.

A tool to assist with network-based hunting for GRU's Drovorub malware c2