
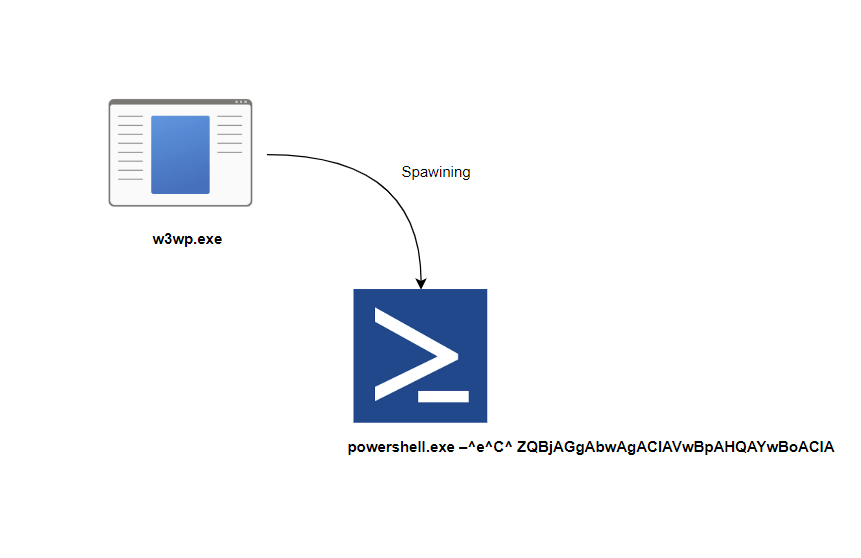
detection-validation
 alwashali/detection-validation
Detection rule validation
adversarial-attackdefensive-toolsintrusion-detection+1
alwashali/detection-validationDetection rule validation
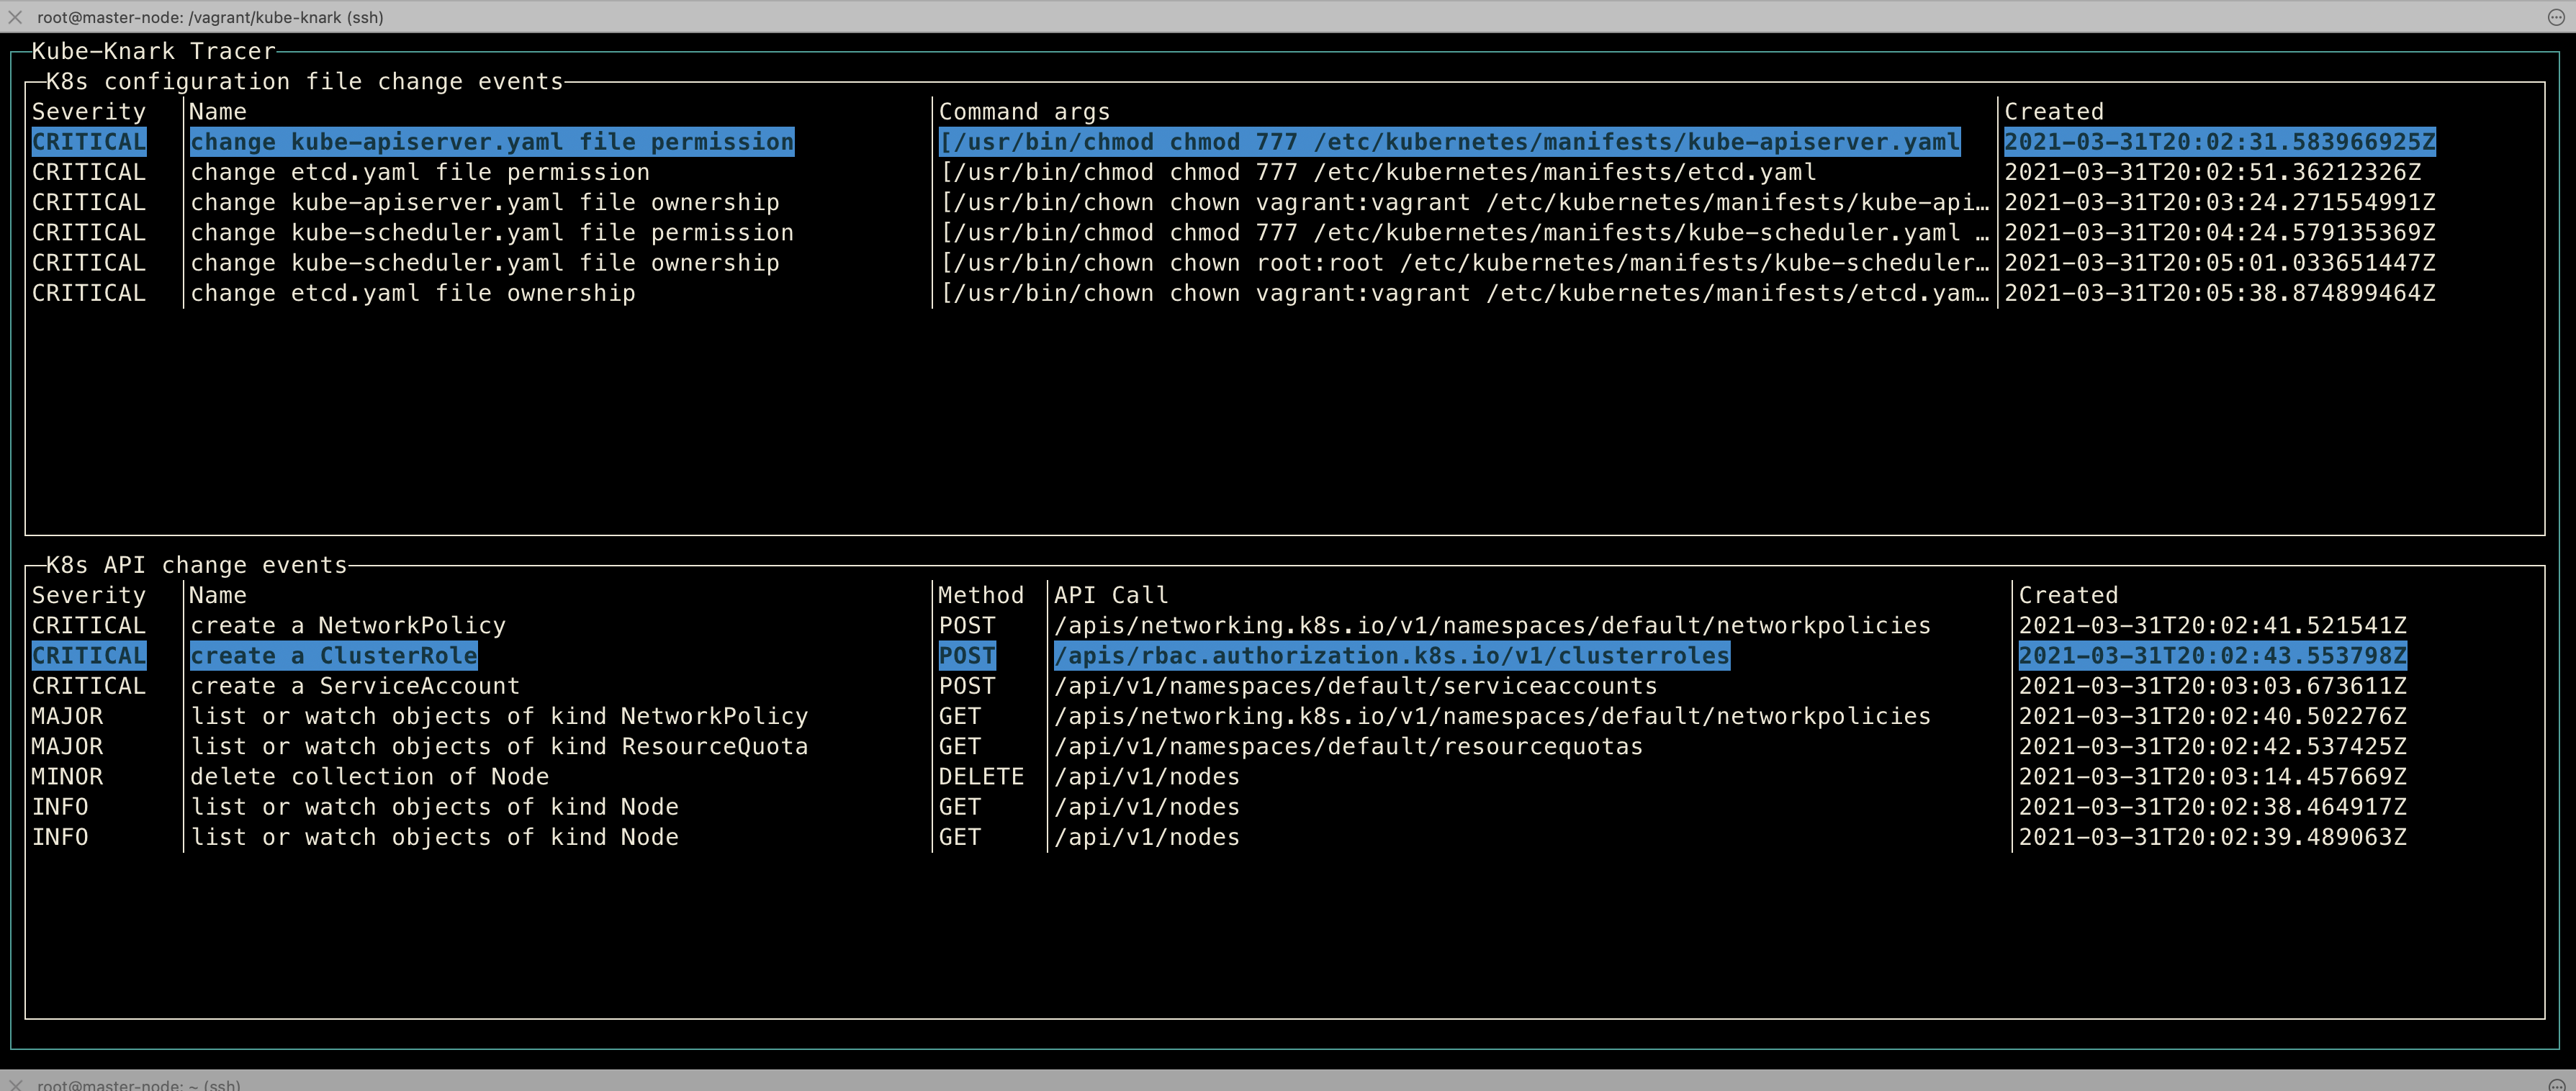 chen-keinan/kube-knark
Open Source runtime tool which help to detect malware code execution and run time mis-configuration change on a kubernetes cluster
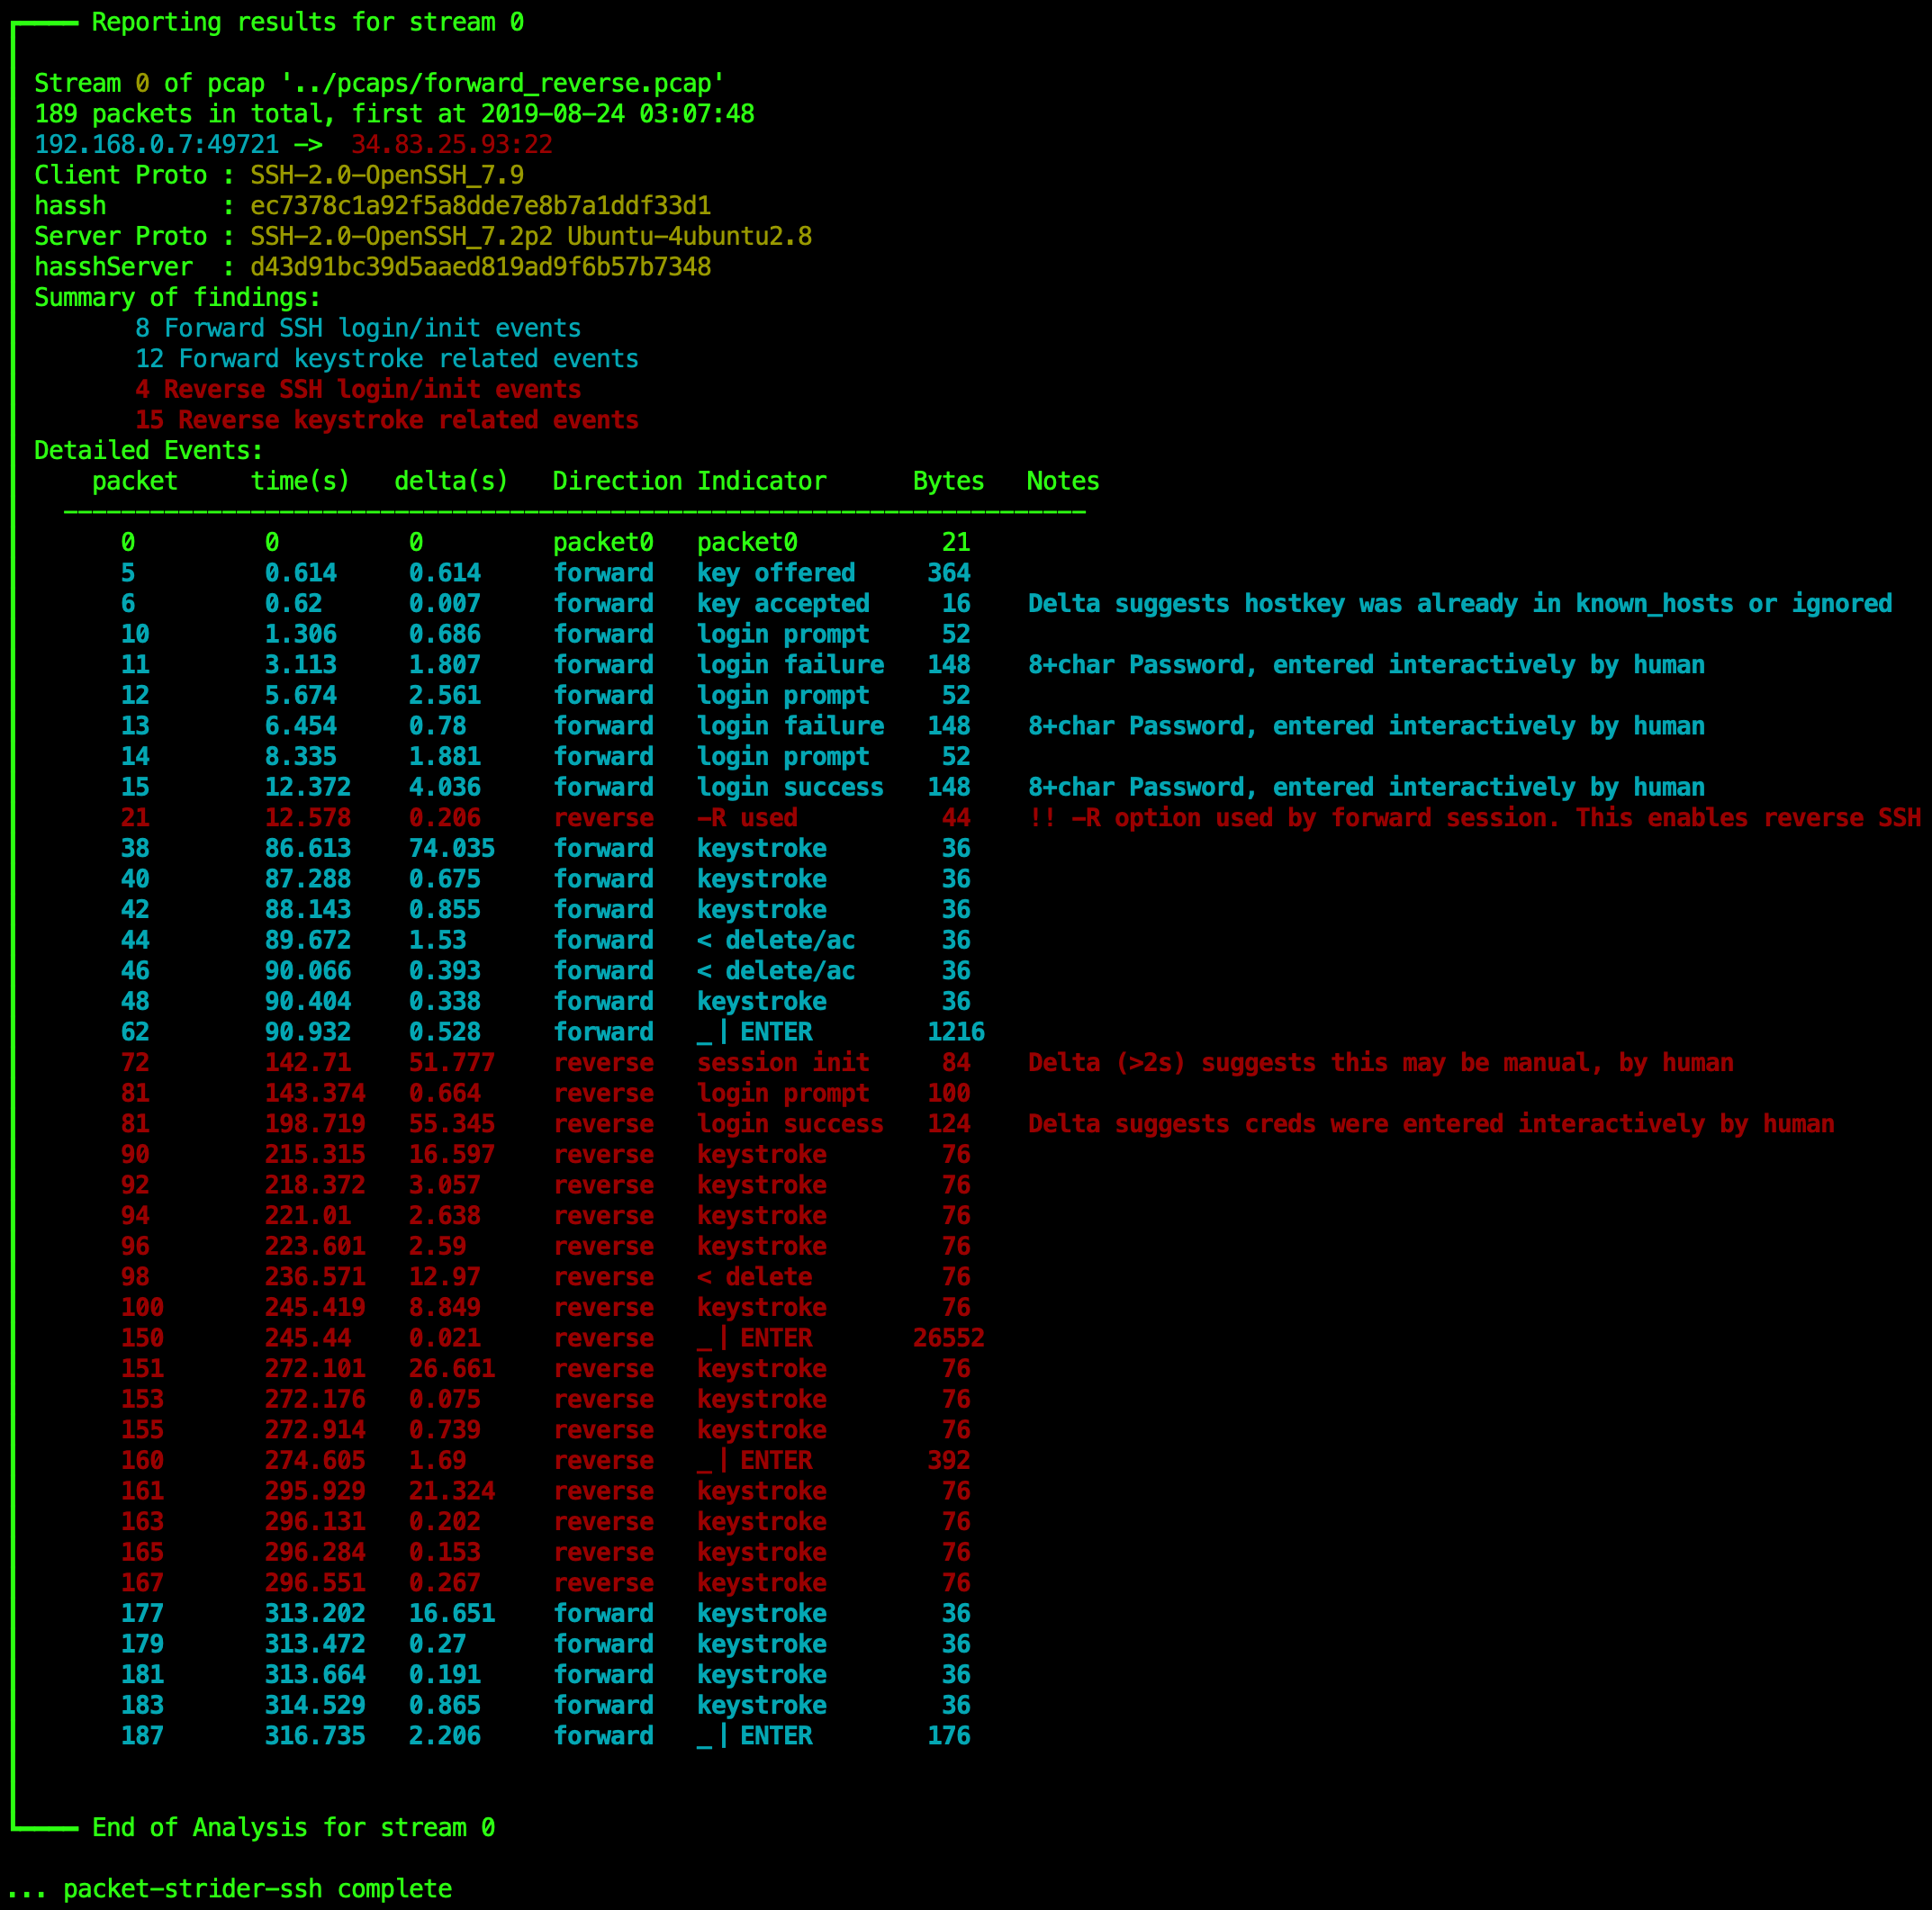 benjeems/packetstrider
A network packet forensics tool for SSH
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
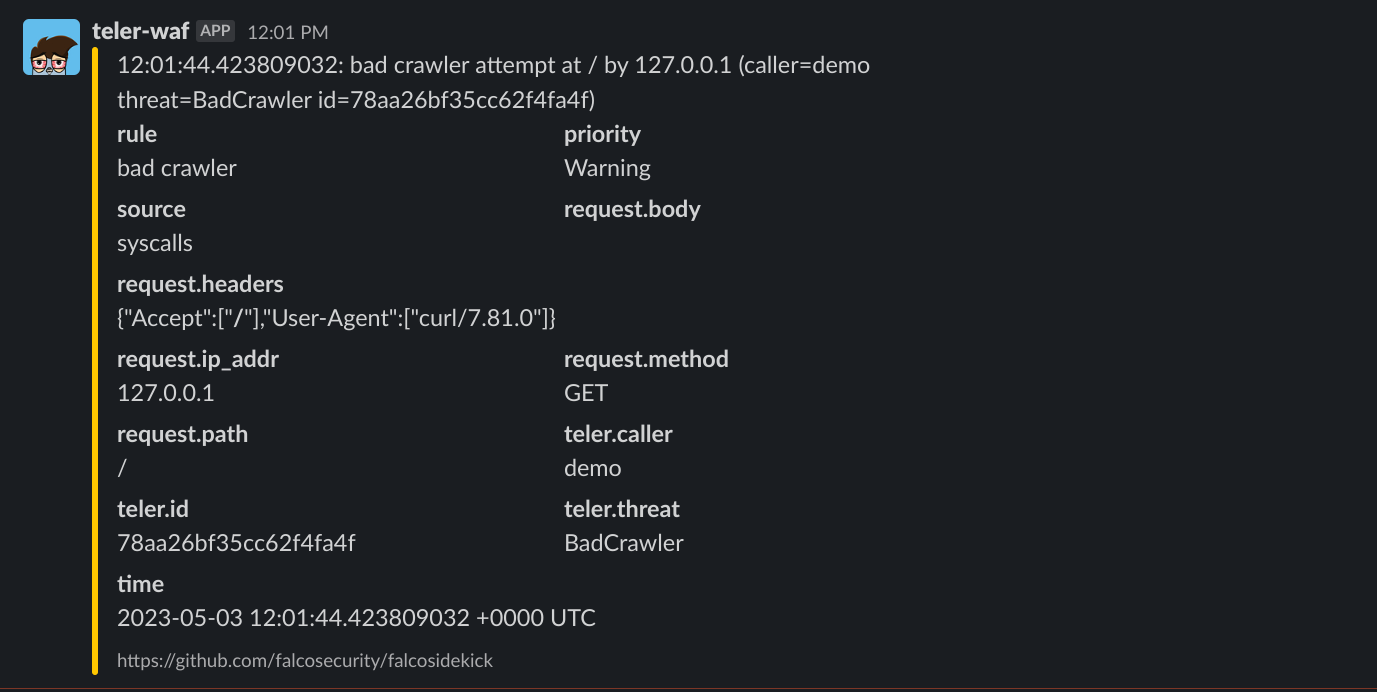 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
 r4j3sh-com/cve-2025-55182
Lightweight Go toolkit plus a Dockerized Next.js lab to explore and triage CVE-2025-55182.
 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 alphasoc/flightsim
A utility to safely generate malicious network traffic patterns and evaluate controls.
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 andreicscs/honeywire
Open-source deception platform that turns any Linux machine into a high-signal canary. Deploy tripwire sensors on files, ports, and network services…
 corelight/go-zeek-broker-ws
A Go library for using zeek broker's websocket API
 snyk/leaky-vessels-dynamic-detector
eBPF-based runtime detector for container breakout vulnerabilities in runc and Docker, monitoring syscalls and Docker daemon calls to detect…
 cyb3rmik3/kql-threat-hunting-queries
A repository of KQL queries focused on threat hunting and threat detecting for Microsoft Sentinel & Microsoft XDR (Former Microsoft 365 Defender).
 metlo-labs/metlo
Metlo is an open-source API security platform.
 0x4d31/galah
Galah: An LLM-powered web honeypot.
 gui774ume/krie
Linux Kernel Runtime Integrity with eBPF
 c3rb3ru5d3d53c/signatures
Community Detection Signature Build and Distribution Pipeline for YARA, Suricata, Snort and Sigma
 corelight/elasticsearch_rules
Elastic version of SOC prime watcher rules