suricata-vedas
 arpsyndicate/suricata-vedas
VEDAS-Driven Autonomous Generation of Suricata Rules for CVEs
exploit-frameworksintrusion-detectionmachine-learning+2
20
arpsyndicate/suricata-vedasVEDAS-Driven Autonomous Generation of Suricata Rules for CVEs
 mahdi13830510/cve-2026-31431-mitigation-suite
Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…
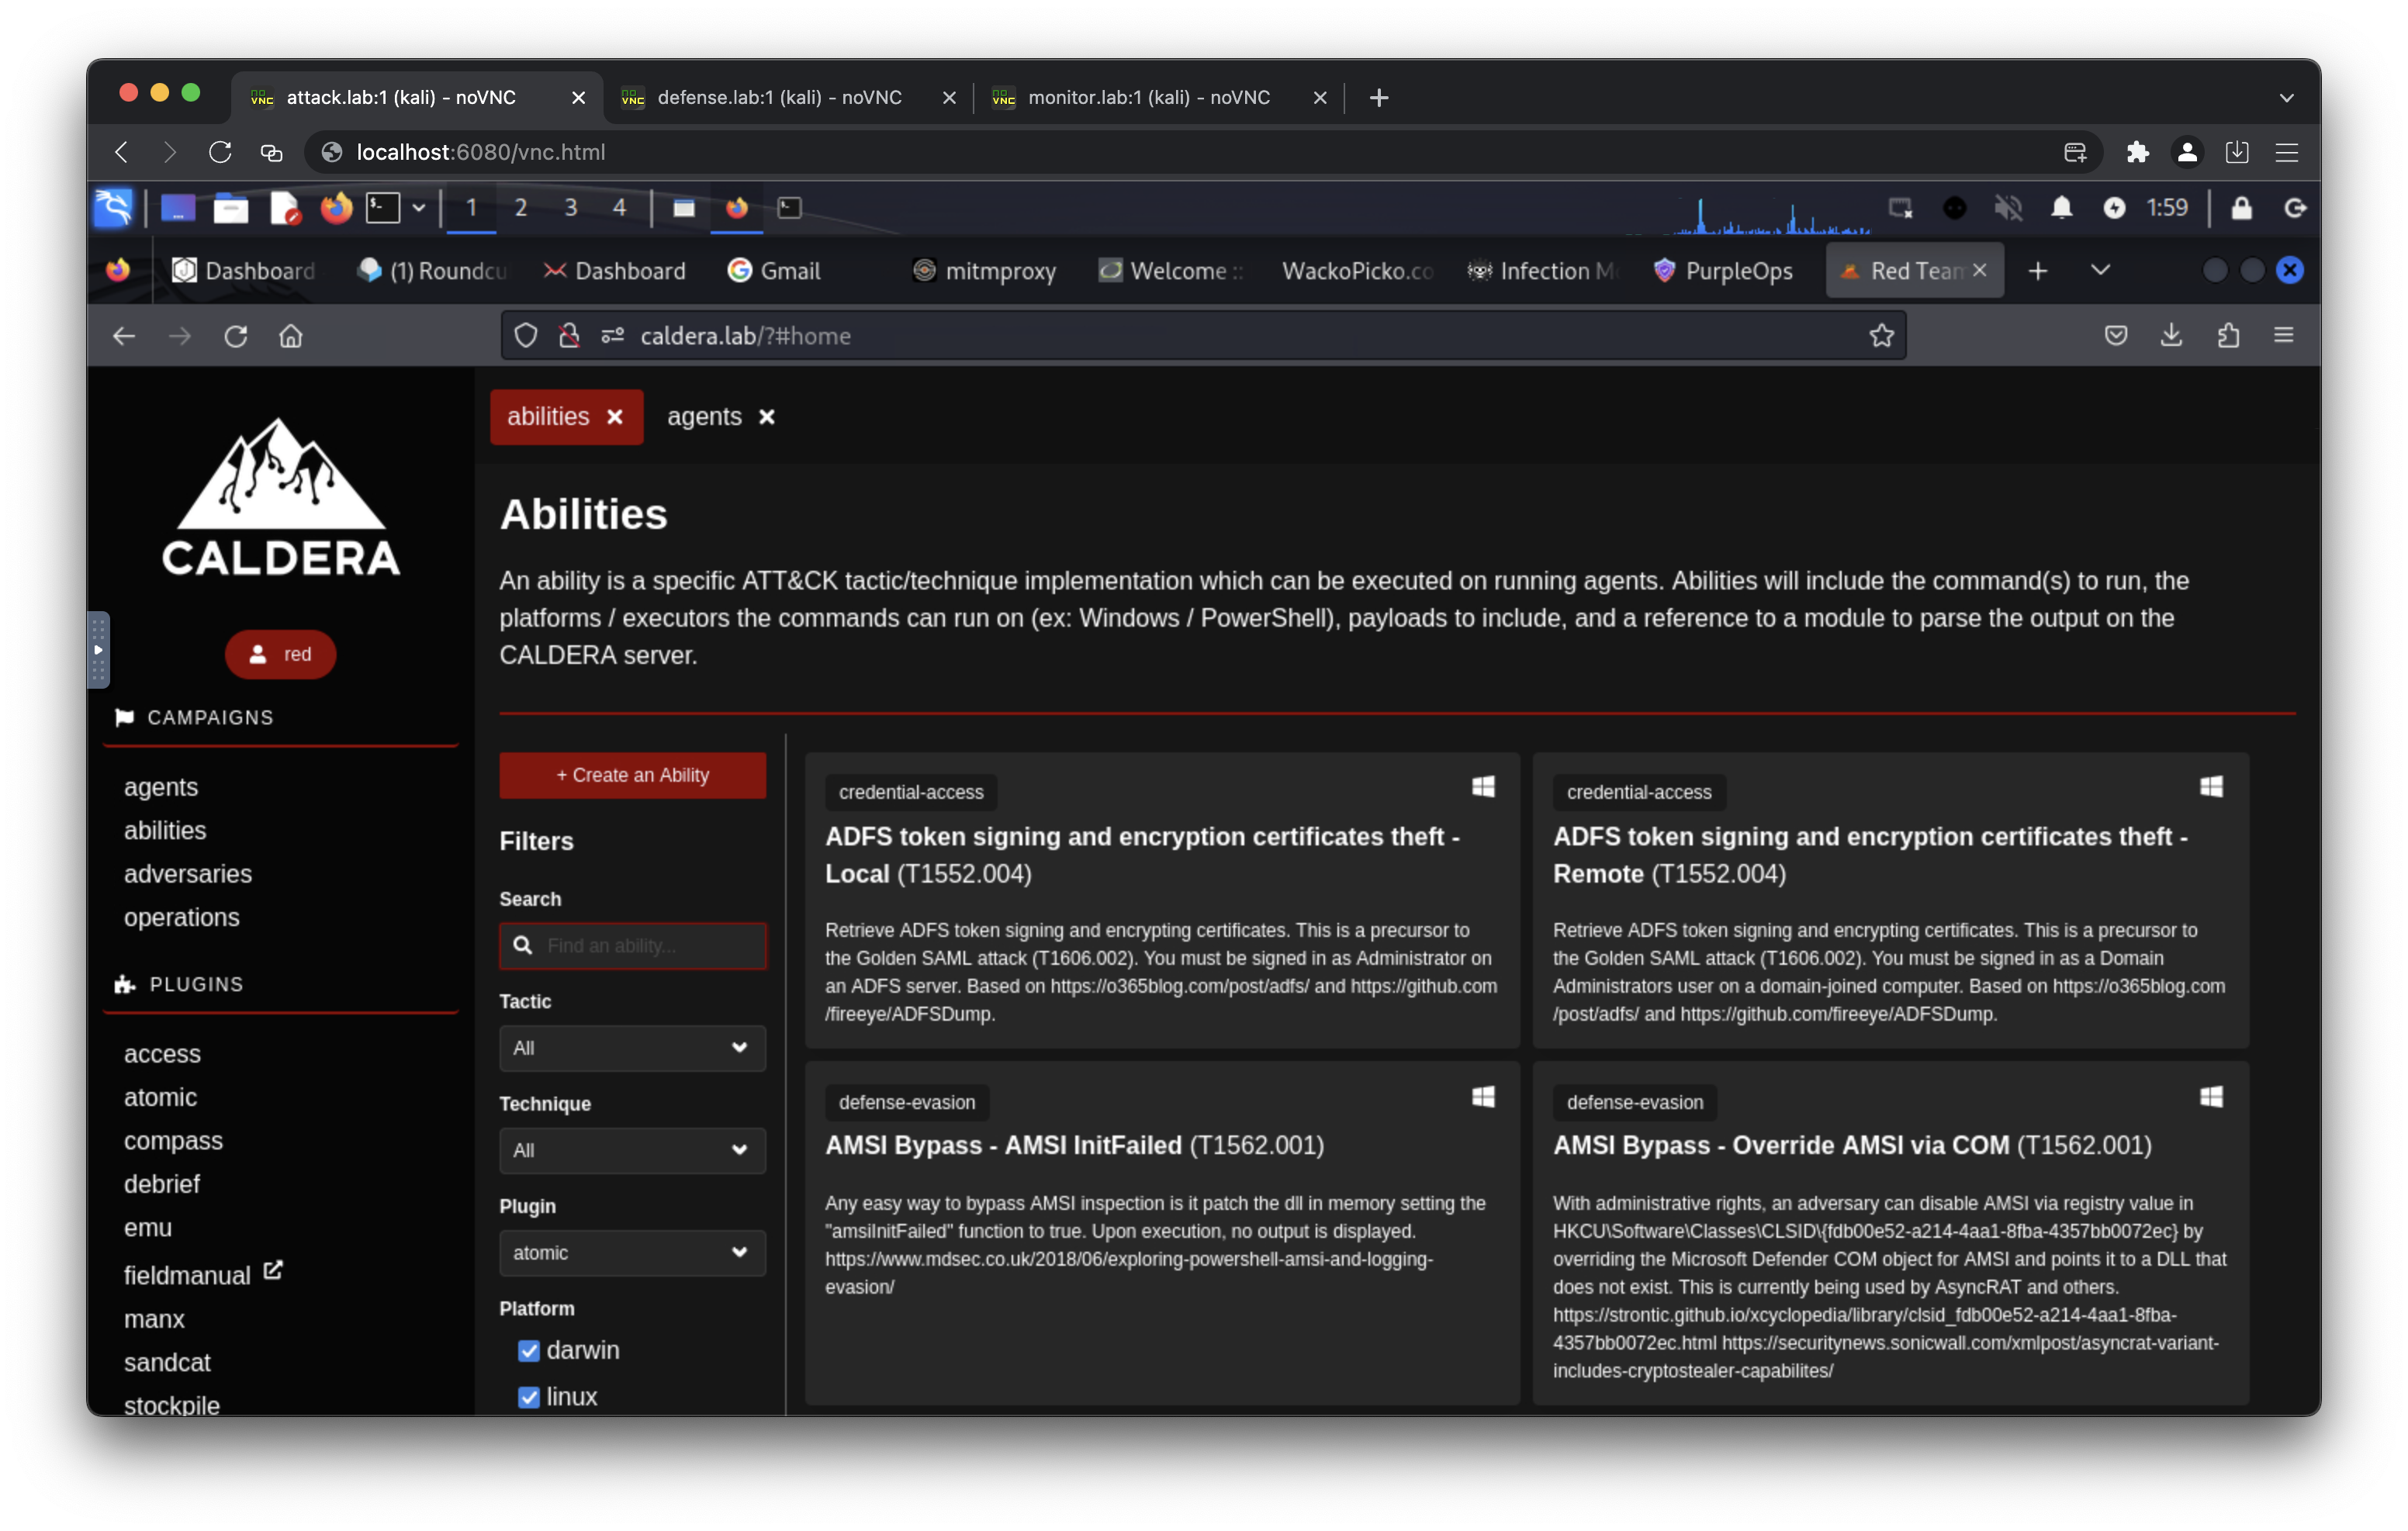
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 azdevops143/fragnesia-charan-cve-2026-46300
Hardened container staging framework with seccomp syscall whitelisting and eBPF telemetry to detect and block container escape and kernel ULP…
 nerium-security/cve-2025-55182
Host-based detection rules for the RCE vulnerability in the React JavaScript framework.
 daryllundy/cve-2025-32463
Detection framework for CVE-2025-32463 sudo privilege escalation vulnerability. Provides real-time monitoring, forensic analysis, and SIEM…