
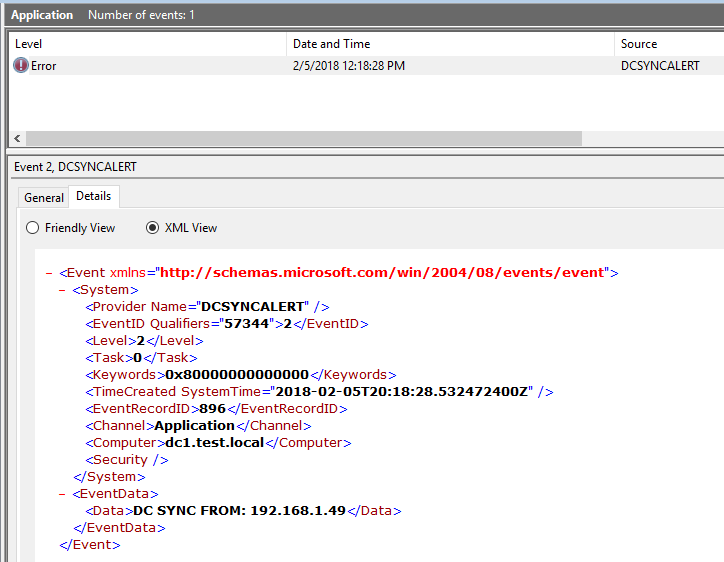
DCSYNCMonitor
 shellster/dcsyncmonitor
Monitors for DCSYNC and DCSHADOW attacks and create custom Windows Events for these events.
defensive-toolsincident-responseintrusion-detection+1
140
shellster/dcsyncmonitorMonitors for DCSYNC and DCSHADOW attacks and create custom Windows Events for these events.
 runreveal/sigmalite
Go library for parsing and executing Sigma detection rules against log entries, supporting field modifiers, CIDR matching, and custom field resolvers…
 nccgroup/reactor
Runs custom filters on Elasticsearch and alerts on matches
 te0rwx/cve-2025-32433-detection
Custom YARA rule for detecting artifacts of CVE-2025-32433, an Erlang/OTP SSH pre-authentication RCE vulnerability. Validated against public PoCs and…
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 orevic21/wazuh-home-soc
Wazuh + Suricata SOC lab detecting real exploits (CVE-2011-2523) and brute-force attacks, with custom detection rules for gaps in default IDS…
 taisa456/network-security-snort
Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…
 0warn/defender
This is a bash script focus on hardening linux. This is a custom think of windows defender but unlike of their privacy issue. User can feel freedom…
 nosie12/fire-wall-server
Python-based simulated firewall to detect and block Spring4Shell (CVE-2022-22965) exploit attempts. This project filters HTTP requests by identifying…
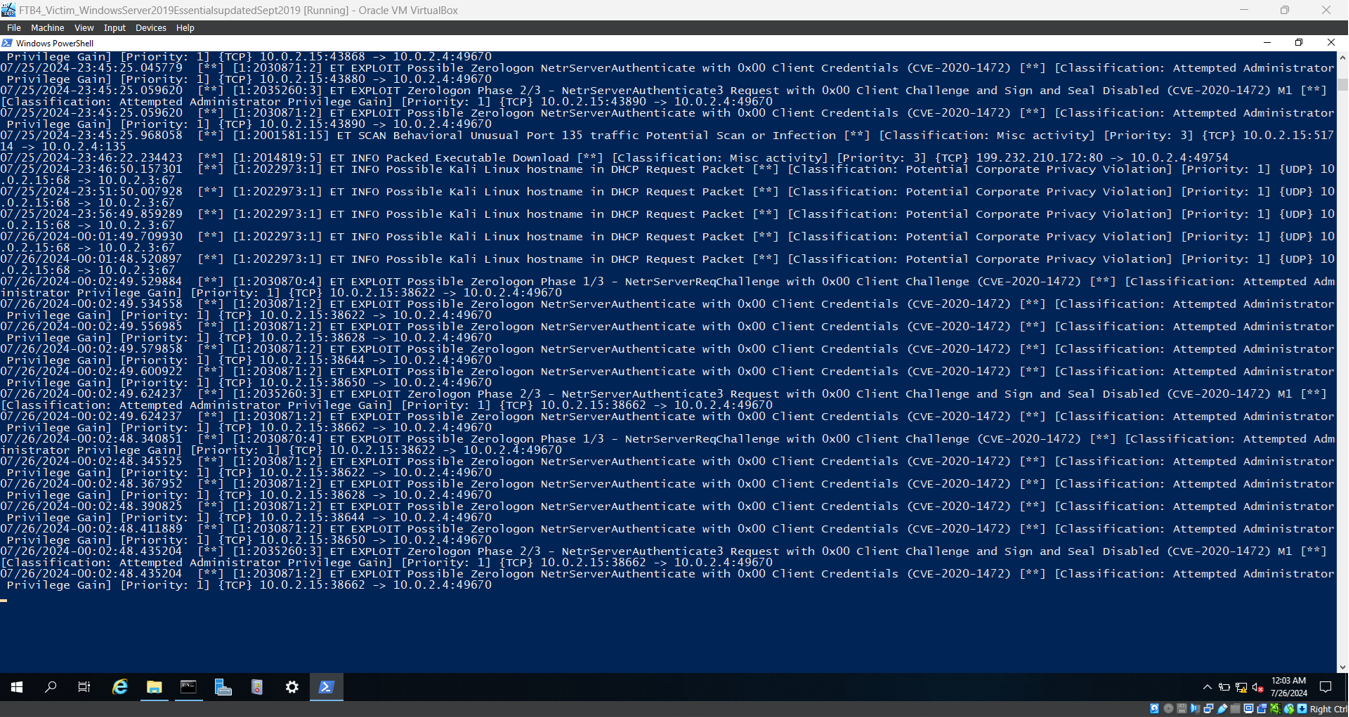 tdevworks/cve-2020-1472-zerologon-demo-detection-mitigation
Educational demo of CVE-2020-1472 (ZeroLogon) detection using Windows Event Logs and Suricata IDS, plus mitigation via Windows Updates. Includes…
 ma111e/melody
Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.
 blackhillsinfosec/eventlogging
Automation scripts to deploy Windows Event Forwarding, Sysmon, and custom audit policies in an Active Directory environment.
 corelight/icanntld
Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 17patmaks/my-sigma-rule-collection
Sigma Rule for CVE-2025-49666
 sigmahq/pysigma
Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)
 thomaspatzke/log4pot
A honeypot for the Log4Shell vulnerability (CVE-2021-44228).