

zeek-quasarrat-detector
 corelight/zeek-quasarrat-detector
Zeek detector for QuasarRat
anomaly-detectionintrusion-detectionmalware-analysis+2
3
corelight/zeek-quasarrat-detectorZeek detector for QuasarRat
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.
 corelight/pingback
A Zeek package to detect the Pingback malware ICMP tunnel command and control (C2) network traffic.
 sigmahq/sigma-cli
The Sigma command line interface based on pySigma
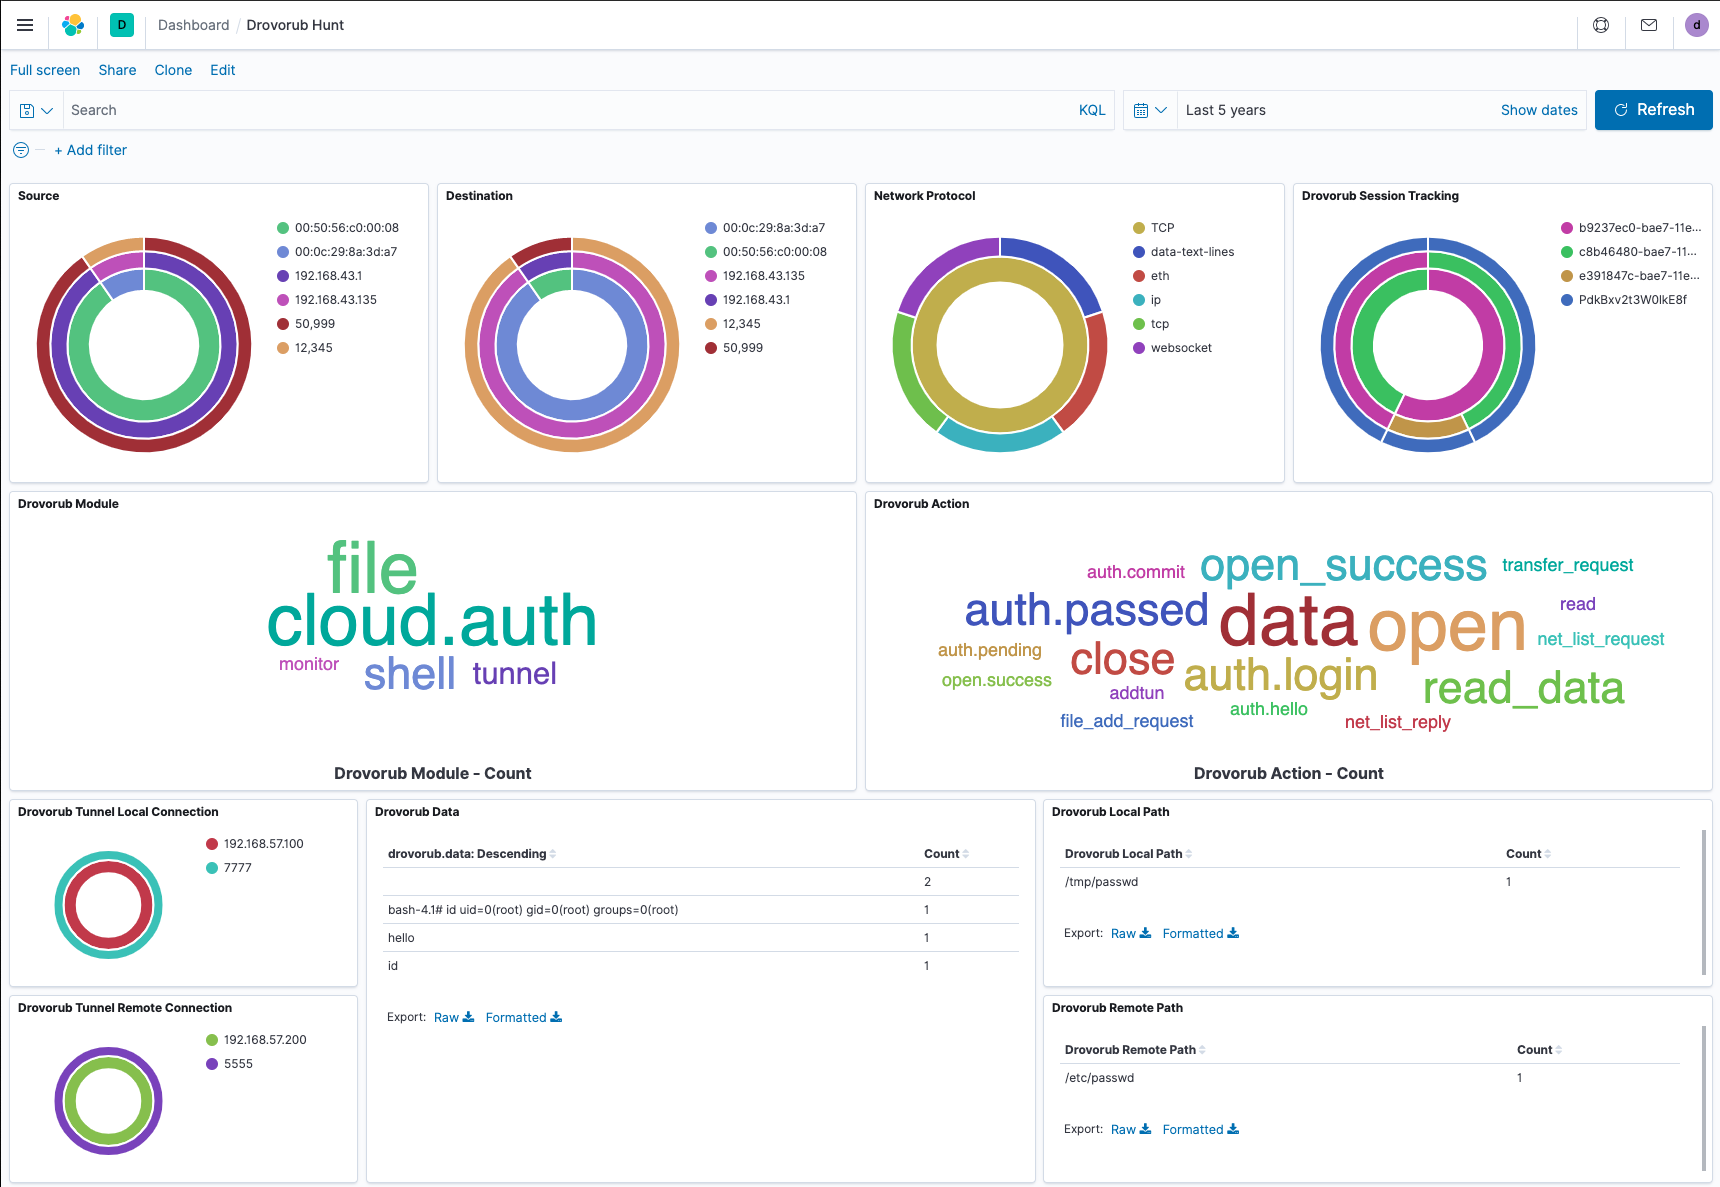 insane-forensics/drovorub-hunt
A tool to assist with network-based hunting for GRU's Drovorub malware c2
 u1tr0nex/cve-2022-30190-follina-lab
Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE
 sans-blue-team/deepbluecli
PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 corelight/corelight-ansible-roles
Corelight-Ansible-Roles are a collection of Ansible Roles and playbooks that install, configure, run and manage a variety of Corelight, Suricata and…
 alphasoc/flightsim
A utility to safely generate malicious network traffic patterns and evaluate controls.
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
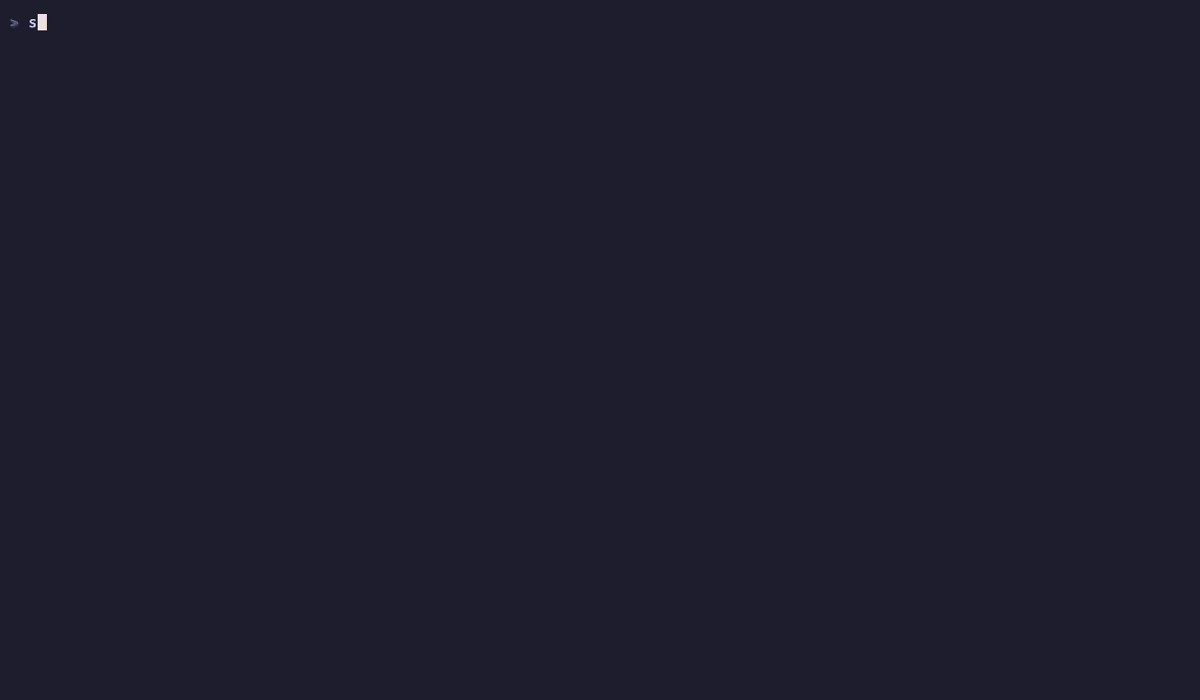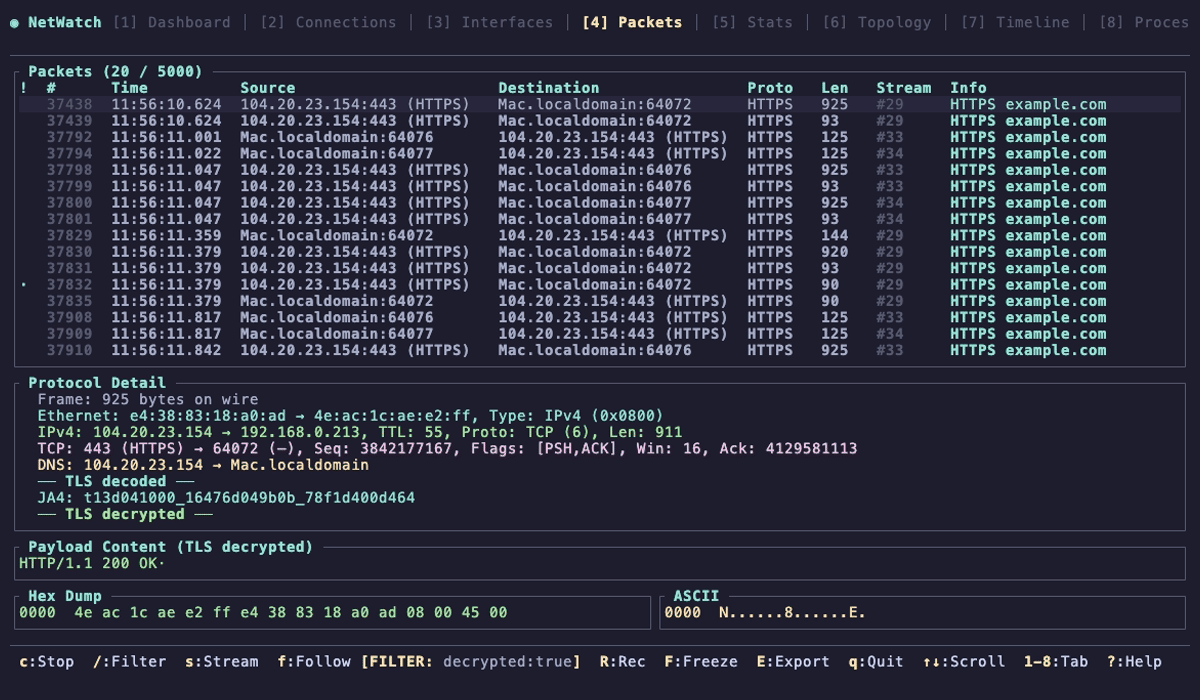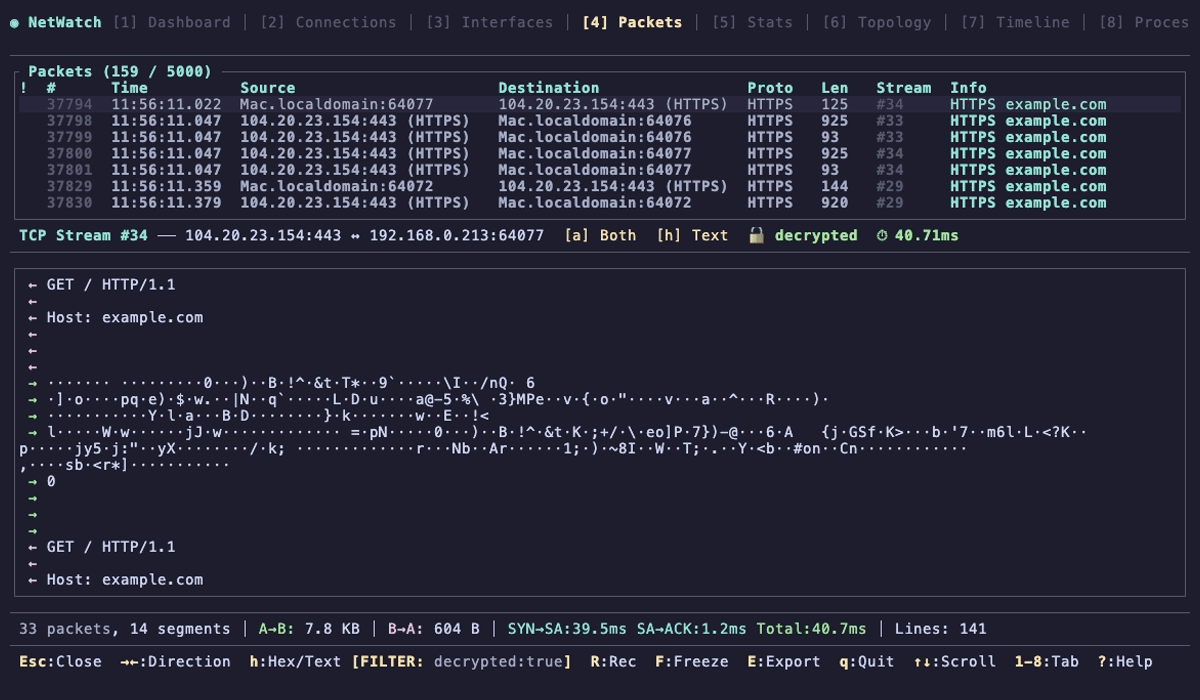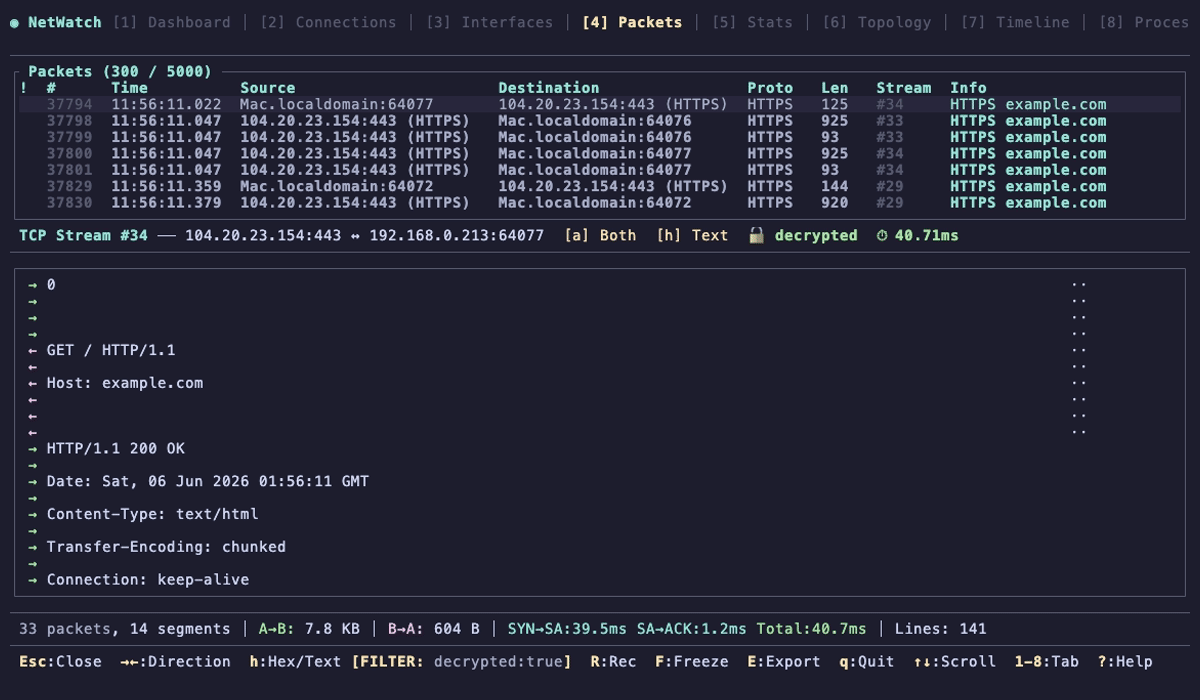 matthart1983/netwatch
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
 backbay-labs/thrunt-god
Threat hunting command system for agentic IDEs
 immersive-labs-sec/bruteratel-detectiontools
A collection of Tools and Rules for decoding Brute Ratel C4 badgers
 zam89/cve-2024-3400-pot
Simple honeypot for CVE-2024-3400 Palo Alto PAN-OS Command Injection Vulnerability
 corelight/c2-detection-manjusaka
Detection of Manjusaka C2 framework
 infokom-ki/zimbra-cve-2026-73570-rules
Wazuh detection rules for CVE-2026-73570, an OS command injection in Zimbra Collaboration Suite, monitoring web access logs and zimbra.log for…
 adnansiyat/how-to-patch-cve-2025-32709
Real-world patching workflow for CVE-2025-32709. From hotfix install to SIEM alert validation—this repo documents every step with screenshots,…