leaky-vessels-dynamic-detector
eBPF-based runtime detector for container breakout vulnerabilities in runc and Docker, monitoring syscalls and Docker daemon calls to detect…

eBPF-based runtime detector for container breakout vulnerabilities in runc and Docker, monitoring syscalls and Docker daemon calls to detect…

Sigma Rules Engine inside the Linux Kernel using eBPF. Focusing on prevention capabilities

Dockerized honeypot for CVE-2021-44228.

SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.

Open-source deception platform that turns any Linux machine into a high-signal canary. Deploy tripwire sensors on files, ports, and network services…

PoC and Detection for CVE-2024-21626

eBPF-based runtime security agent for Kubernetes that detects unknown processes and file changes, enforces pre-registered constraints, and automates…

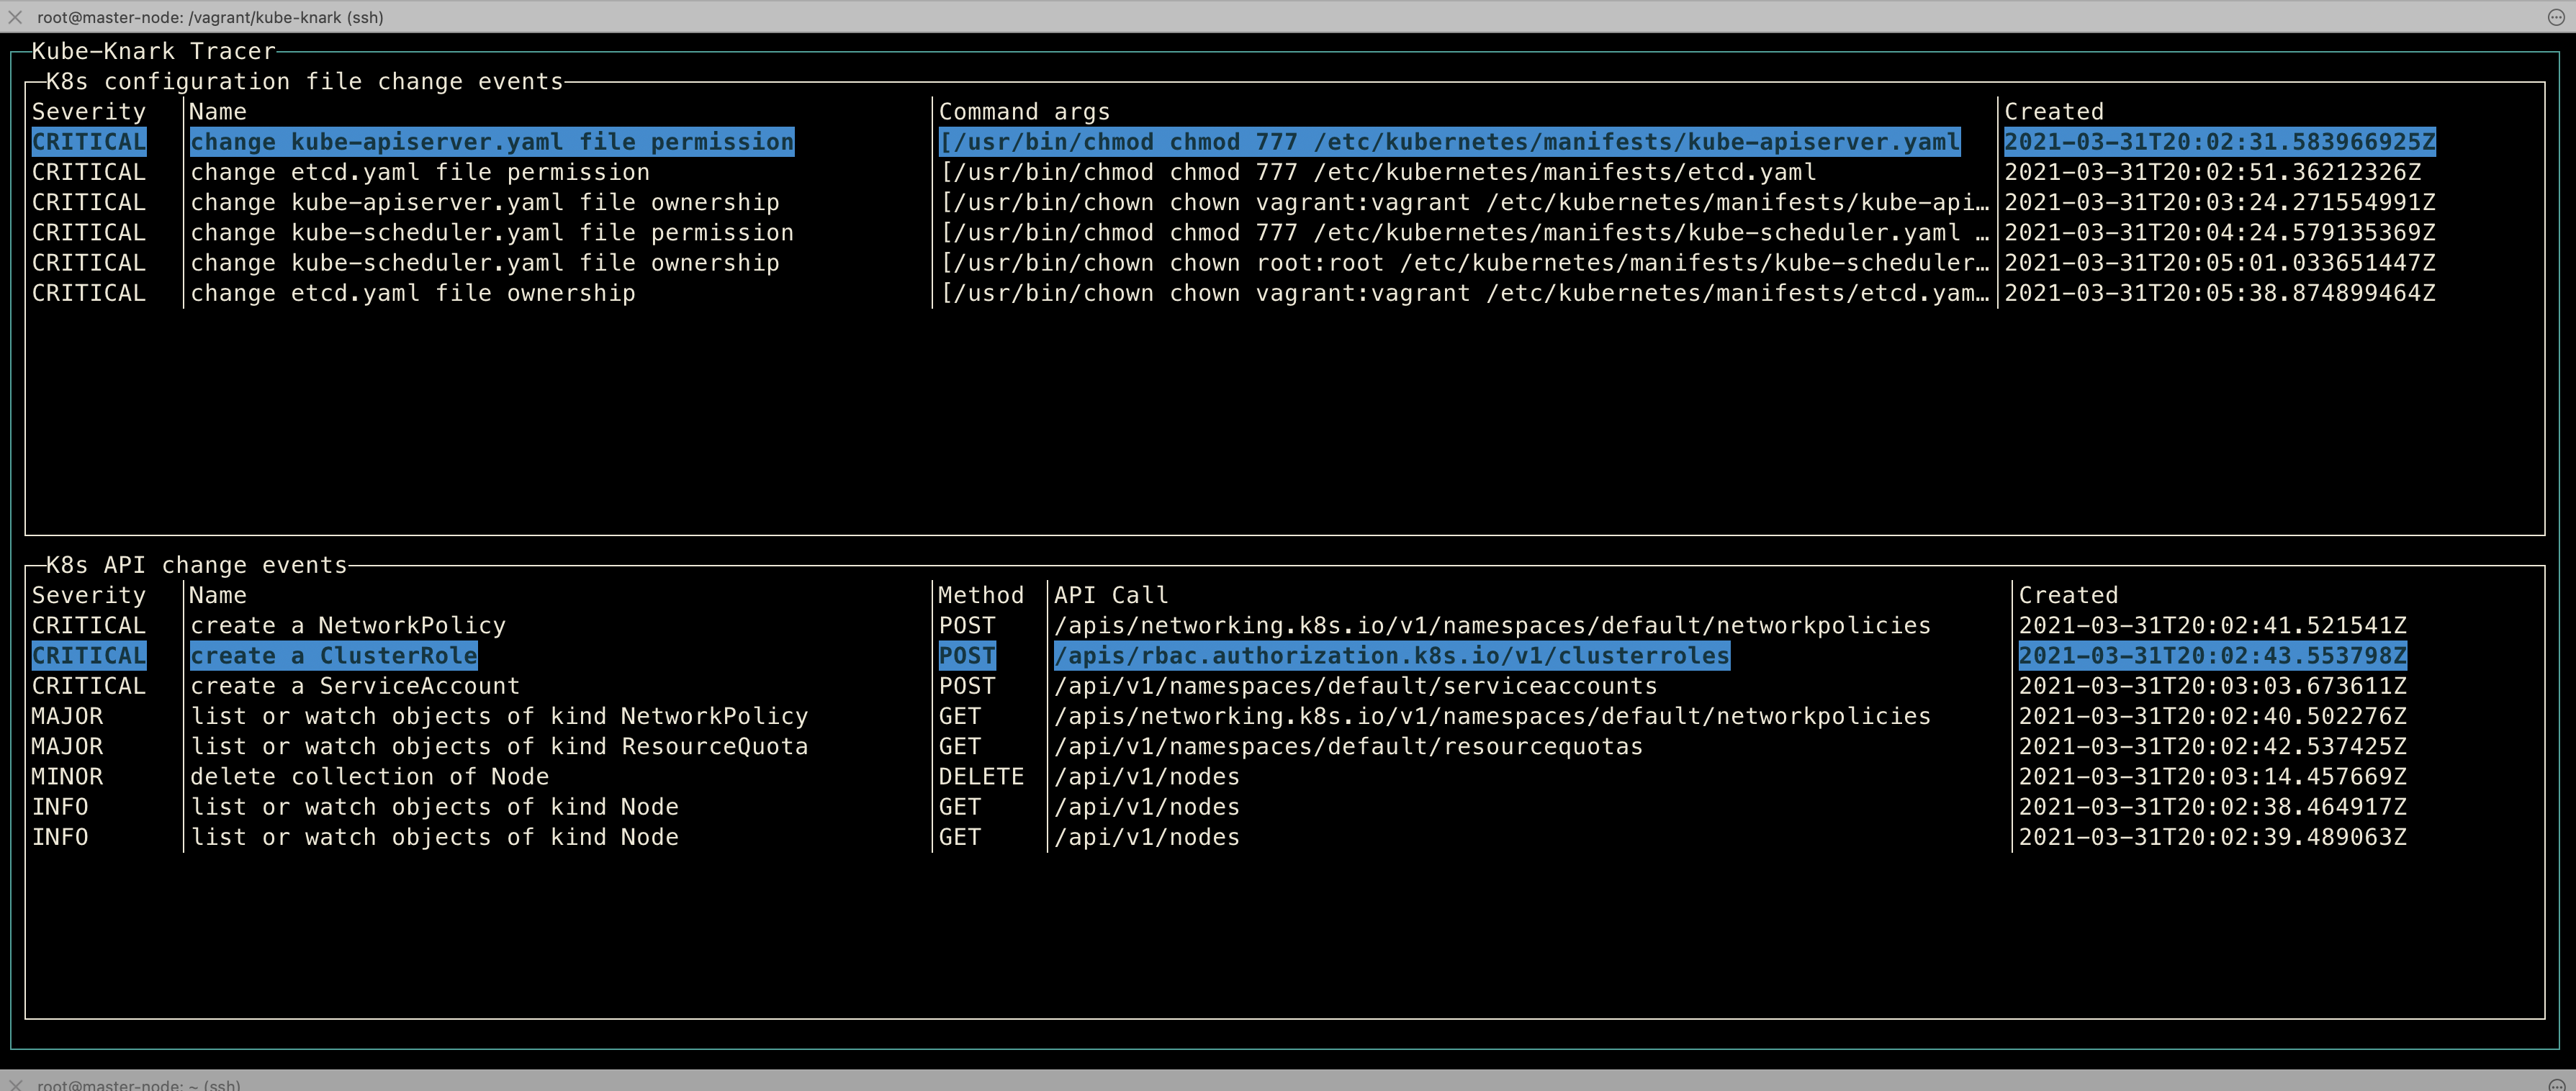
Open Source runtime tool which help to detect malware code execution and run time mis-configuration change on a kubernetes cluster

An eBPF detection program for CVE-2022-0847

Detection-engineering reference mapping Windows, cloud, container, identity, and ICS attack classes to Sigma rules, trust-boundary models, BYOVD…

Experimental Decoy Broker

Comprehensive technical research on CVE-2026-43284 (Dirty Frag), including Linux kernel internals, root cause analysis, patch analysis, detection…

Educational demo of CVE-2024-21626 runc container escape with eBPF-based detection gadget for exploitation attempts.

Anti-Virus for K8s. Protect your Applications running on Kubernetes from malicious attacks with pre-registered source code, runtime processes…

Research and detection guidance for CVE-2026-31431, an io_uring-based bypass of syscall monitoring. Provides detection rules for Tetragon, Falco, and…

Defensive IR playbook and detection package for CVE-2026-31431 (Copy Fail) Linux kernel LPE, including Sigma, auditd, Falco, Wazuh, YARA, eBPF, and…

Hardened container staging framework with seccomp syscall whitelisting and eBPF telemetry to detect and block container escape and kernel ULP…