
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
25 results
MISP preview

MISP

GitHubmisp/misp

MISP (core software) - Open Source Threat Intelligence and Sharing Platform
curated-resourcesdatabase-securitydefensive-tools+10
6.5k4 days ago
ThreatIngestor preview

ThreatIngestor

GitHubpedramamini/threatingestor

Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
information-gatheringintrusion-detectionioc-management+3
9303 months ago
tarian preview

tarian

GitHubdevopstoday11/tarian

Anti-Virus for K8s. Protect your Applications running on Kubernetes from malicious attacks with pre-registered source code, runtime processes…
cloud-securitycontainer-securitydevsecops+2
24 years ago
Malcolm preview

Malcolm

GitHubcisagov/malcolm

Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
digital-forensicsdns-analysisforensics+9
2.5k26 days ago
Malcolm preview

Malcolm

GitHubidaholab/malcolm

Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…

defensive-toolsdigital-forensicsforensics+8
48126 days ago
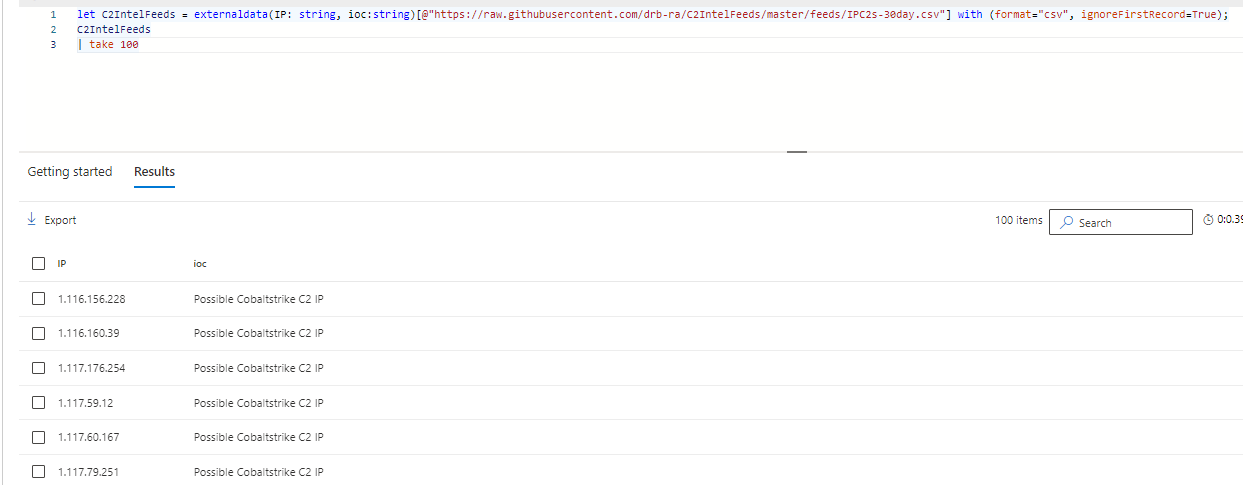
ARTIF preview

ARTIF

GitHubcred-club/artif

An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
information-gatheringintrusion-detectionioc-management+5
2514 years ago
Open-Source-Threat-Intel-Feeds preview

Open-Source-Threat-Intel-Feeds

GitHubbert-janp/open-source-threat-intel-feeds

This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…

intrusion-detectionioc-managementnetwork-security+3
9468 days ago
ioc preview

ioc

GitHubgendigitalinc/ioc

Threat Intel IoCs + bits and pieces of dark matter. Published by Gen Threat Labs.

defensive-toolsintrusion-detectionioc-management+3
4593 months ago
threat-intel preview

threat-intel

GitHubvolexity/threat-intel

Signatures and IoCs from public Volexity blog posts.
defensive-toolsintrusion-detectionioc-management+4
37212 days ago
log4shell-rex preview

log4shell-rex

GitHubback2root/log4shell-rex

PCRE RegEx matching Log4Shell CVE-2021-44228 IOC in your logs
incident-responseintrusion-detectionioc-management+3
2914 years ago
Log4Shell_CVE-2021-44228_related_attacks_IOCs preview

Log4Shell_CVE-2021-44228_related_attacks_IOCs

GitHubreddrip7/log4shell_cve-2021-44228_related_attacks_iocs

Curated repository of Indicators of Compromise (IOCs), attack source IPs, and Snort/Suricata detection rules for Log4Shell (CVE-2021-44228) attacks.
exploitationincident-responseintrusion-detection+3
444 years ago
copy-fail-CVE-2026-31431-IOC preview

copy-fail-CVE-2026-31431-IOC

GitHubkadir/copy-fail-cve-2026-31431-ioc

Detection, mitigation, and IOC toolkit for Copy Fail CVE-2026-31431 Linux kernel page-cache privilege escalation
forensicsincident-responseintrusion-detection+2
314 months ago
synacktiv-rules preview

synacktiv-rules

GitHubsynacktiv/synacktiv-rules

Public repository of Sigma and YARA rules created by Synacktiv
forensicsintrusion-detectionioc-management+3
2111 months ago
mimikatz-detector-busylight preview

mimikatz-detector-busylight

GitHubnccgroup/mimikatz-detector-busylight

USB HID driver emulation with PID/VID (0x3bca/0x27bb) of Plenom A/S Busylight Alpha, that is supported by Mimikatz. When mimikatz is executed, a…
defensive-toolsincident-responseintrusion-detection+3
214 years ago
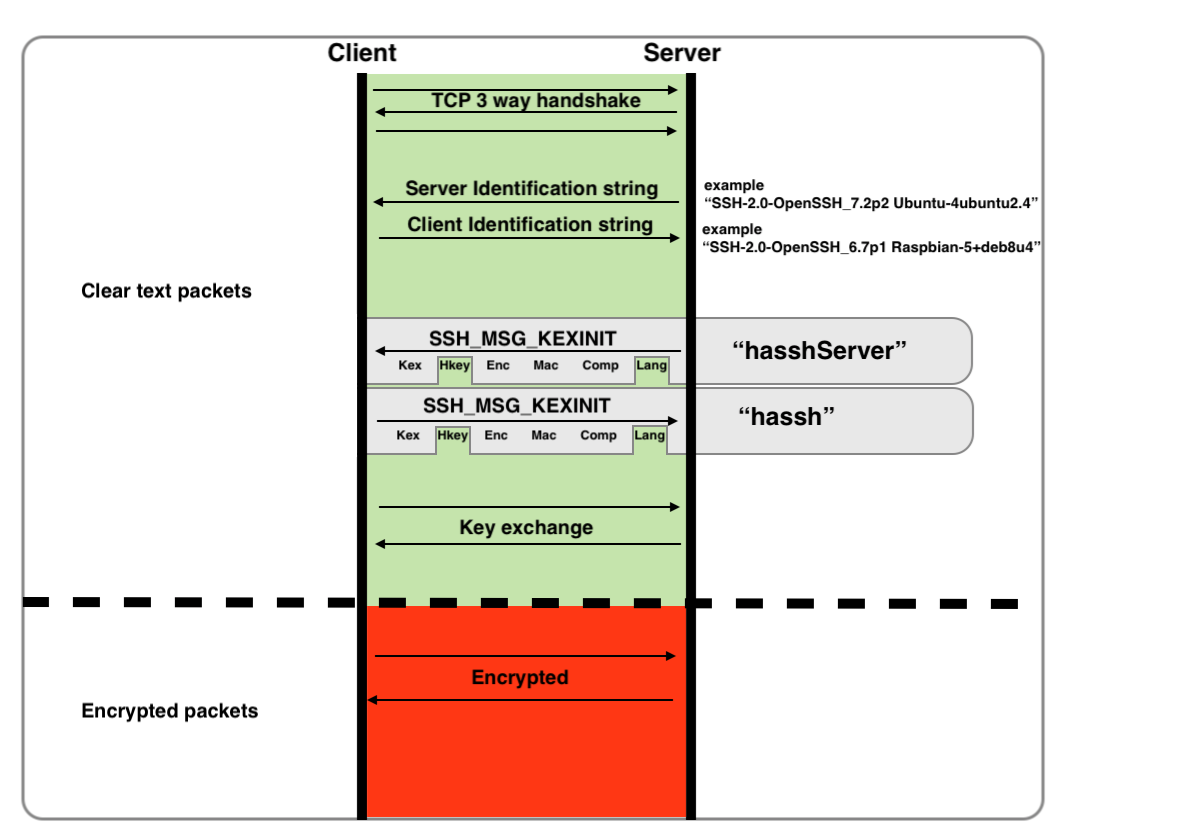
hassh preview

hassh

GitHubcorelight/hassh

Fingerprint SSH clients and servers.

anomaly-detectionforensicsintrusion-detection+4
122 years ago
honeypot preview

honeypot

GitHubrxerium/honeypot

🍯Honeypot Threat Intel

defensive-toolsintrusion-detectionioc-management+4
11 year ago
cve-2025-8088 preview

cve-2025-8088

GitHubtravisbgreen/cve-2025-8088

cve-2025-8088_detection

exploitationintrusion-detectionioc-management+3
11 year ago
Sigma-Rule-for-CVE-2021-40438-exploitation-attempt preview

Sigma-Rule-for-CVE-2021-40438-exploitation-attempt

GitHubpisut4152/sigma-rule-for-cve-2021-40438-exploitation-attempt

Sigma-Rule-for-CVE-2021-40438-Attack-Attemp

intrusion-detectionioc-managementlog-analysis+3
14 years ago
Previous12Next