

ARTIF
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
information-gatheringintrusion-detectionioc-management+5
249
cred-club/artifAn advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 corelight/community-id-spec
An open standard for hashing network flows into identifiers, a.k.a "Community IDs".
 neo23x0/process-watcher
A process monitoring tool that tries to detect exploitation
 julioliraup/antiphishing
Advanced Phishing Protection: Suricata rulesets open and free

 sigmahq/pysigma-backend-opensearch
pySigma OpenSearch backend
 corelight/ecs-logstash-mappings
Mapping Corelight or Zeek data to Elastic Common Schema logs
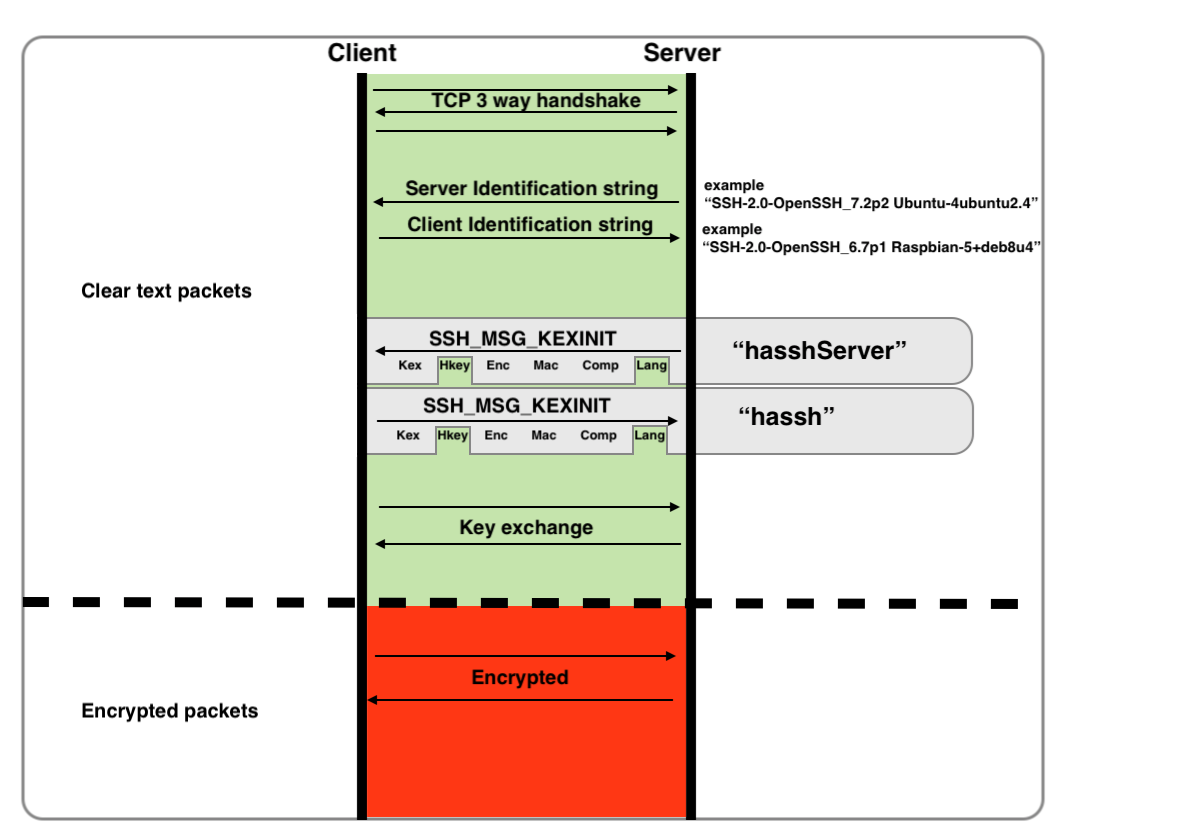 corelight/hassh
Fingerprint SSH clients and servers.
 corelight/cve-2022-24497
Zeek-based network detector for CVE-2022-24497, identifying RPC portmap exploit attempts via real-time traffic analysis and alerting.
 gelim/cve-2020-3952
VMWare vmdir missing access control exploit checker
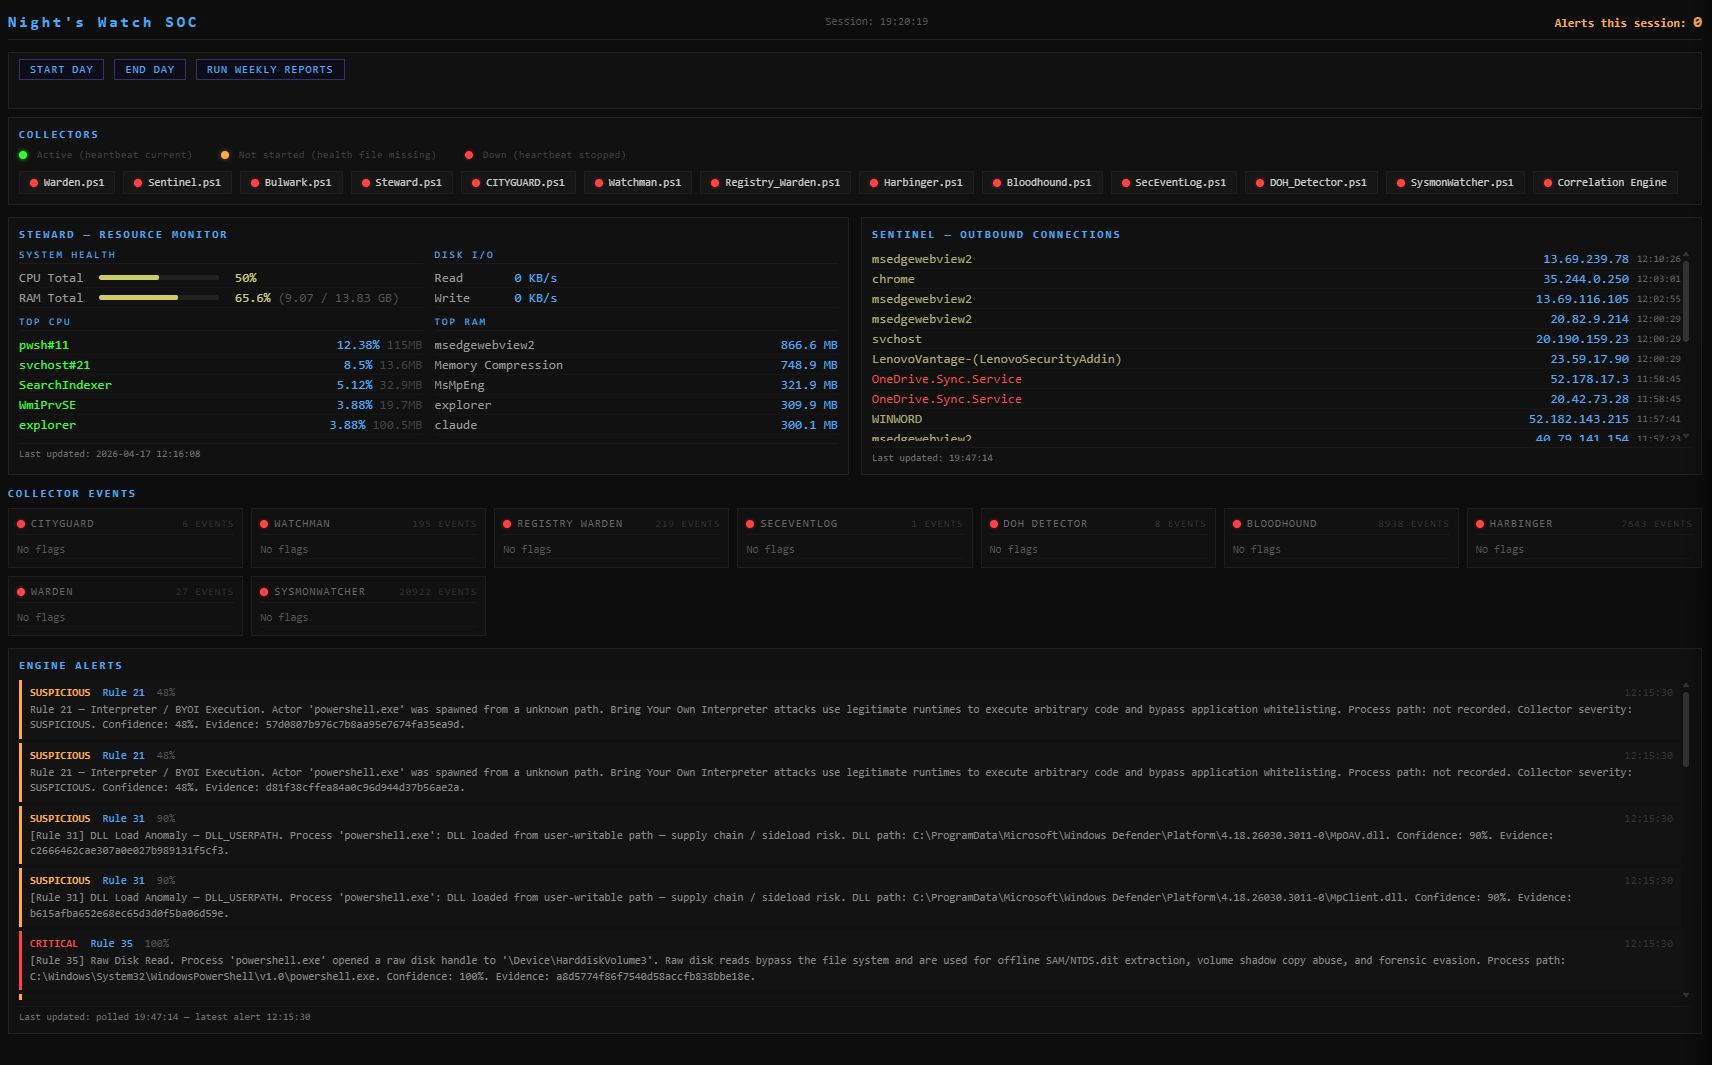 nate-ryan-7690/home_soc_suite
A personal Windows SOC suite built in PowerShell — monitors network connections, resource usage, scheduled tasks and power events with severity…
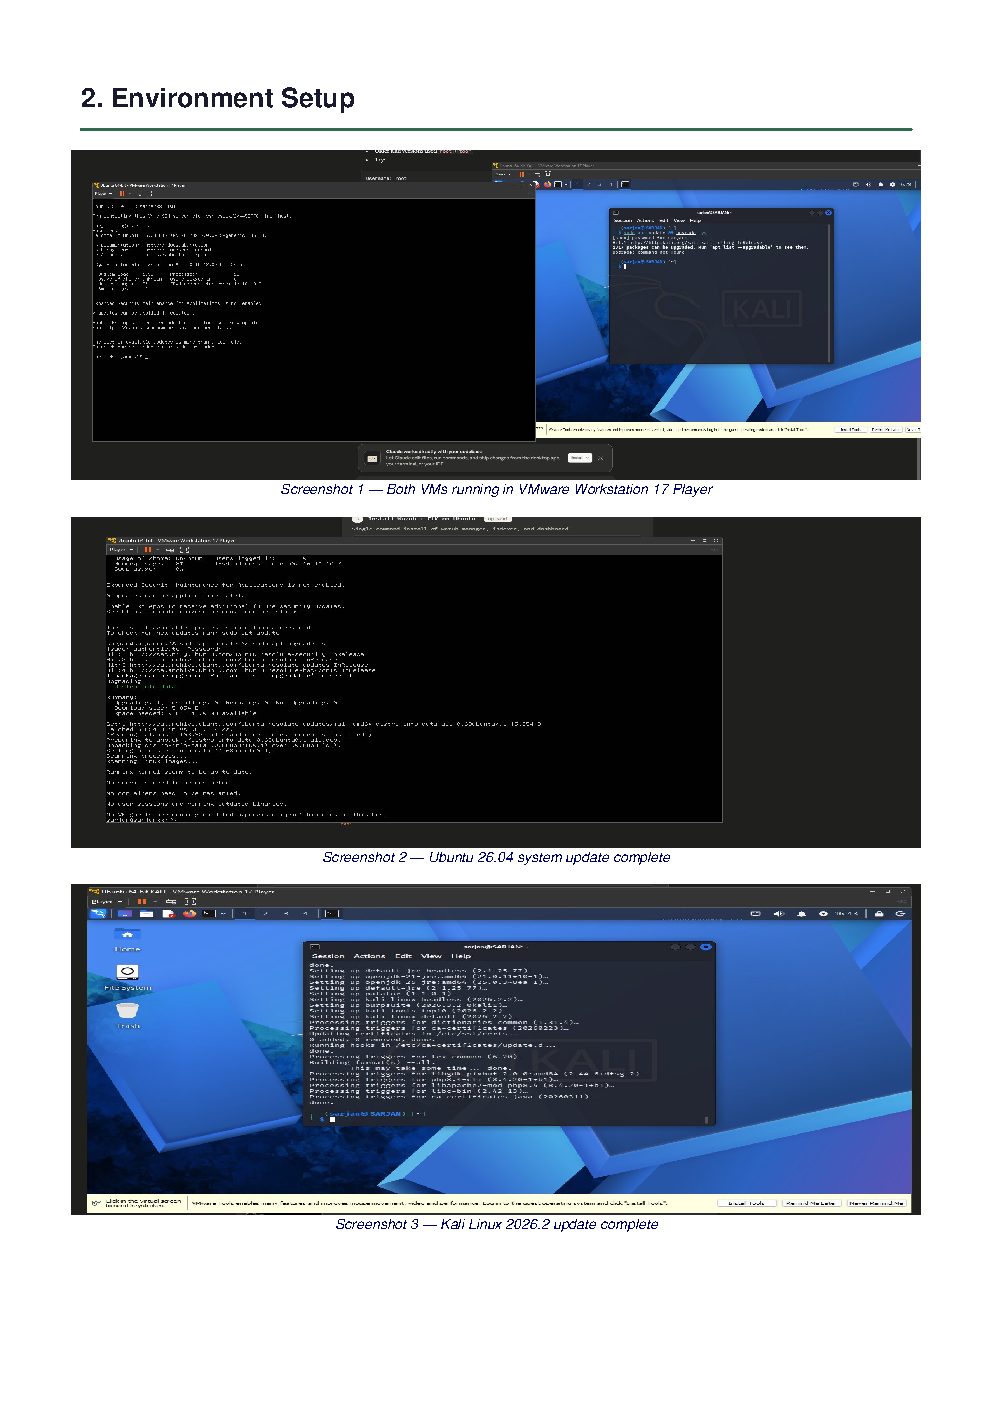 sarjanpatel22/siem-threat-detection-lab
Blue-team SIEM lab: Wazuh 4.7.5 detecting 7 simulated attacks (SSH brute force, Slowloris DoS / CVE-2007-6750, web attacks) with real-time MITRE…
 hackura/xz-cve-2024-3094
Python demo simulating CVE-2024-3094: a supply chain backdoor in XZ Utils with a trigger-based stealth activation.
 phpatch/weblogchecker
Free access-log compromise analyzer: webshell interactions, exploitation patterns and brute-force bursts in your Apache/nginx logs - severity,…
 insomnisec/detections-cve-2026-23918
Detection rules for CVE-2026-23918 Apache http2 RCE - Credit: stringa.ai, isec.pl
 stamusnetworks/scirius
Web interface for Suricata ruleset management, threat hunting, and rule tuning with multi-source feed aggregation, transformation, and activity…
 agentshield-ai/sigma-ai
Sigma detection rules for AI agent security monitoring