
plague
 connectedlucy/plague
Default Detections for EDR
anomaly-detectionconfiguration-auditingcurated-resources+4
connectedlucy/plagueDefault Detections for EDR
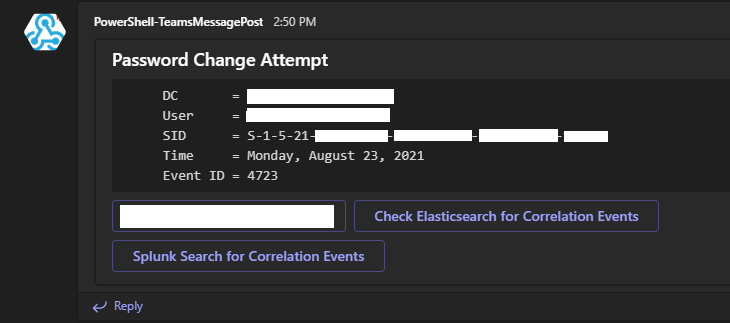 osbornepro/btps-secpack
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…
 d3sre/intelligentprocesslifecycle
The Intelligent Process Lifecycle of Active Cyber Defenders
 freeguy-6/dmz-security-monitoring-hardening
CY376 Blue Team project — pfSense DMZ, Suricata IDS/IPS, and automated host hardening against CVE-2014-6271
 paolokappa/sharepointsecuritymonitor
A comprehensive PowerShell-based SharePoint security monitoring solution with CVE-2025-53770 protection, advanced DLL analysis, threat detection, and…
 mckinnonit/zabbix-template-cve-2020-1472
Zabbix Template to monitor for Windows Event Viewer event's related to Netlogon Elevation of Privilege Vulnerability - CVE-2020-1472. Monitors event…
 treussart/probemanager
Centralize Management of Intrusion Detection System like Suricata Bro Ossec ...