

arkime
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
defensive-toolsdigital-forensicsforensics+7
arkime/arkimeArkime is an open source, large scale, full packet capturing, indexing, and database system.
 ossec/ossec-hids
OSSEC is an Open Source Host-based Intrusion Detection System that performs log analysis, file integrity checking, policy monitoring, rootkit…
 kismetwireless/kismet
Github mirror of official Kismet repository
 zoneminder/zoneminder
ZoneMinder is a free, open source Closed-circuit television software application developed for Linux which supports IP, USB and Analog cameras.
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 julioliraup/antiphishing
Advanced Phishing Protection: Suricata rulesets open and free
 northpolesec/santa
A binary and file access authorization system for macOS.
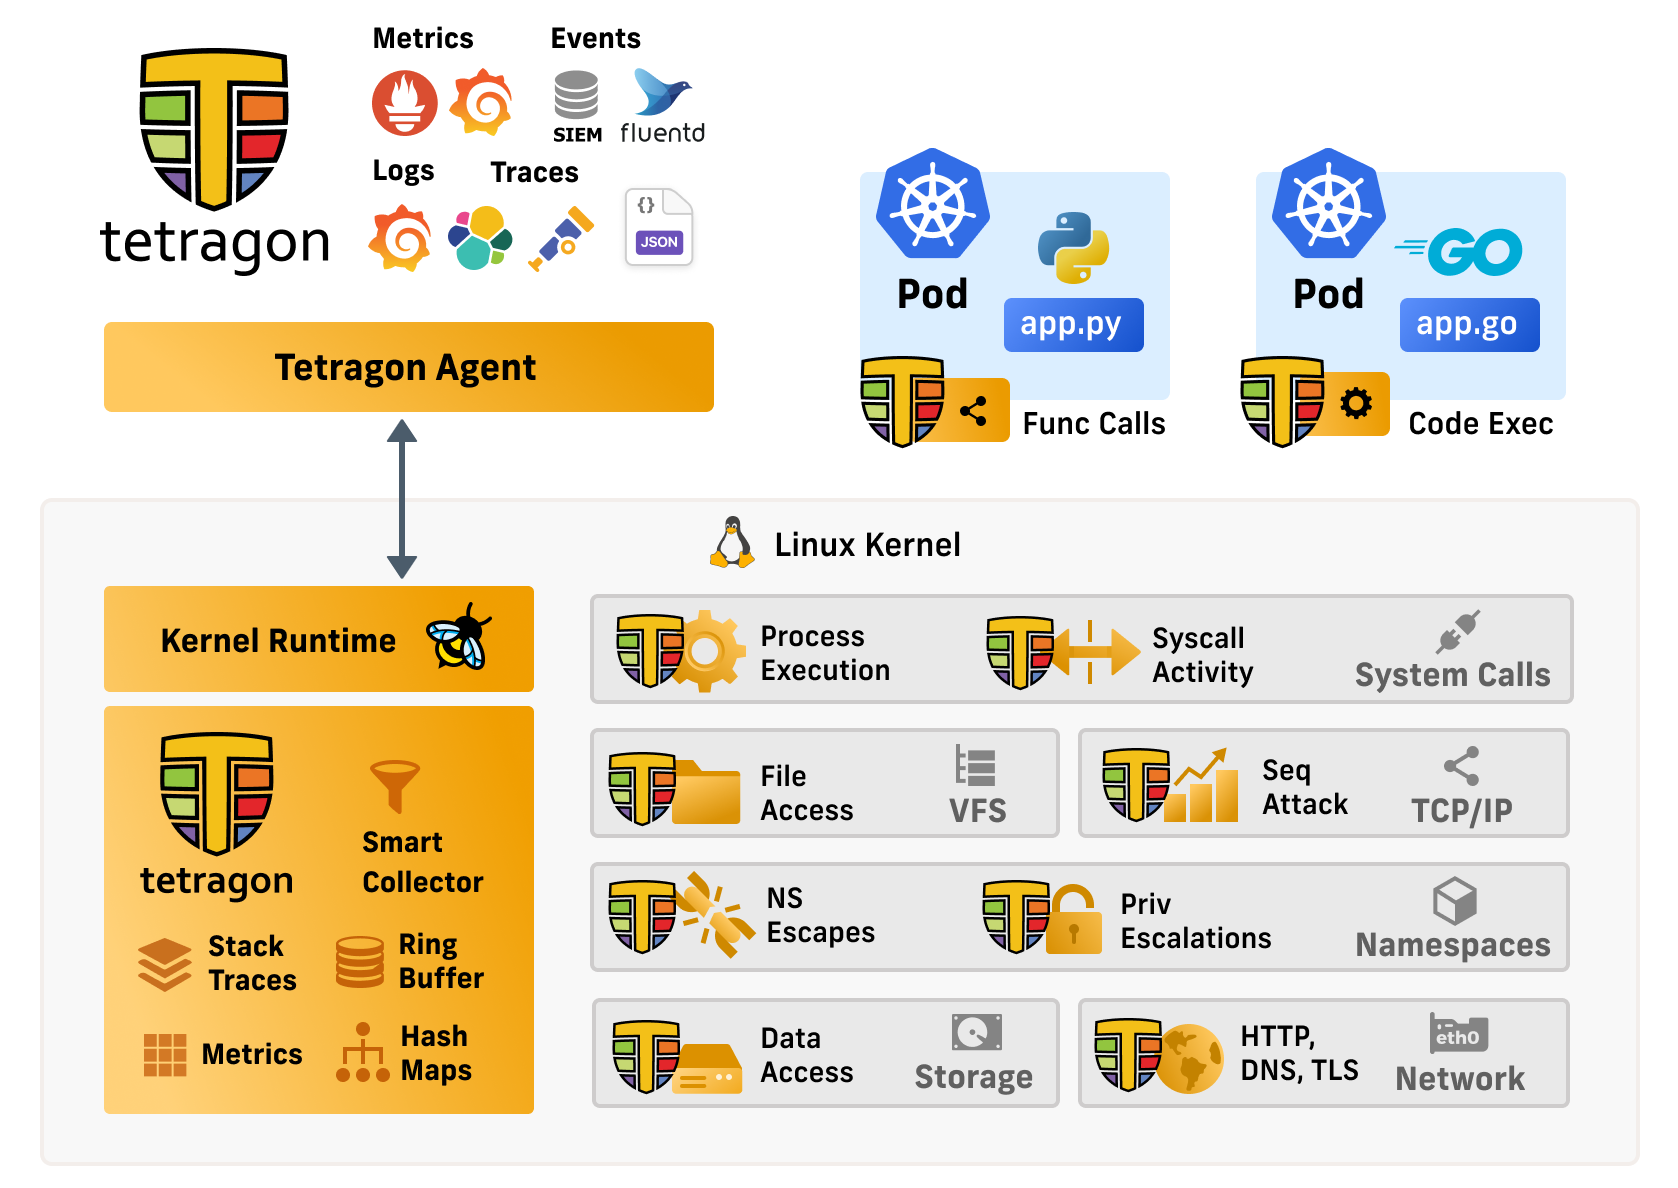 cilium/tetragon
eBPF-based Security Observability and Runtime Enforcement
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
 nzymeorg/nzyme
WiFi, Bluetooth and Ethernet Threat Detection.
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
 inverse-inc/packetfence
PacketFence is a fully supported, trusted, Free and Open Source network access control (NAC) solution. Boasting an impressive feature set including a…
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

 arpsyndicate/vedas-signatures
VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 12000 CVEs