
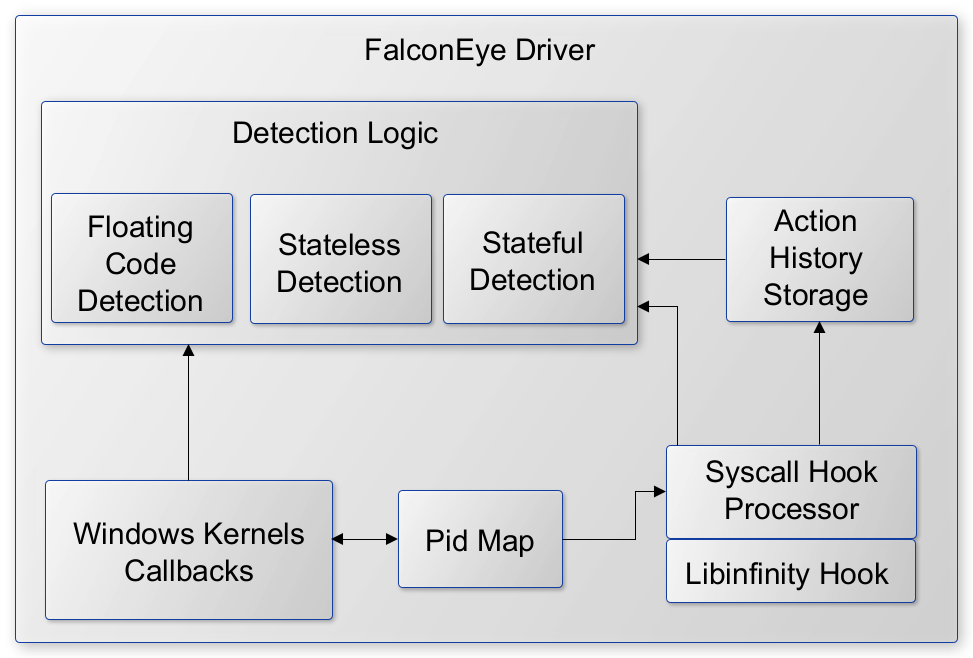
FalconEye
 rajiv2790/falconeye
Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…
binary-analysisdefensive-toolsintrusion-detection+1
309
rajiv2790/falconeyeKernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…
 dinotools/dionaea
Low-interaction honeypot that emulates vulnerable network services to capture malware, shellcode, and exploit attempts, with IPv6 and TLS support.