
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
33 results
stackrox preview

stackrox

GitHubstackrox/stackrox

The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…
anomaly-detectioncloud-infrastructure-securitycloud-security+6
1.3k
6h 38m ago
bombini preview

bombini

GitHubbombinisecurity/bombini

eBPF Security Monitoring and Sandboxing Agent Based on Aya
container-securitydefensive-toolsintrusion-detection
681 day ago
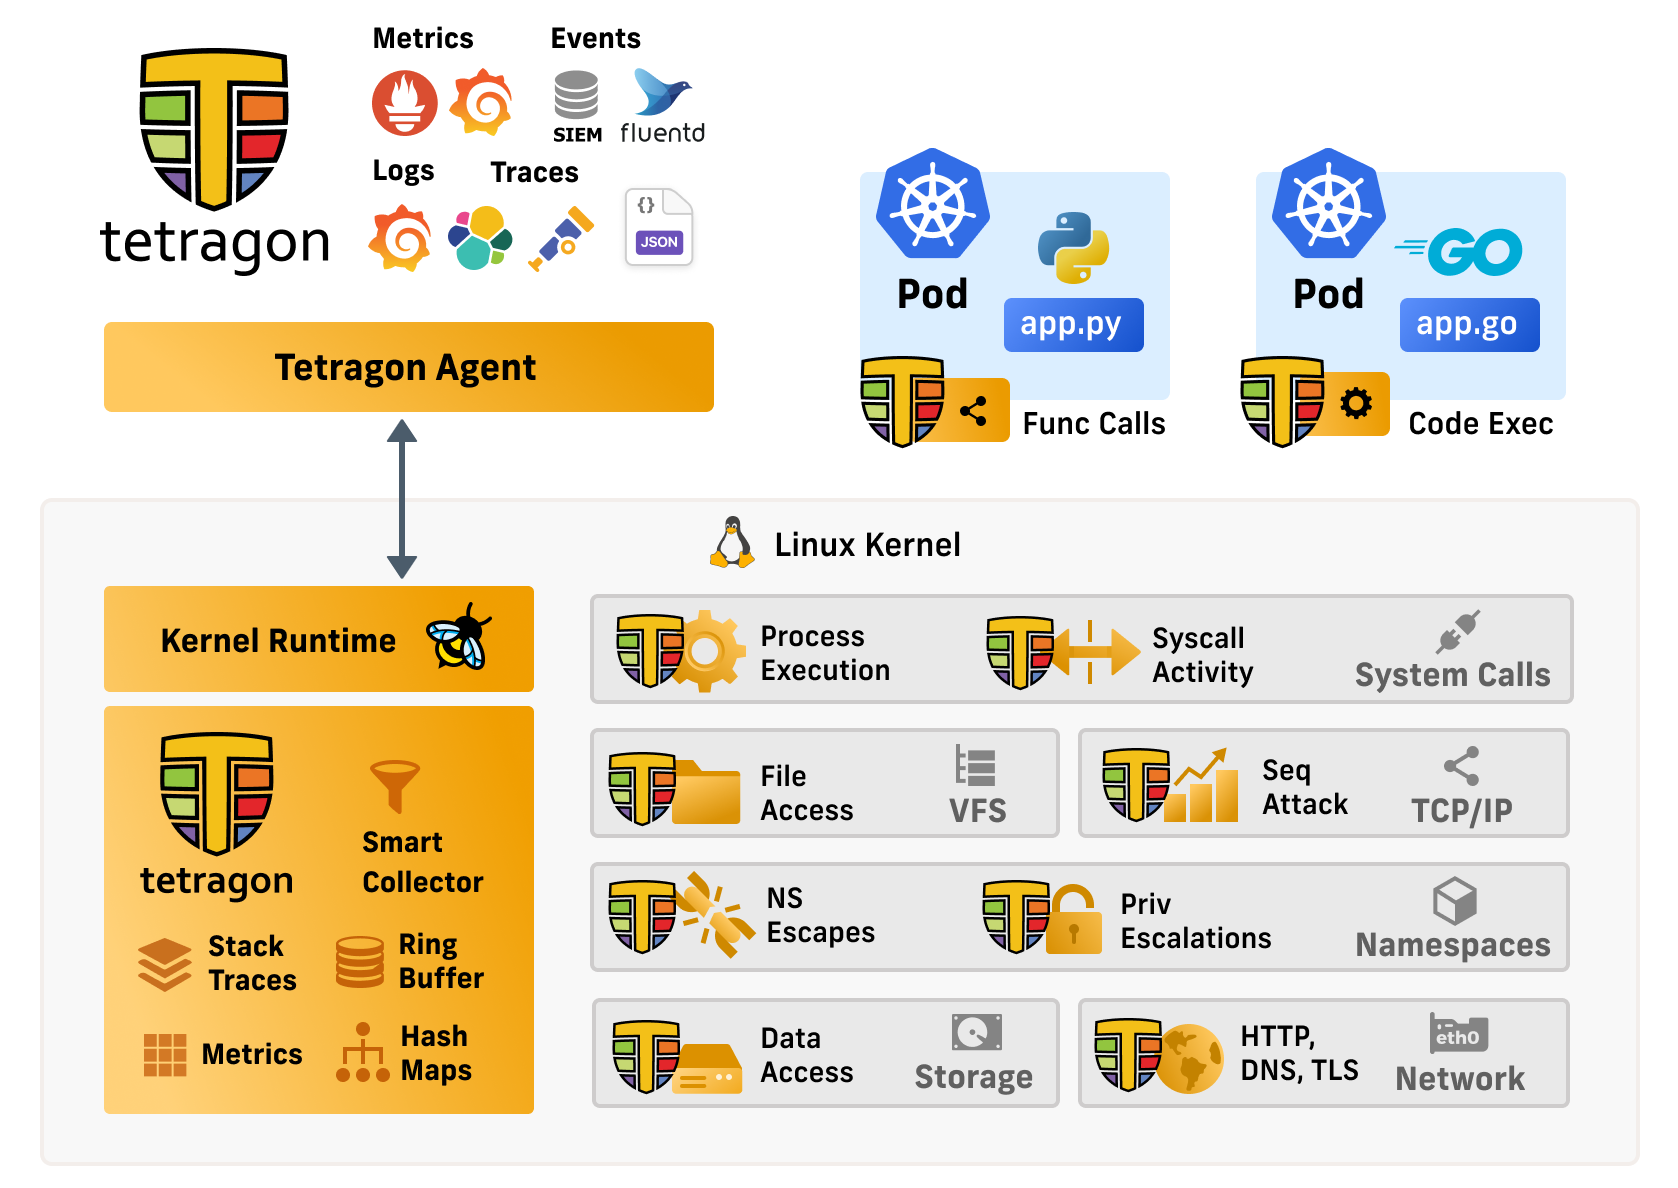
tetragon preview

tetragon

GitHubcilium/tetragon

eBPF-based Security Observability and Runtime Enforcement

chaos-engineeringcloud-securitycontainer-security+2
5.0k2 days ago
so-crates preview

so-crates

GitHubdougburks/so-crates

SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

container-securitydigital-forensicseducation+8
6062 days ago
falco preview

falco

GitHubfalcosecurity/falco

Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
anomaly-detectionanti-botchaos-engineering+10
9.4k2 days ago
beelzebub preview

beelzebub

GitHubbeelzebub-labs/beelzebub

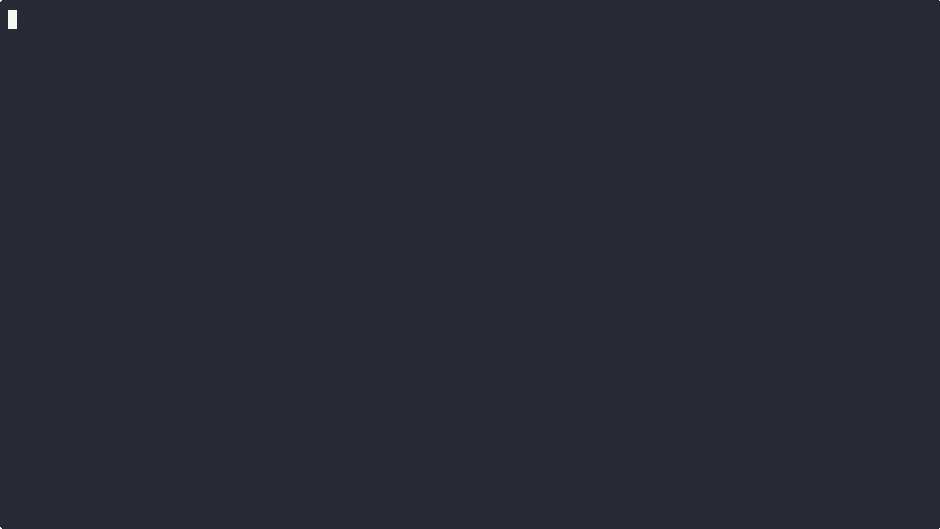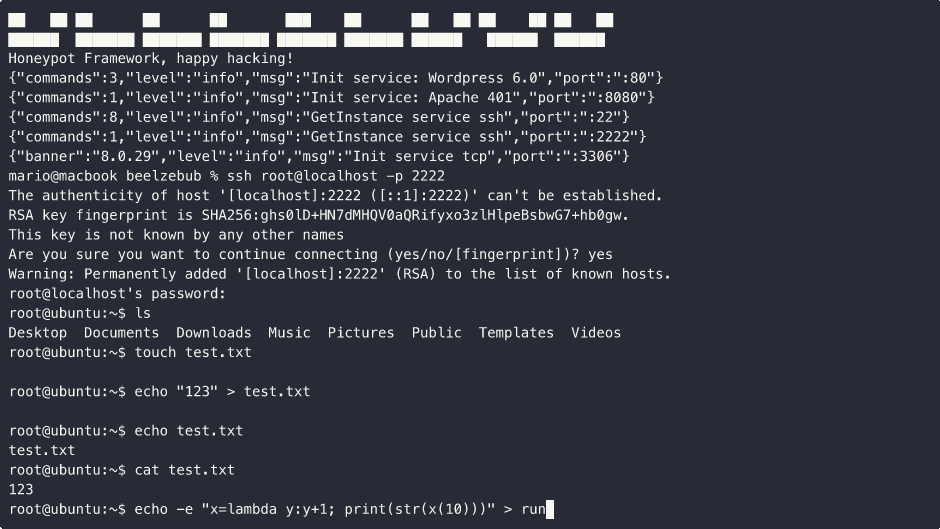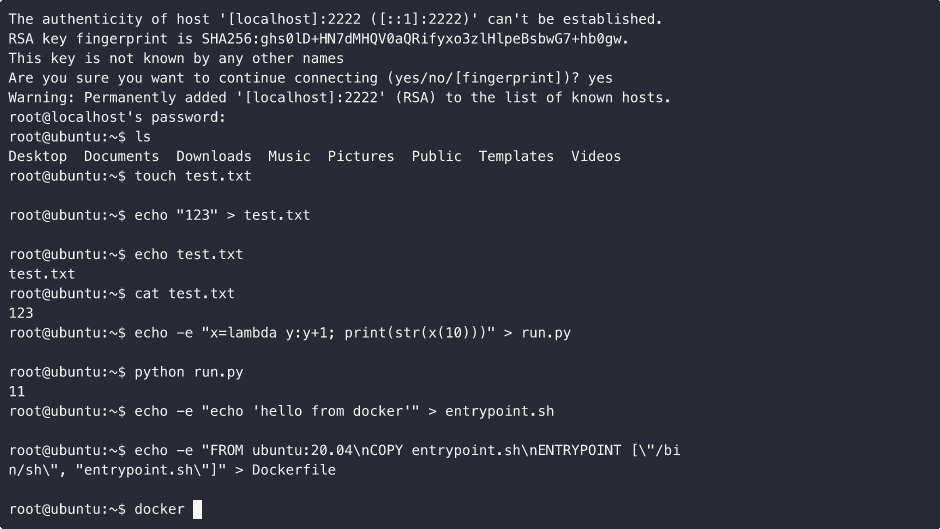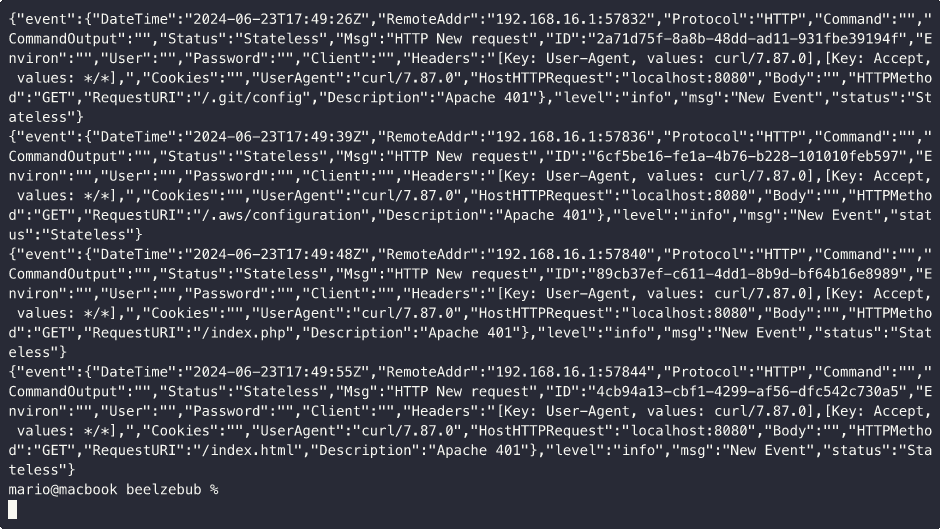
A secure low code deception runtime framework, leveraging AI for System Virtualization.
ai-securityapi-securitycontainer-security+7
2.2k2 days ago
CVE-2025-32433-LAB preview

CVE-2025-32433-LAB

GitHubdamnkrishna/cve-2025-32433-lab

A Flaw in SSH protocol message handling, a malicious actor could gain unauthorized access to affected systems and execute arbitrary commands without…

container-securityeducationexploitation+6
5 days ago
cicd-sensor preview

cicd-sensor

GitLabcicd-sensor/cicd-sensor

eBPF-powered runtime security sensor for CI/CD pipelines. Detects supply-chain attacks, logs process ancestry and file access, and provides forensic…
cloud-securitydevsecopsforensics+3
16 days ago
HoneyWire preview

HoneyWire

GitHubandreicscs/honeywire

Open-source deception platform that turns any Linux machine into a high-signal canary. Deploy tripwire sensors on files, ports, and network services…
container-securitydevsecopsincident-response+3
11026 days ago
LeitWacht preview

LeitWacht

GitLableitwacht/leitwacht

Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration
anomaly-detectioncloud-infrastructure-securitycloud-security+9
1 month ago
Dirty-Frag-Research-CVE-2026-43284- preview

Dirty-Frag-Research-CVE-2026-43284-

GitHubnabhan-mohy/dirty-frag-research-cve-2026-43284-

Comprehensive technical research on CVE-2026-43284 (Dirty Frag), including Linux kernel internals, root cause analysis, patch analysis, detection…
container-securityincident-responseintrusion-detection+2
1 month ago
cyber-decoy preview

cyber-decoy

GitHubsecdev02/cyber-decoy

Experimental Decoy Broker
container-securitydefensive-toolsintrusion-detection+3
32 months ago
FRAGNESIA-Charan-cve-2026-46300 preview

FRAGNESIA-Charan-cve-2026-46300

GitHubazdevops143/fragnesia-charan-cve-2026-46300

Hardened container staging framework with seccomp syscall whitelisting and eBPF telemetry to detect and block container escape and kernel ULP…
cloud-securitycontainer-securityeducation+3
3 months ago
d8-copy-fail-mitigation preview

d8-copy-fail-mitigation

GitHubdeckhouse/d8-copy-fail-mitigation

Kubernetes-native CVE-2026-31431 mitigation with automated kernel module blocking, runtime Falco detection rules, and bashible-based node…
cloud-securityconfiguration-auditingcontainer-security+3
4 months ago
CVE-2026-31431-detection-defense preview

CVE-2026-31431-detection-defense

GitHubdetect-defenselab/cve-2026-31431-detection-defense

Research and detection guidance for CVE-2026-31431, an io_uring-based bypass of syscall monitoring. Provides detection rules for Tetragon, Falco, and…
container-securitydefensive-toolsexploitation+2
4 months ago
cve-2026-31431 preview

cve-2026-31431

GitHubashok523/cve-2026-31431

Defensive IR playbook and detection package for CVE-2026-31431 (Copy Fail) Linux kernel LPE, including Sigma, auditd, Falco, Wazuh, YARA, eBPF, and…

container-securityincident-responseintrusion-detection+3
4 months ago
raxe-ce preview

raxe-ce

GitHubraxe-ai/raxe-ce

Runtime protection for AI agents

ai-securityanomaly-detectiondefensive-tools+5
1215 months ago
clawguard preview

clawguard

GitHubsafeagent-beihang/clawguard

Enterprise AI agent security toolkit providing pre-flight auditing, configuration hardening, runtime threat detection, and active defense against…

ai-securityanomaly-detectioncode-analysis+5
505 months ago
Previous12Next