

ntopng
 ntop/ntopng
Web-based Traffic and Cybersecurity Network Traffic Monitoring
anomaly-detectiondns-analysisintrusion-detection+6
ntop/ntopngWeb-based Traffic and Cybersecurity Network Traffic Monitoring
 cisagov/malcolm
Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…
 kismetwireless/kismet
Github mirror of official Kismet repository
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 ntop/ndpi
Open Source Deep Packet Inspection Software Toolkit
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
 stamparm/maltrail
Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…
 julioliraup/antiphishing
Advanced Phishing Protection: Suricata rulesets open and free

 the-tcpdump-group/libpcap
System-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…
 a2awais/threat-hunting
Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
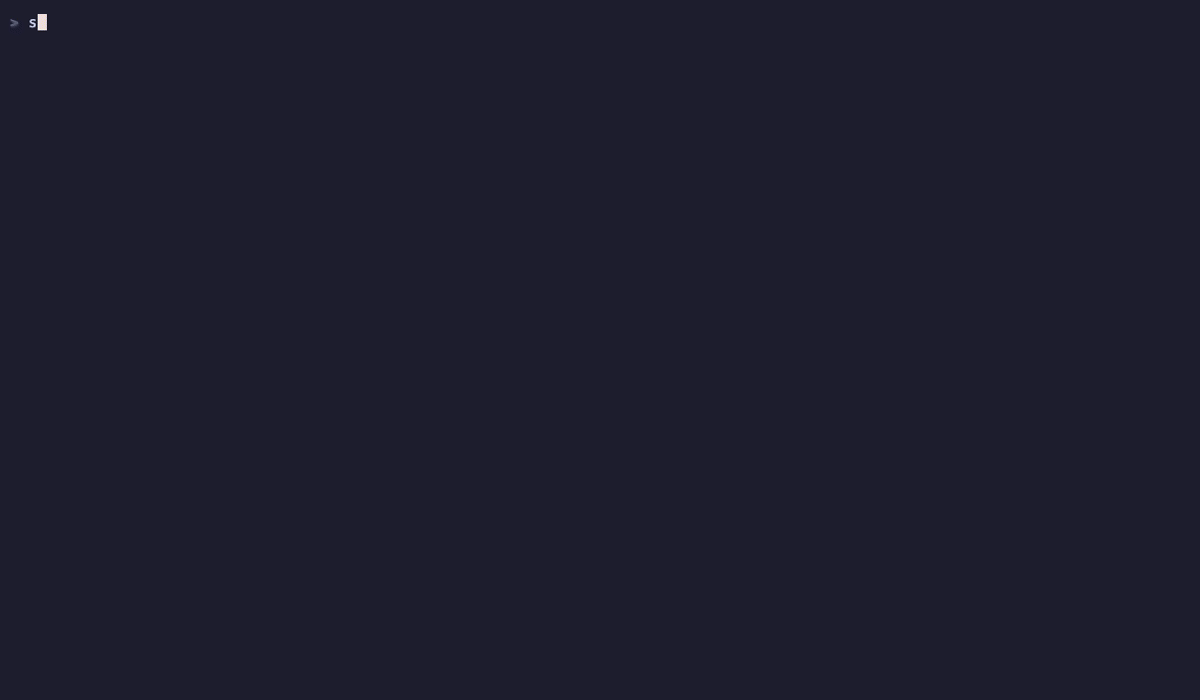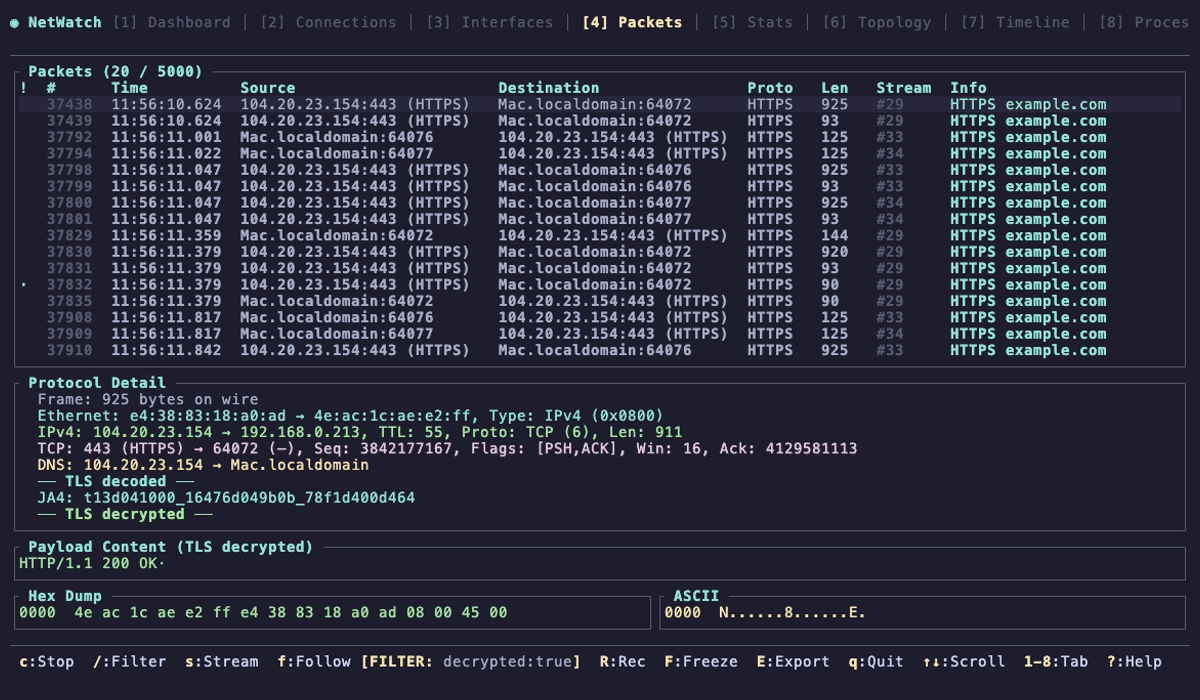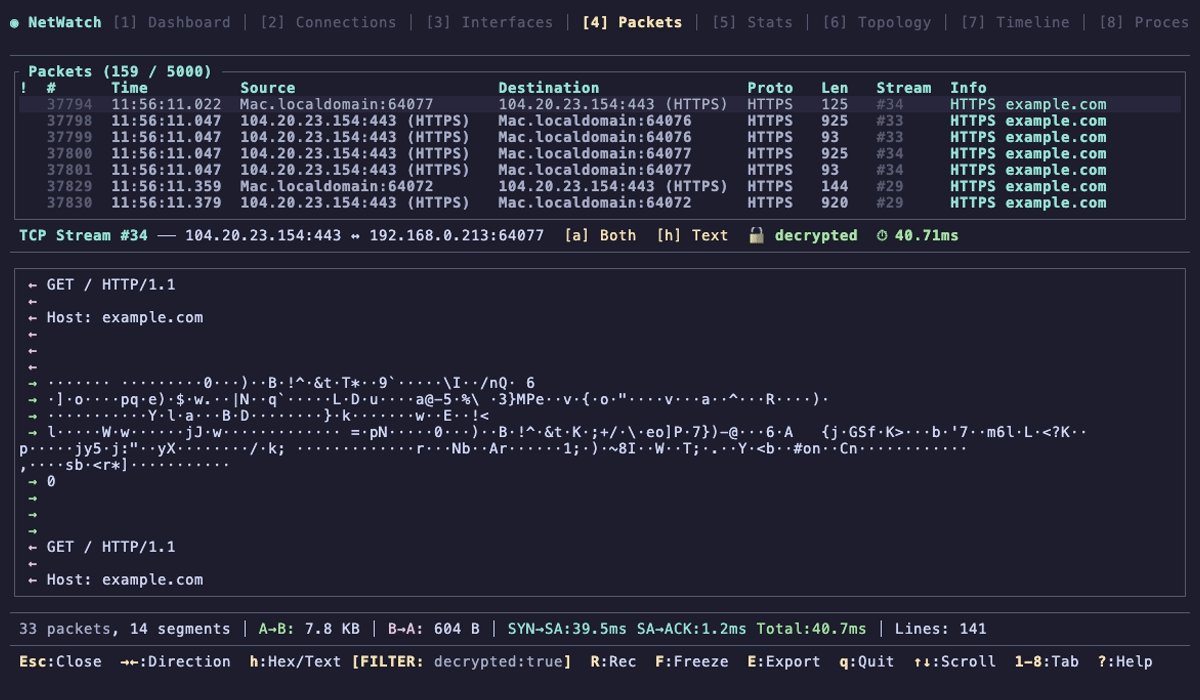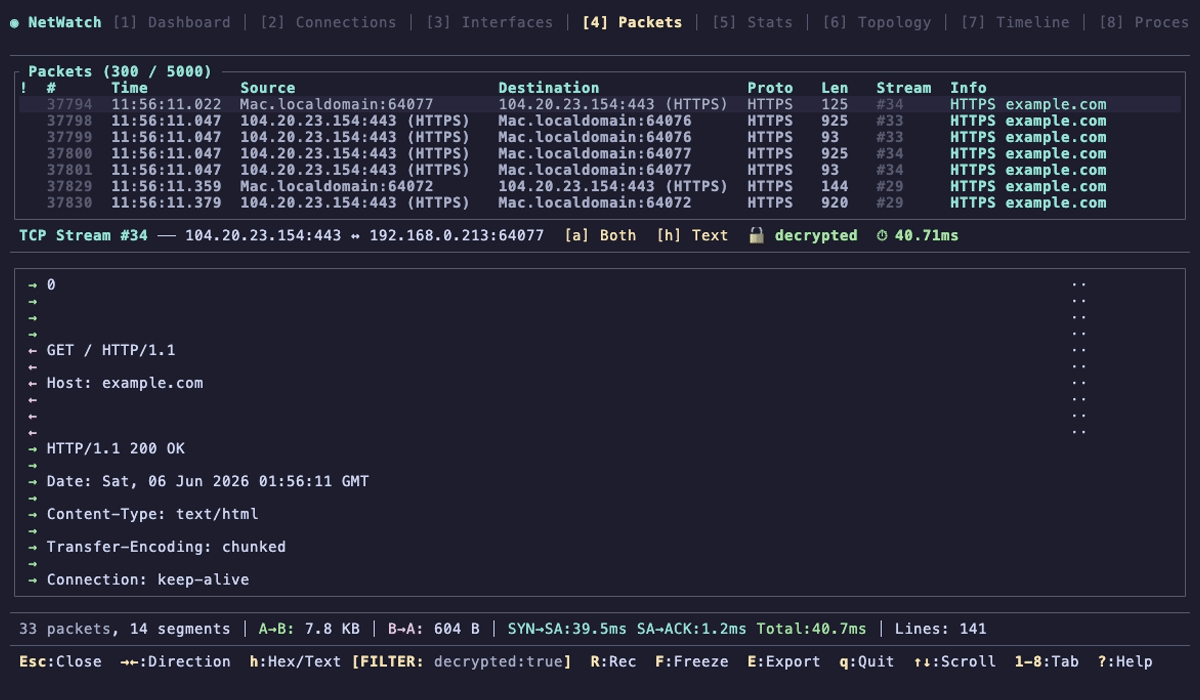 matthart1983/netwatch
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
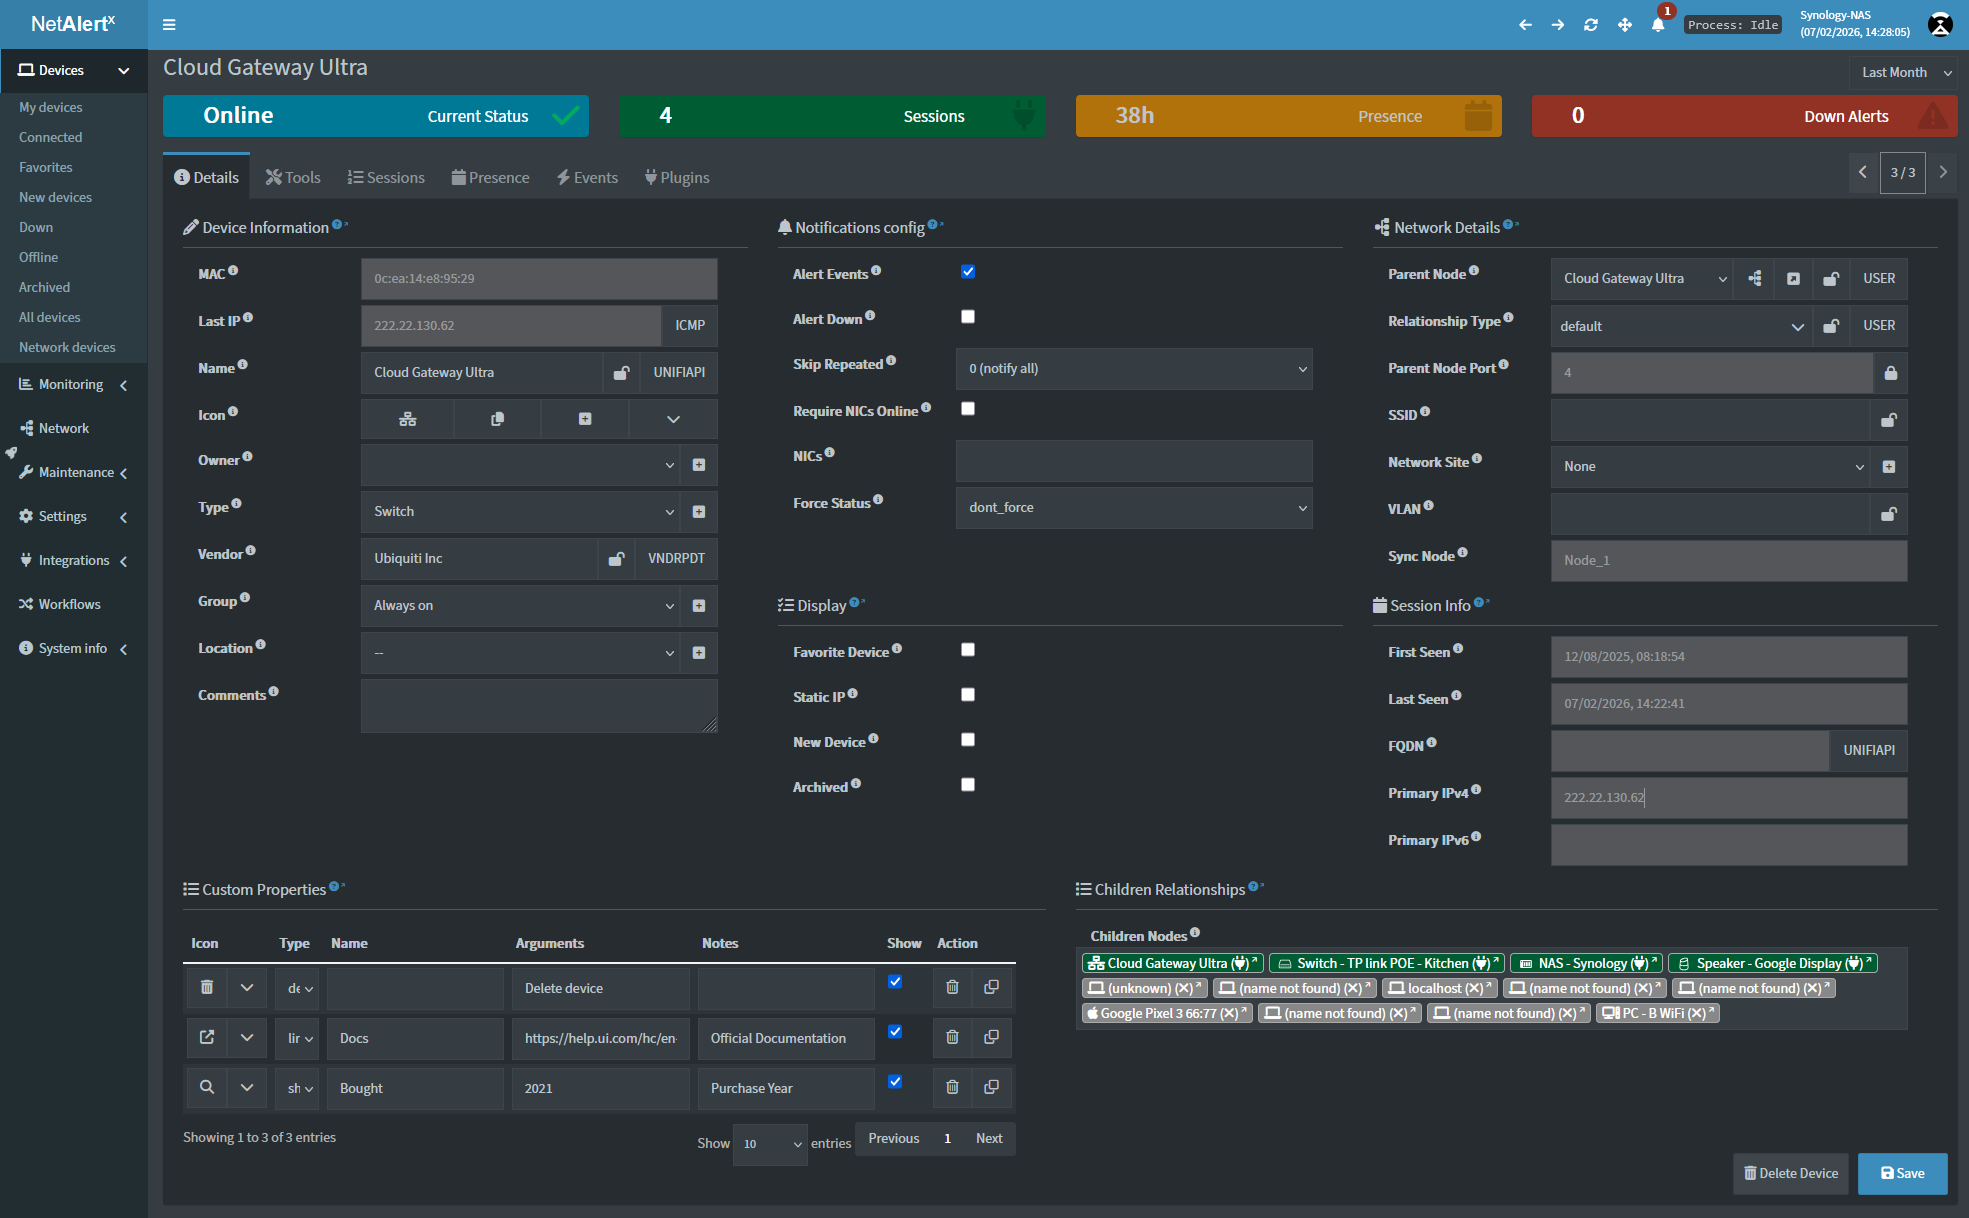 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
 0xmr007/lab4purplesec
Lab4PurpleSec is a modular Purple Team homelab combining a vulnerable Active Directory environment (GOAD), a Docker-based web DMZ, pfSense +…
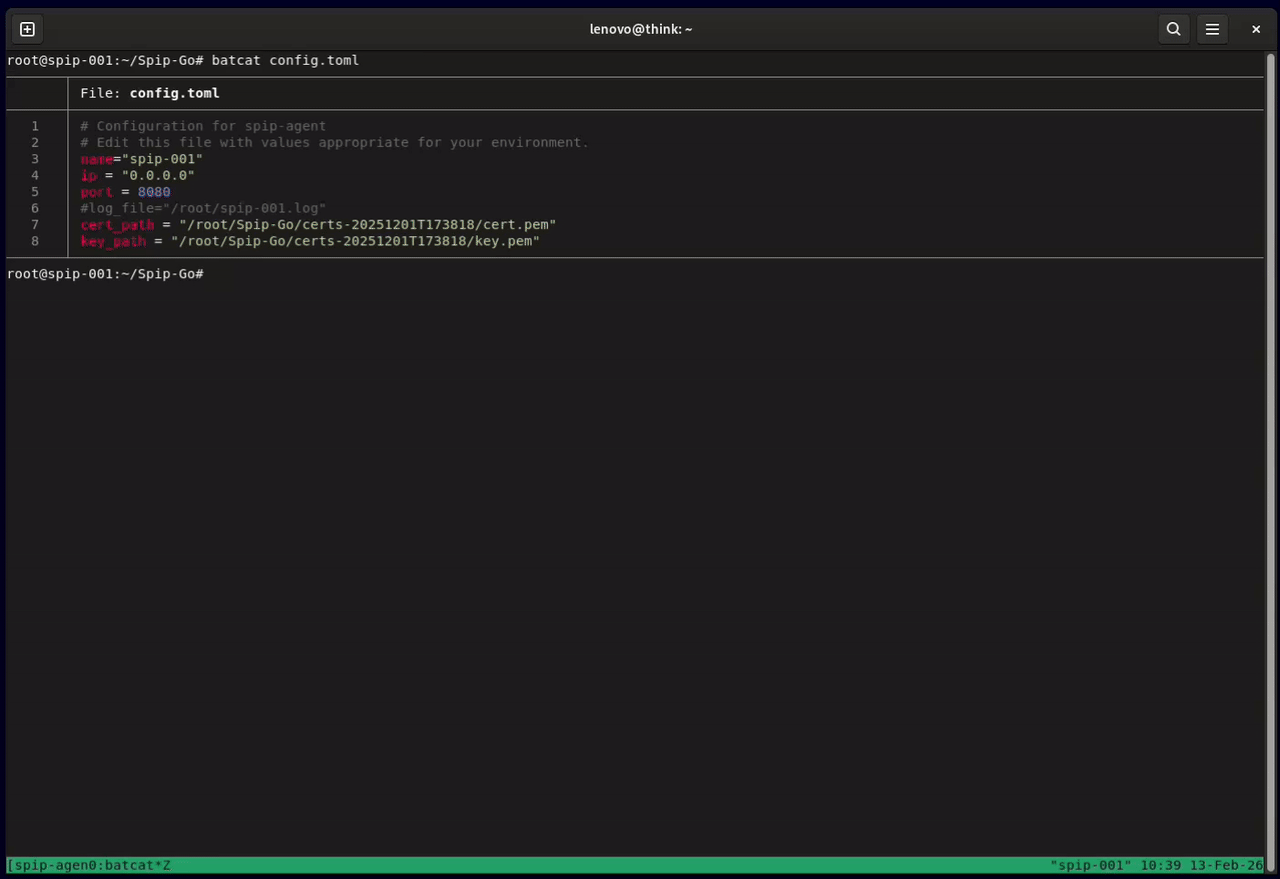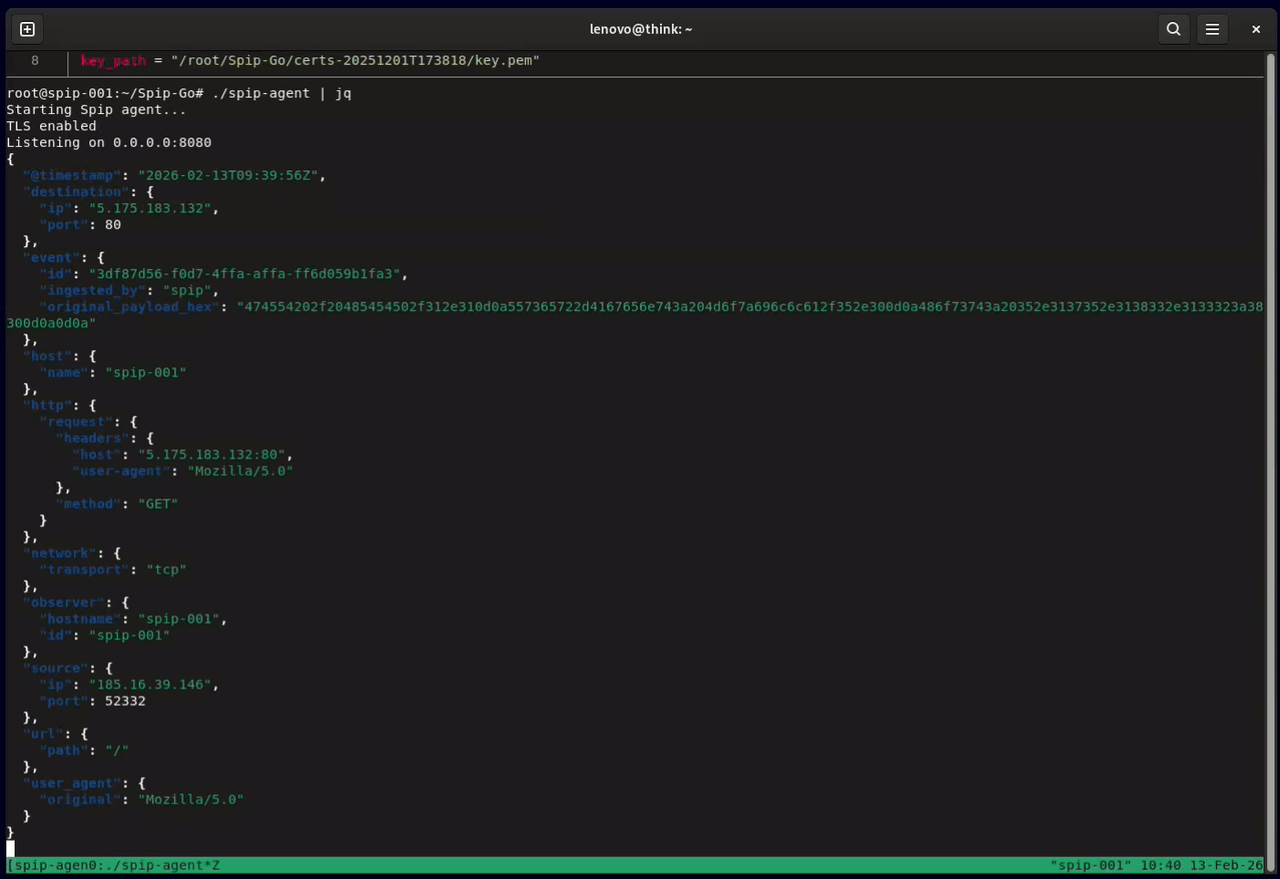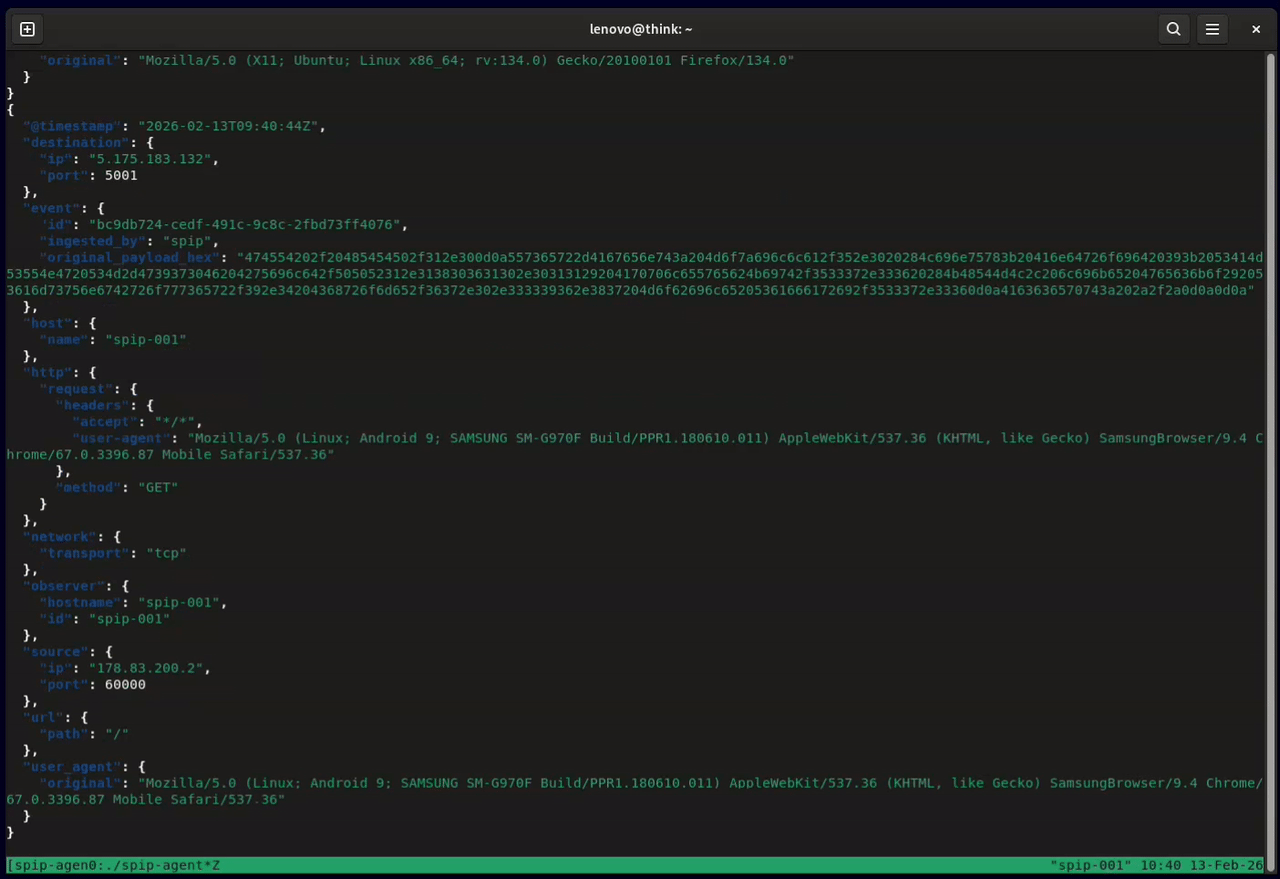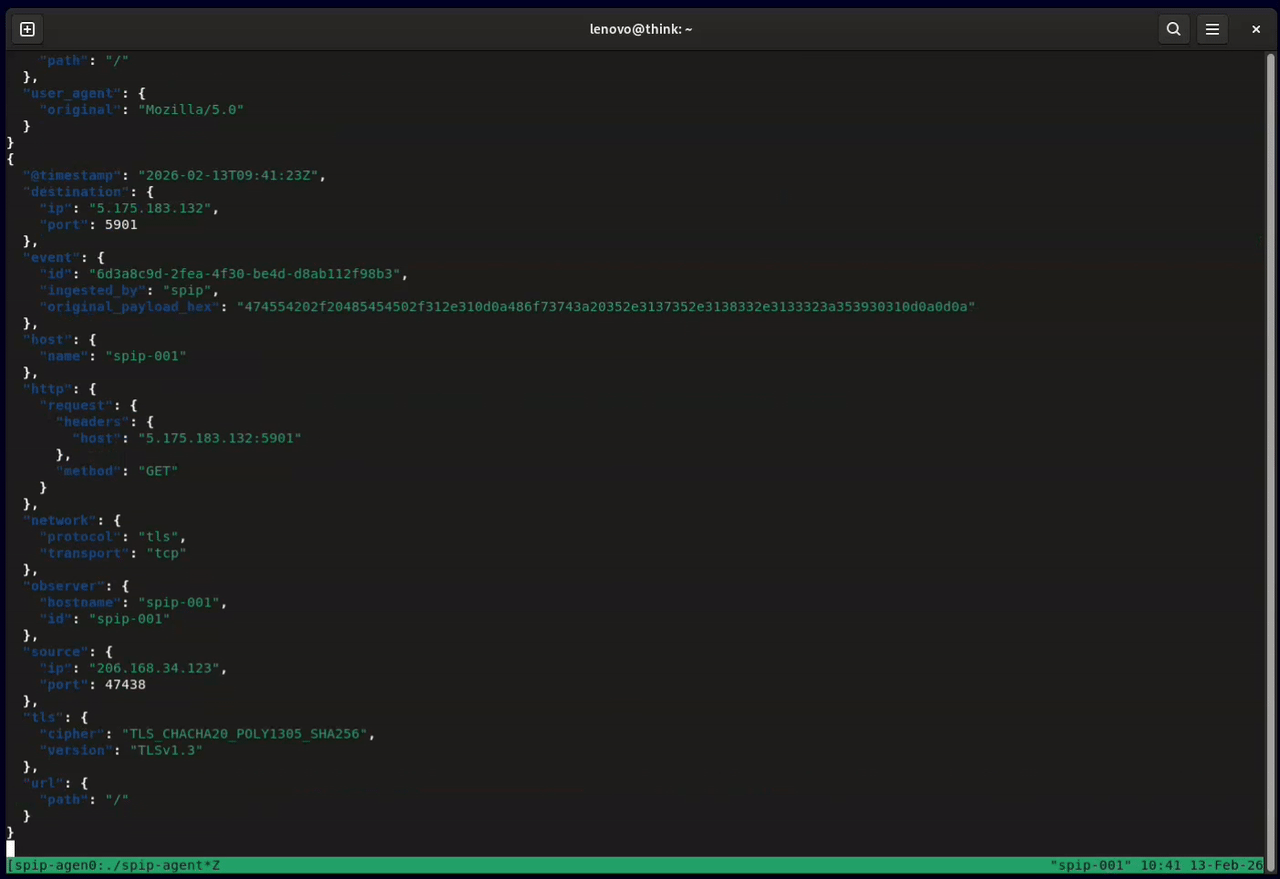 honeylabshq/spip-go
Spip network sensor written in Go
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.