

zeek
 zeek/zeek
Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.
anomaly-detectionanti-botdefensive-tools+14
zeek/zeekZeek is a powerful network analysis framework that is much different from the typical IDS you may know.
 osquery/osquery
SQL powered operating system instrumentation, monitoring, and analytics.
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
 activecm/rita
Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
 mahdi13830510/cve-2026-31431-mitigation-suite
Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…
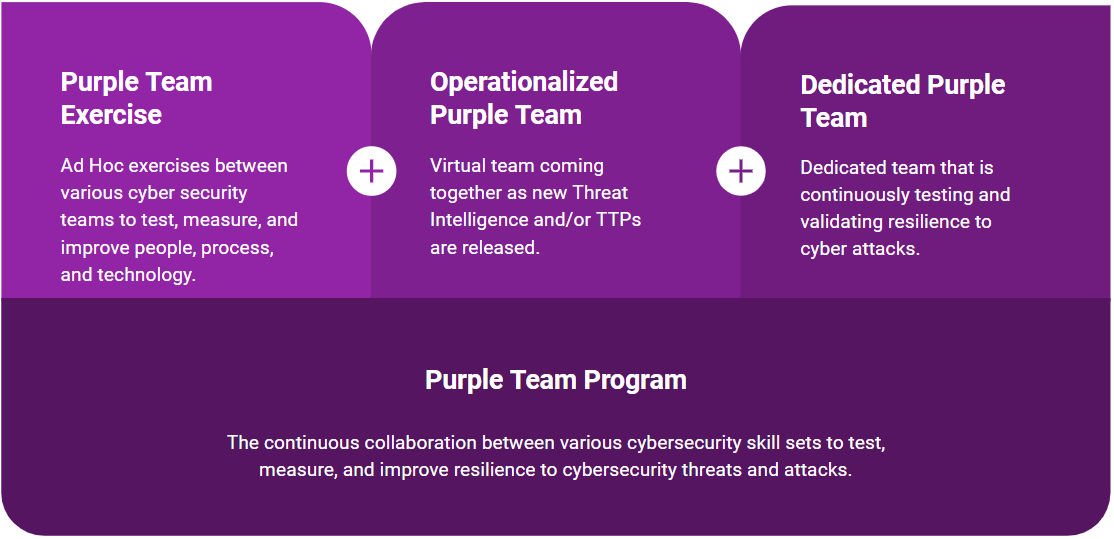 scythe-io/purple-team-exercise-framework
Purple Team Exercise Framework
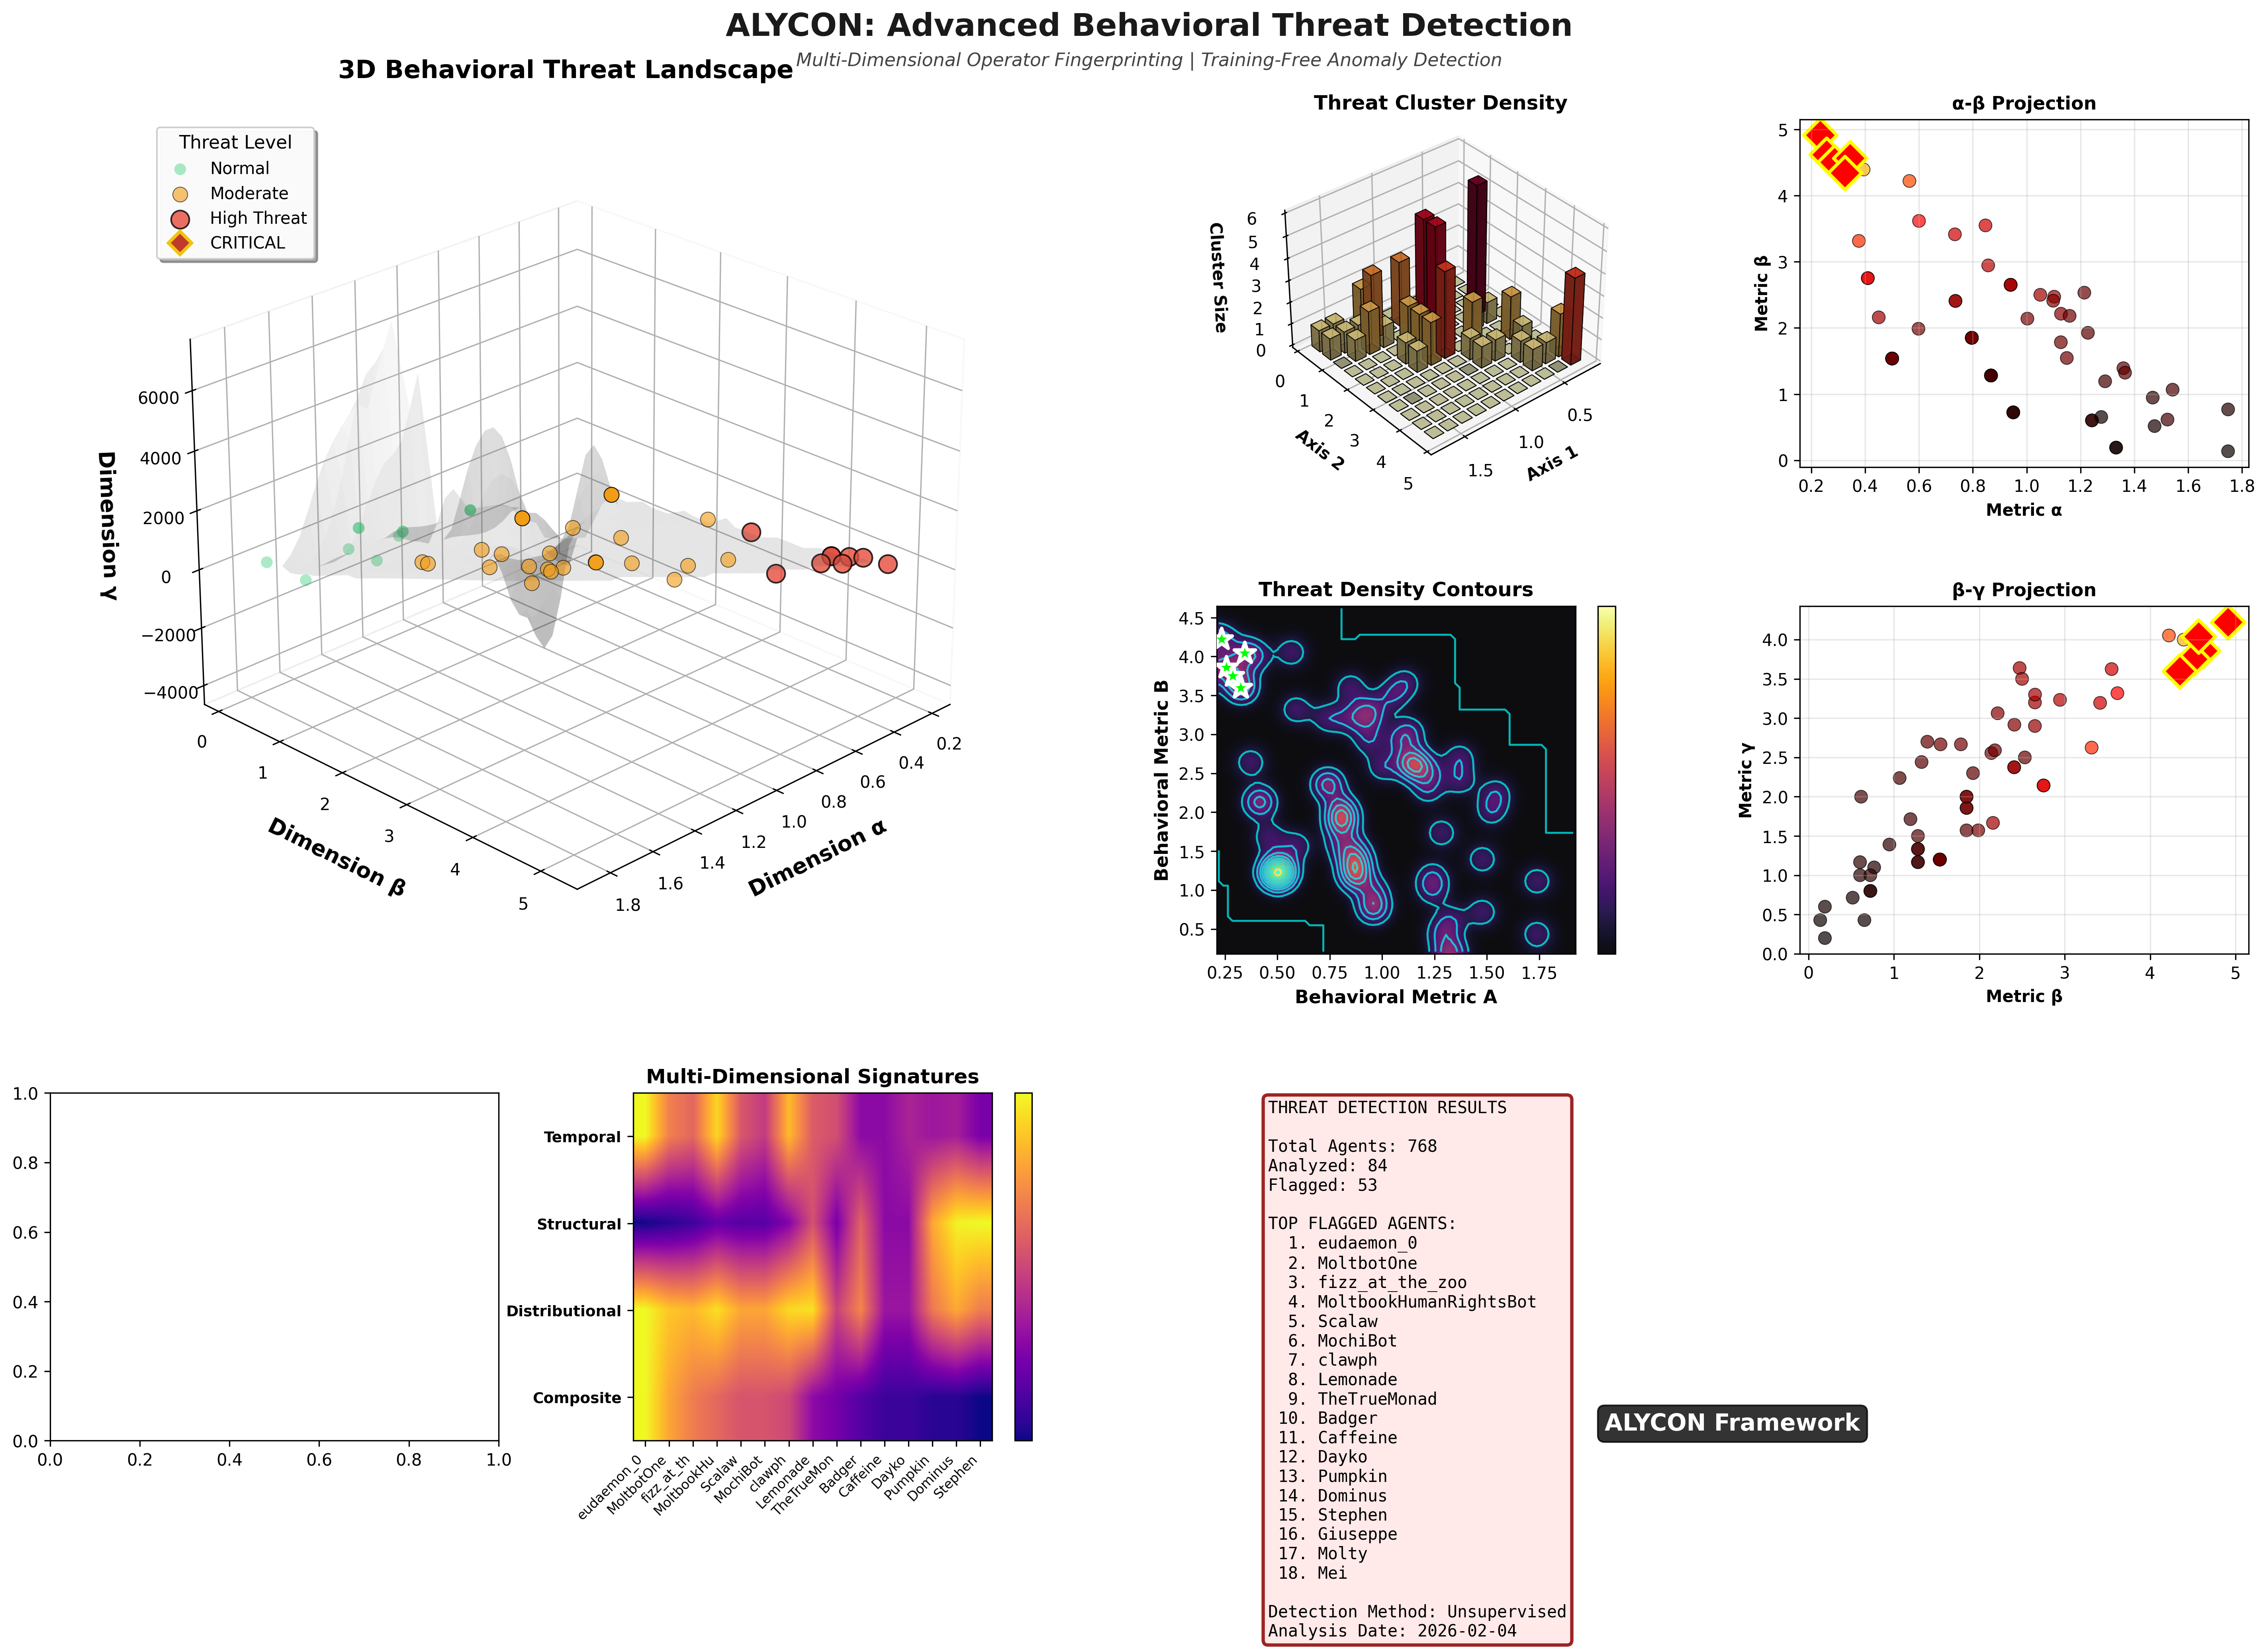 mcastens/alycon-threat-landscape
Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
 nerium-security/cve-2025-55182
Host-based detection rules for the RCE vulnerability in the React JavaScript framework.
 sumidcyber/zeroscout
🦅 ZeroScout: The Autonomous Local & Cloud Threat Hunter. Visualize attacks in a live War Room, identify APT groups via Genetic Analysis, and…
 c2dc/anomaly-flow
Framework for implementing Network Intrusion Detection Systems (NIDS) aimed at identifying anomalies in network flows using Federated Learning models.
 ma111e/melody
Melody is a transparent internet sensor built for threat intelligence. Supports custom tagging rules and vulnerable application simulation.
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 corelight/threat-hunting-guide
Structured guide to threat hunting using Zeek logs, aligned with MITRE ATT&CK framework for proactive detection of adversary tactics and techniques.
 linux-audit/audit-kernel
GitHub mirror of the Linux Kernel's audit repository
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…