
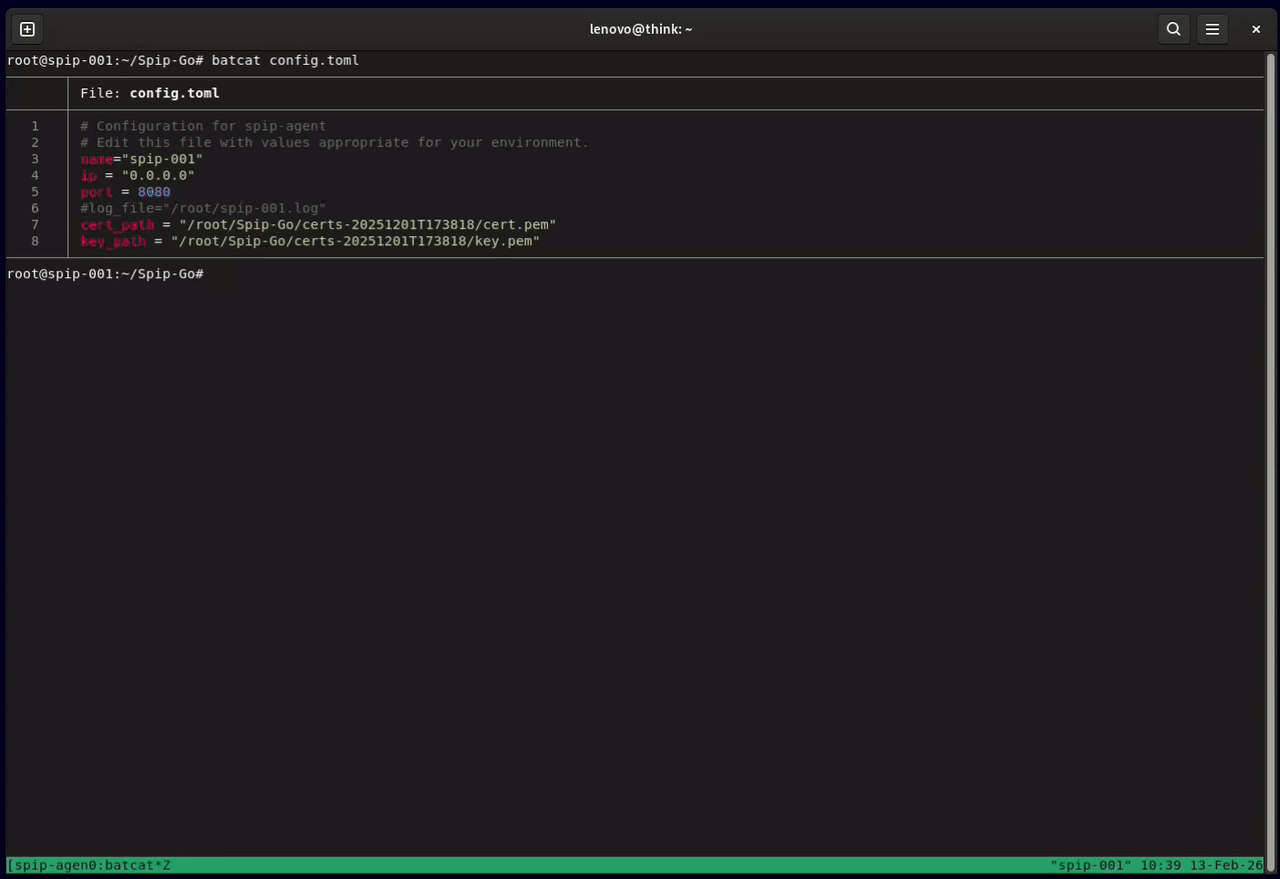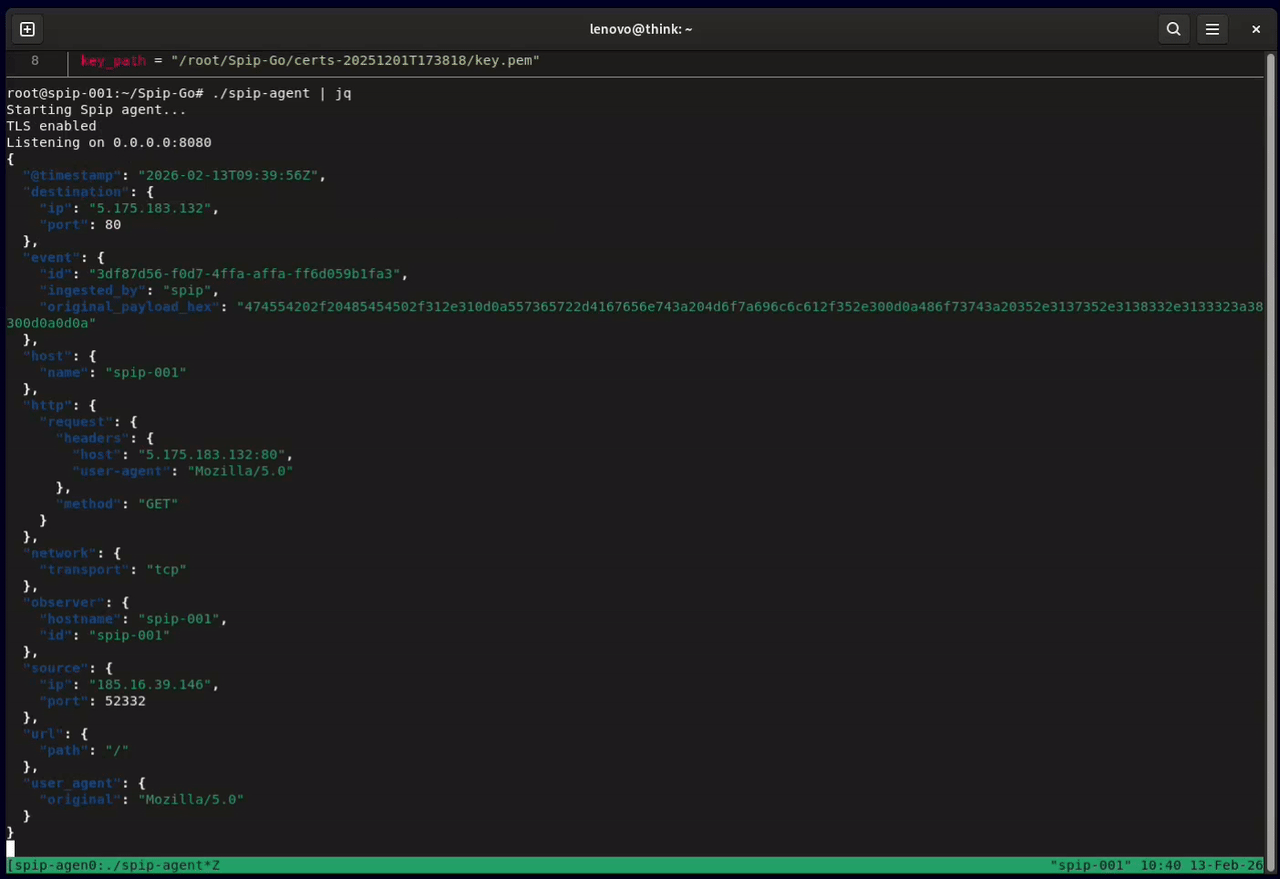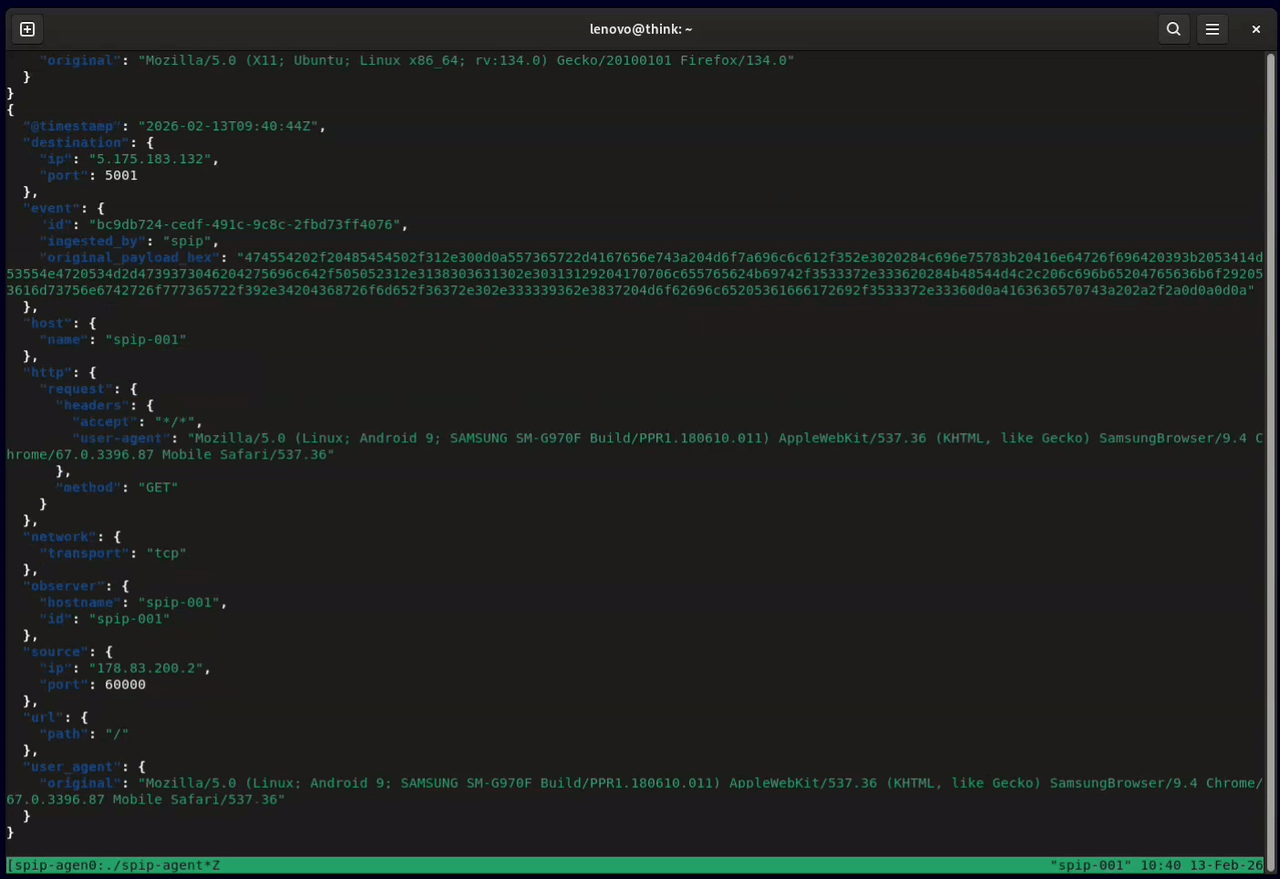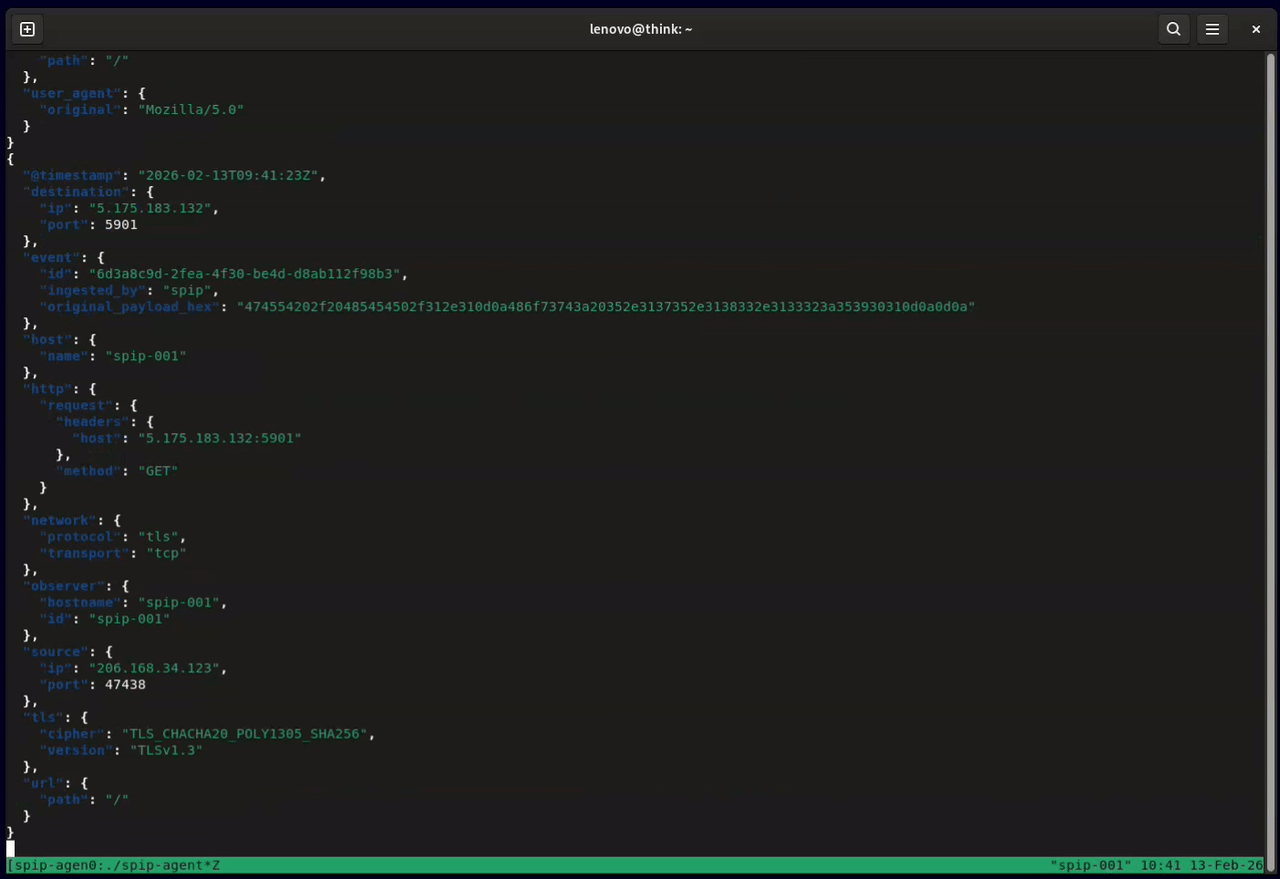
Spip-Go
 honeylabshq/spip-go
Spip network sensor written in Go
defensive-toolsincident-responseinformation-gathering+7
honeylabshq/spip-goSpip network sensor written in Go
 kismetwireless/kismet
Github mirror of official Kismet repository
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
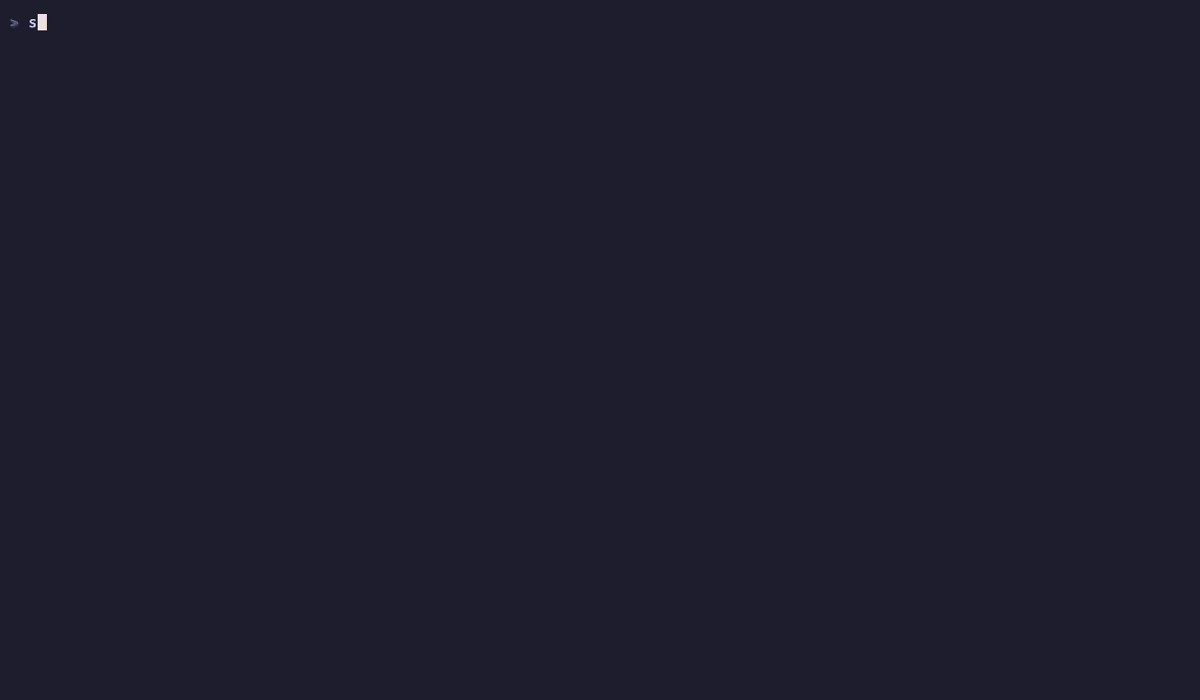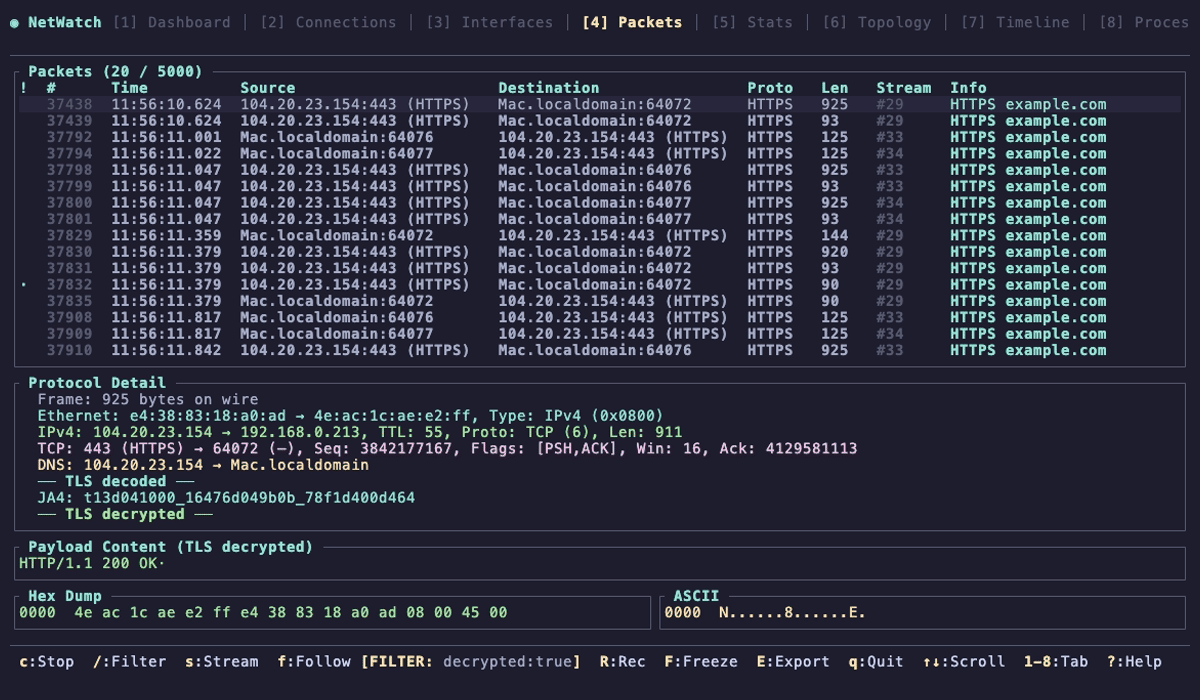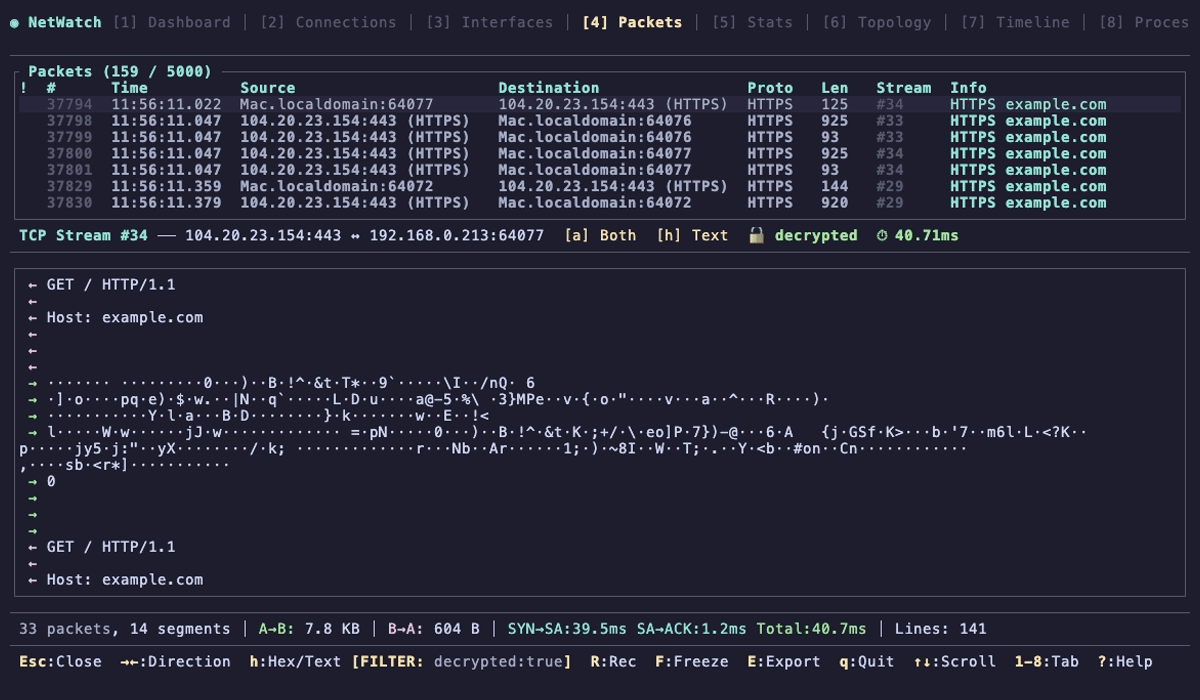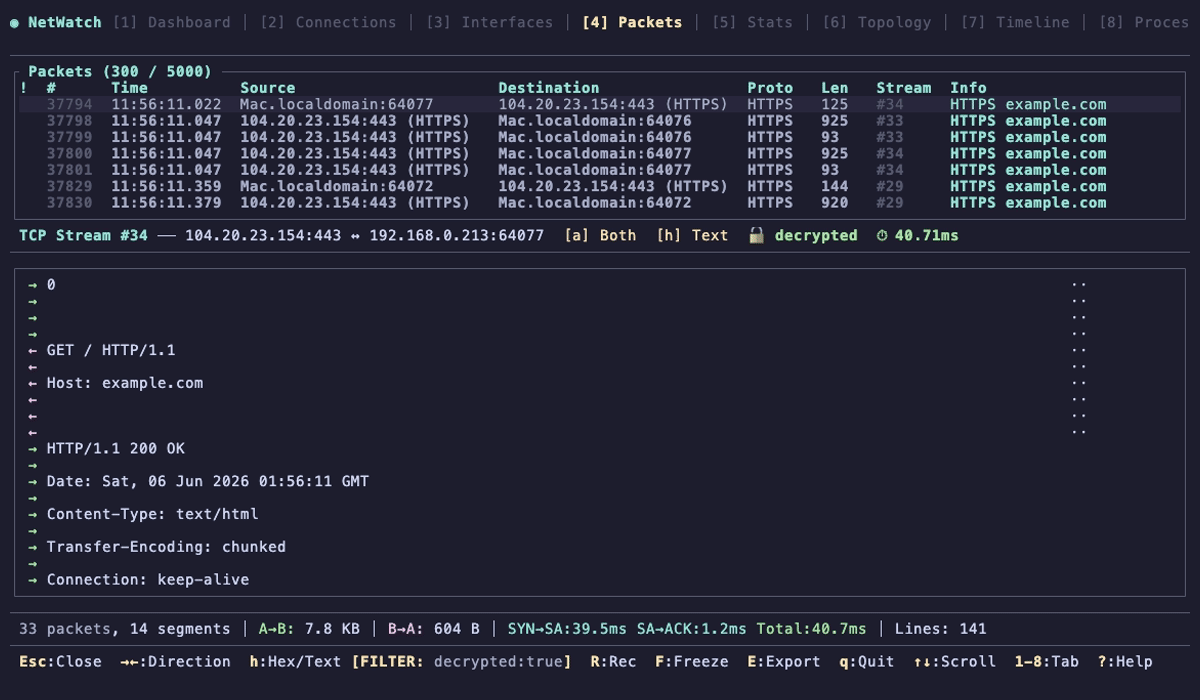 matthart1983/netwatch
Real-time network diagnostics in your terminal. One command, zero config, instant visibility.
 rbidou/pyrasp
Runtime Application Self Protection for Python web servers, serverless functions and MCP servers, detecting attacks, prompt injection and data leaks…
 corelight/ecs-logstash-mappings
Mapping Corelight or Zeek data to Elastic Common Schema logs
 fox-it/cisco-ios-xe-implant-detection
Cisco IOS XE implant scanning & detection (CVE-2023-20198, CVE-2023-20273)
 the-tcpdump-group/libpcap
System-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…
 foxio-llc/ja4
JA4+ is a suite of network fingerprinting standards
 manishrawat21/detection-rules
This repository contains validated detection rules for adversary behaviors observed during APT29 simulation. Each rule was tested against the actual…
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
 ait-aecid/logdata-anomaly-miner
This tool parses log data and allows to define analysis pipelines for anomaly detection. It was designed to run the analysis with limited resources…
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
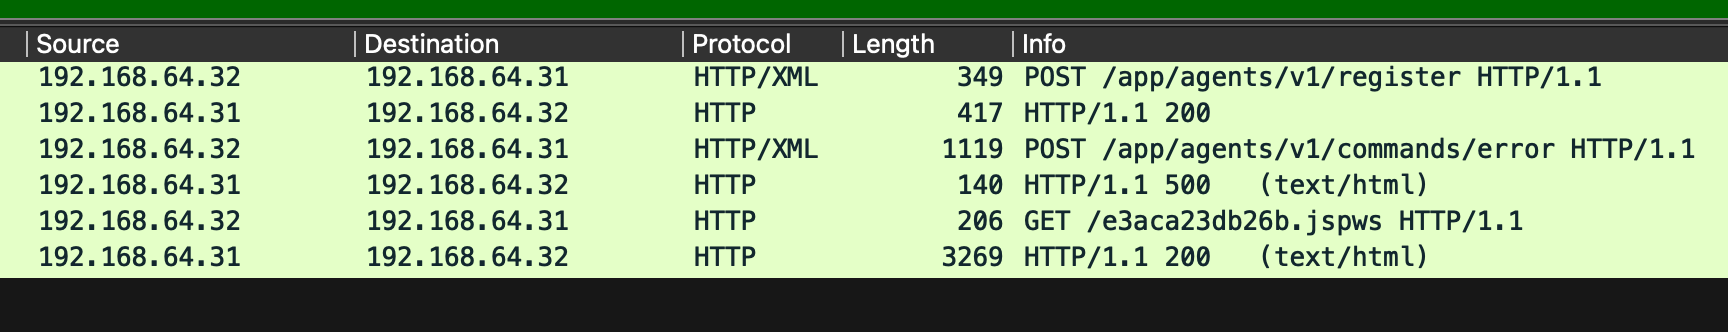 boredhackerblog/teamcity-cve-2026-63077-pcap
teamcity teamcity-CVE-2026-63077 exploitation pcap
 nfstream/nfstream
NFStream: a Flexible Network Data Analysis Framework.
 eliangonzi00/pockeycloakcve-2023-0264
Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…
 agentshield-ai/sigma-ai
Sigma detection rules for AI agent security monitoring