Zeek-Intelligence-Feeds

Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…

Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…

The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…

PacketFence is a fully supported, trusted, Free and Open Source network access control (NAC) solution. Boasting an impressive feature set including a…

Real-time malicious traffic detection system using public blacklists, static malware trails, and heuristic analysis to identify threats across DNS,…

Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…

ZoneMinder is a free, open source Closed-circuit television software application developed for Linux which supports IP, USB and Analog cameras.

Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…

Arkime is an open source, large scale, full packet capturing, indexing, and database system.

Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration

TheLightScope

This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…

Zeek is a powerful network analysis framework that is much different from the typical IDS you may know.

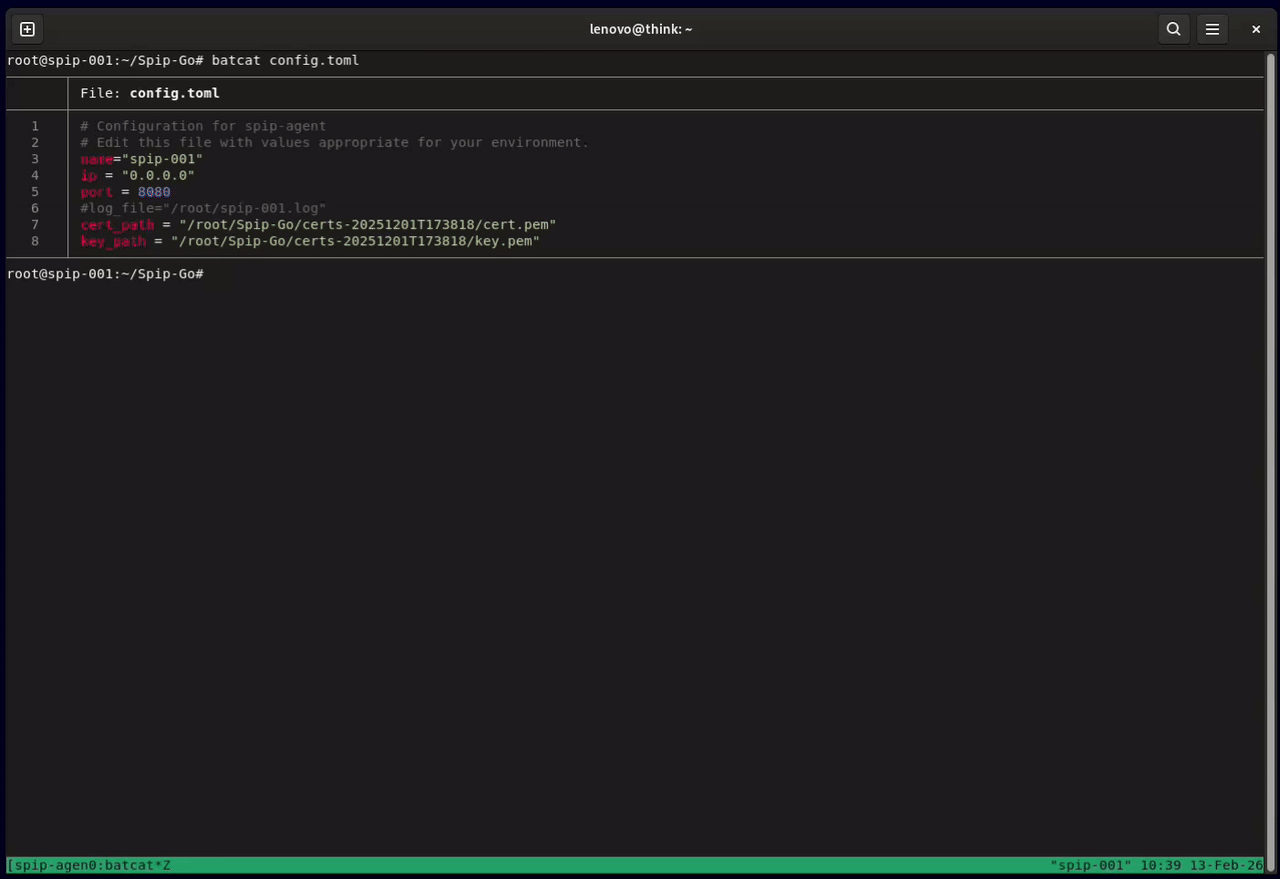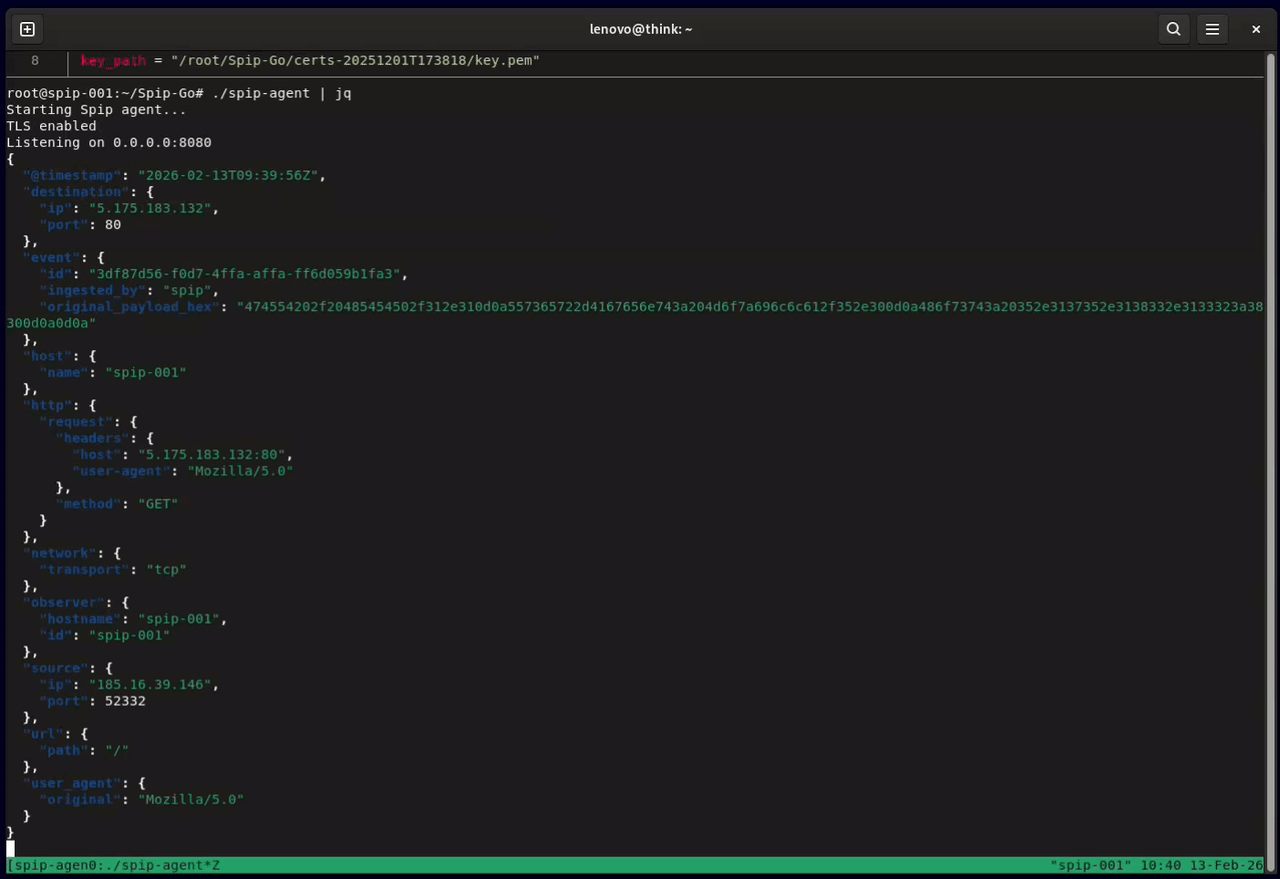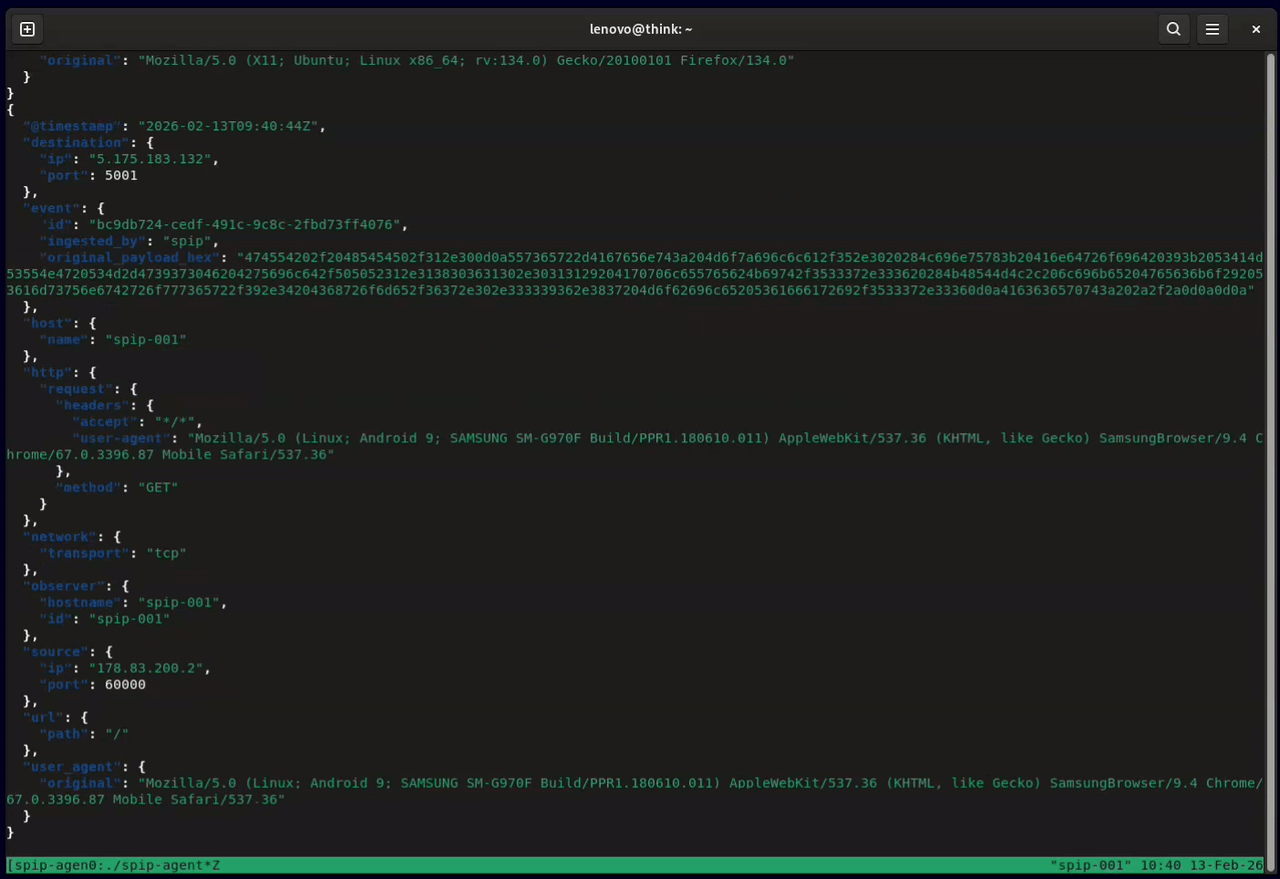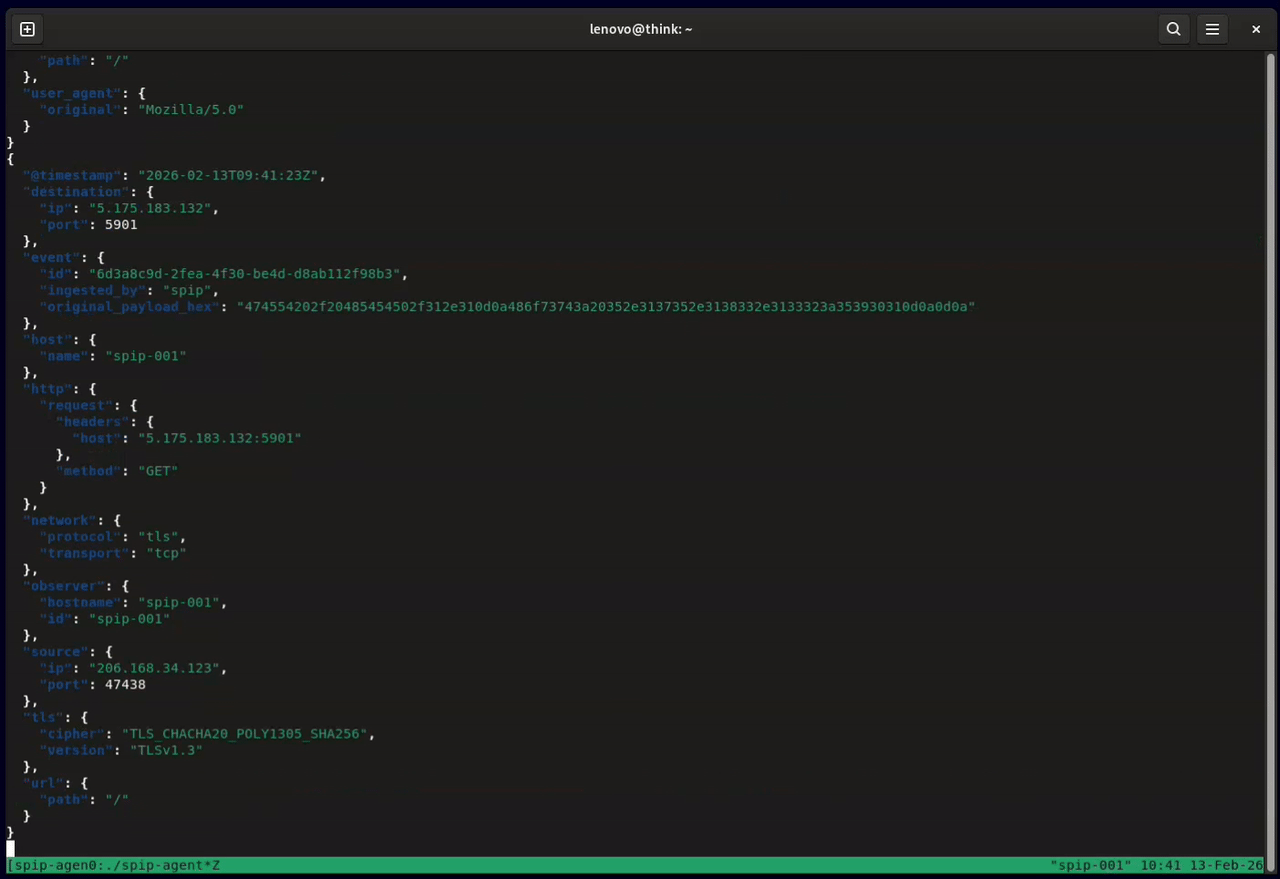
Spip network sensor written in Go

Containerized network traffic analysis suite ingesting PCAP, Zeek logs, and Suricata alerts for automated normalization, enrichment, and correlation…

Malcolm is a powerful, easily deployable network traffic analysis tool suite for full packet capture artifacts (PCAP files), Zeek logs and Suricata…

Open Source Deep Packet Inspection Software Toolkit

Github mirror of official Kismet repository

Advanced Phishing Protection: Suricata rulesets open and free