

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
74 results
arkime preview

arkime

GitHubarkime/arkime

Arkime is an open source, large scale, full packet capturing, indexing, and database system.
defensive-toolsdigital-forensicsforensics+7
7.6k12h 9m ago
TLDR preview

TLDR

GitLabgitlab-security-oss/tldr

Sigma-based detection rules, log queries, atomic tests, and response procedures for monitoring and threat hunting in GitLab environments.

curated-resourcesdefensive-toolseducation+3
31 day ago
Threat-Hunting preview

Threat-Hunting

GitHuba2awais/threat-hunting

Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
educationincident-responseinformation-gathering+4
862 days ago
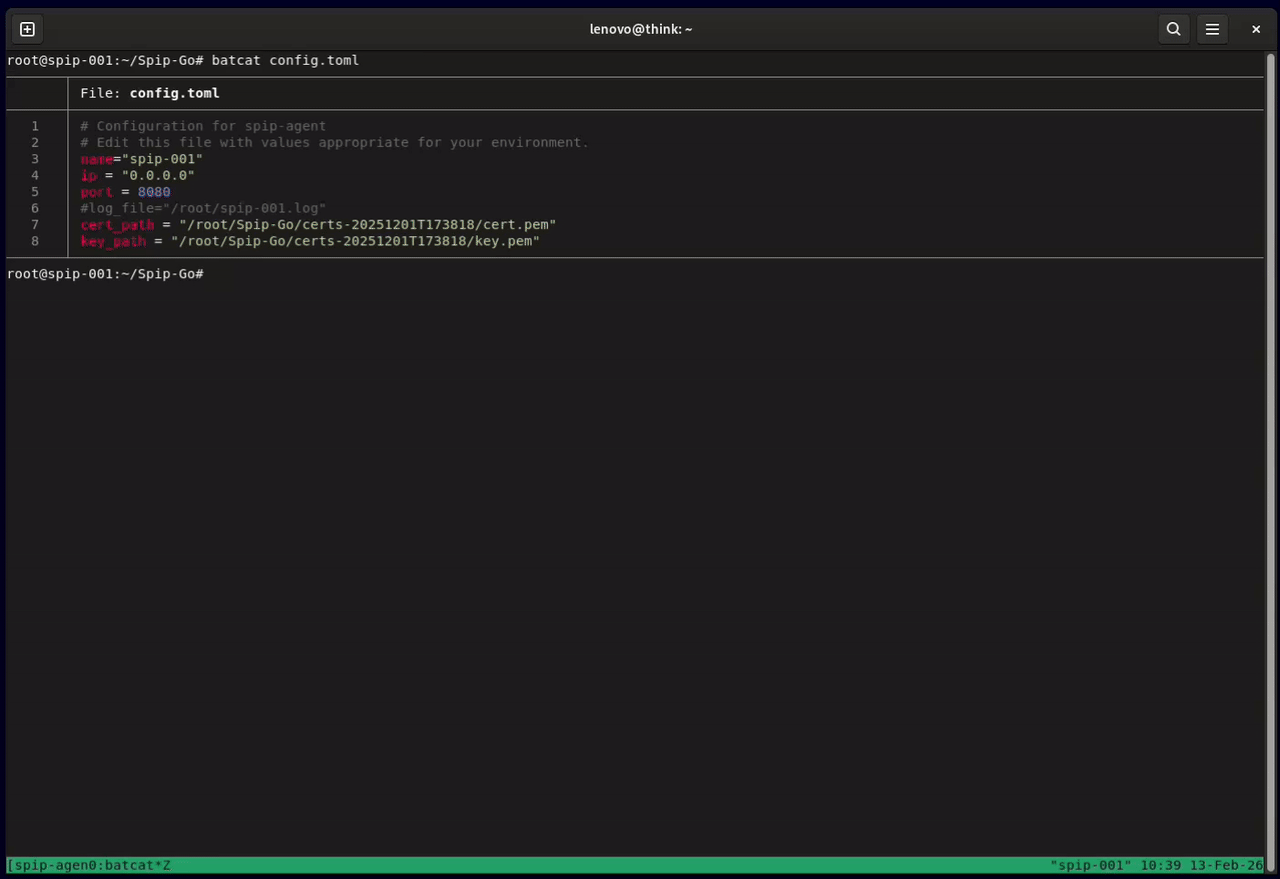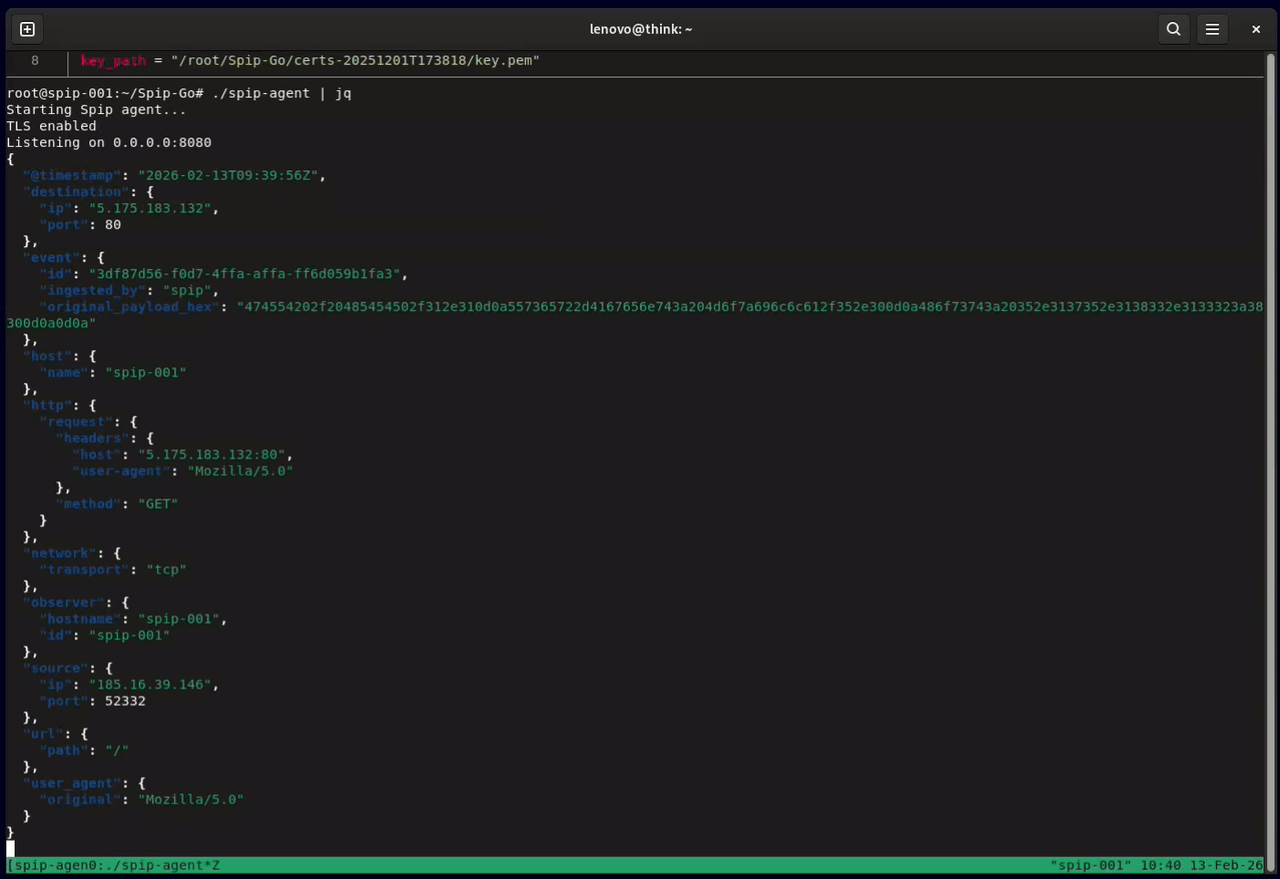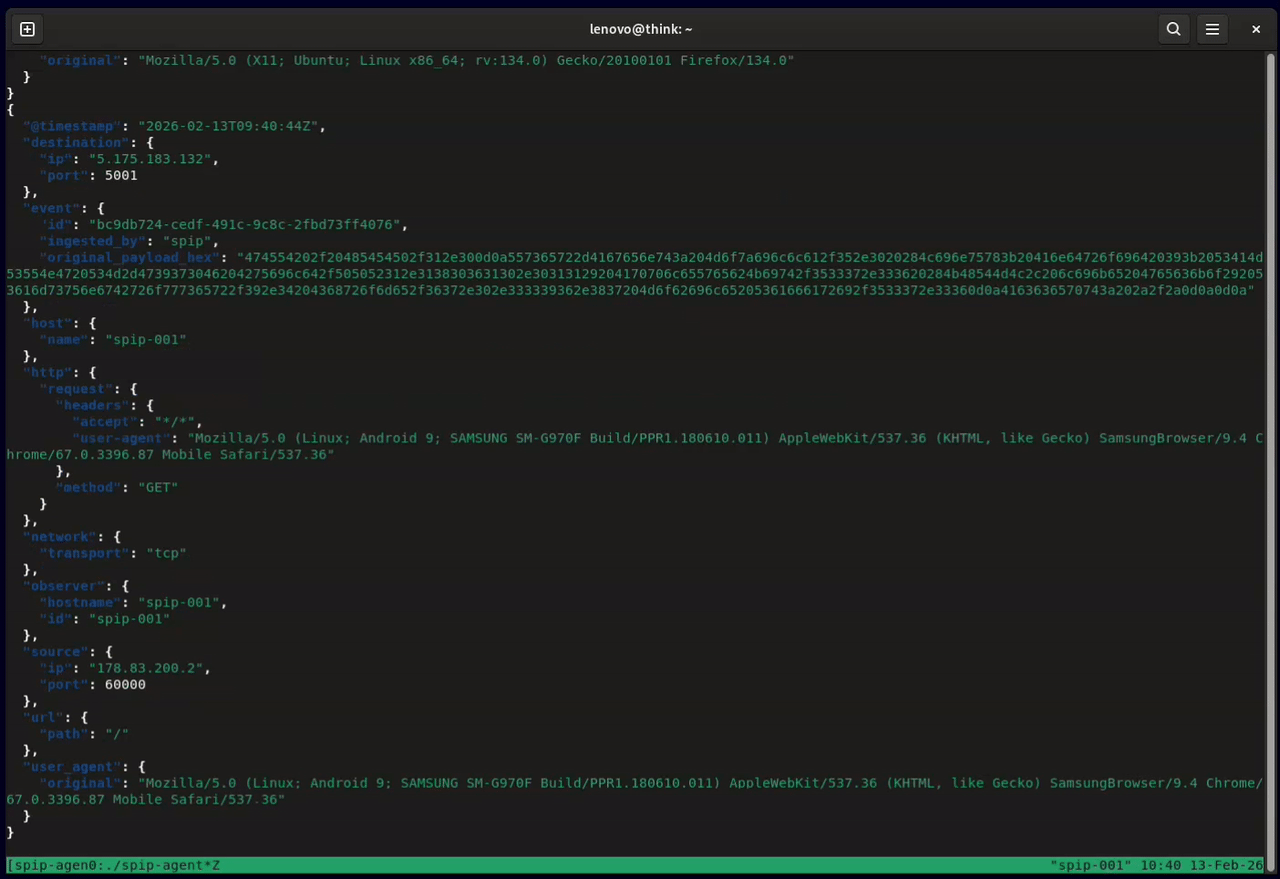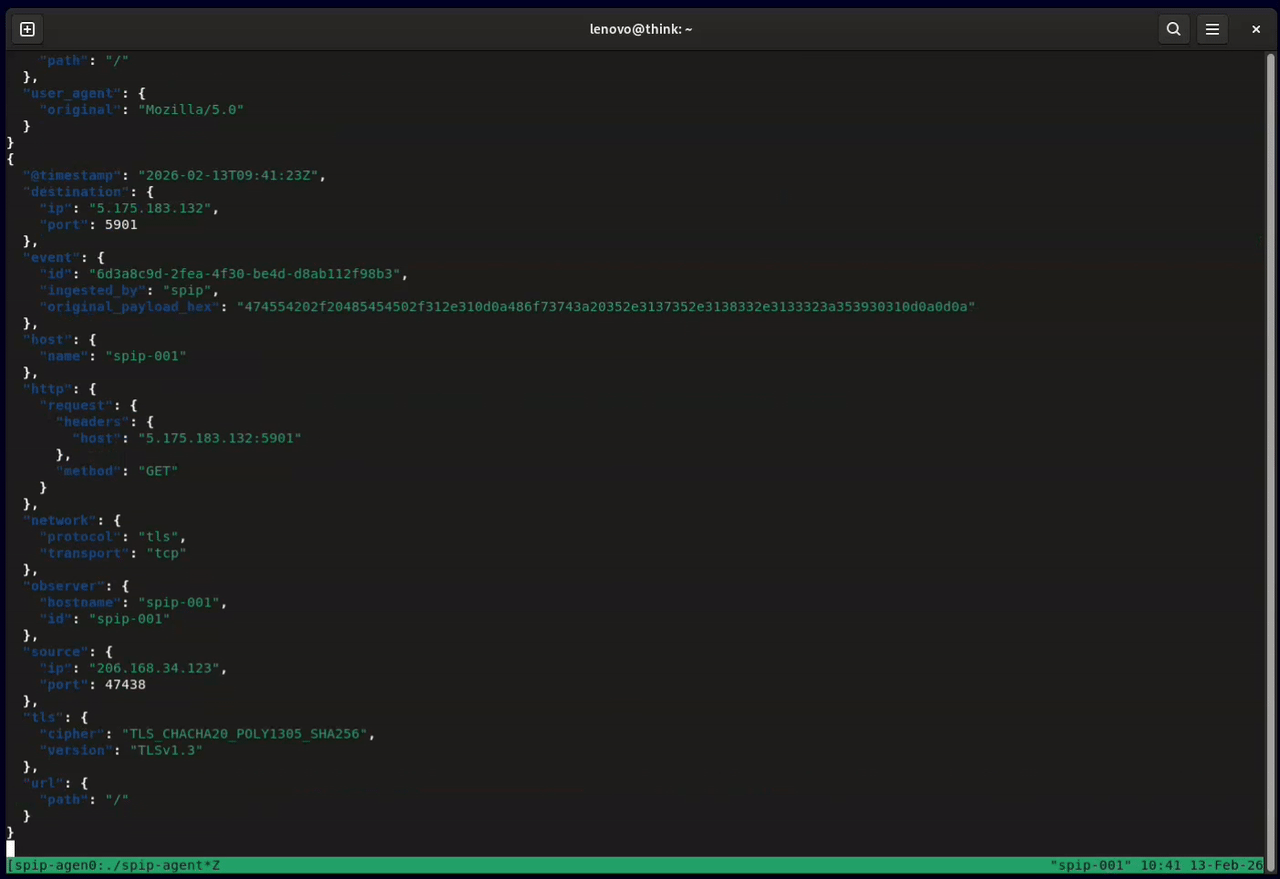
ecs-logstash-mappings preview

ecs-logstash-mappings

GitHubcorelight/ecs-logstash-mappings

Mapping Corelight or Zeek data to Elastic Common Schema logs
incident-responseintrusion-detectionlog-analysis+2
123 days ago
Spip-Go preview

Spip-Go

GitHubhoneylabshq/spip-go

Spip network sensor written in Go
defensive-toolsincident-responseinformation-gathering+7
83 days ago
DeTTECT preview

DeTTECT

GitHubrabobank-cdc/dettect

Detect Tactics, Techniques & Combat Threats
defensive-toolsincident-responseintrusion-detection+4
2.4k10 days ago
sysmon-modular preview

sysmon-modular

GitHubolafhartong/sysmon-modular

A repository of sysmon configuration modules

defensive-toolsdigital-forensicsincident-response+2
3.2k15 days ago
OpcUaTrap preview

OpcUaTrap

GitHub0xajstrike/opcuatrap

High-interaction OPC UA honeypot for ICS/SCADA — multi-profile (oil & gas, water, power grid), live process simulation, per-session threat scoring,…

defensive-toolsincident-responseinformation-gathering+5
221 days ago
dshield preview

dshield

GitHubdshield-isc/dshield

Installs and configures a DShield honeypot sensor on Raspberry Pi or Ubuntu, running Cowrie SSH and HTTP honeypots and forwarding firewall logs to…
defensive-toolsincident-responseinformation-gathering+5
53624 days ago
cisco-ios-xe-implant-detection preview

cisco-ios-xe-implant-detection

GitHubfox-it/cisco-ios-xe-implant-detection

Cisco IOS XE implant scanning & detection (CVE-2023-20198, CVE-2023-20273)

exploitationforensicsintrusion-detection+3
4129 days ago
ddos-reduction-system preview

ddos-reduction-system

GitHubdevinblack001/ddos-reduction-system

Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…

anomaly-detectiondefensive-toolsincident-response+6
21 month ago
GPEWebDefender preview

GPEWebDefender

GitHubgopasteverything/gpewebdefender

Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.

defensive-toolsincident-responseinformation-gathering+8
52 months ago
NetScope preview

NetScope

GitHubspectralzero/netscope

Offline-first network investigation and response platform for Windows. Turns a pcap or live capture into a full forensic verdict — attack story,…
anomaly-detectiondigital-forensicsincident-response+5
42 months ago
wp2shell-compromise-scanner-plugin preview

wp2shell-compromise-scanner-plugin

GitHubeyesecurity/wp2shell-compromise-scanner-plugin

Read-only WordPress plugin that scans for artifacts of the wp2shell exploit chain (CVE-2026-63030 / CVE-2026-60137)
database-securitydigital-forensicsforensics+5
3 months ago
CVE-2025-32433-Detection preview

CVE-2025-32433-Detection

GitHubte0rwx/cve-2025-32433-detection

Custom YARA rule for detecting artifacts of CVE-2025-32433, an Erlang/OTP SSH pre-authentication RCE vulnerability. Validated against public PoCs and…
incident-responseintrusion-detectionmalware-analysis+2
3 months ago
thrunt-god preview

thrunt-god

GitHubbackbay-labs/thrunt-god

Threat hunting command system for agentic IDEs
incident-responseinformation-gatheringintrusion-detection+5
413 months ago
rita preview

rita

GitHubactivecm/rita

Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
anomaly-detectioncommand-and-controldns-analysis+4
6674 months ago
copy-fail-CVE-2026-31431-IOC preview

copy-fail-CVE-2026-31431-IOC

GitHubkadir/copy-fail-cve-2026-31431-ioc

Detection, mitigation, and IOC toolkit for Copy Fail CVE-2026-31431 Linux kernel page-cache privilege escalation

forensicsincident-responseintrusion-detection+2
316 months ago
Previous12345Next
