phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…

An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…

Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…

Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)

A real-time traffic monitoring tool that detects and displays network traffic volume per IP address to identify potential DDoS attacks.

Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…

Docker-based lab for CVE-2024-27198 TeamCity authentication bypass. Includes exploit reproduction, IoC hunting with Sigma/Suricata rules, and…

Tool that gathers a customizable set of ETW telemetry and generates user-defined detections

Sniffles: Packet Capture Generator for IDS and Regular Expression Evaluation

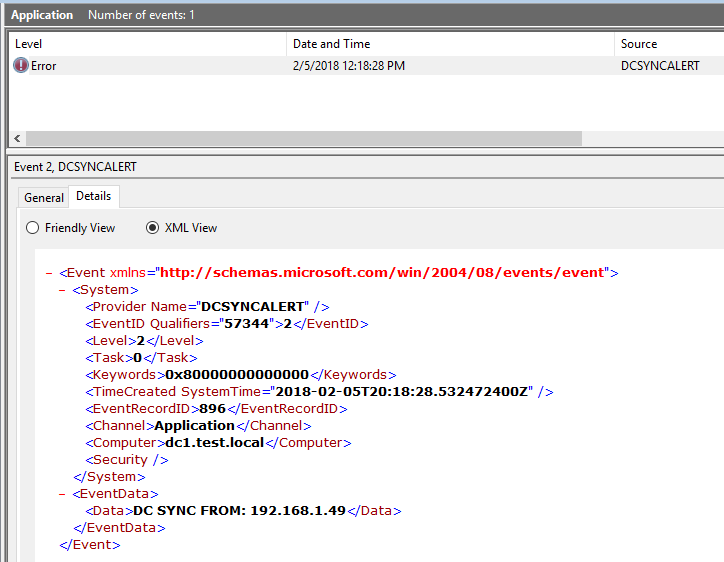
Monitors for DCSYNC and DCSHADOW attacks and create custom Windows Events for these events.

JA4+ is a suite of network fingerprinting standards

PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…

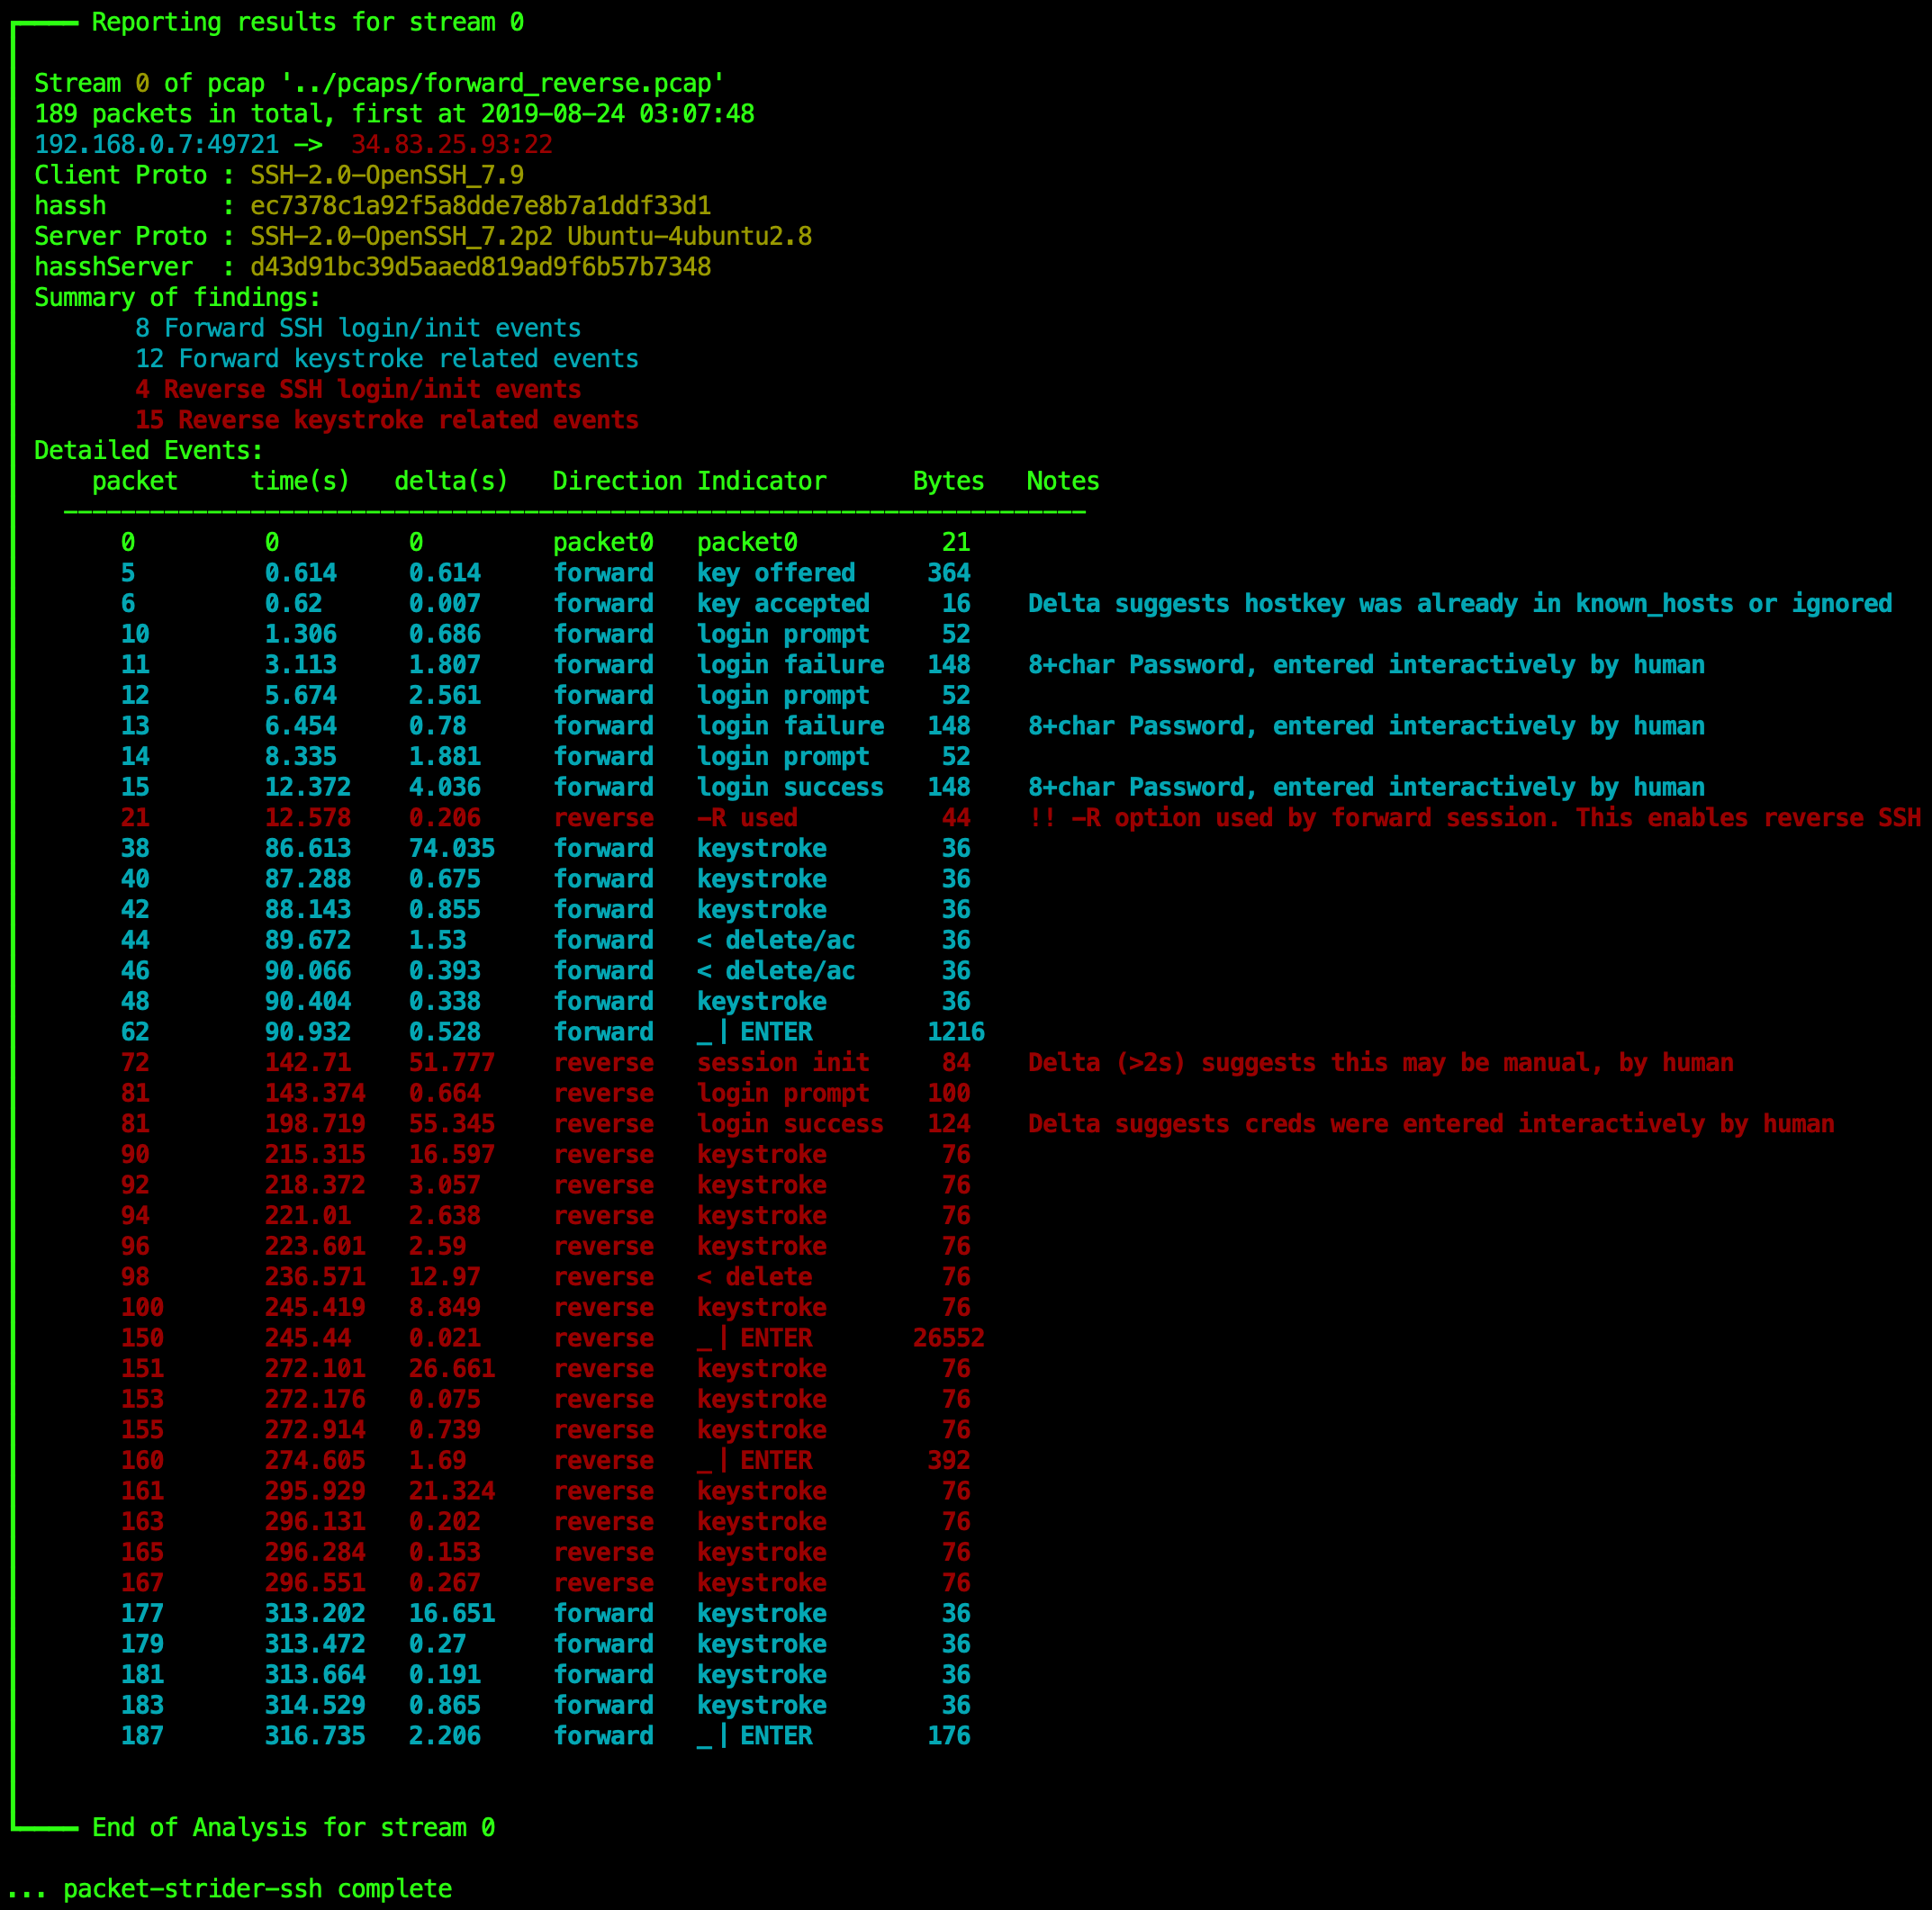
A network packet forensics tool for SSH

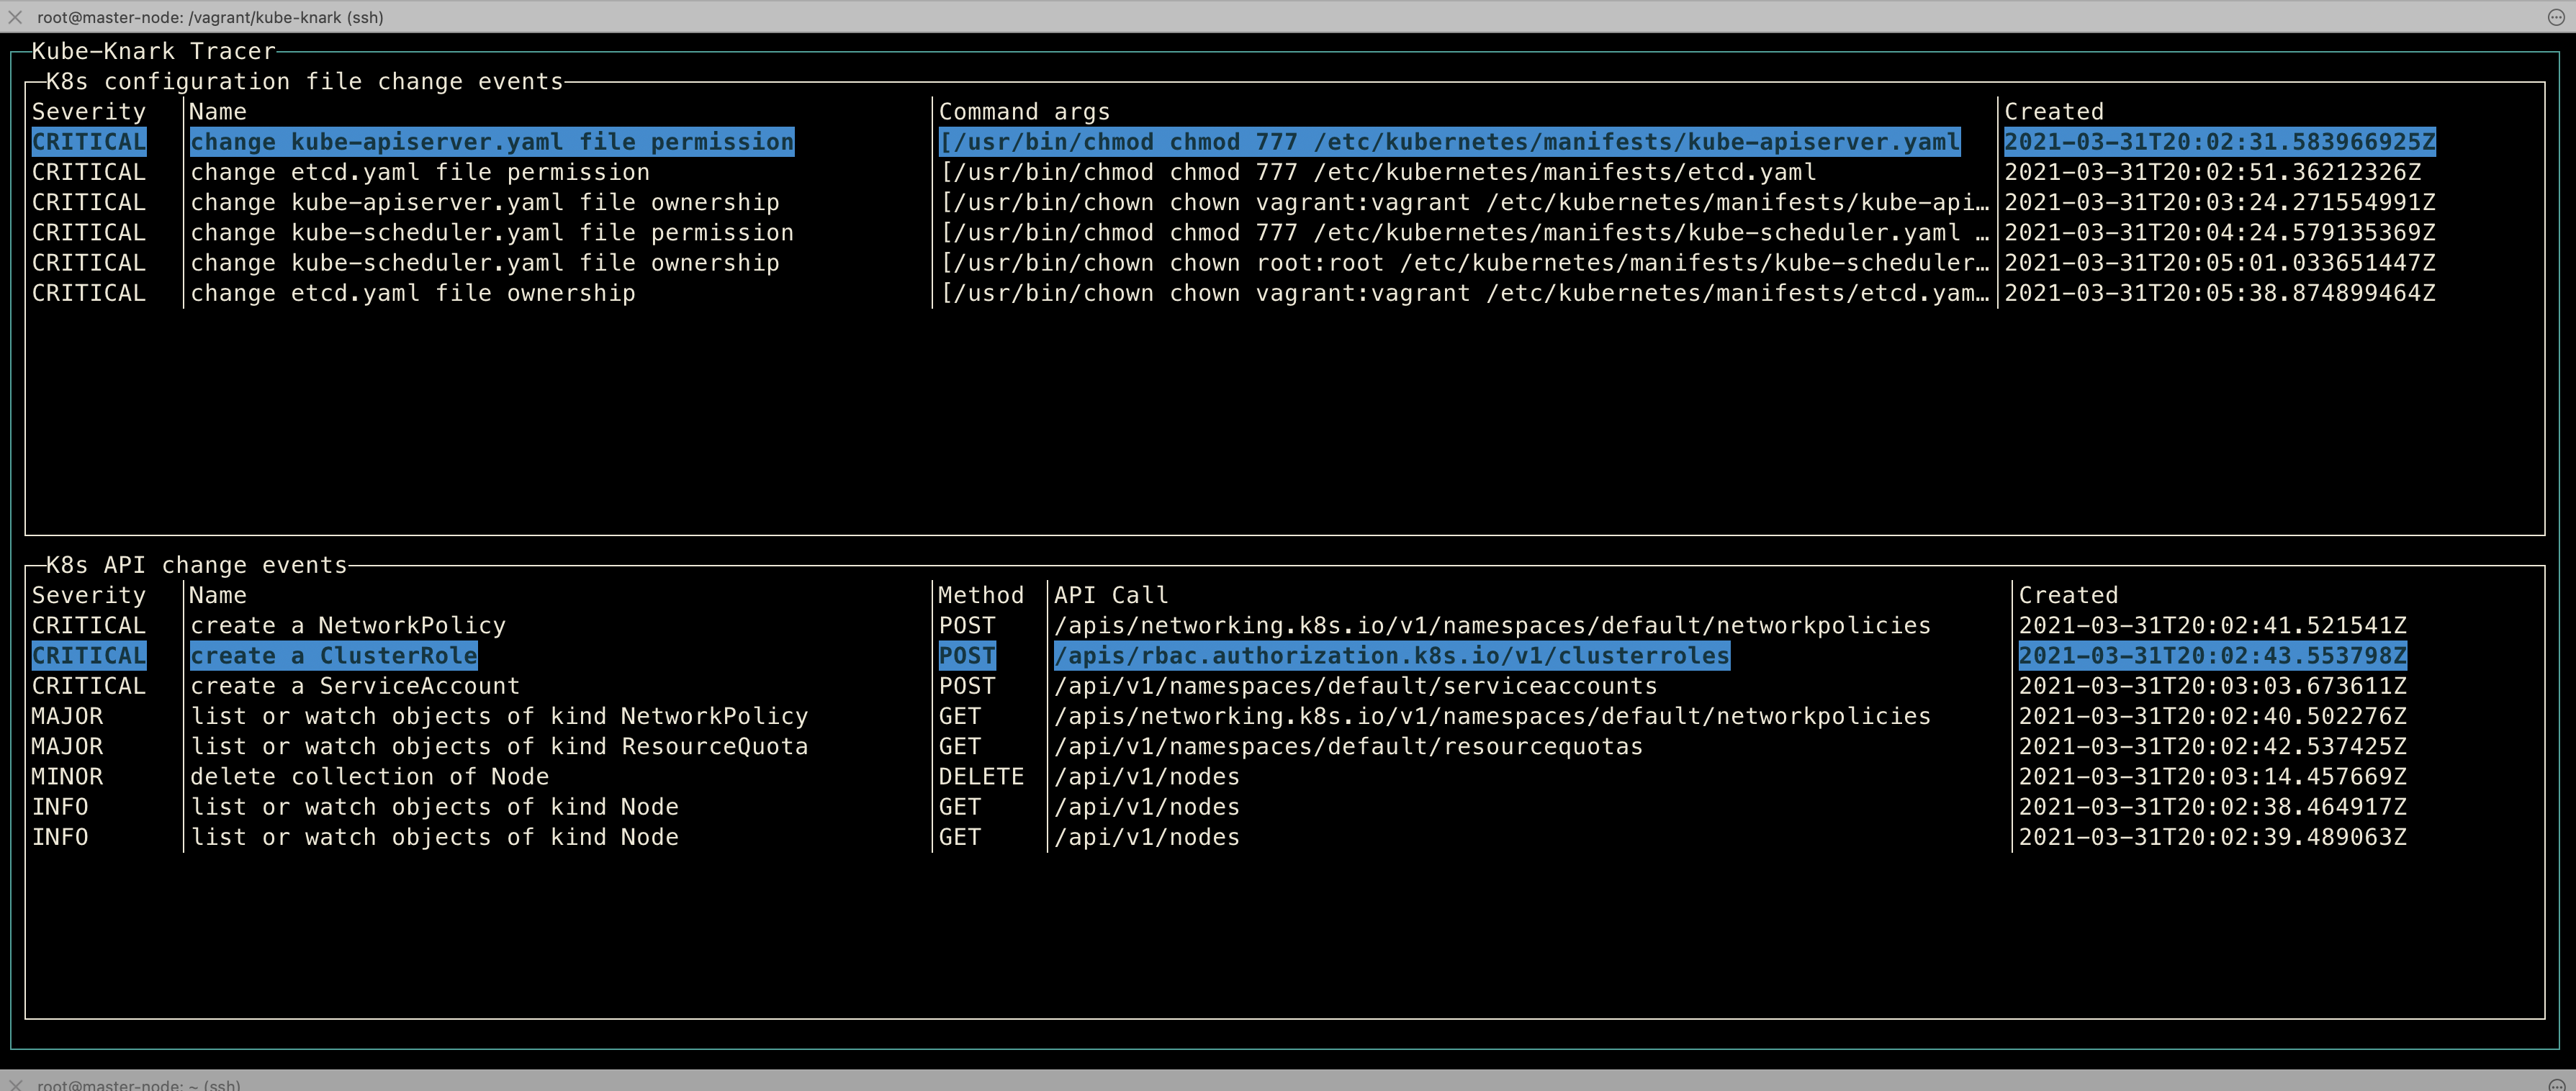
Open Source runtime tool which help to detect malware code execution and run time mis-configuration change on a kubernetes cluster

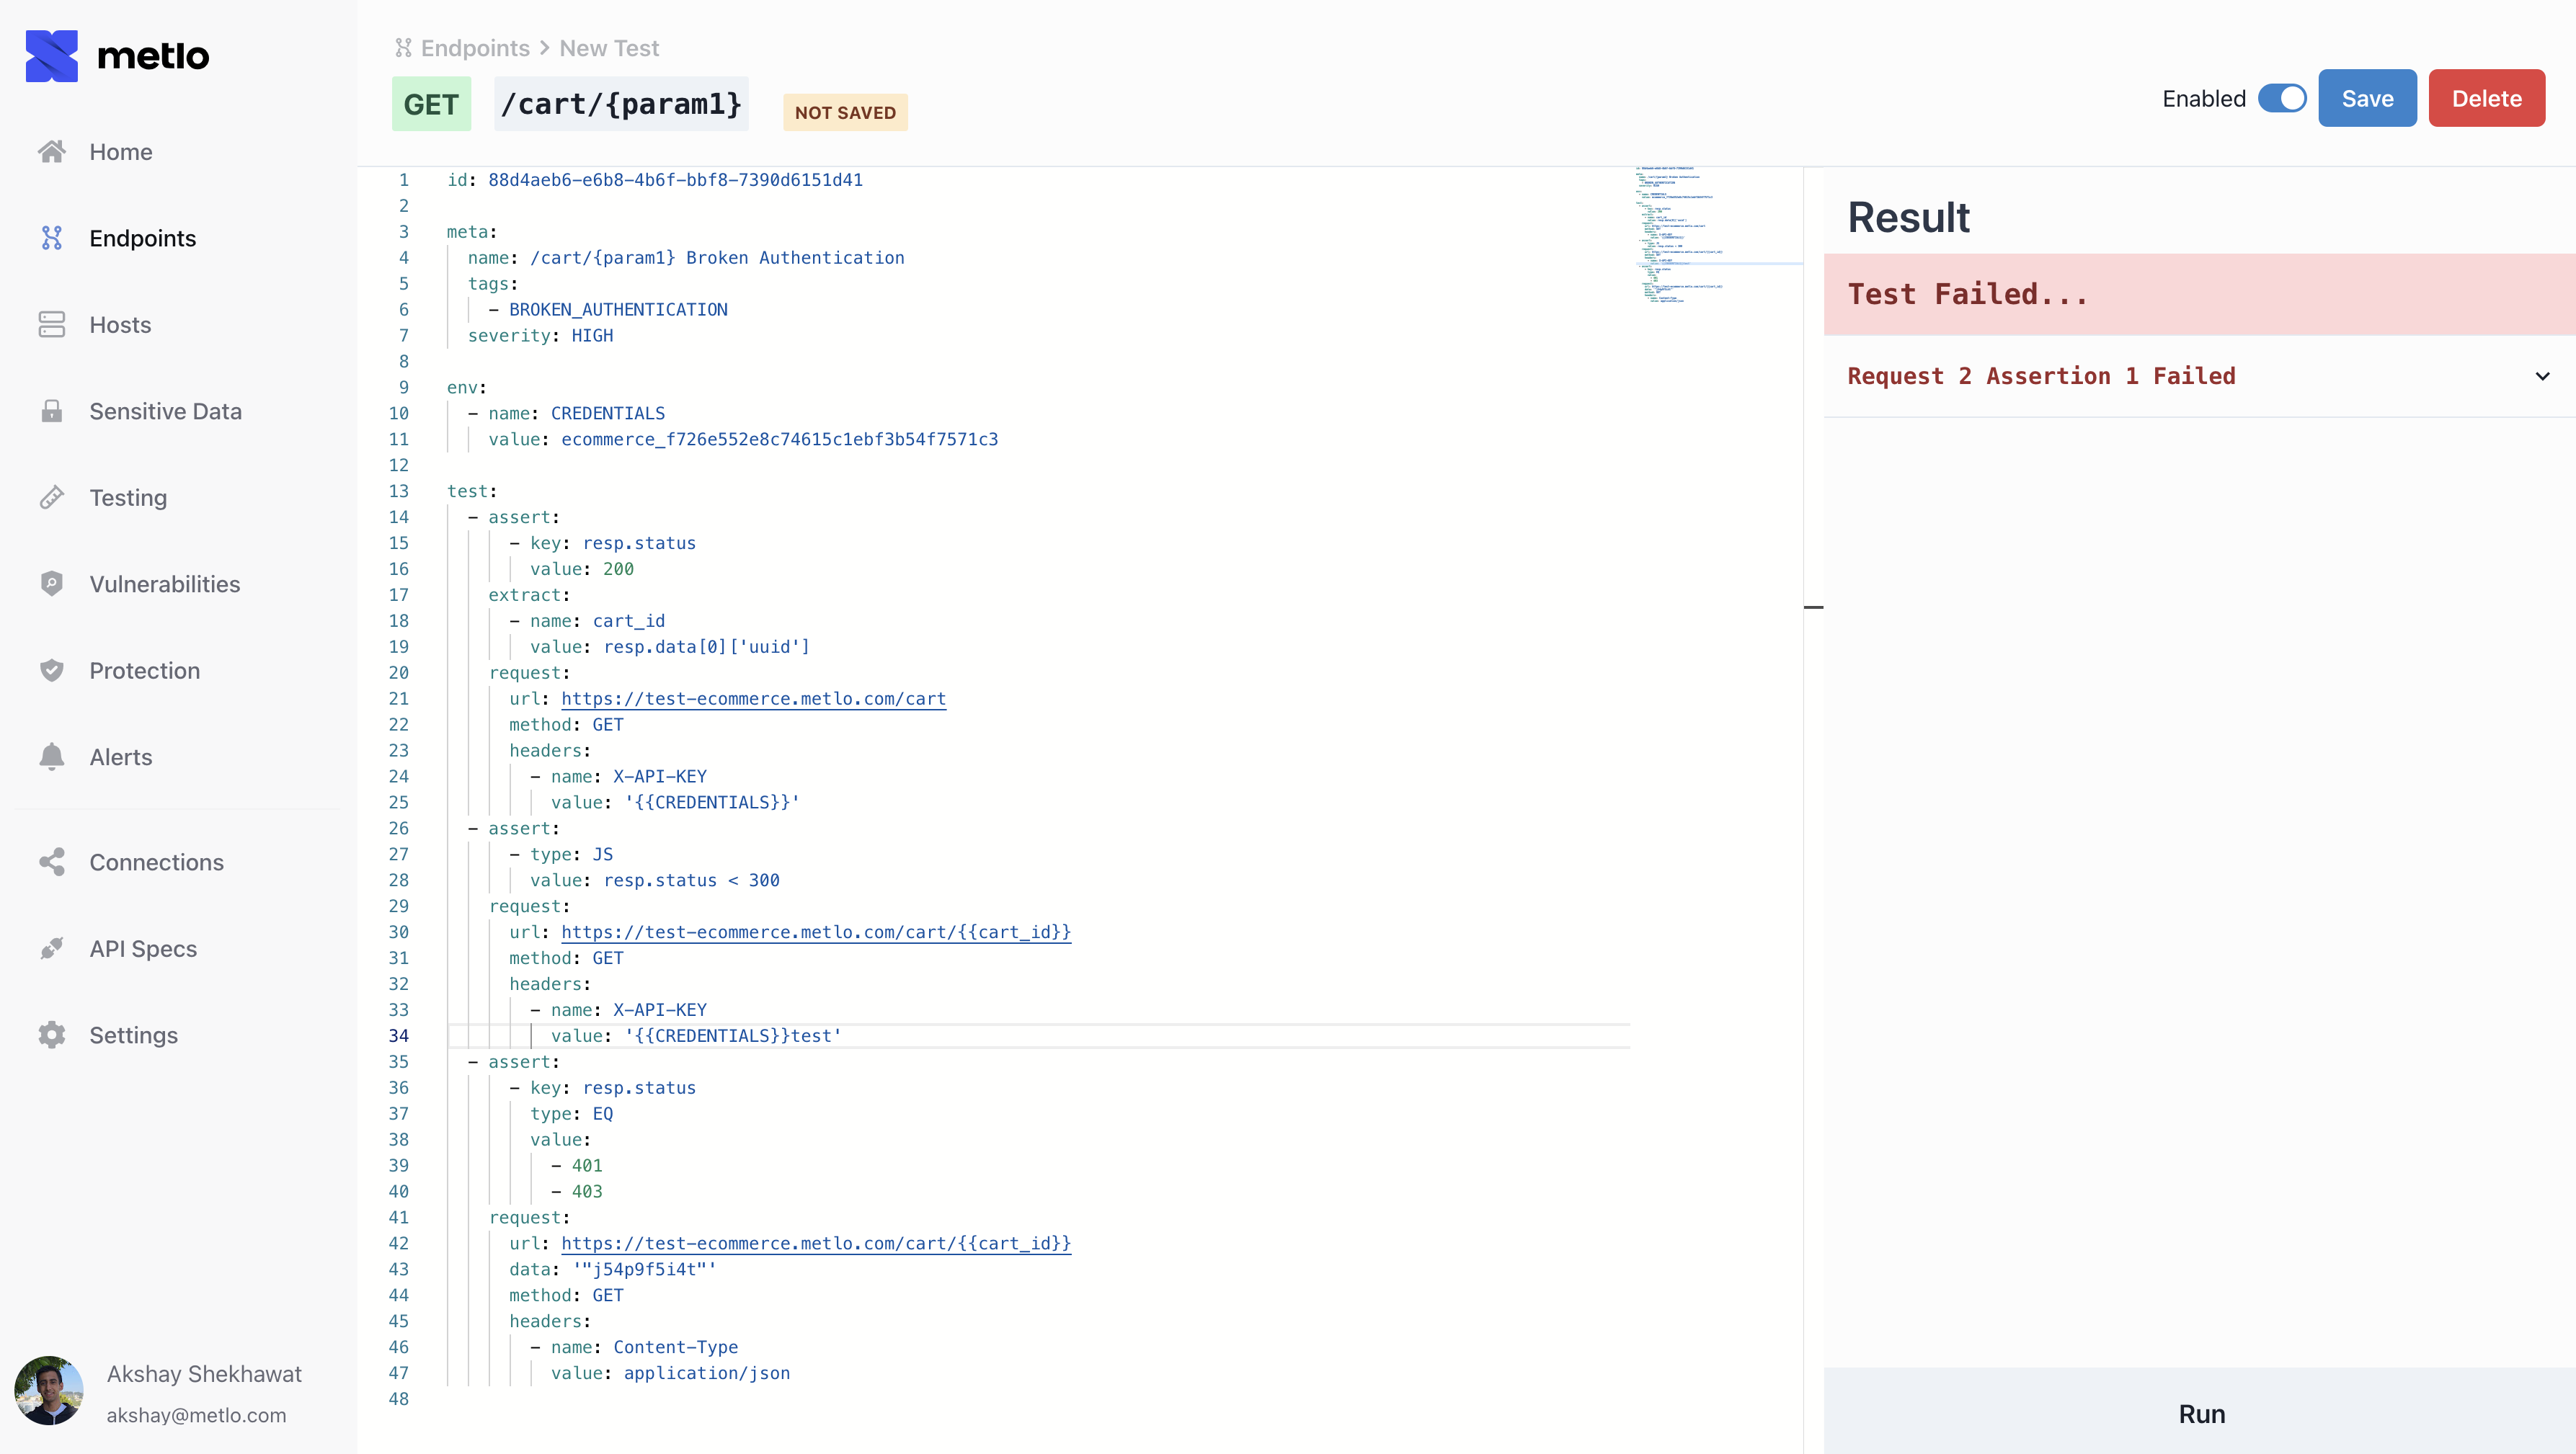
Metlo is an open-source API security platform.

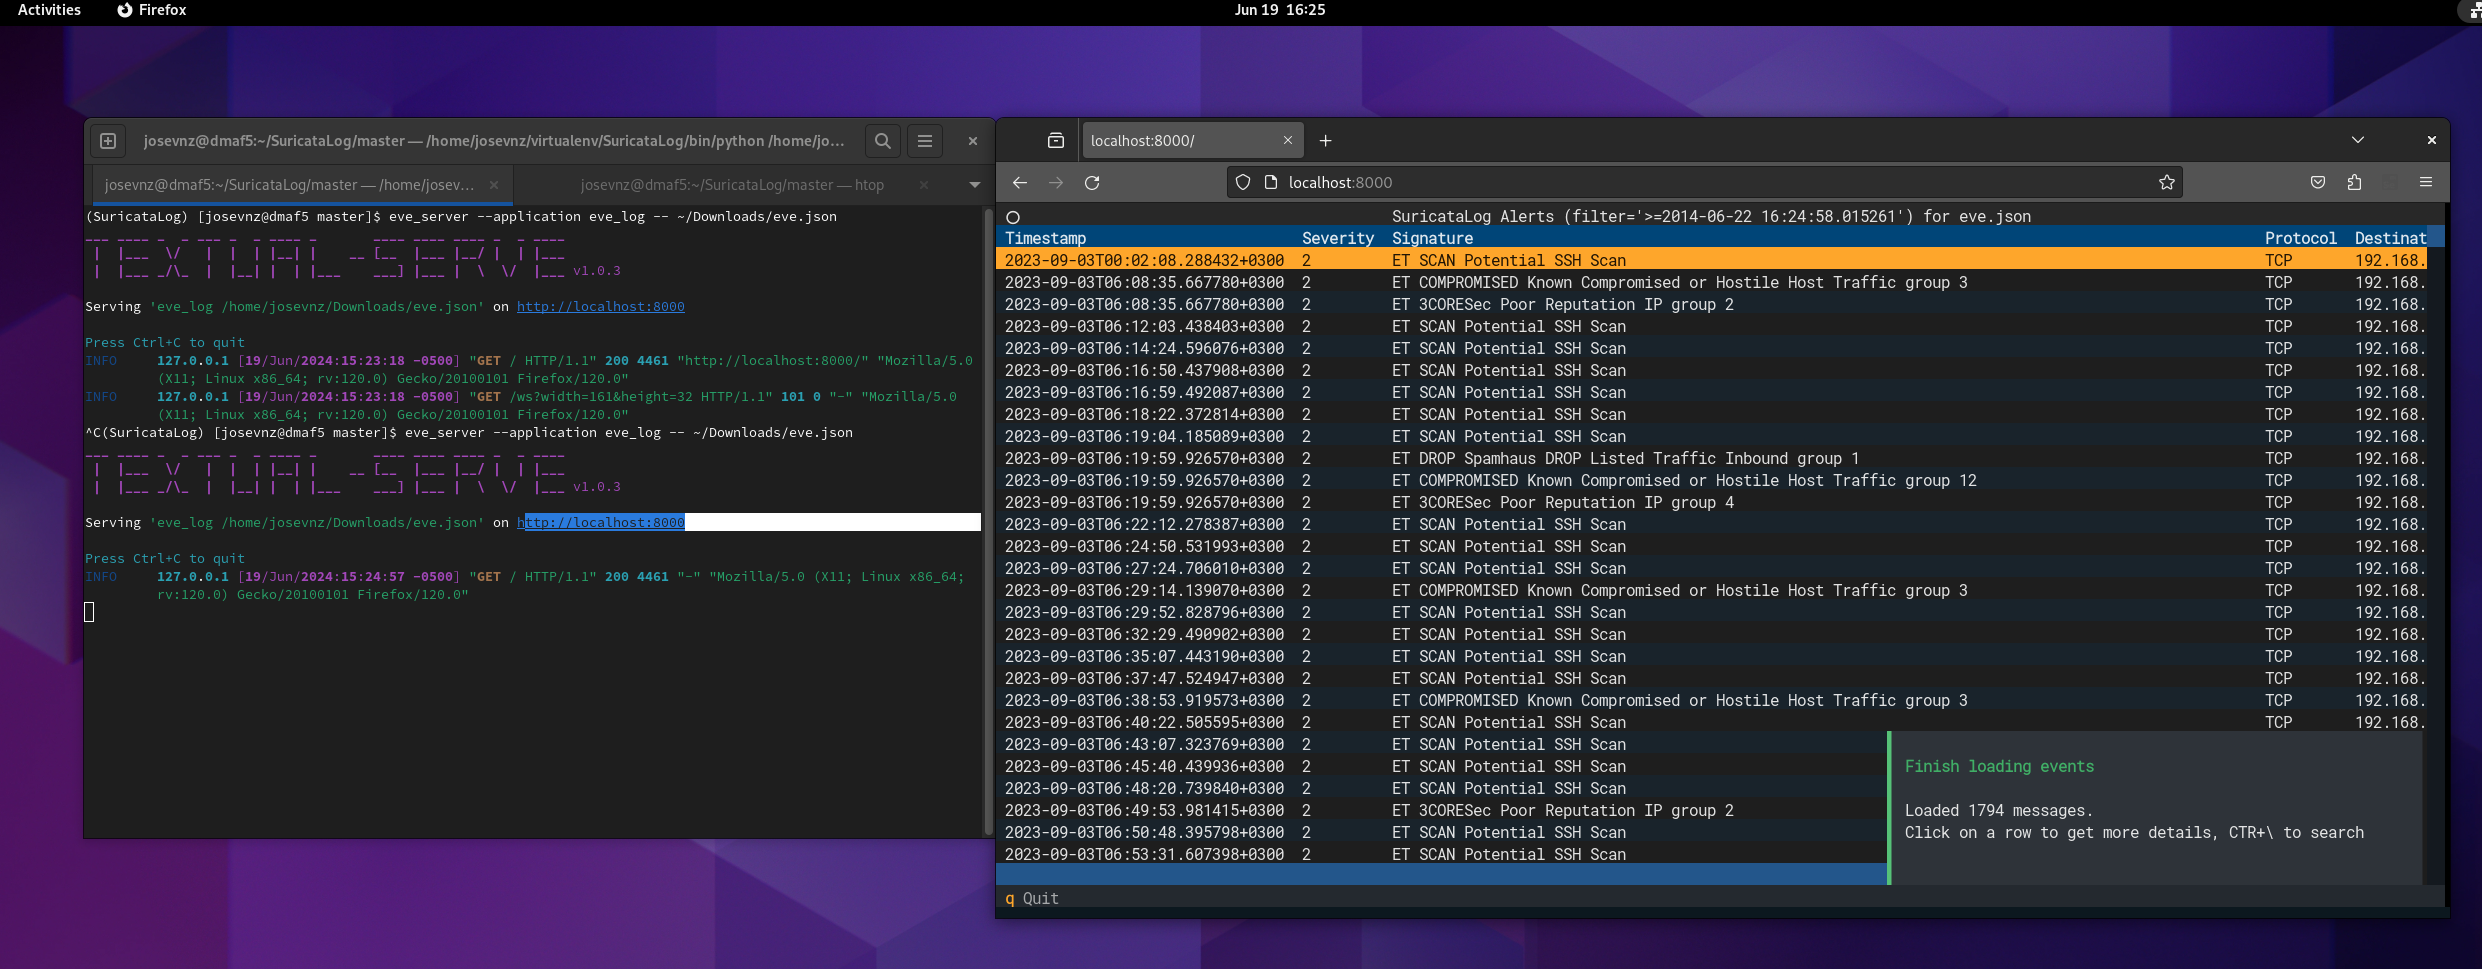
Parse, filter, and visualize Suricata eve.json logs with CLI tools for alerts, flows, DNS, and payloads. Includes a tutorial for learning Suricata…

Monitors Asterisk authentication logs and automatically bans IPs with repeated failed login attempts using iptables, with configurable thresholds and…