
artillery
 trustedsec/artillery
Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.
anomaly-detectiondefensive-toolshardware-iot-security+5
339
trustedsec/artilleryOpen-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.
 g0dse11/detecttrace
Open-source detection engineering tool that traces security detections end to end and identifies the first failing stage.
 haidang-infosec/phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…
 mr-r3b00t/cve-2021-44228
PowerShell-based backdoor detection tool for VMware Horizon connection servers, targeting CVE-2021-44228. Includes canary with optional submission…
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
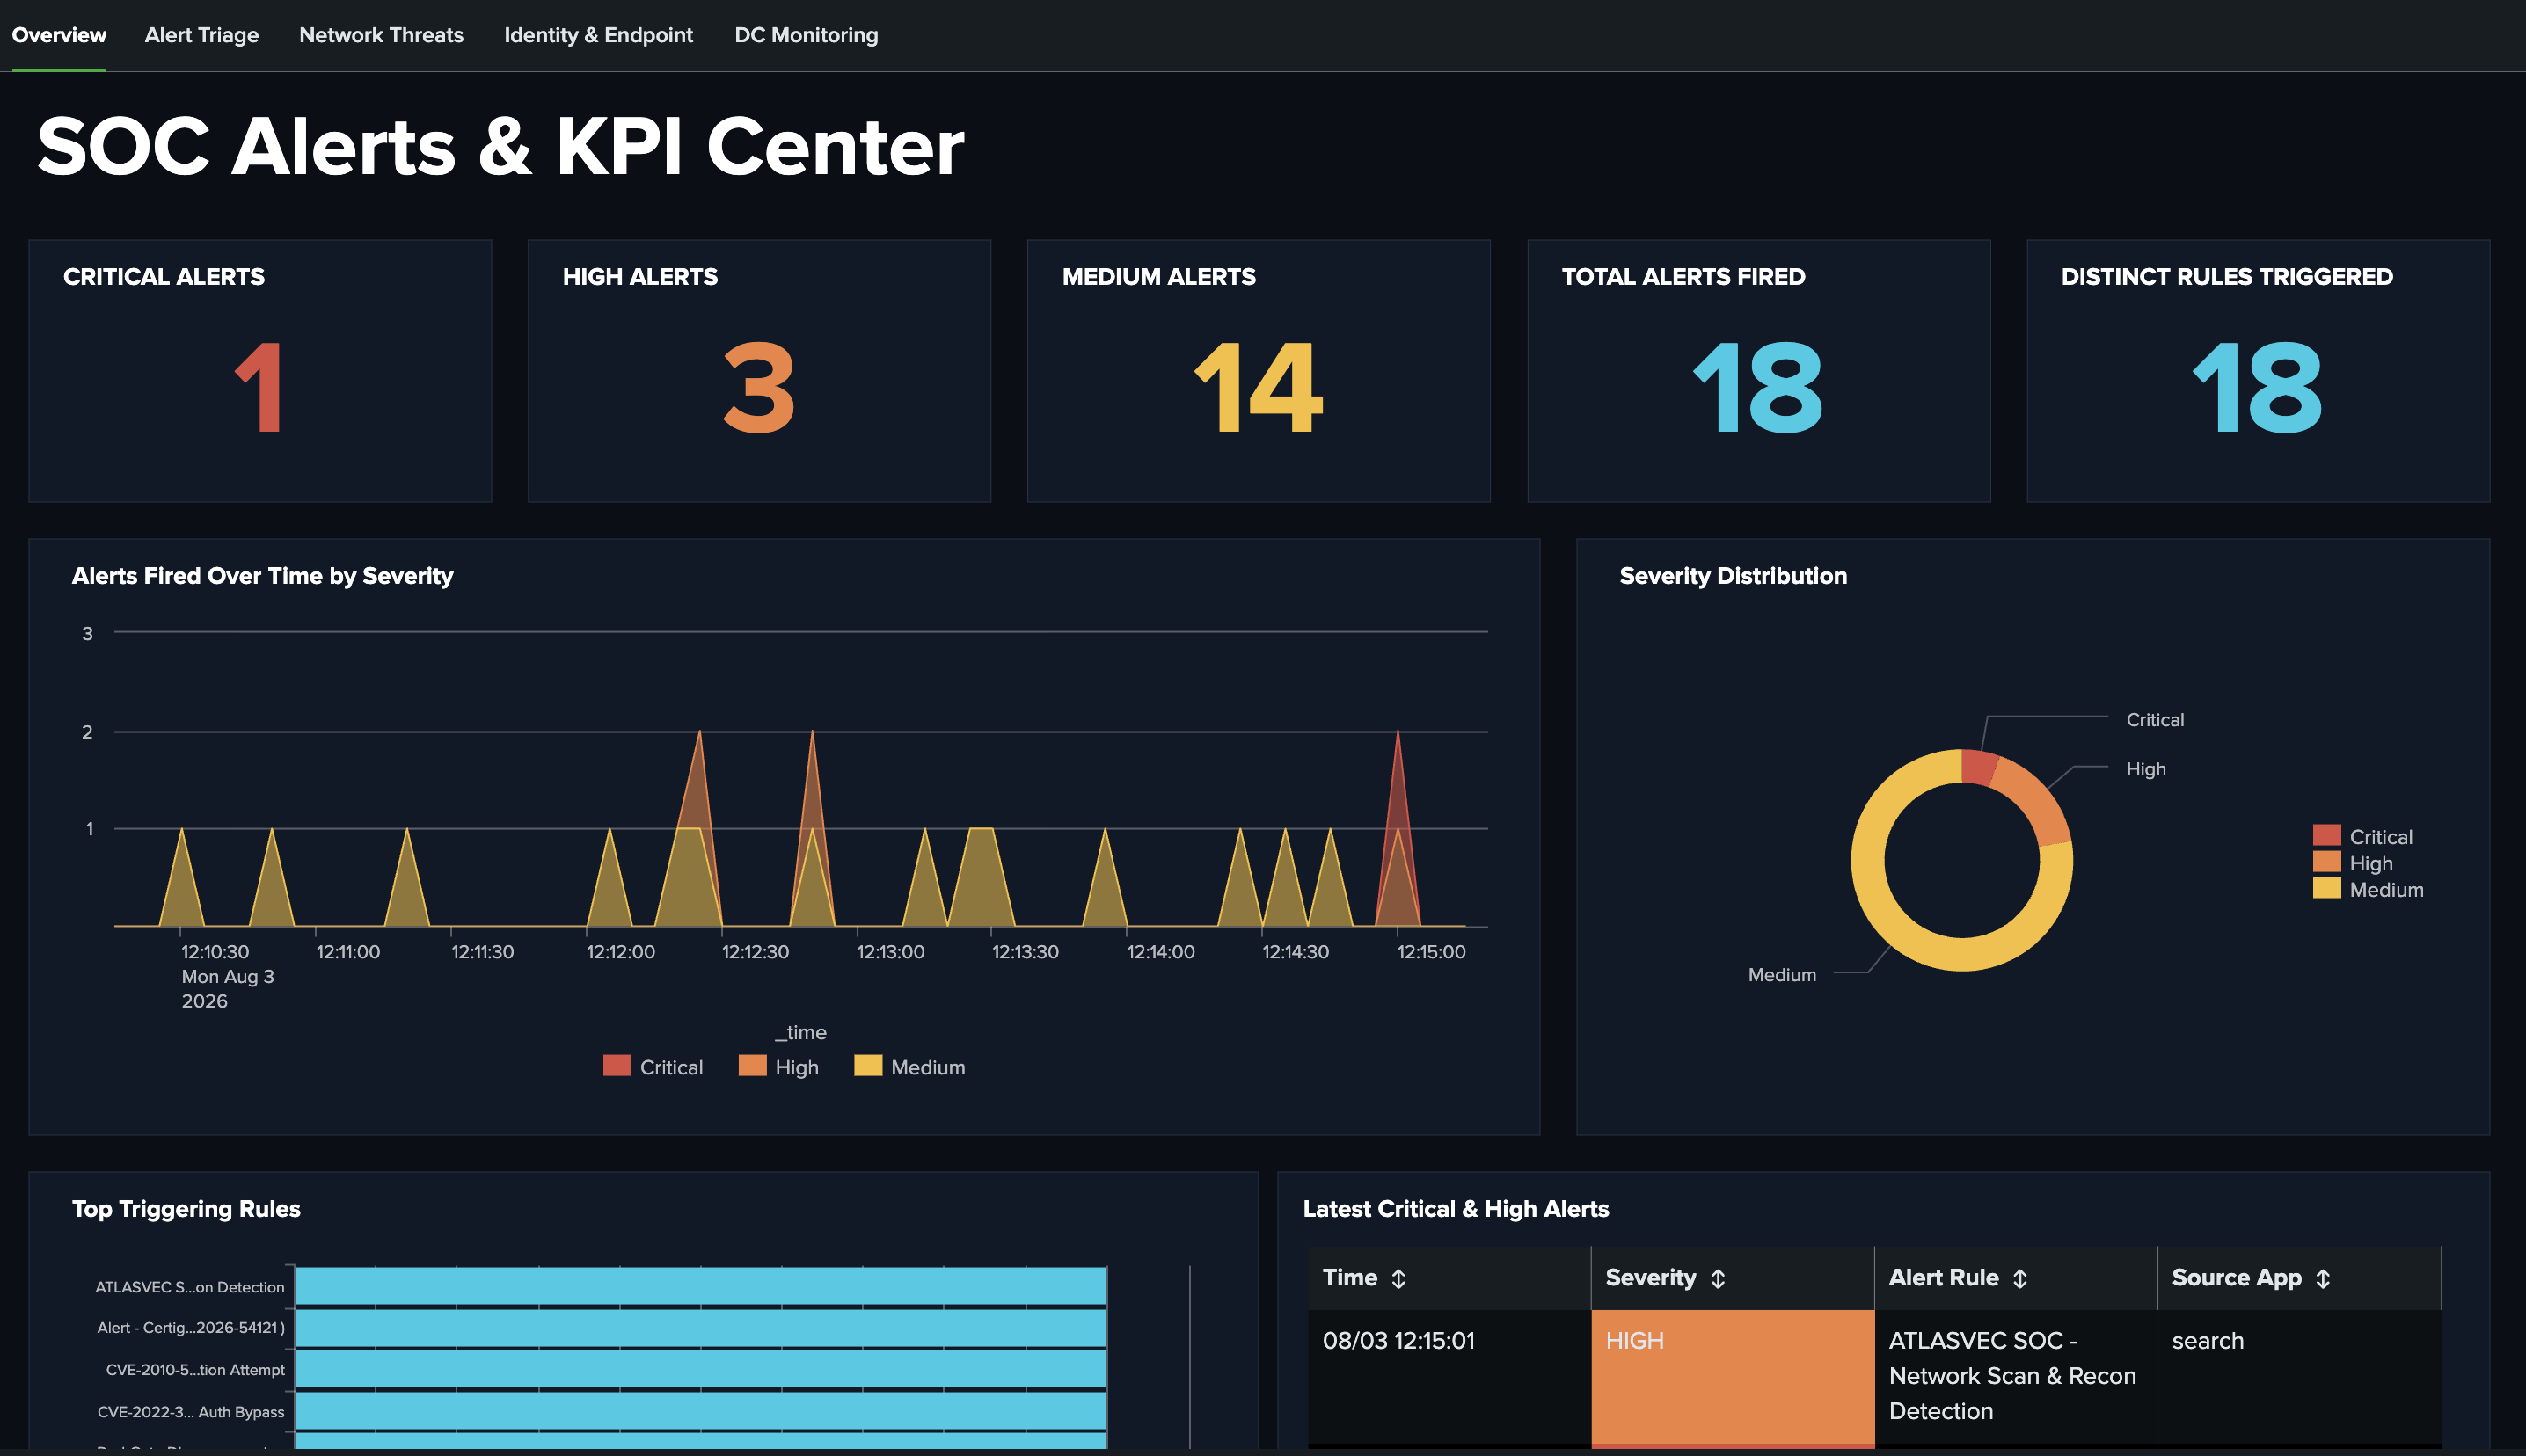 atlasvector/certighost-cve-2026-54121
Splunk detection writeup for CVE-2026-54121 (CertiGhost): AD CS certificate chase abuse leading to full domain compromise. Lab-validated detection,…
 immersive-labs-sec/bruteratel-detectiontools
A collection of Tools and Rules for decoding Brute Ratel C4 badgers
 theflink/hunt-weird-imageloads
Small tool to play with IOCs caused by Imageload events
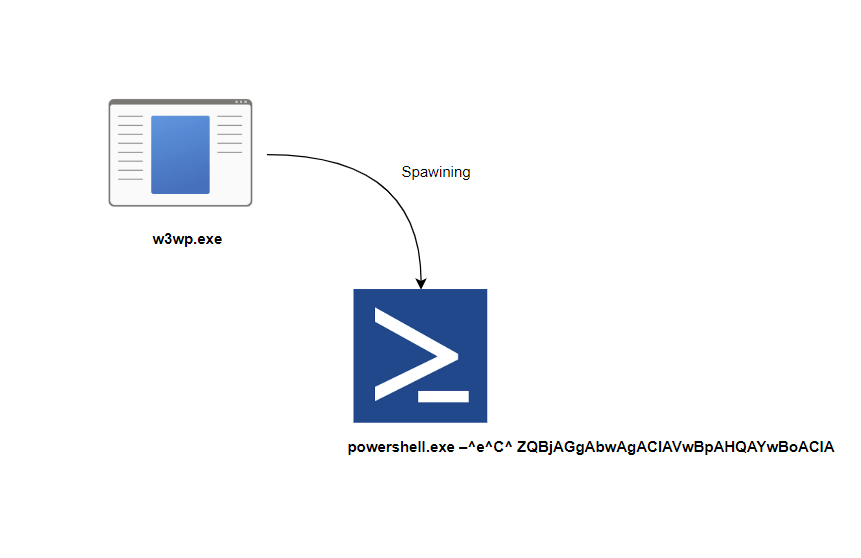 alwashali/detection-validation
Detection rule validation
 sigmahq/pysigma
Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)
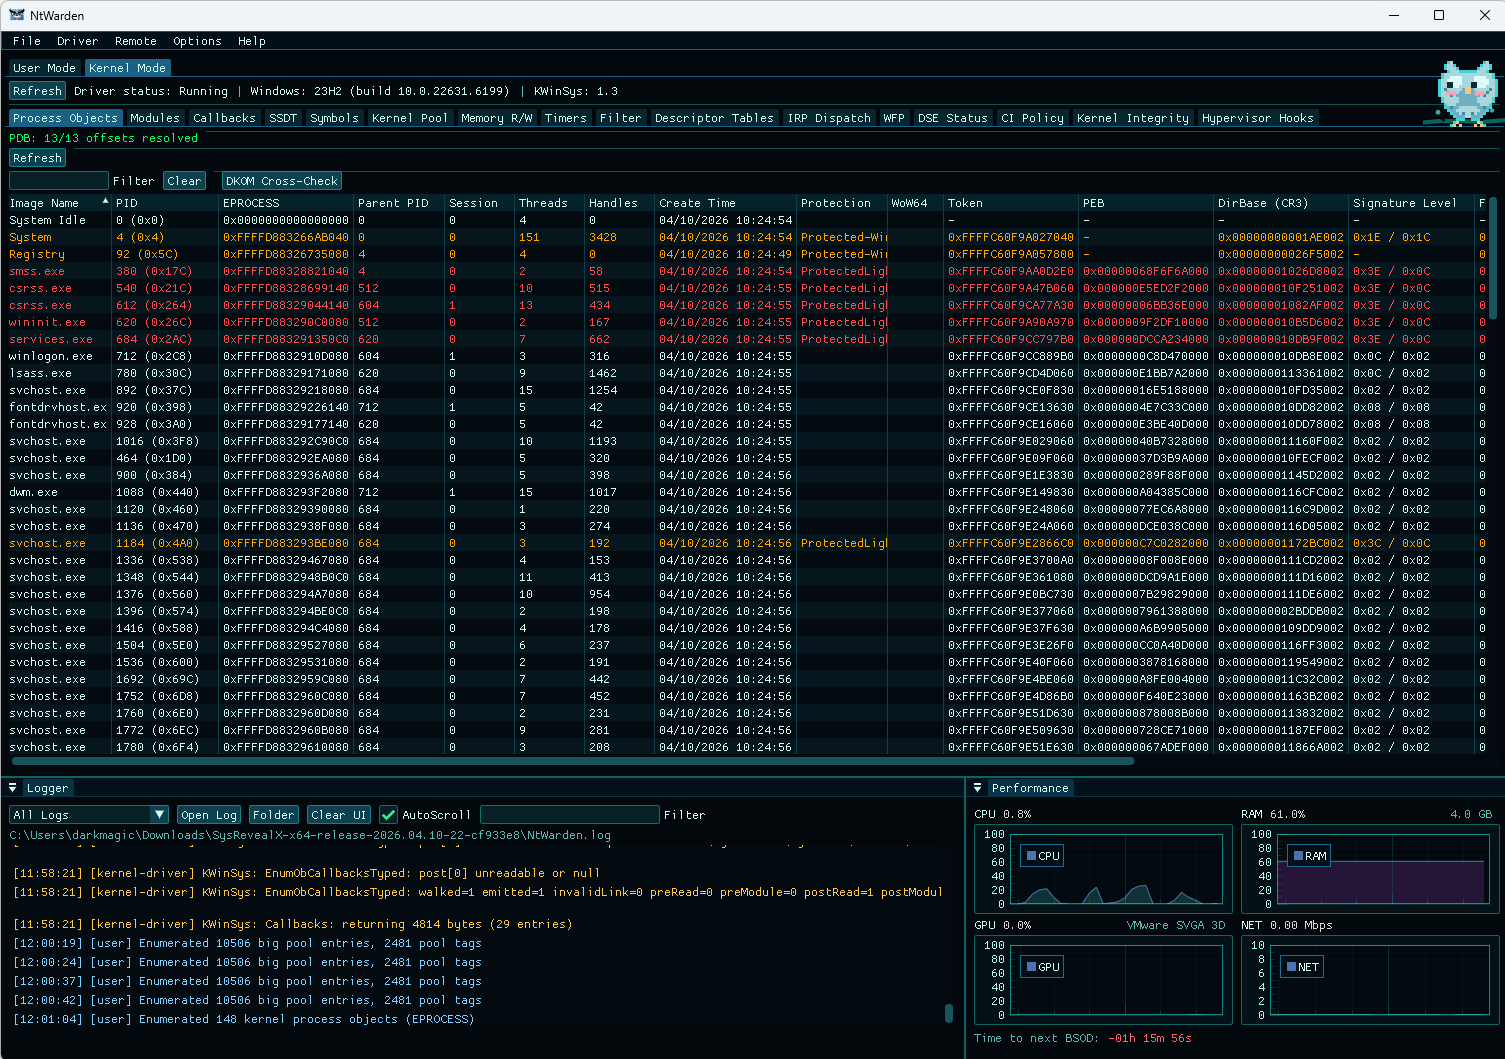 mrt4ntr4/ntwarden
Windows Analysis and Research Toolkit
 northpolesec/santa
A binary and file access authorization system for macOS.
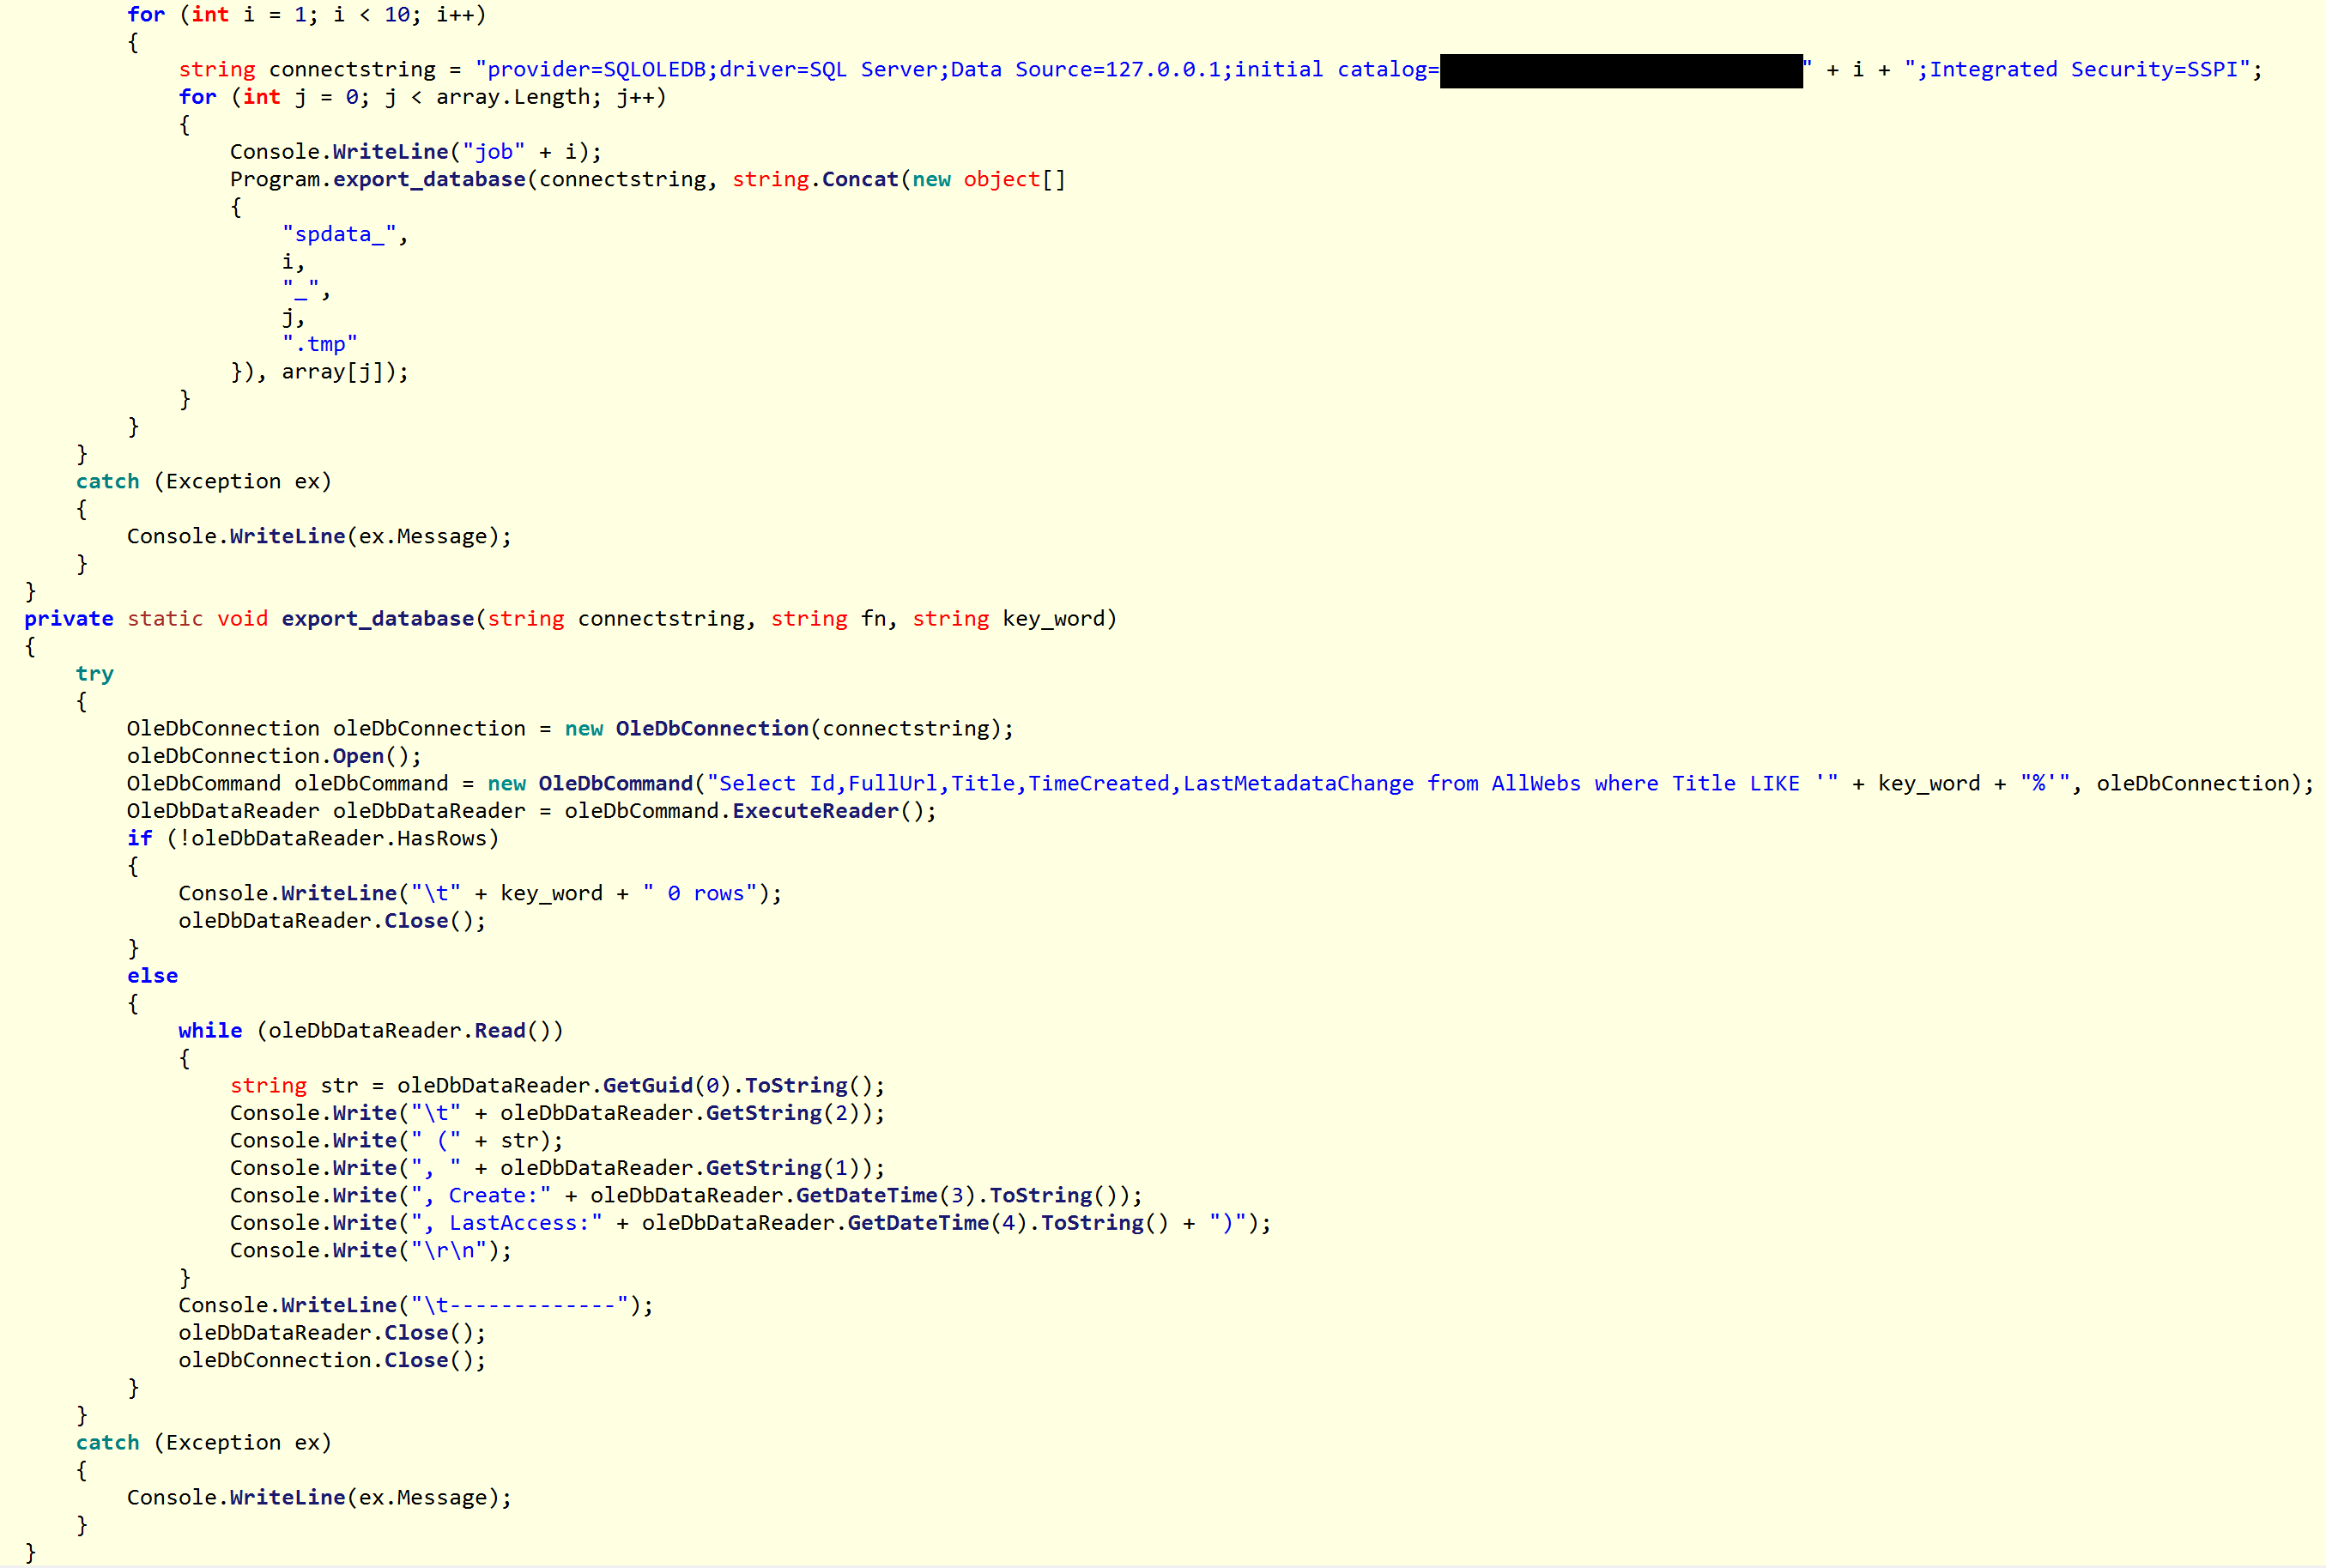 nccgroup/royal_apt
Royal APT - APT15 - Related Information from NCC Group Cyber Defense Operations Research
 synacktiv/nmap-farewell
Automated Network Security with Rust: Detecting and Blocking Port Scanners
 corelight/go-zeek-broker-ws
A Go library for using zeek broker's websocket API
 corelight/pingback
A Zeek package to detect the Pingback malware ICMP tunnel command and control (C2) network traffic.
 corelight/raspi-corelight
Corelight@Home script
 jenderal92/ddos-traffic-monitor
A real-time traffic monitoring tool that detects and displays network traffic volume per IP address to identify potential DDoS attacks.