
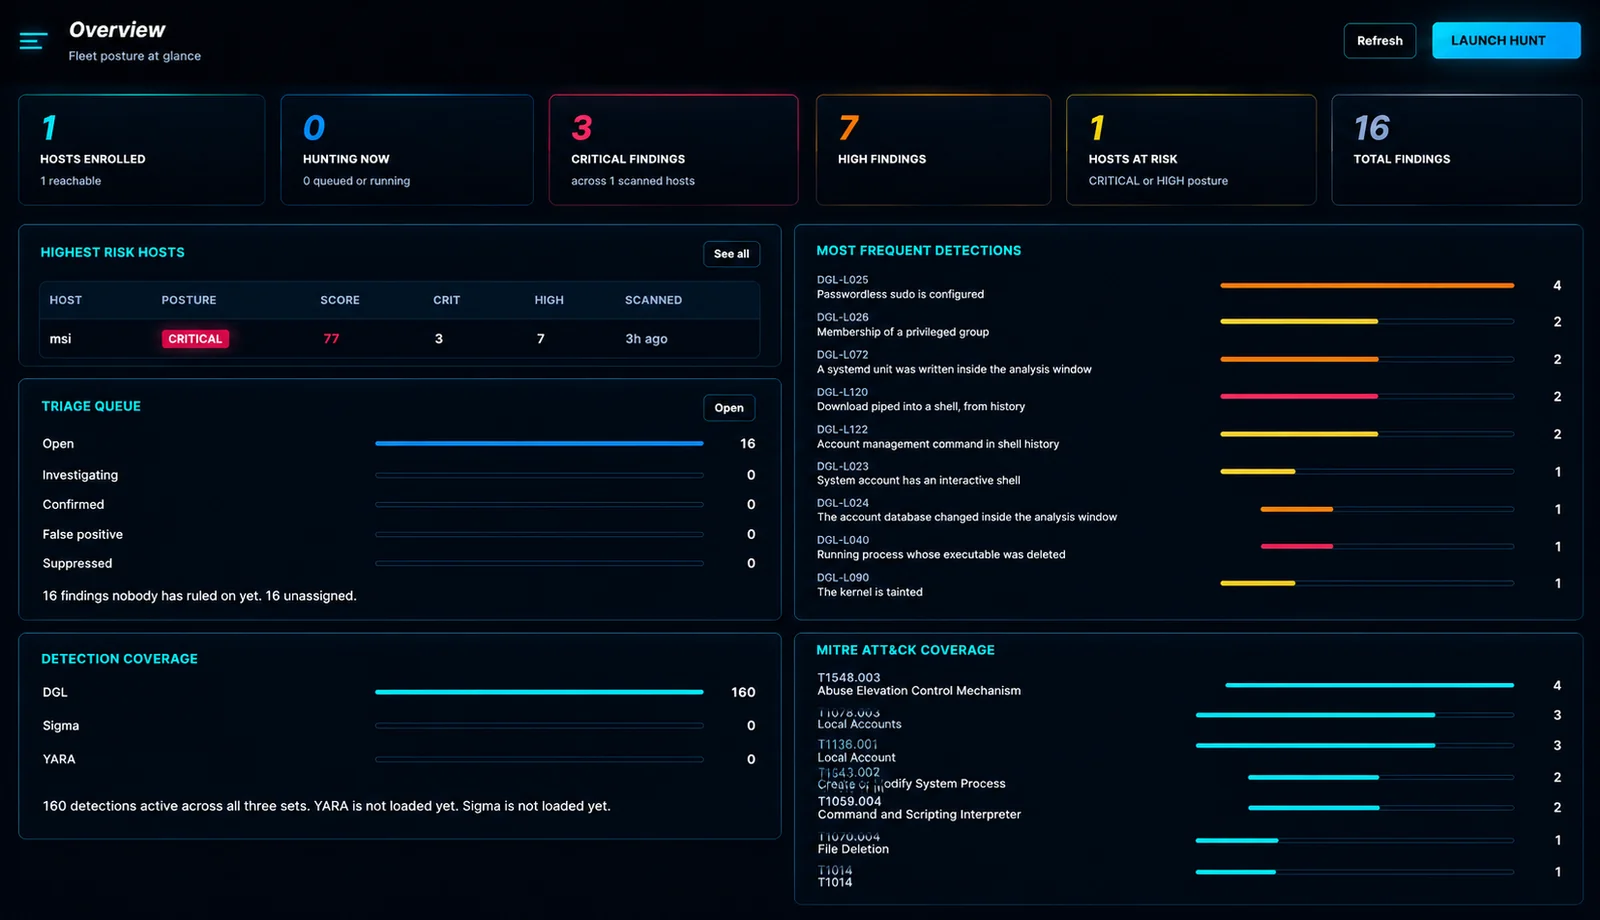
douglas-042-HQ
 douglas-042/douglas-042-hq
Central console for Douglas-042 HEADQUARTERS collectors. Sweeps a fleet, correlates results across hosts, and manages IOC feeds and SIEM delivery…
defensive-toolsforensicsincident-response+5
douglas-042/douglas-042-hqCentral console for Douglas-042 HEADQUARTERS collectors. Sweeps a fleet, correlates results across hosts, and manages IOC feeds and SIEM delivery…
 withsecurelabs/lazarus-sigma-rules
Sigma rules for detecting Lazarus Group TTPs, covering malicious document execution, PowerShell abuse, scheduled tasks, and credential access,…
 kevin-robertson/conveigh
Conveigh is a Windows PowerShell LLMNR/NBNS spoofer detection tool
 paolokappa/sharepointsecuritymonitor
A comprehensive PowerShell-based SharePoint security monitoring solution with CVE-2025-53770 protection, advanced DLL analysis, threat detection, and…
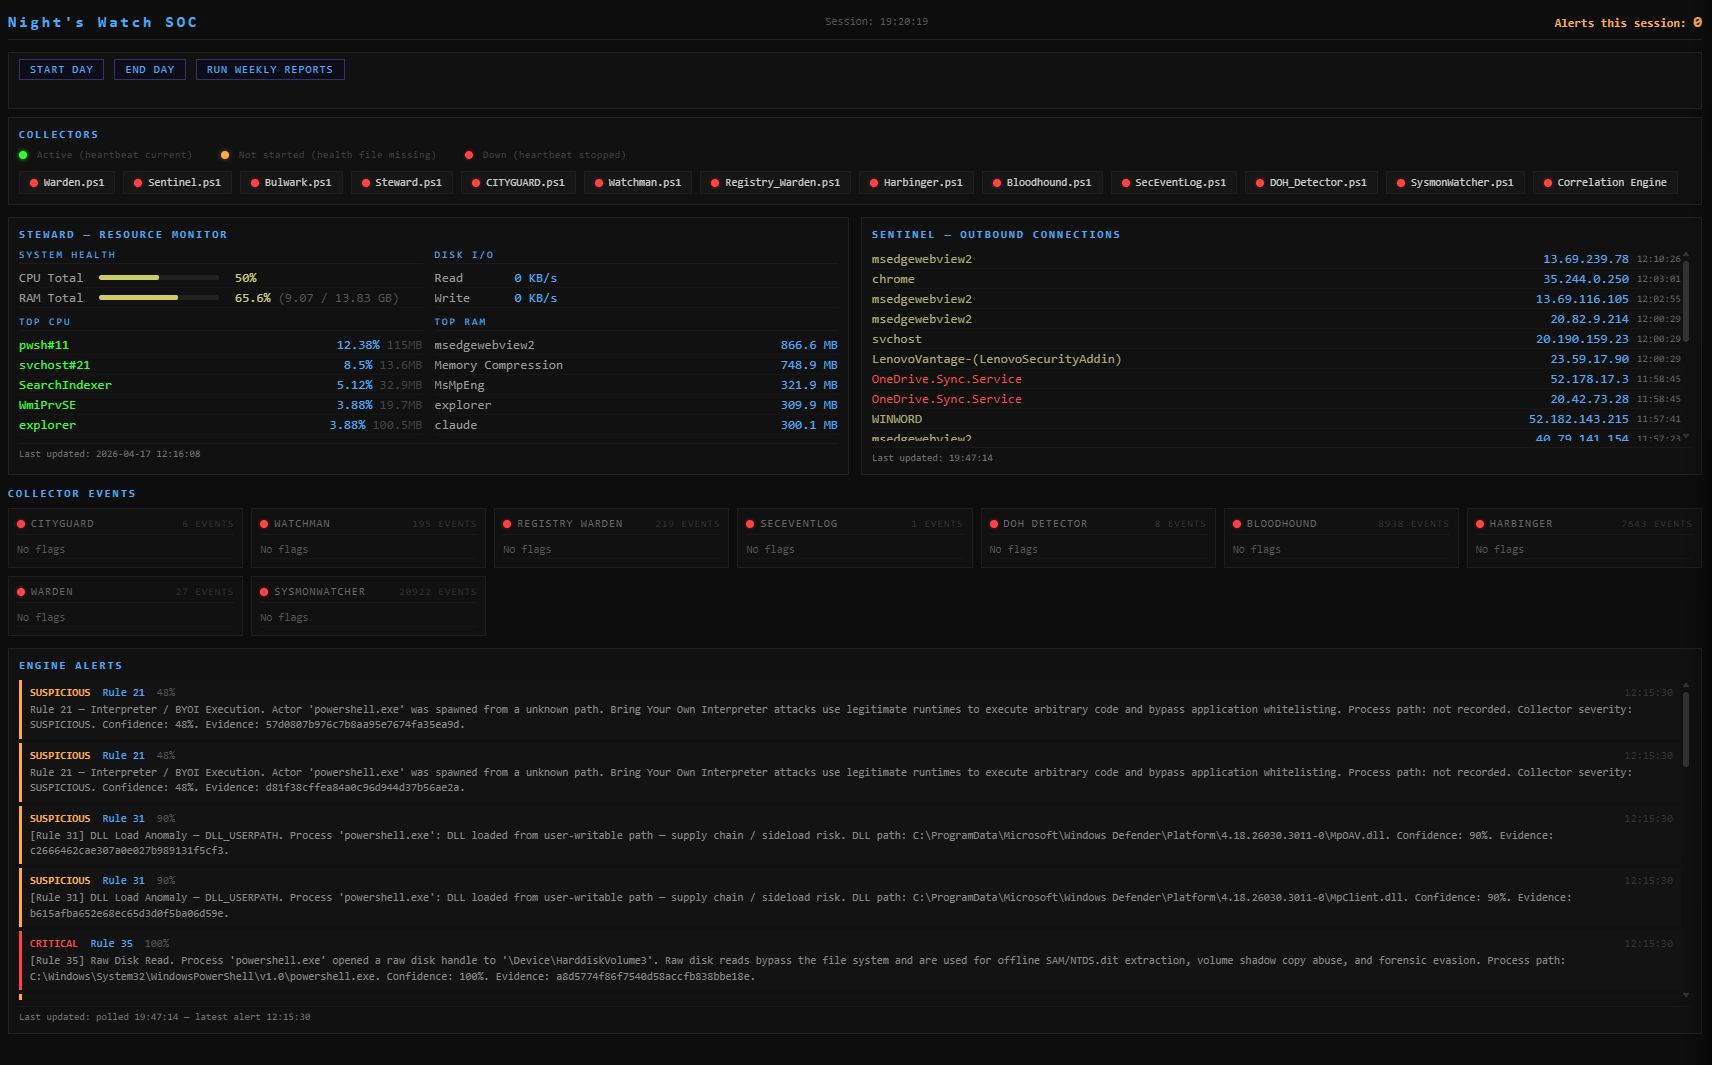 nate-ryan-7690/home_soc_suite
A personal Windows SOC suite built in PowerShell — monitors network connections, resource usage, scheduled tasks and power events with severity…
 arisharazakhan-cpu/dod-blue-team-network-lab
High fidelity defensive security lab simulating a DoD aligned enterprise network with Active Directory, VLAN segmentation, STIG based hardening,…
 clong/detectionlab
Automate the creation of a lab environment complete with security tooling and logging best practices
 sans-blue-team/deepbluecli
PowerShell-based threat hunting tool that analyzes Windows Event Logs to detect malicious activity including credential attacks, obfuscated commands,…
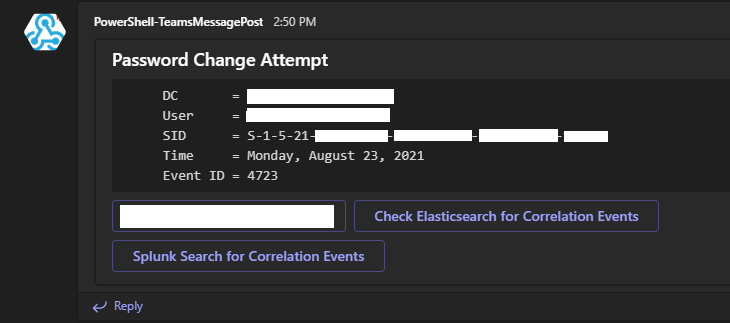 osbornepro/btps-secpack
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…
 0x0v1/audix
Audix is a PowerShell tool to quickly configure the Windows Event Audit Policies for security monitoring
 blackhillsinfosec/eventlogging
Automation scripts to deploy Windows Event Forwarding, Sysmon, and custom audit policies in an Active Directory environment.