uefi_bootkit_softlanding

First public analysis of SoftLanding UEFI bootkit: Ring -2 implant, CVE-2025-7029, 240+ Gigabyte boards, GPU AI evasion, dual C2. YARA + Sigma +…

First public analysis of SoftLanding UEFI bootkit: Ring -2 implant, CVE-2025-7029, 240+ Gigabyte boards, GPU AI evasion, dual C2. YARA + Sigma +…

A Zeek package to detect the Pingback malware ICMP tunnel command and control (C2) network traffic.


Repo containing lua scripts and PCAP to find CVE-2020-0601 exploit attempts via network traffic

eBPF-based Linux rootkit detector using multi-channel cross-view analysis (sched_switch, NMI, /proc) to detect DKOM, tracepoint tampering, and…

Pulled Pork for Snort and Suricata rule management (from Google code)

psad: Intrusion Detection and Log Analysis with iptables

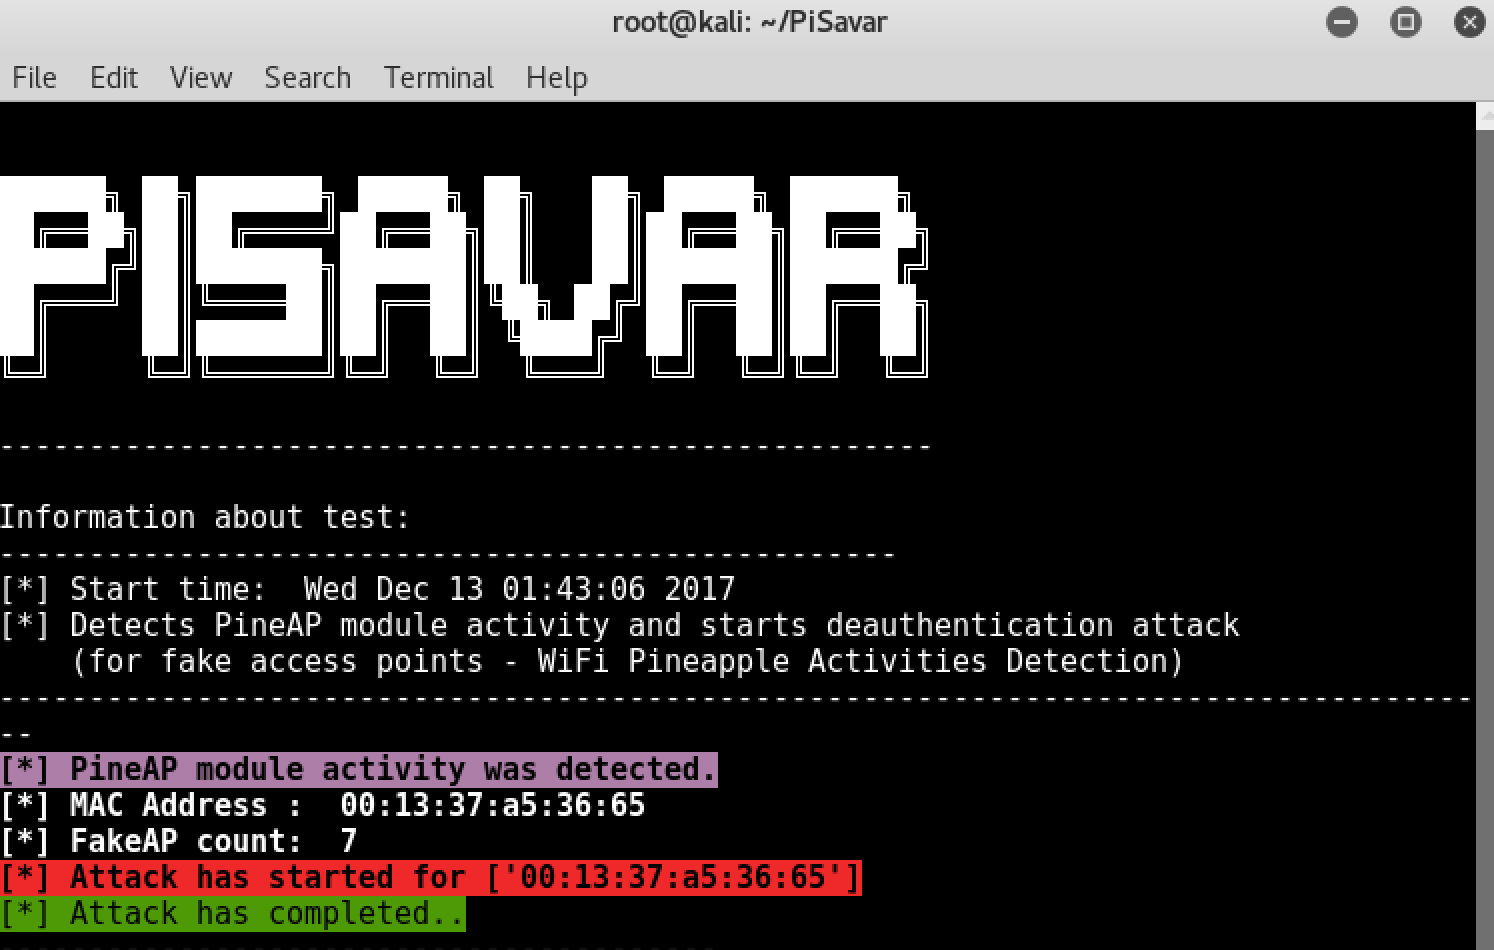
📡 🍍Detects activities of PineAP module and starts deauthentication attack (for fake access points - WiFi Pineapple Activities Detection)

A host based IDS written in C# Targetted at Metasploit

A python2 script for sweeping a network to find windows systems compromised with the DOUBLEPULSAR implant.

Deep Learning models for network traffic classification

eBPF-based runtime detector for container breakout vulnerabilities in runc and Docker, monitoring syscalls and Docker daemon calls to detect…

Security Onion 16.04 - Linux distro for threat hunting, enterprise security monitoring, and log management