ddos-reduction-system

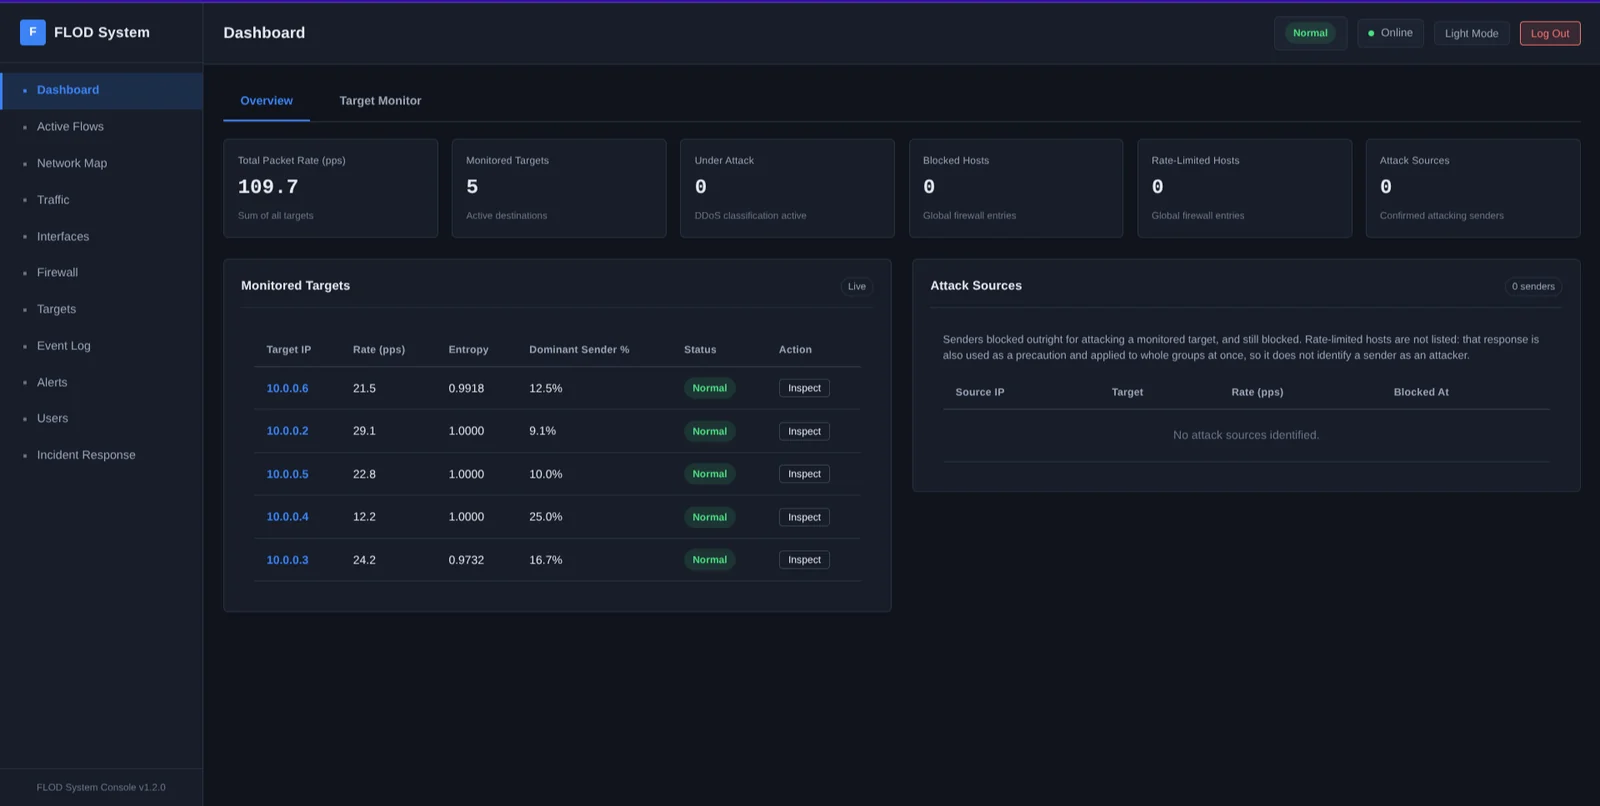
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…

Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…

Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.

StyleSmuggler (CVE-2026-75650) IOC toolkit for Magento Open Source and Adobe Commerce. Detect compromised stores, Rust implants, PHP web shells,…

CVE proof-of-concept labs, exploit scripts, and detection/prevention rules (Nginx, Apache, Snort, YARA) for high-severity CVEs. Authorized security…

Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…

An open-source, self-hosted AI-powered SIEM, EDR and SOAR platform for modern security operations.

Research and detection toolkit for Linux kernel LPE CVE-2026-31431, including exploit analysis, YARA rules, auditd/Falco detection, patching guide,…

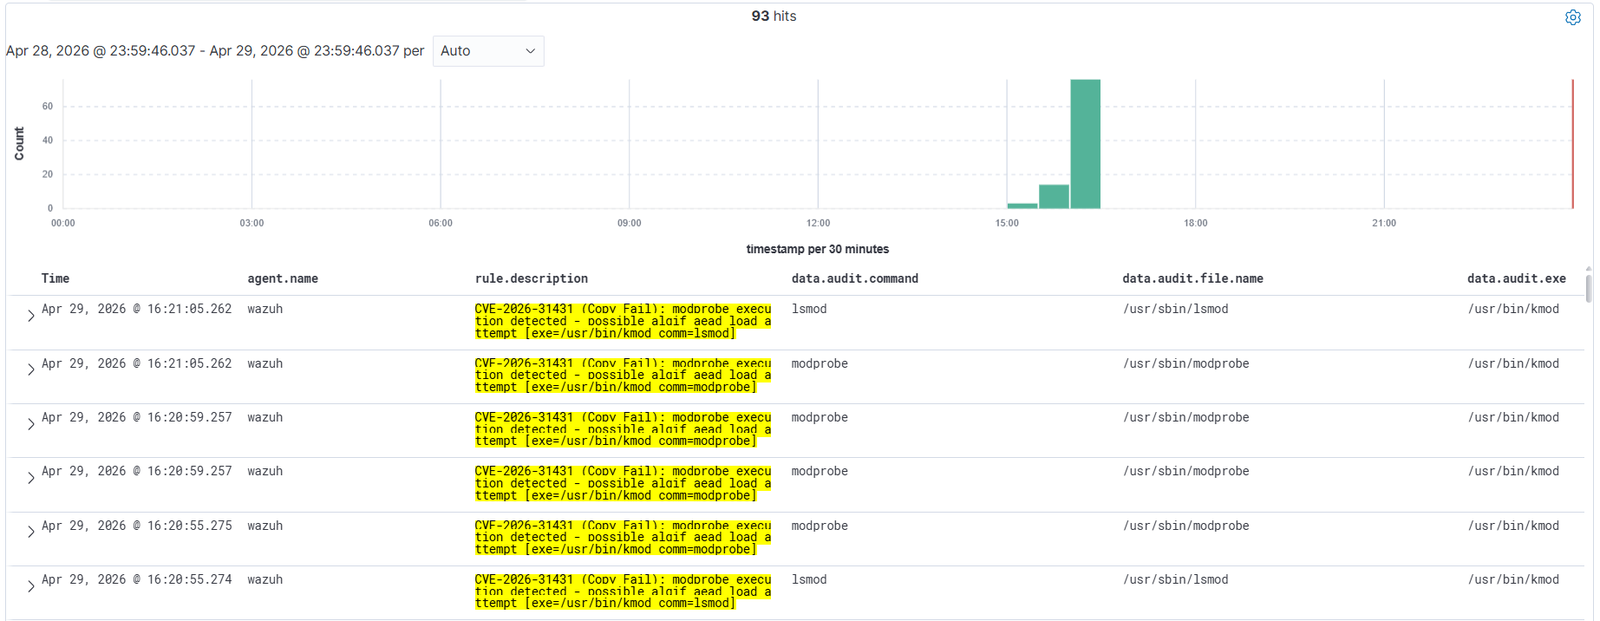
Wazuh 4.14.4 detection rules for CVE-2026-31431 (Copy Fail) - Linux Local Privilege Escalation via authencesn page cache write

Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…

Low-interaction honeypot that emulates vulnerable network services to capture malware, shellcode, and exploit attempts, with IPv6 and TLS support.

Develop, validate, and publish SIEM detection rules for Elastic Security, with Python CLI tooling, KQL parsing, Kibana integration, and packaged…

Detect Tactics, Techniques & Combat Threats

Purpleteam scripts simulation & Detection - trigger events for SOC detections

Python library to parse and convert Sigma rules into queries (and whatever else you could imagine)

DECeption with Evaluative Integrated Validation Engine (DECEIVE): Let an LLM do all the hard honeypot work!

Network anomaly detector that monitors raw packets to identify port scanning activity in real time, with flexible sniffing duration controls and live…

Runs custom filters on Elasticsearch and alerts on matches

Corelight-Ansible-Roles are a collection of Ansible Roles and playbooks that install, configure, run and manage a variety of Corelight, Suricata and…