
OshoosiClaw
 oyesanyf/oshoosiclaw
Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
ai-securityanomaly-detectioncommand-and-control+8
oyesanyf/oshoosiclawAutonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…
 cognis-digital/c2detect
C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel
 bert-janp/open-source-threat-intel-feeds
This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…
 shahidmallaofficial/cpanel-cve-2026-41940-fix
One-shot detection and remediation for cPanel/WHM servers compromised via CVE-2026-41940, including IOC checks, malware cleanup, C2 blocking, and…
 immersive-labs-sec/bruteratel-detectiontools
A collection of Tools and Rules for decoding Brute Ratel C4 badgers
 criticalpathsecurity/zeek-intelligence-feeds
Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…
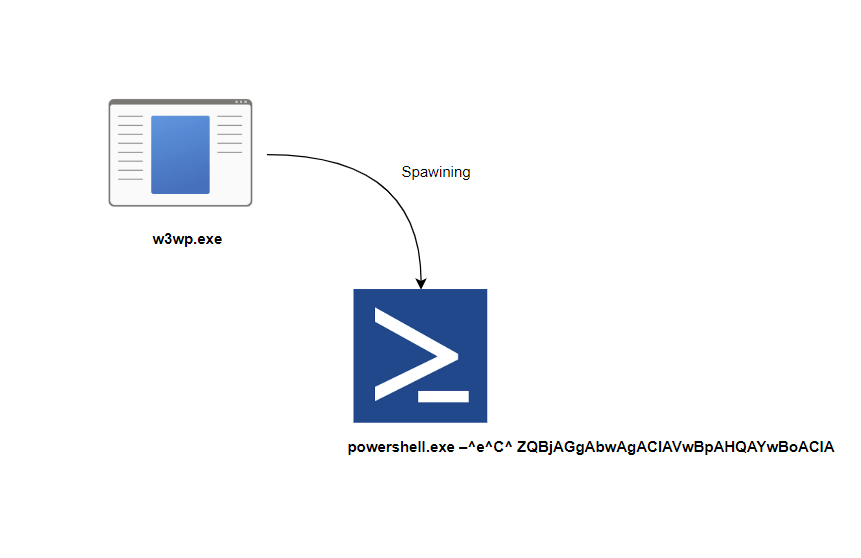 alwashali/detection-validation
Detection rule validation
 embee-research/yara-detection-rules
Yara Rules for Modern Malware
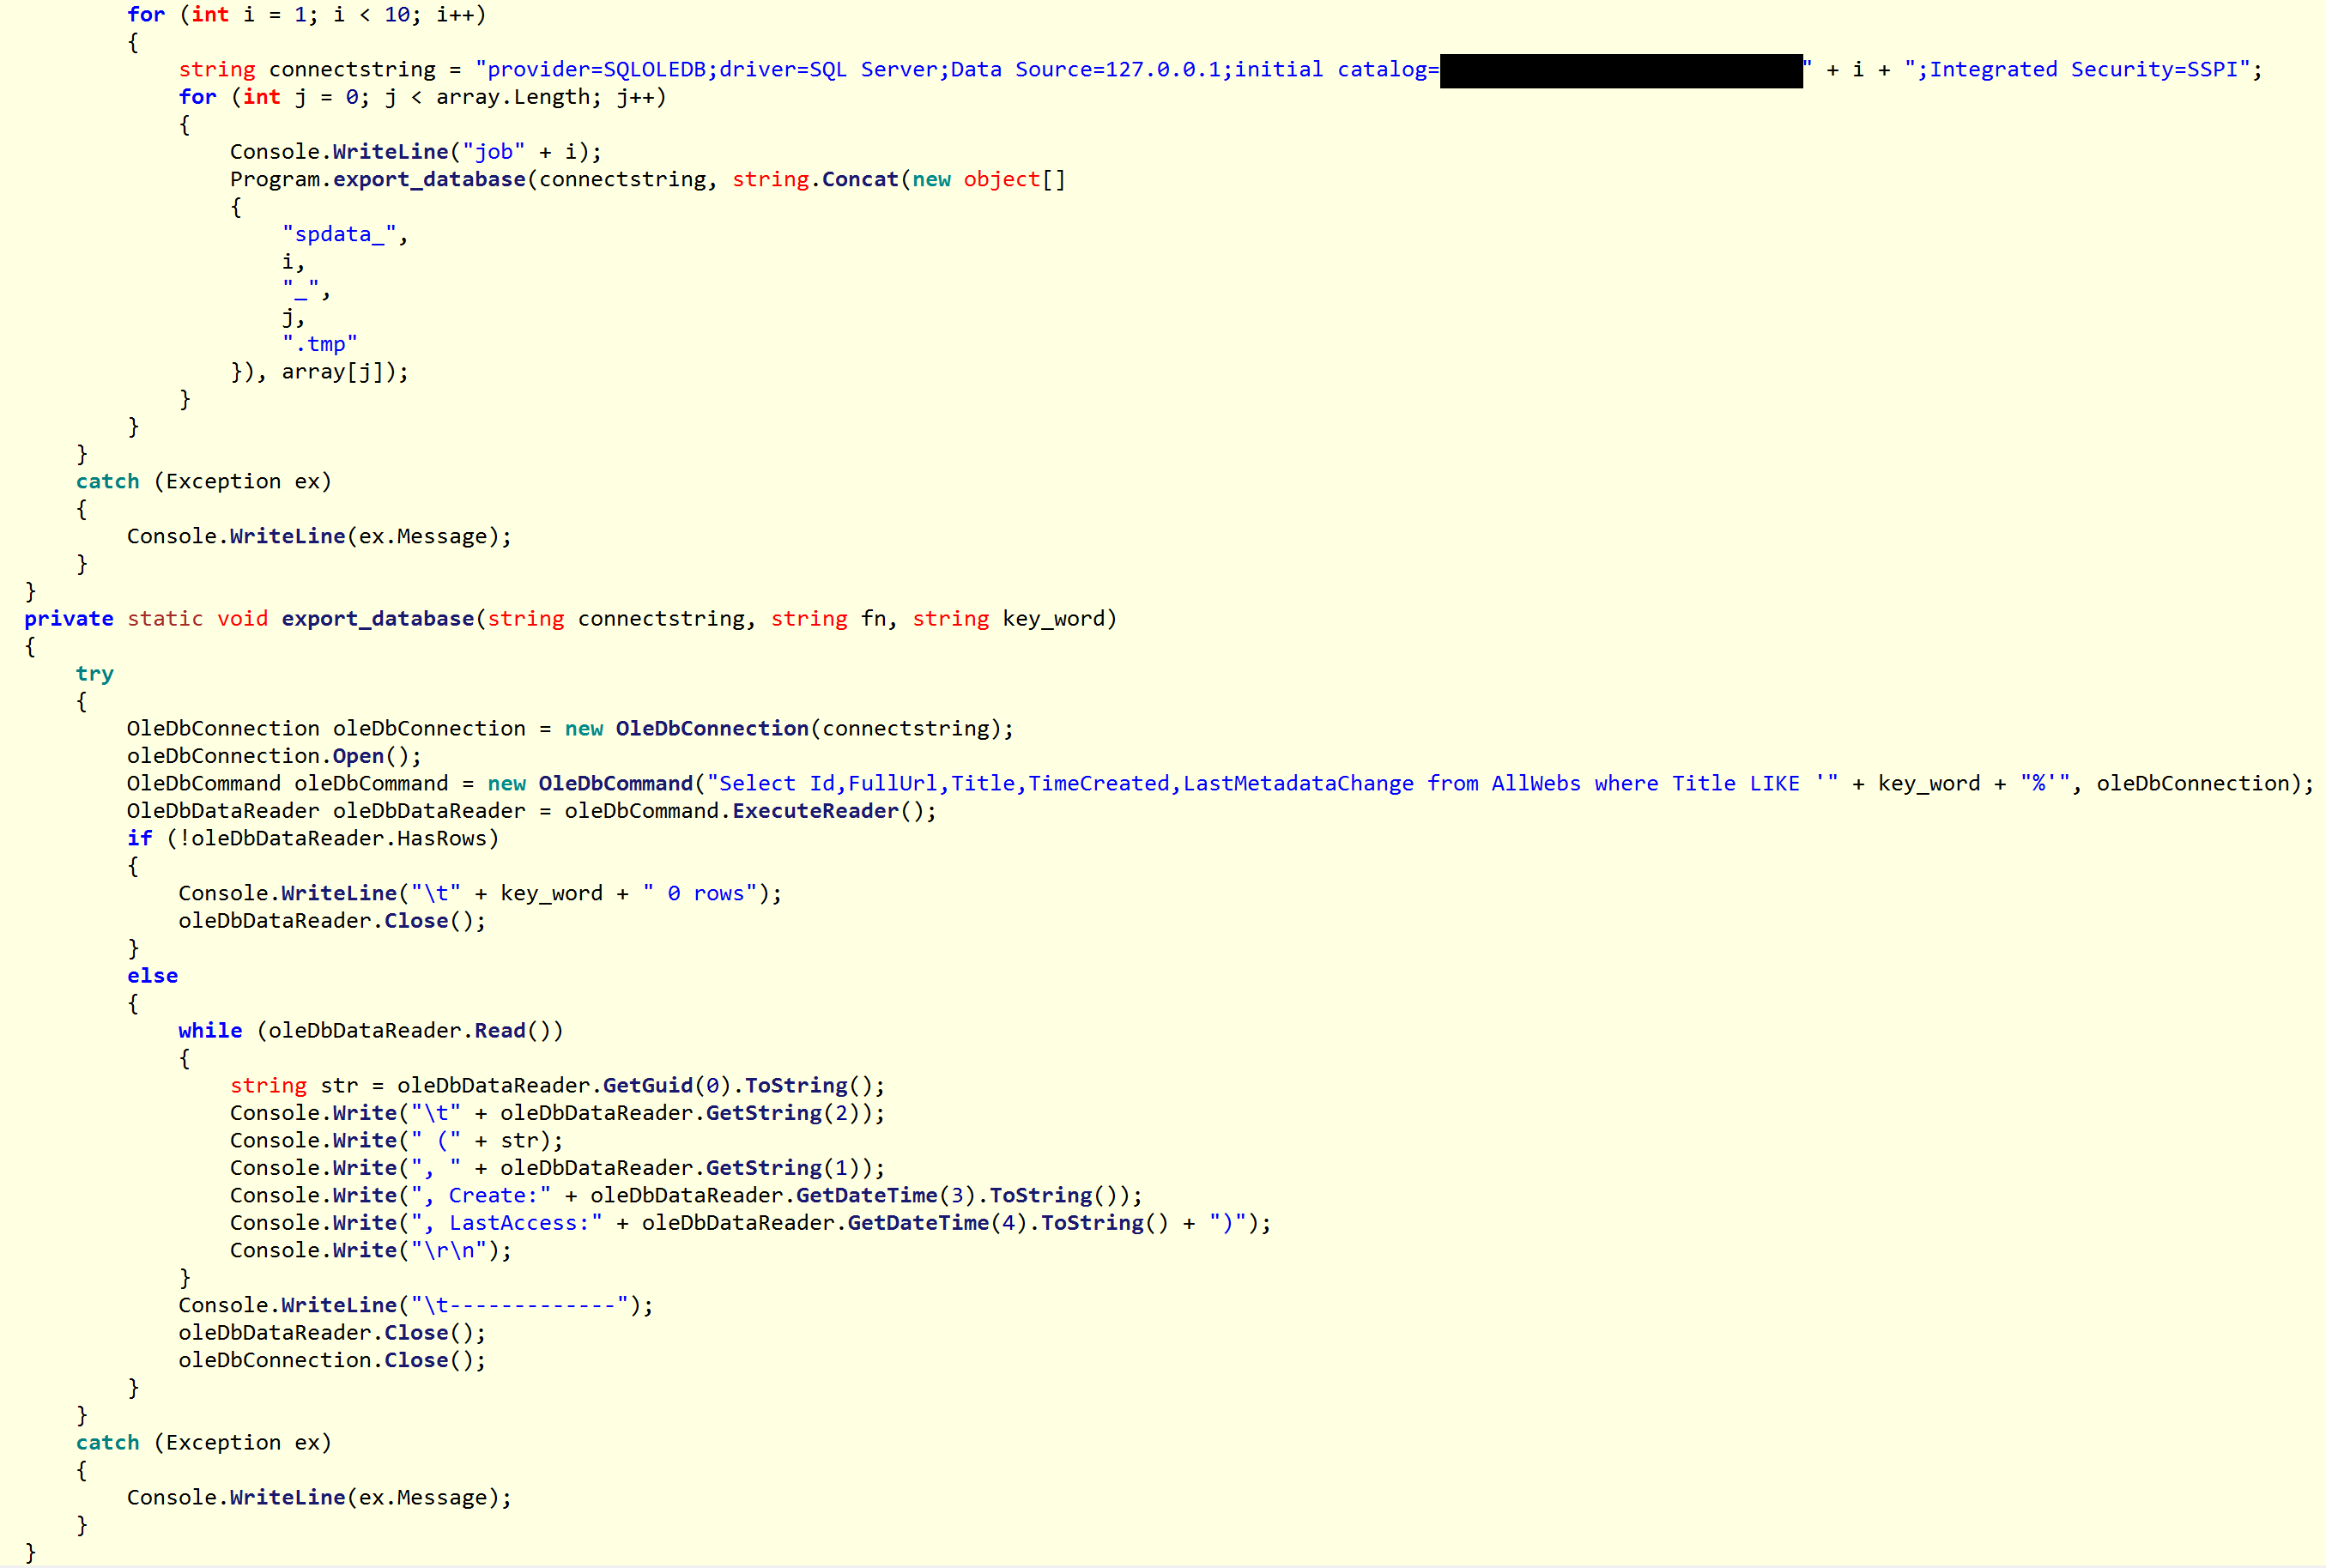 nccgroup/royal_apt
Royal APT - APT15 - Related Information from NCC Group Cyber Defense Operations Research
 corelight/c2-detection-manjusaka
Detection of Manjusaka C2 framework
 corelight/pingback
A Zeek package to detect the Pingback malware ICMP tunnel command and control (C2) network traffic.
 corelight/redxor
Detection of Linux Malware C2 RedXOR - demonstration
 corelight/zeek-agenttesla-detector
A Zeek based Agent Tesla malware C2 detector.
 corelight/zeek-asyncrat-detector
A Zeek based AsyncRAT malware detector.
 corelight/zeek-caldera-detector
A Zeek based Mitre Caldera detector.
 corelight/zeek-netsupport-detector
A Zeek based NetSupport detector. NetSupport is often abused by attackers in malware.
 corelight/zeek-quasarrat-detector
Zeek detector for QuasarRat
 corelight/zeek-spicy-facefish
A Zeek protocol analyzer for the Facefish rootkit, based on Spicy.