

GPEWebDefender
 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
defensive-toolsincident-responseinformation-gathering+8
5
gopasteverything/gpewebdefenderLightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 alphasoc/flightsim
A utility to safely generate malicious network traffic patterns and evaluate controls.
 sonitbahl/sshintel
Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
 hpfeeds/hpfeeds
Honeynet Project generic authenticated datafeed protocol
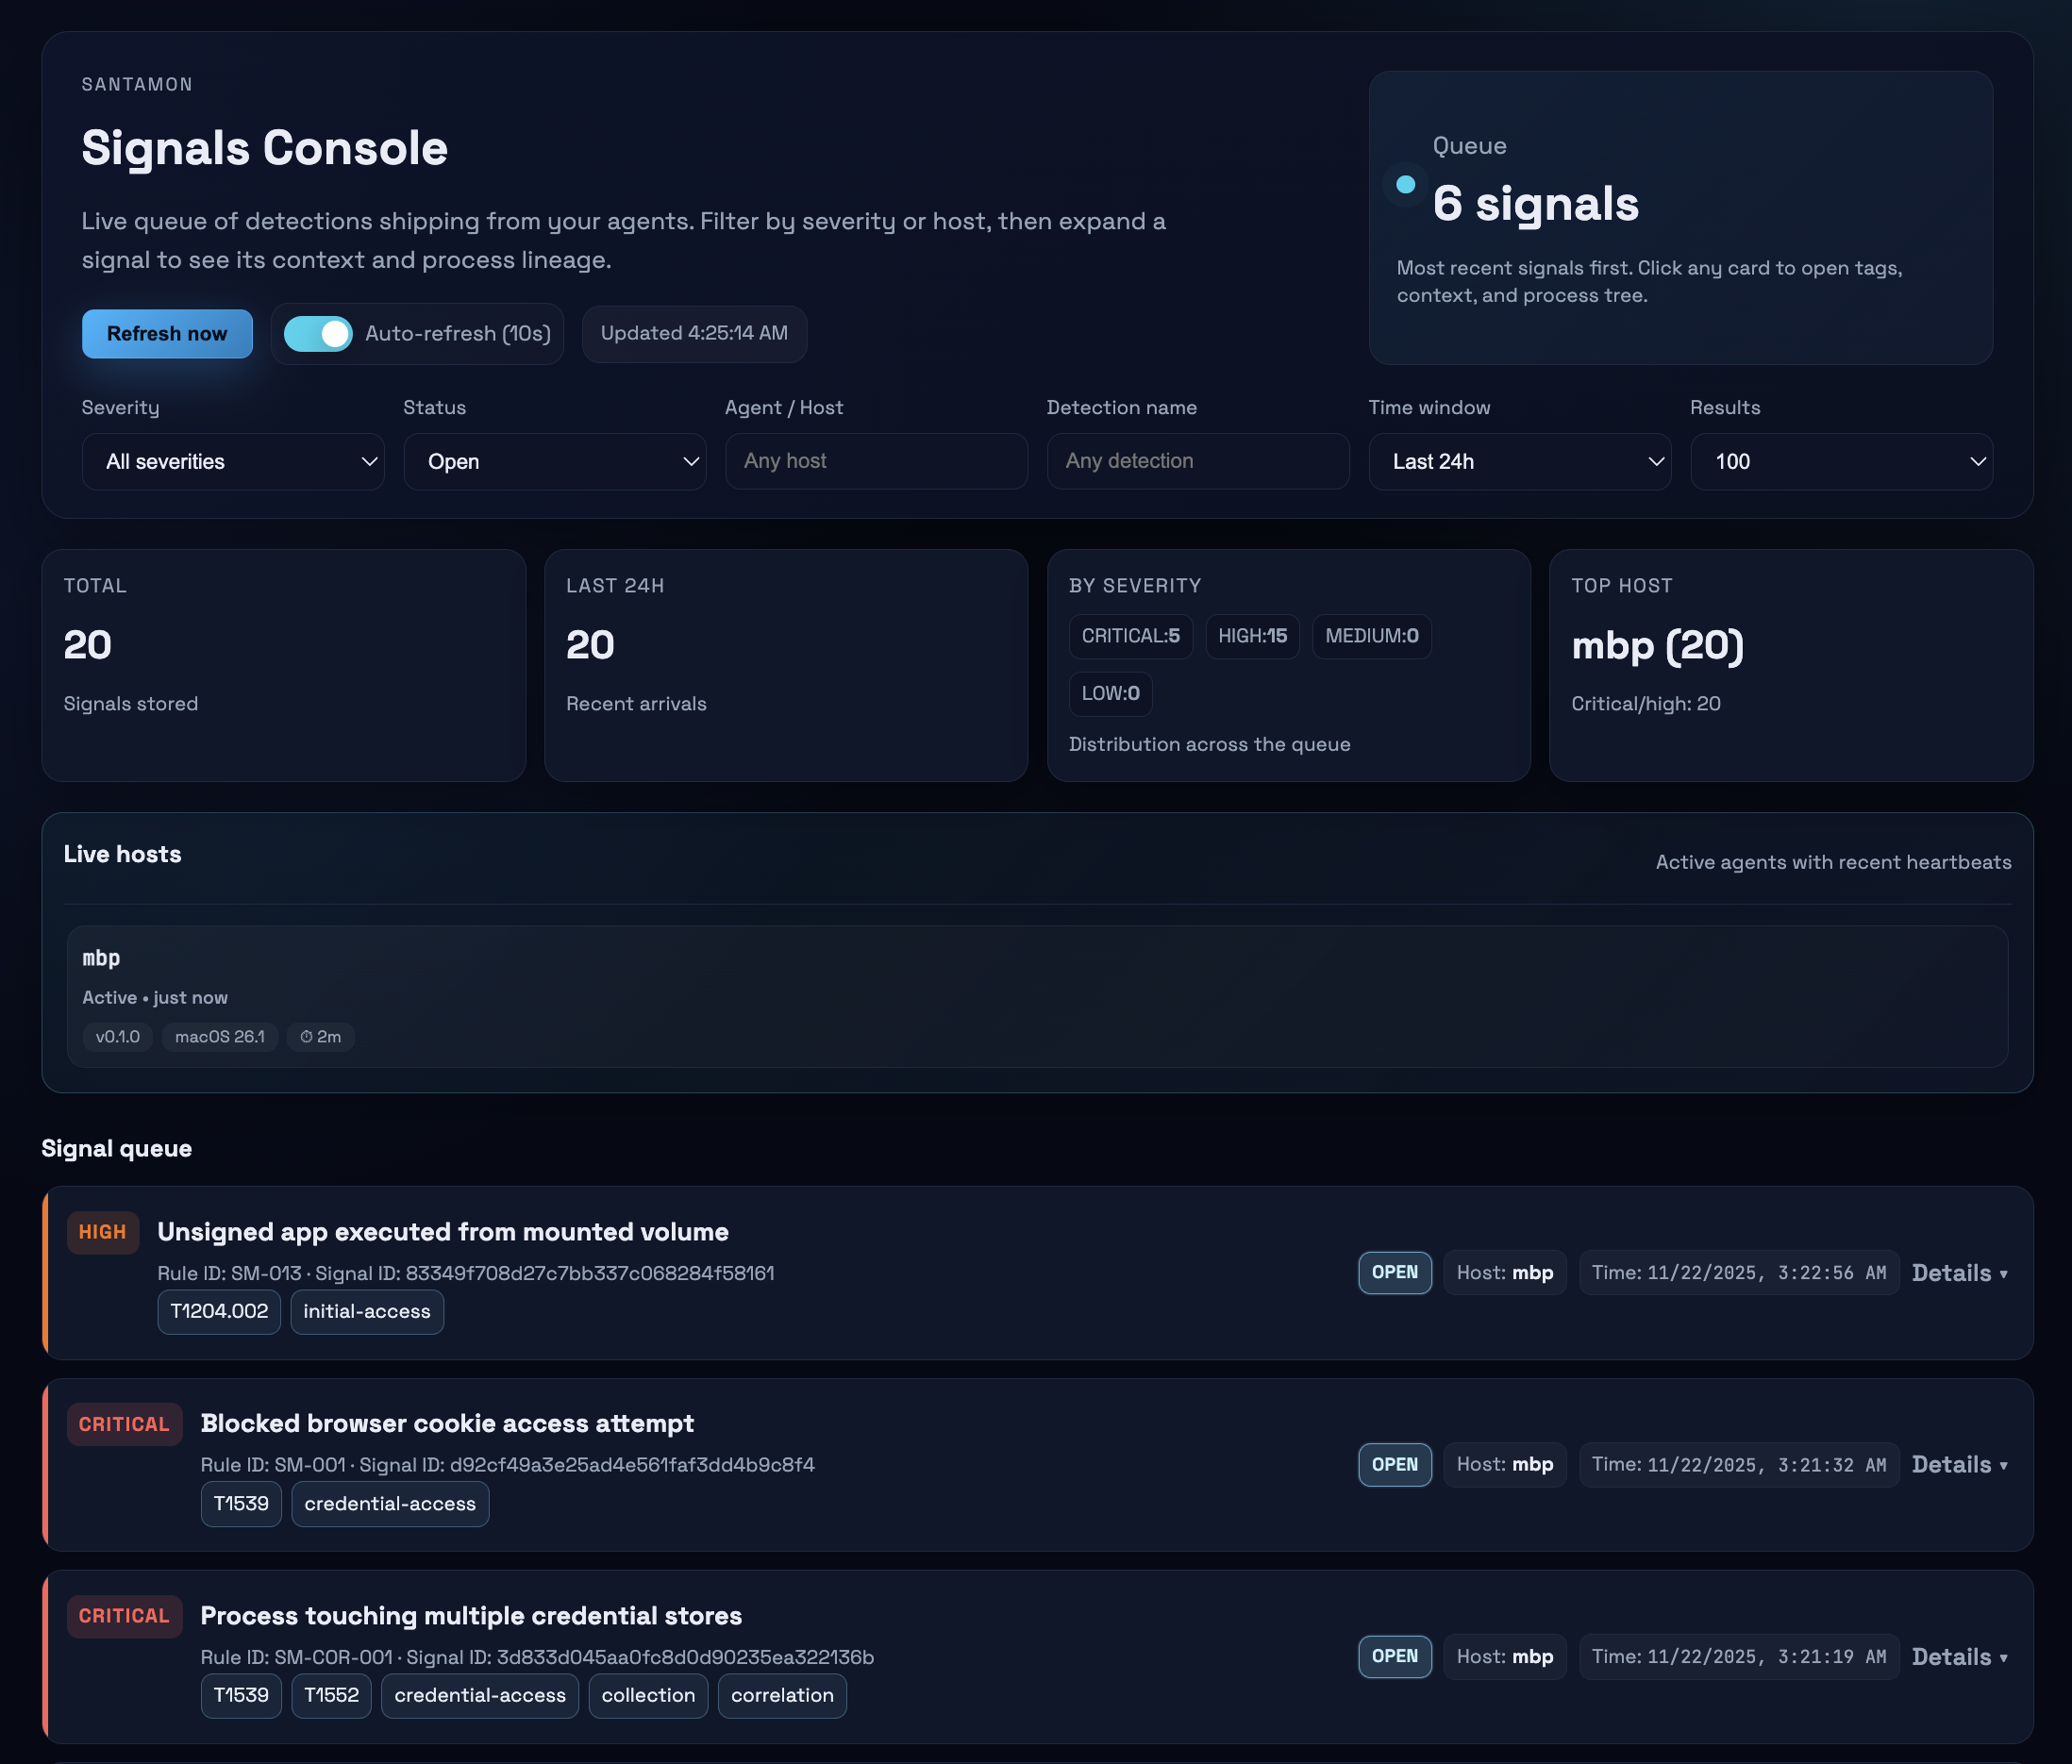 0x4d31/santamon
Lightweight macOS detection agent built on Santa’s Endpoint Security telemetry.
 andreicscs/honeywire
Open-source deception platform that turns any Linux machine into a high-signal canary. Deploy tripwire sensors on files, ports, and network services…
 siddharth2440/network-detection-engine
Lightweight network intrusion detection engine capturing live traffic with libpcap. Detects SYN/ICMP floods, port scans, and signature-based web…
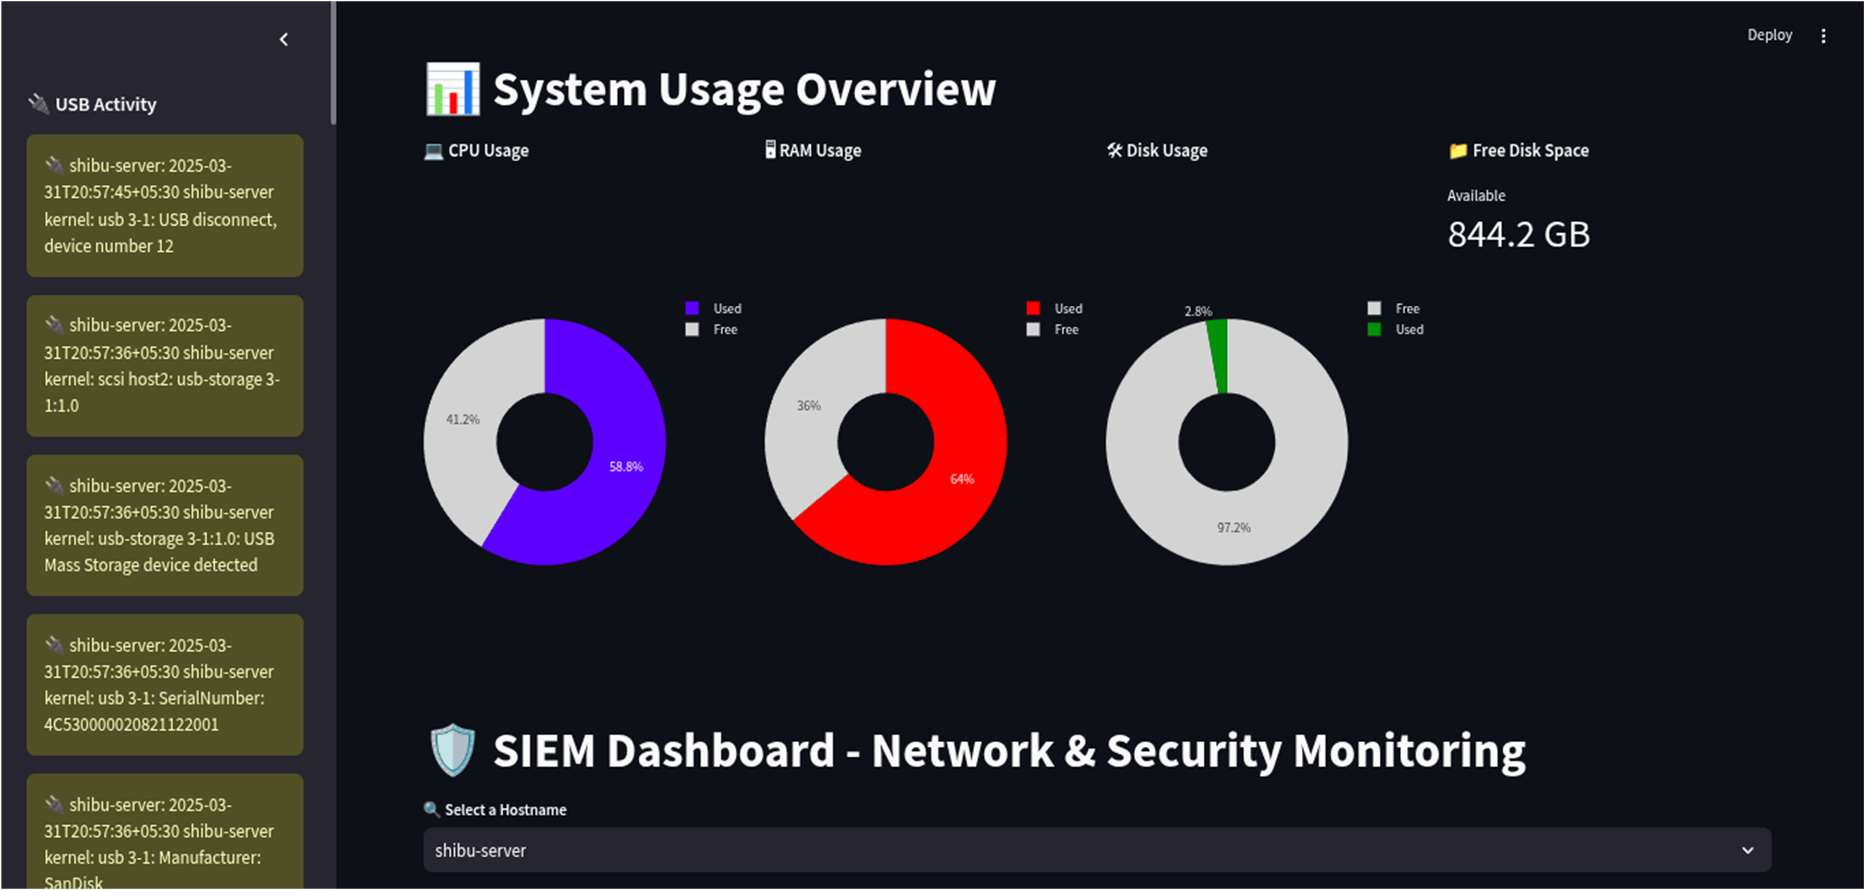
 itzmeshervin/siem-dashboard
A lightweight, real-time Security Information and Event Management (SIEM) dashboard built using Streamlit. It collects system logs, detects USB and…
 owasp/intrusion-alert-educational-network-ids
Lightweight Python-based IDS that monitors network traffic in real-time using Scapy, detecting DoS/DDoS attacks via per-IP request rate analysis with…
 logisek/baconsampler
Sniffs outbound traffic for suspicious, beacon-like callbacks, because if it keeps coming back on schedule, it's probably not breakfast.
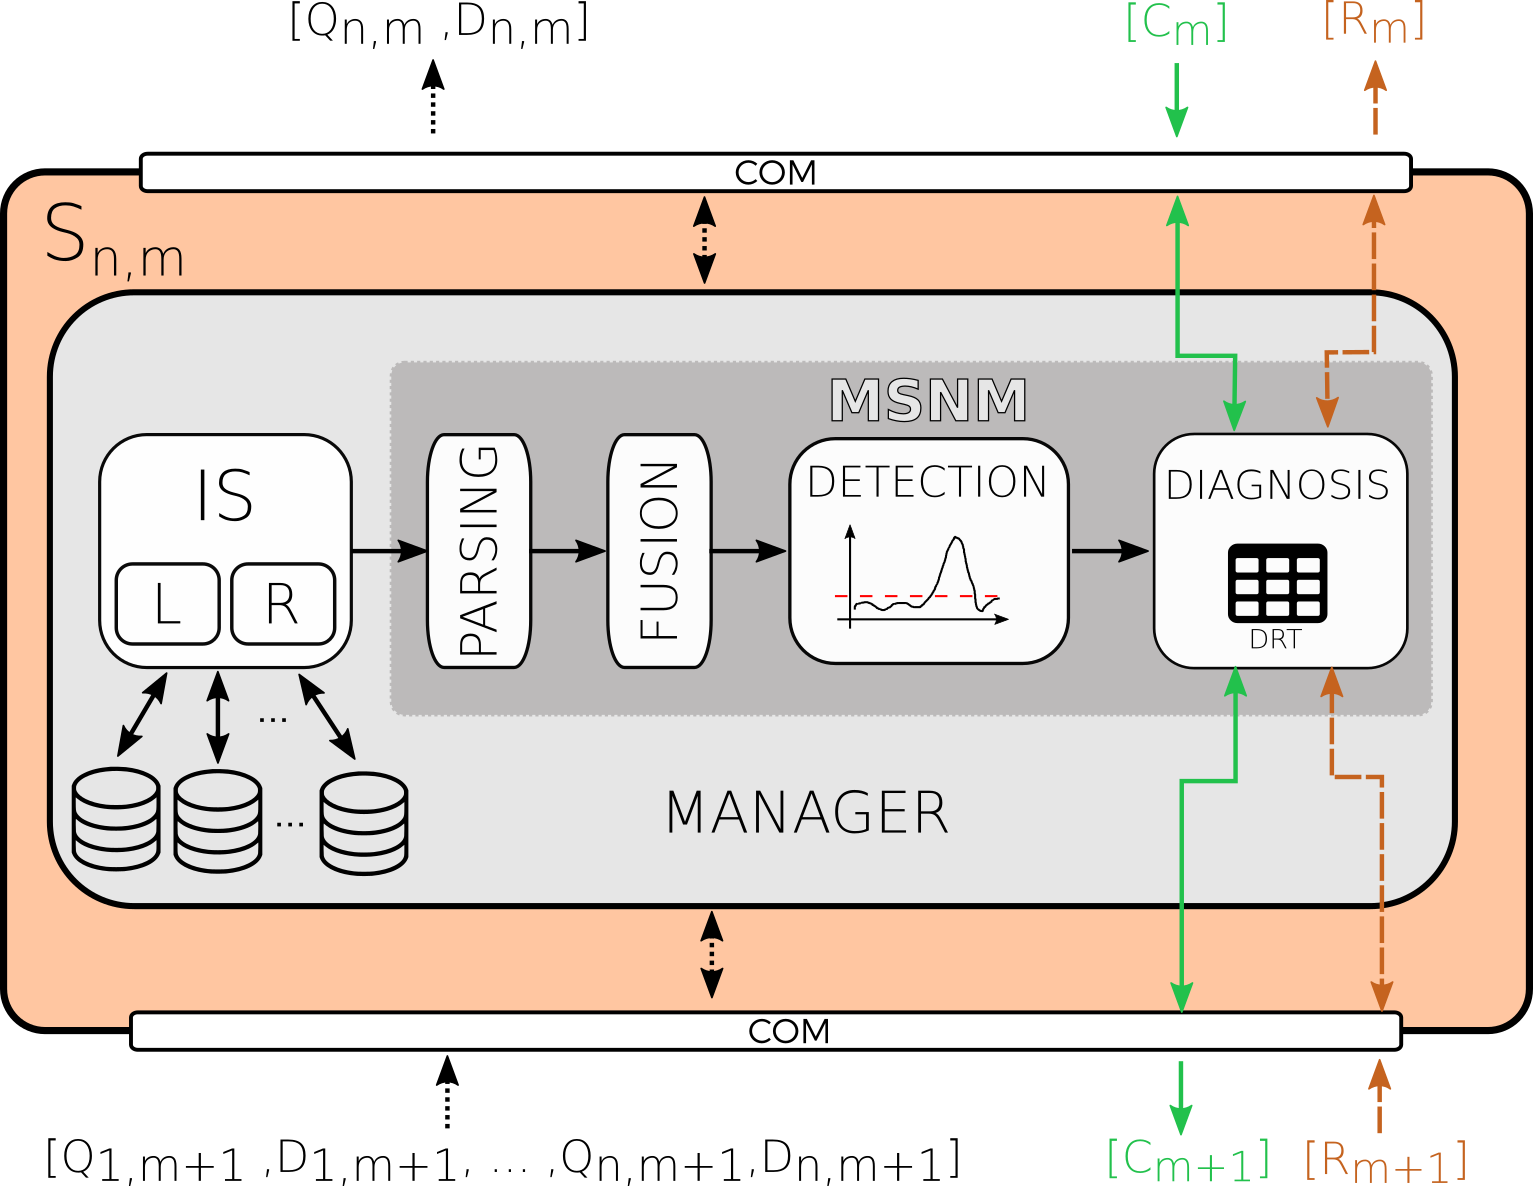 nesg-ugr/msnm-sensor
Multivariate statistical network monitoring sensor that detects anomalies using PCA-based techniques, aggregating lightweight statistics from…
 lopqto/cve-2021-41773_honeypot
Lightweight honeypot for Apache HTTP Server path traversal vulnerability CVE-2021-41773, designed to capture and log exploitation attempts.
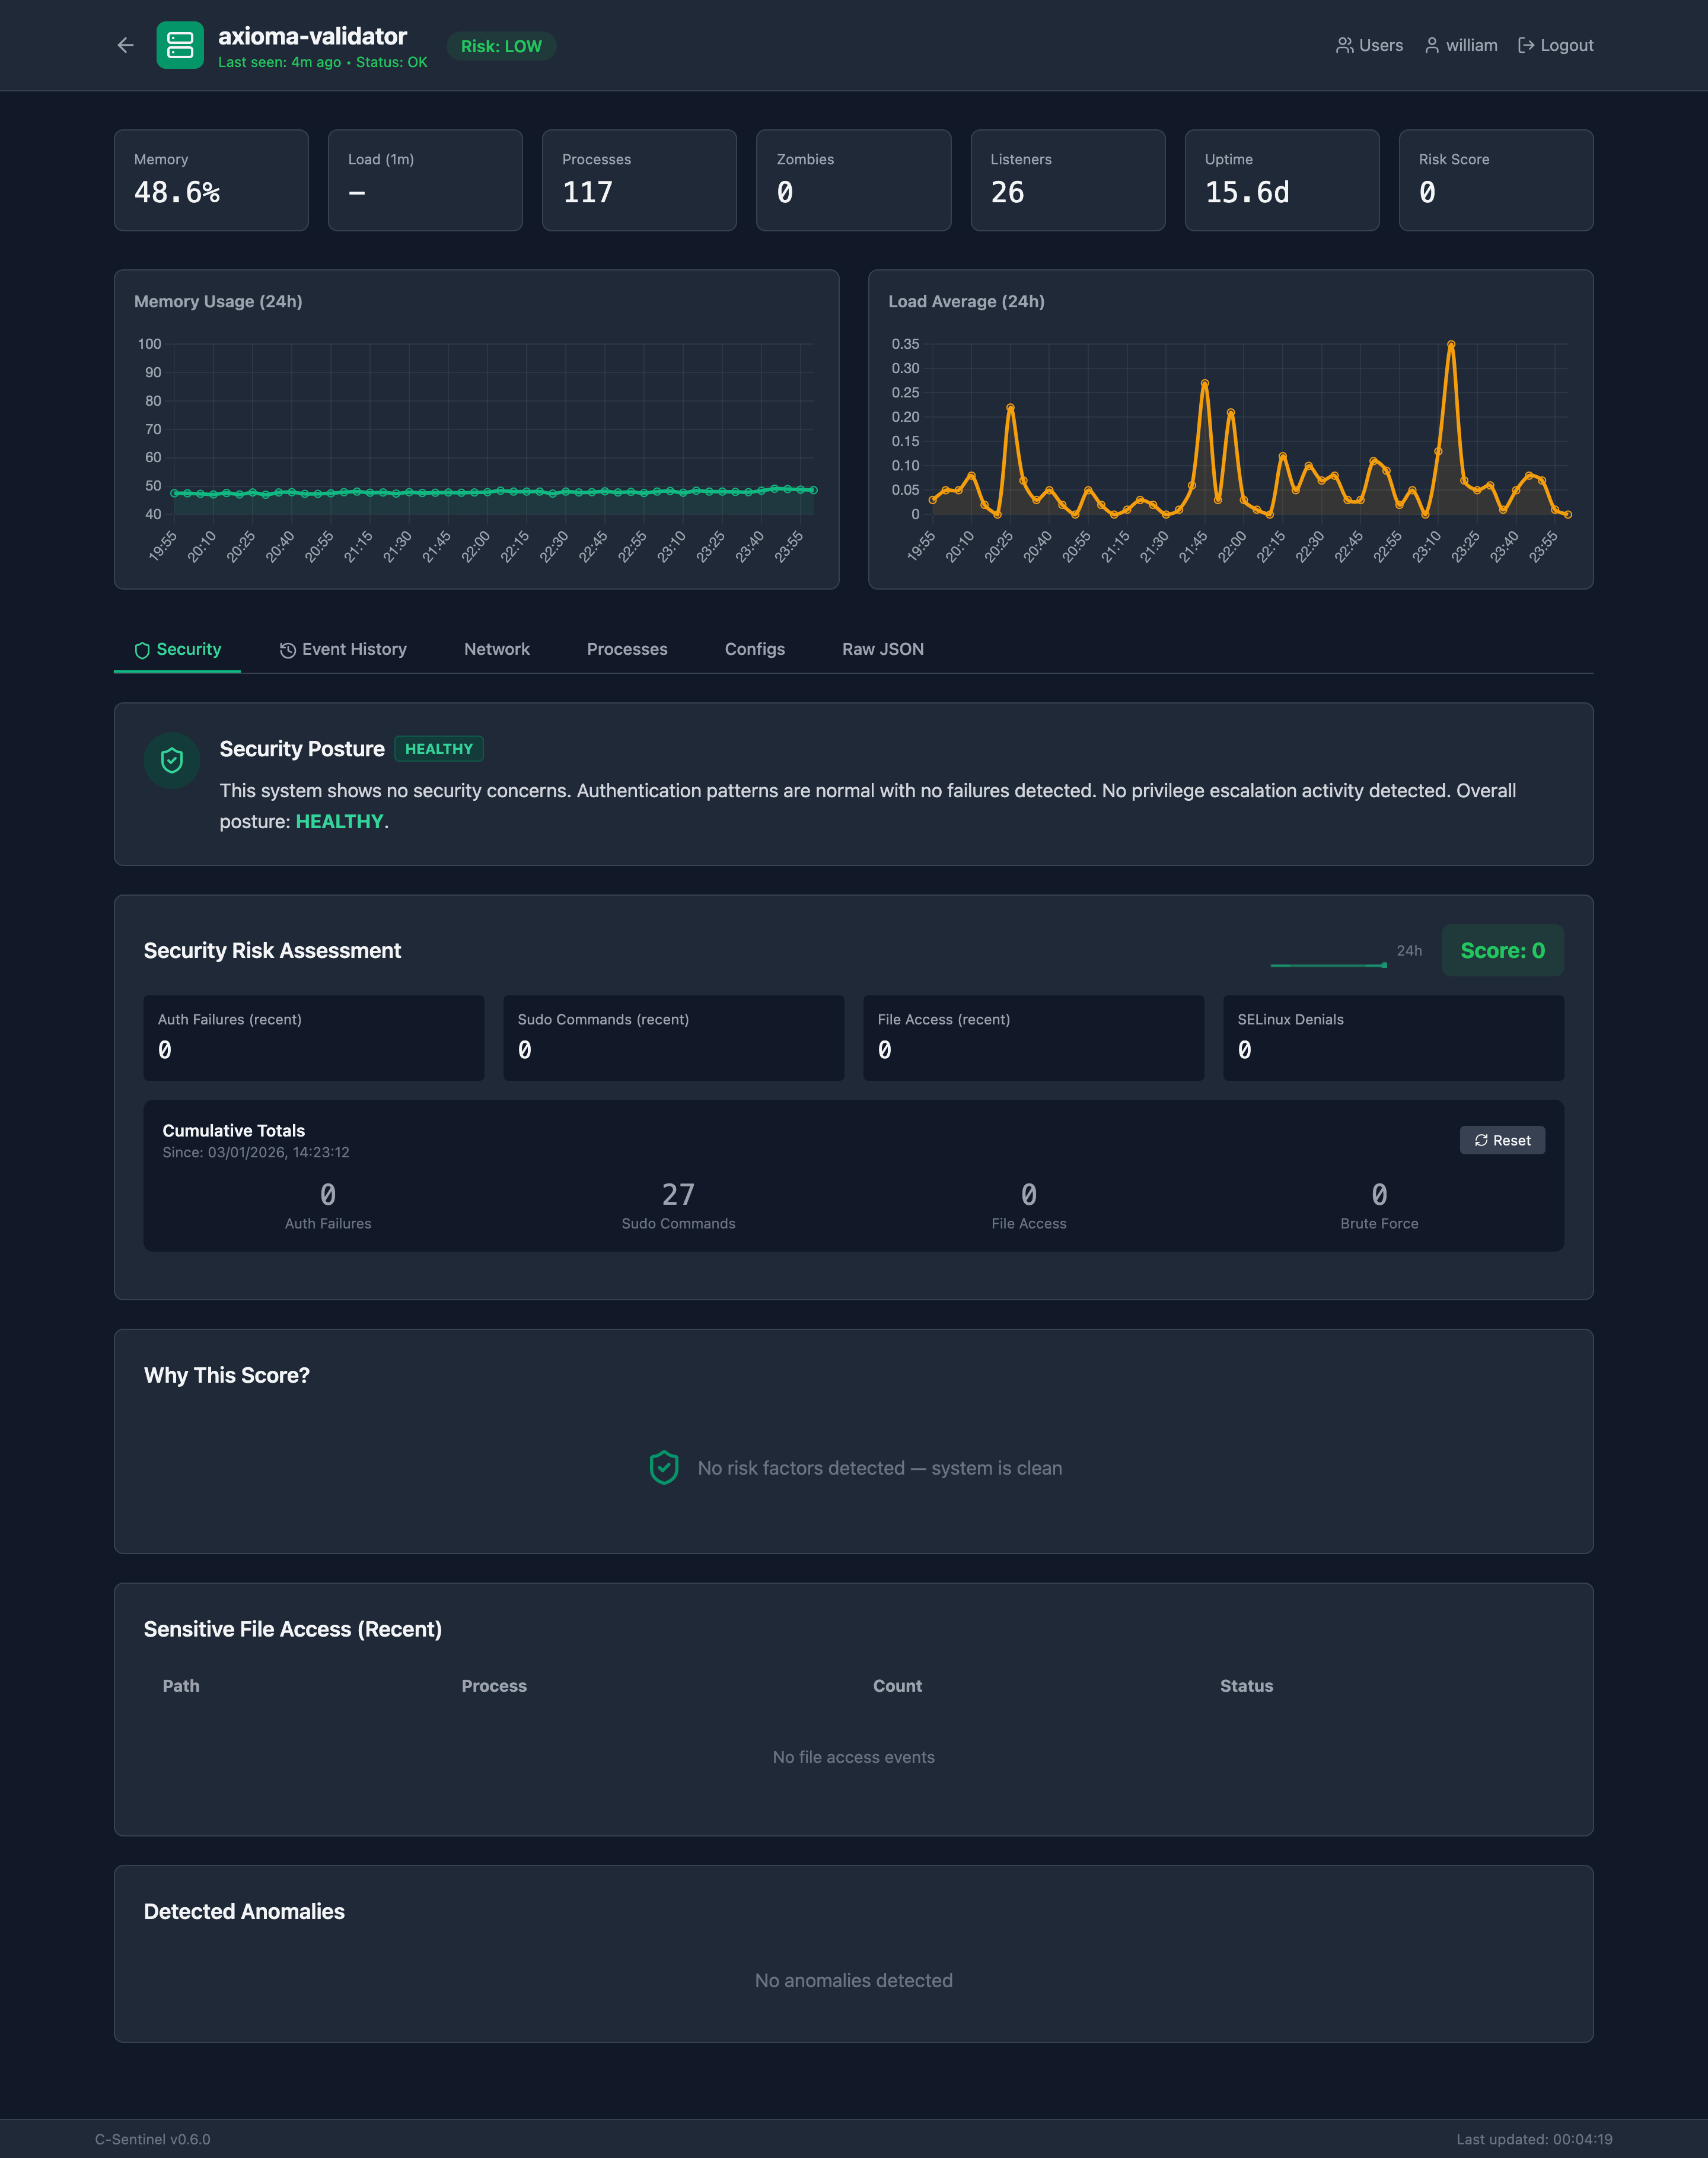 speytech/c-sentinel
Semantic Observability for UNIX Systems - A lightweight C-based system prober with AI-powered analysis
 fksvs/siper
XDP Based Lightweight and Fast Firewall
 r4j3sh-com/cve-2025-55182
Lightweight Go toolkit plus a Dockerized Next.js lab to explore and triage CVE-2025-55182.