
thrunt-god
 backbay-labs/thrunt-god
Threat hunting command system for agentic IDEs
incident-responseinformation-gatheringintrusion-detection+5
36
backbay-labs/thrunt-godThreat hunting command system for agentic IDEs
 hpfeeds/hpfeeds
Honeynet Project generic authenticated datafeed protocol
 malwaretech/log4jtools
Tools for investigating Log4j CVE-2021-44228
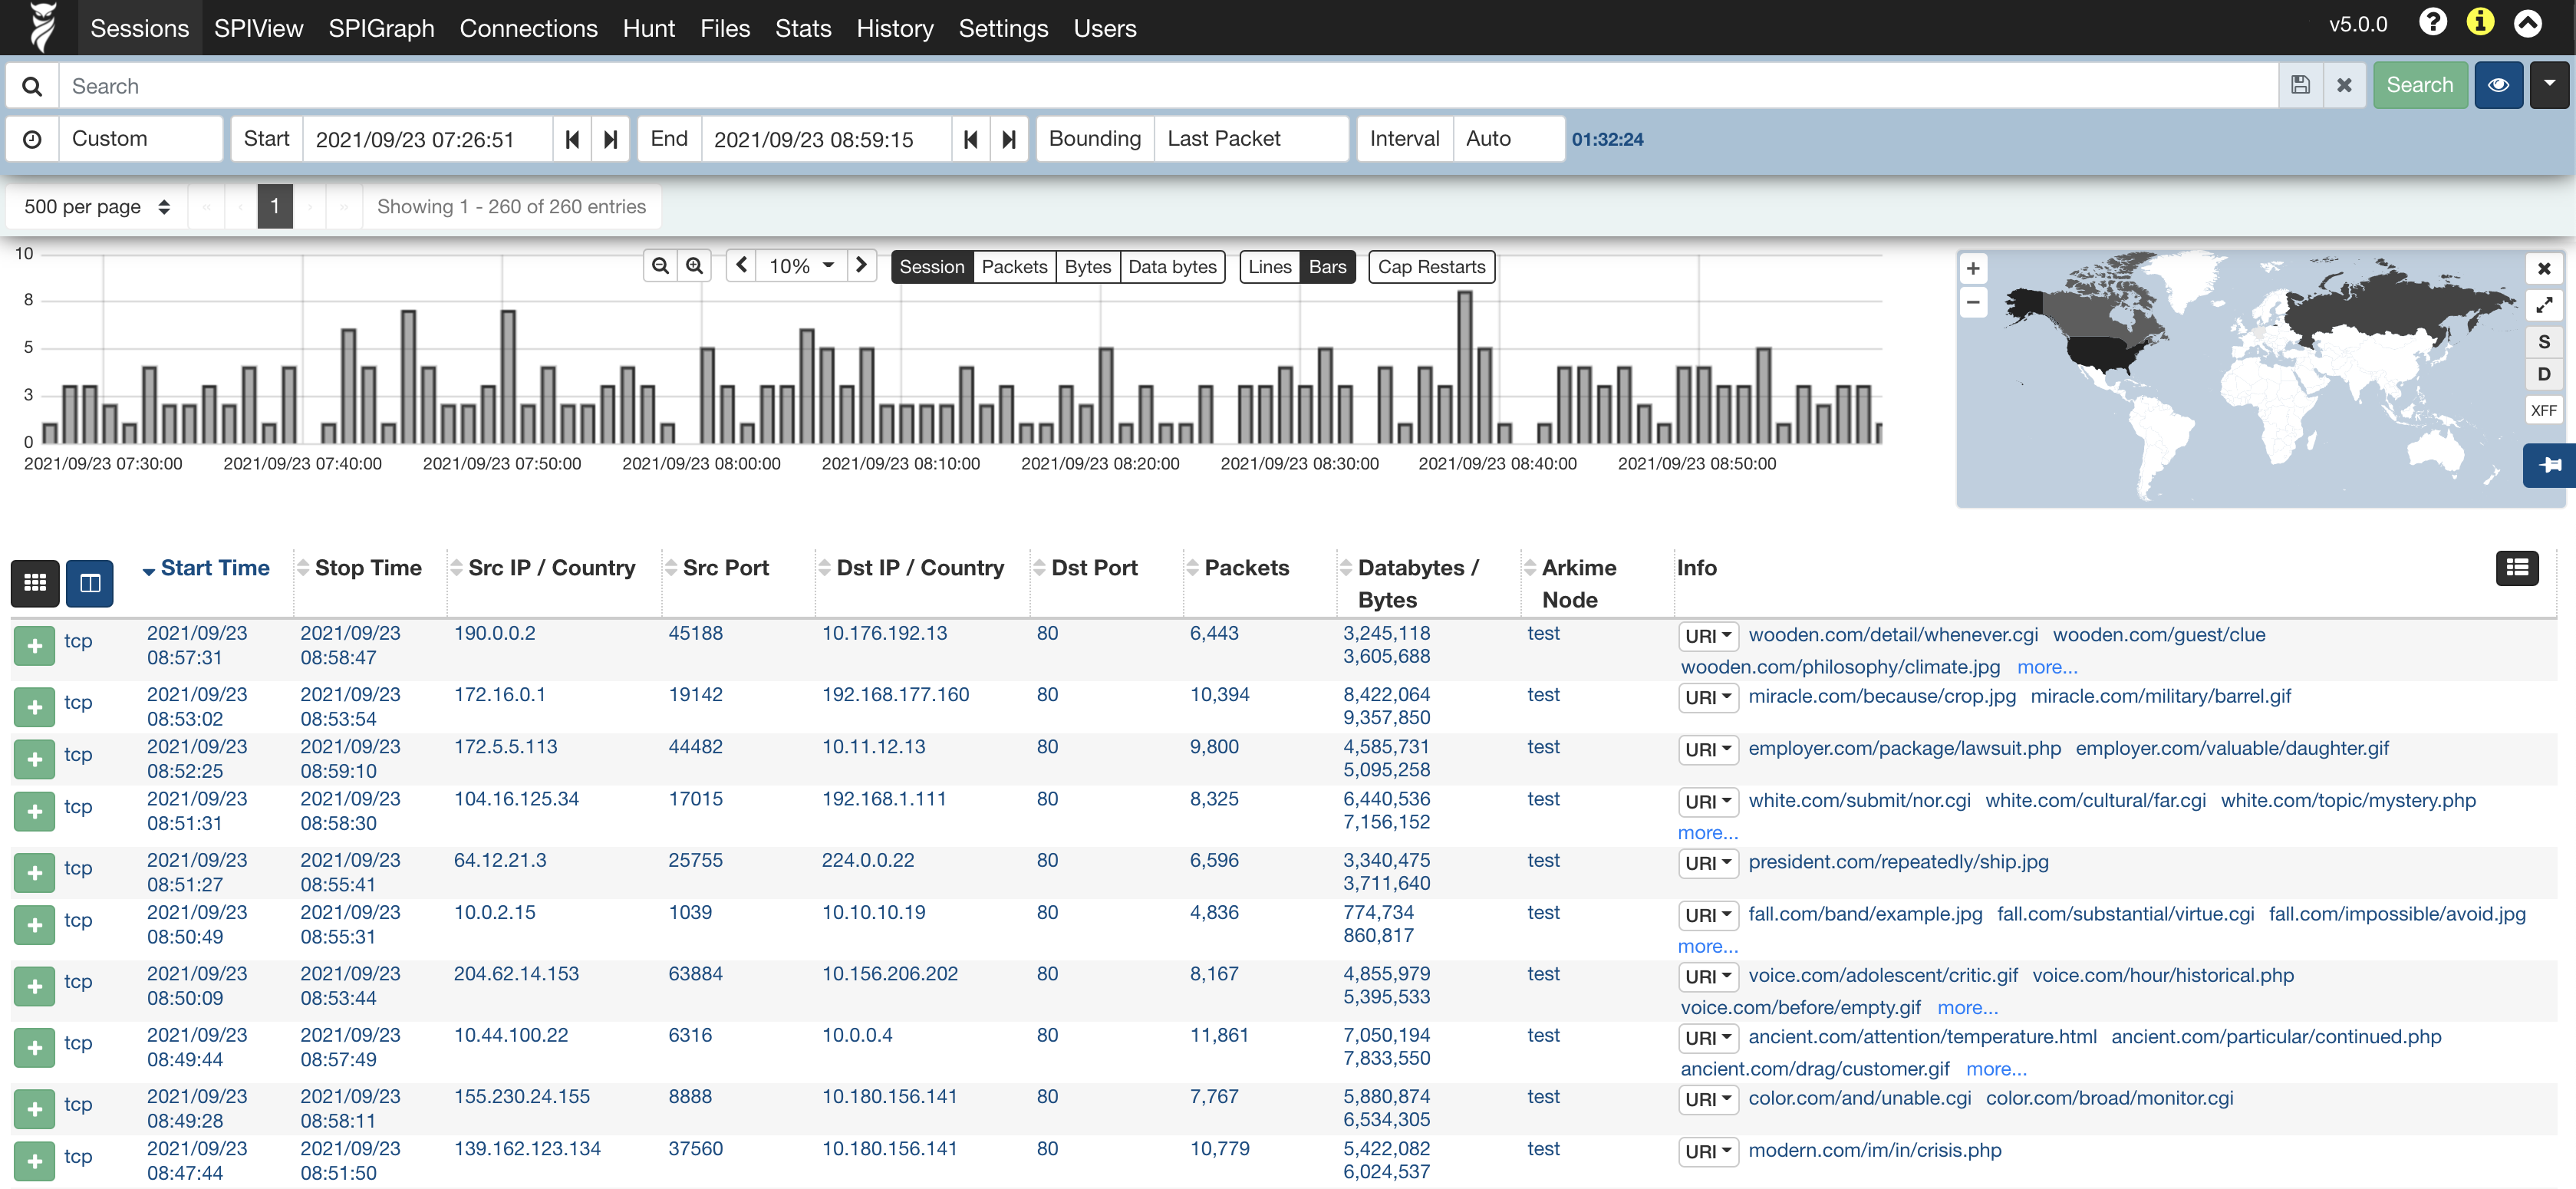 arkime/arkime
Arkime is an open source, large scale, full packet capturing, indexing, and database system.
 the-tcpdump-group/libpcap
System-independent library for user-level packet capture and filtering. Provides a portable framework for low-level network monitoring, security…
 kismetwireless/kismet
Github mirror of official Kismet repository
 pedramamini/threatingestor
Automated threat intelligence aggregation tool that extracts and normalizes indicators from multiple sources (OSINT feeds, malware reports) into a…
 mushorg/buttinsky
Botnet monitoring is a crucial part in threat analysis and often neglected due to the lack of proper open source tools. Our tool will provide an open…
 corelight/icanntld
Zeek script using the official ICANN Top-Level Domain (TLD) list with the Input Framework to extract the relevant information from a DNS query and…
 cred-club/artif
An advanced real time threat intelligence framework to identify threats and malicious web traffic on the basis of IP reputation and historical data.
 kolya5544/bearftp
Honeypot FTP server written in .NET Core (C#) for both Linux and Windows.
 sage-s11/sigcorr
SigCorr is the first open-source tool to detect cross-protocol attack chains spanning SS7/MAP, Diameter S6a, and GTPv2-C through unified subscriber…
 d0n601/wp-mhn
Integrates your Modern Honeypot Network Server and Wordpress Blog via MHN's REST API and WP's shortcodes
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
 nesg-ugr/msnm-sensor
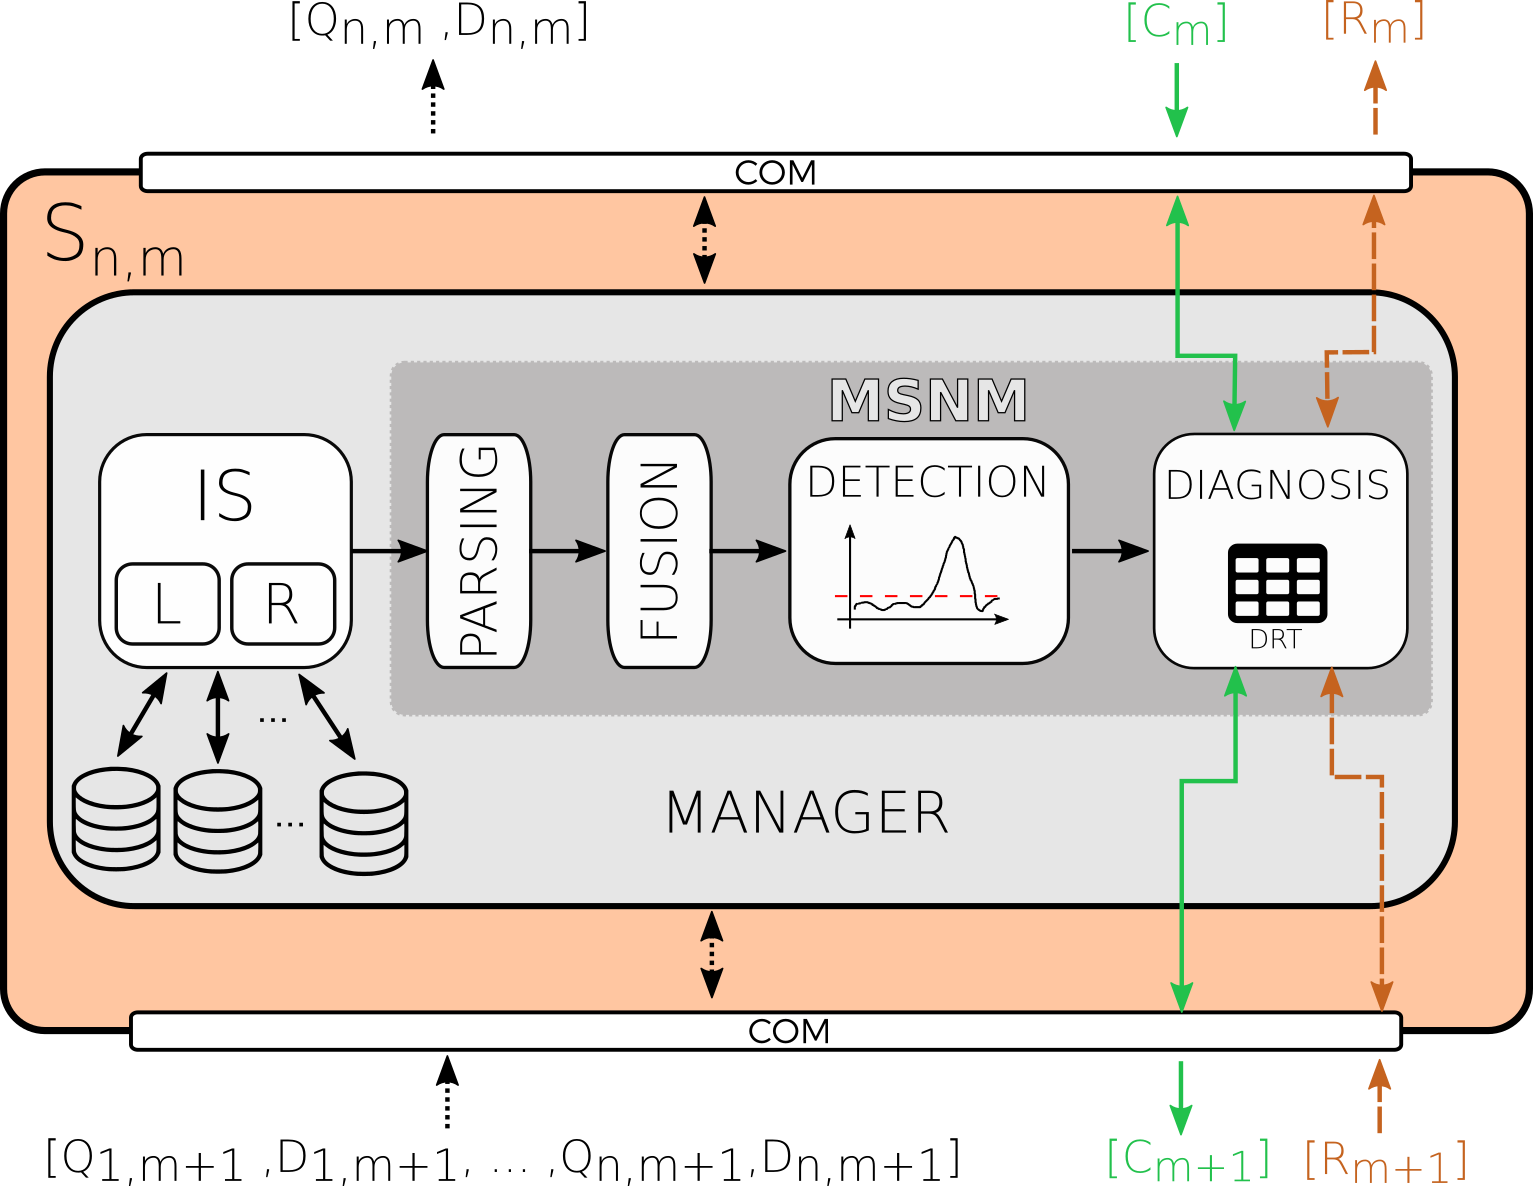
Multivariate statistical network monitoring sensor that detects anomalies using PCA-based techniques, aggregating lightweight statistics from…
 corelight/top-dns
Top DNS Measurement for Bro
 mcastens/alycon-threat-landscape
Training-free anomaly detection framework using Shannon Entropy, Fisher Information, and Wasserstein Distance to map system states into geometrically…
 randomuserid/tylium
Primary data pipelines for intrusion detection, security analytics and threat hunting