
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
30 results
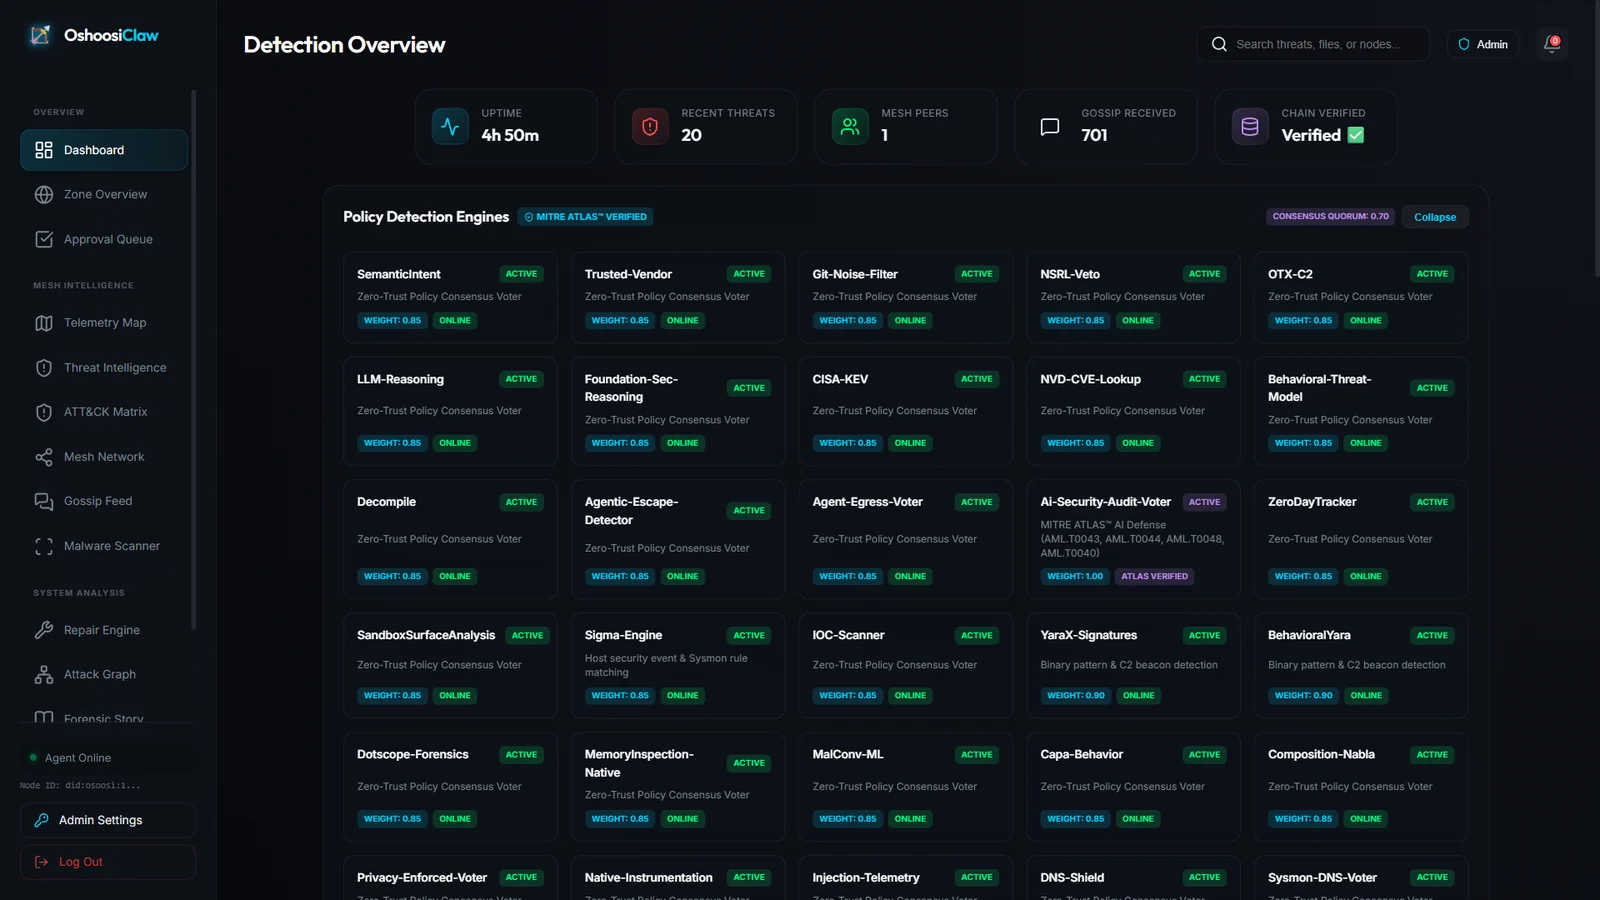
OshoosiClaw preview

OshoosiClaw

GitHuboyesanyf/oshoosiclaw

Autonomous Rust endpoint security agent combining Ring-0 Windows driver and Linux eBPF pre-execution blocking, YARA detection, MITRE ATT&CK mapping,…

ai-securityanomaly-detectioncommand-and-control+8
7
17h 7m ago
c2detect preview

c2detect

GitHubcognis-digital/c2detect

C2 server fingerprinter — Cobalt Strike, Sliver, Mythic, Havoc, Brute Ratel

command-and-controldefensive-toolsfingerprint-spoofing+8
421 month ago
Open-Source-Threat-Intel-Feeds preview

Open-Source-Threat-Intel-Feeds

GitHubbert-janp/open-source-threat-intel-feeds

This repository contains Open Source freely usable Threat Intel feeds that can be used without additional requirements. Contains multiple types such…

intrusion-detectionioc-managementnetwork-security+3
97019h 14m ago
Loki preview

Loki

GitHubneo23x0/loki

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

anomaly-detectiondigital-forensicsdisk-forensics+11
3.8k10 months ago
flightsim preview

flightsim

GitHubalphasoc/flightsim

A utility to safely generate malicious network traffic patterns and evaluate controls.

command-and-controldefensive-toolsdns-analysis+4
1.4k2 years ago
rita preview

rita

GitHubactivecm/rita

Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.
anomaly-detectioncommand-and-controldns-analysis+4
6194 months ago
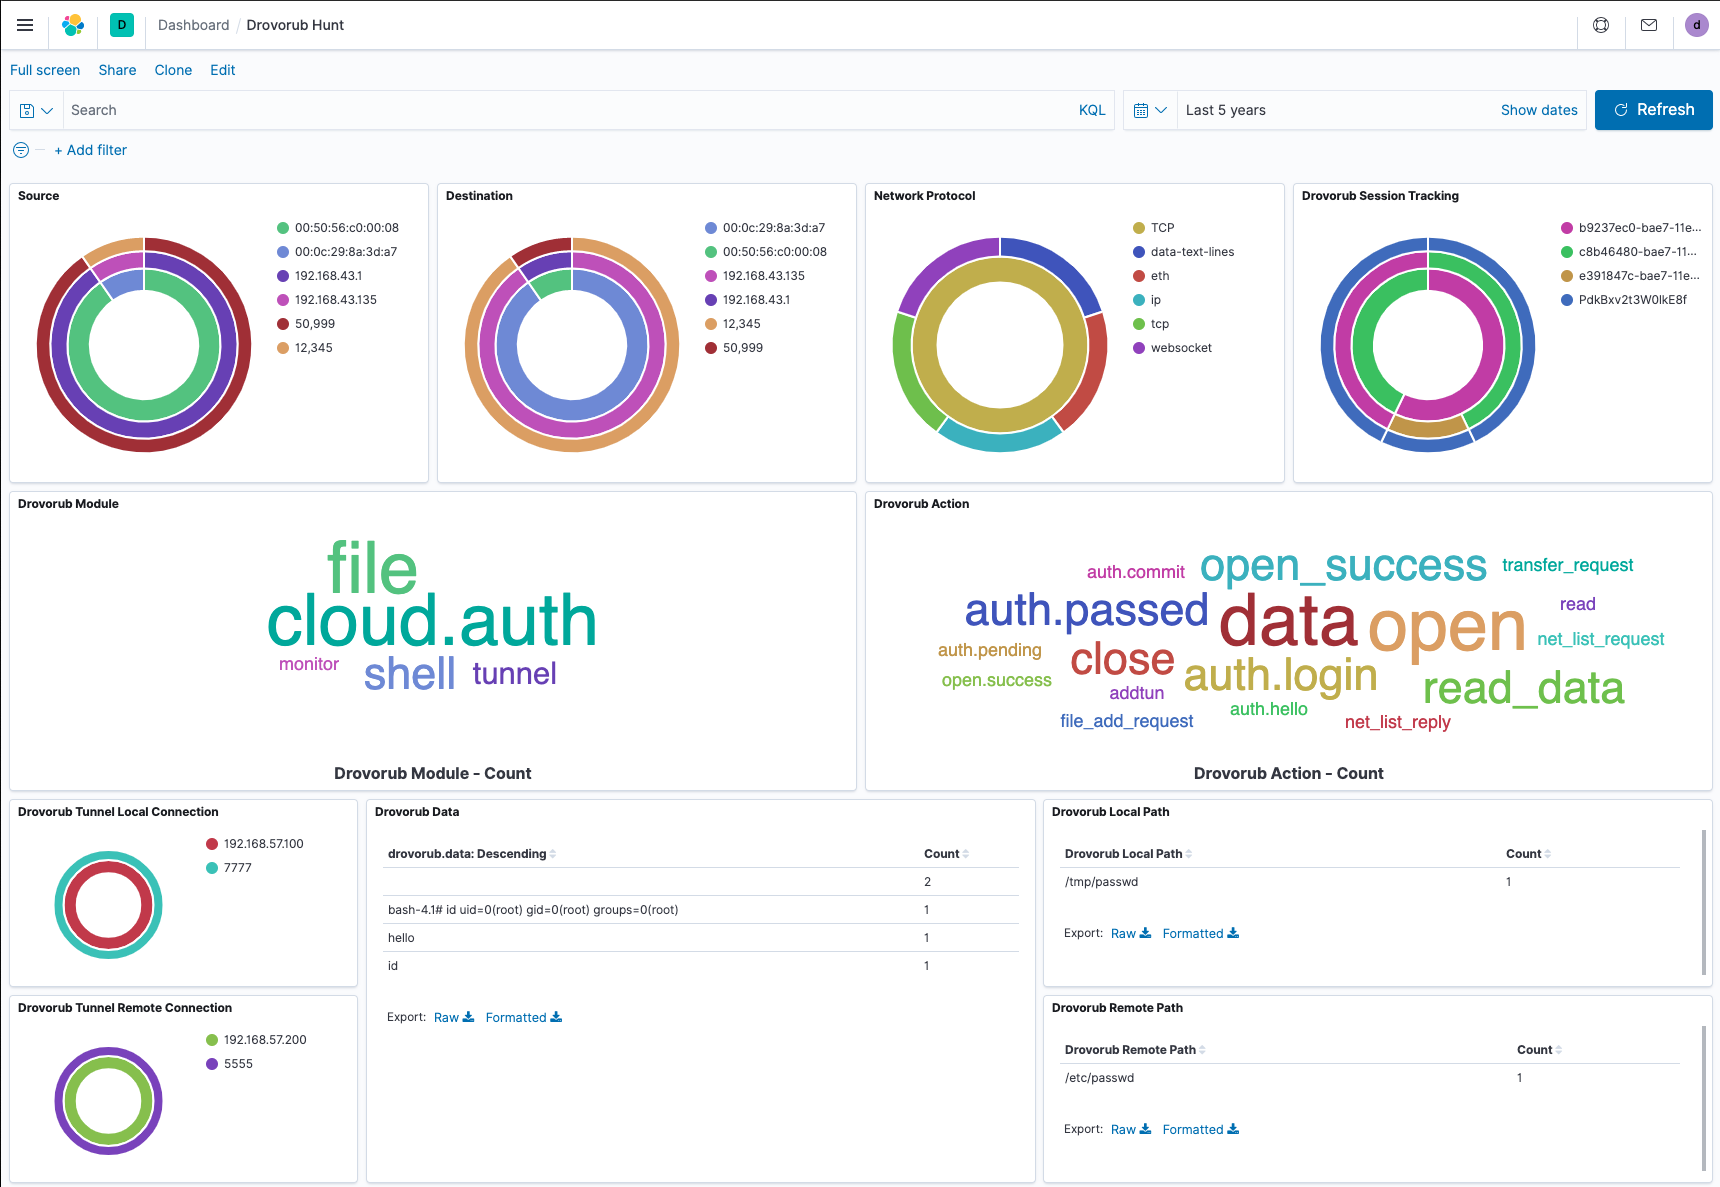
drovorub-hunt preview

drovorub-hunt

GitHubinsane-forensics/drovorub-hunt

A tool to assist with network-based hunting for GRU's Drovorub malware c2

incident-responseintrusion-detectionmalware-analysis+3
256 years ago
Threat-Hunting preview

Threat-Hunting

GitHuba2awais/threat-hunting

Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
educationincident-responseinformation-gathering+4
801 day ago
Royal_APT preview

Royal_APT

GitHubnccgroup/royal_apt

Royal APT - APT15 - Related Information from NCC Group Cyber Defense Operations Research

command-and-controlcurated-resourcesintrusion-detection+3
528 years ago
Zeek-Intelligence-Feeds preview

Zeek-Intelligence-Feeds

GitHubcriticalpathsecurity/zeek-intelligence-feeds

Aggregated Zeek-format threat intelligence feeds with combined indicators from public and curated sources for continuous IDS and network threat…

command-and-controlintrusion-detectionnetwork-security+3
3989h 35m ago
got-responded preview

got-responded

GitHubjoda32/got-responded

A simple tool to detect NBT-NS and LLMNR spoofing (and messing with them a bit)

intrusion-detectionnetwork-securitypenetration-testing+1
367 years ago
zeek-netsupport-detector preview

zeek-netsupport-detector

GitHubcorelight/zeek-netsupport-detector

A Zeek based NetSupport detector. NetSupport is often abused by attackers in malware.

command-and-controldefensive-toolsintrusion-detection+3
21 year ago
Yara-detection-rules preview

Yara-detection-rules

GitHubembee-research/yara-detection-rules

Yara Rules for Modern Malware
curated-resourcesdefensive-toolsintrusion-detection+2
802 years ago
CVE-2026-24207 preview

CVE-2026-24207

GitHuboffseckit/cve-2026-24207

CVE-2026-24207 — NVIDIA Triton SageMaker auth bypass to unauth RCE. Detection script, bypass demo, RCE-chain PoC, and IDS rules.
authenticationcloud-securitycommand-and-control+8
14 months ago
BruteRatel-DetectionTools preview

BruteRatel-DetectionTools

GitHubimmersive-labs-sec/bruteratel-detectiontools

A collection of Tools and Rules for decoding Brute Ratel C4 badgers
command-and-controldefensive-toolsincident-response+3
674 years ago
BerrySentinel preview

BerrySentinel

GitHubdereeqw/berrysentinel

Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
anomaly-detectioncommand-and-controldefensive-tools+8
138 months ago
cpanel-cve-2026-41940-fix preview

cpanel-cve-2026-41940-fix

GitHubshahidmallaofficial/cpanel-cve-2026-41940-fix

One-shot detection and remediation for cPanel/WHM servers compromised via CVE-2026-41940, including IOC checks, malware cleanup, C2 blocking, and…
cloud-infrastructure-securityconfiguration-auditingdigital-forensics+5
46 months ago
zeek-asyncrat-detector preview

zeek-asyncrat-detector

GitHubcorelight/zeek-asyncrat-detector

A Zeek based AsyncRAT malware detector.

anomaly-detectioncommand-and-controlintrusion-detection+3
31 year ago
Previous12Next